

joro
 bishopfox/joro
A collaborative web exploitation framework.
command-and-controlexploit-frameworksfuzzing+5
bishopfox/joroA collaborative web exploitation framework.
 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 kyle41111/ai-file
A listener profile for the Mythic C2 framework that utilizes AI vendors file API's
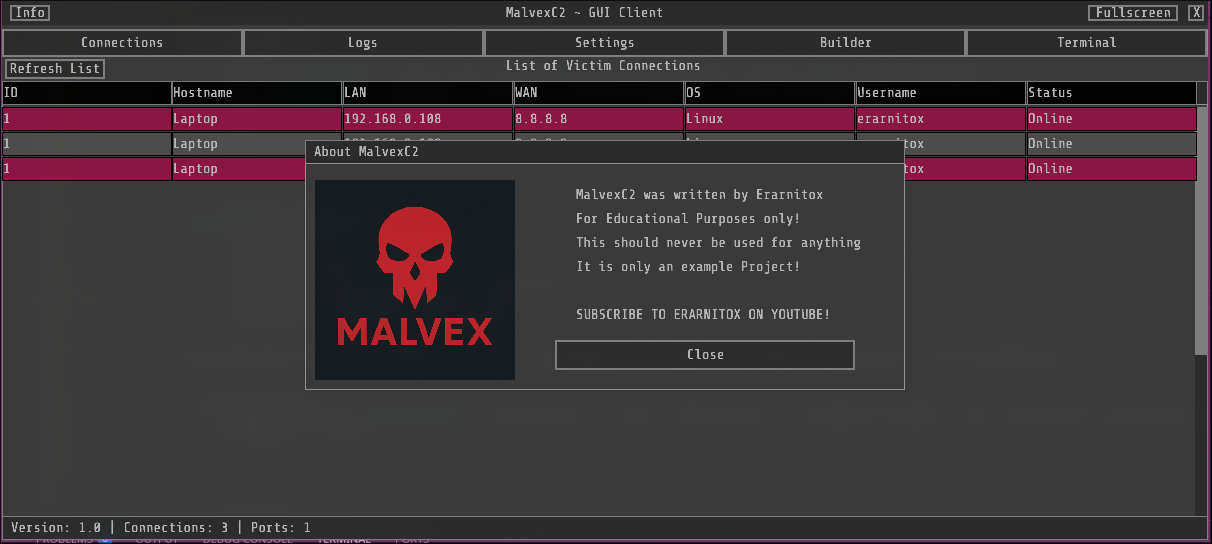 erarnitox/malvexc2
A simple C2 Framework written in modern C++
 nccgroup/async-pico-hub
Async PICO Hub is a work-in-progress framework to extend Cobalt Strike with custom event monitoring and in-process Asynchronous BOFs
 leviticus-triage/chromsploit-framework
Advanced AI-Powered Exploitation Framework | CVE-2025-4664 & CVE-2025-2783 & CVE-2025-2857 & CVE-2025-30397 |
 linnemanlabs/glimmer
Adversary emulation and C2 framework for security research
 razureink/fucker
Penetration testing framework with AI-driven decision engine
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 capture0x/adstrike
AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
 praetorian-inc/pentestly
Python and Powershell internal penetration testing framework
 byt3bl33d3r/silenttrinity
An asynchronous, collaborative post-exploitation agent powered by Python and .NET's DLR
 gh05tcrew/metasploitmcp
MCP Server for Metasploit
 empireproject/empire-gui
Empire client application
 rand0m1ze/ezsploit
Linux bash script automation for metasploit