

blitzstrike
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
exploitationinformation-gatheringpayload-generation+8
515
shinthink/blitzstrikeMCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
 kryptsec/oasis
Open-source AI security benchmarking CLI. Measure how AI models perform offensive security tasks with MITRE ATT&CK analysis and KSM scoring.
 blacksnufkin/cheshire
Adaptix C2 service plugin that drives LitterBox payload analysis from the operator UI.
 cogensec/gideon
Autonomous security operations agent for threat intelligence, vulnerability research, IOC analysis, and red teaming. Supports dual-mode operations…
 sydsec1/syd
Air-gapped cybersecurity assistant for security professionals. 100% offline AI-powered analysis tool for Nmap, Volatility, BloodHound, Metasploit,…
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 darkr4y/geacon
Practice Go programming and implement CobaltStrike's Beacon in Go
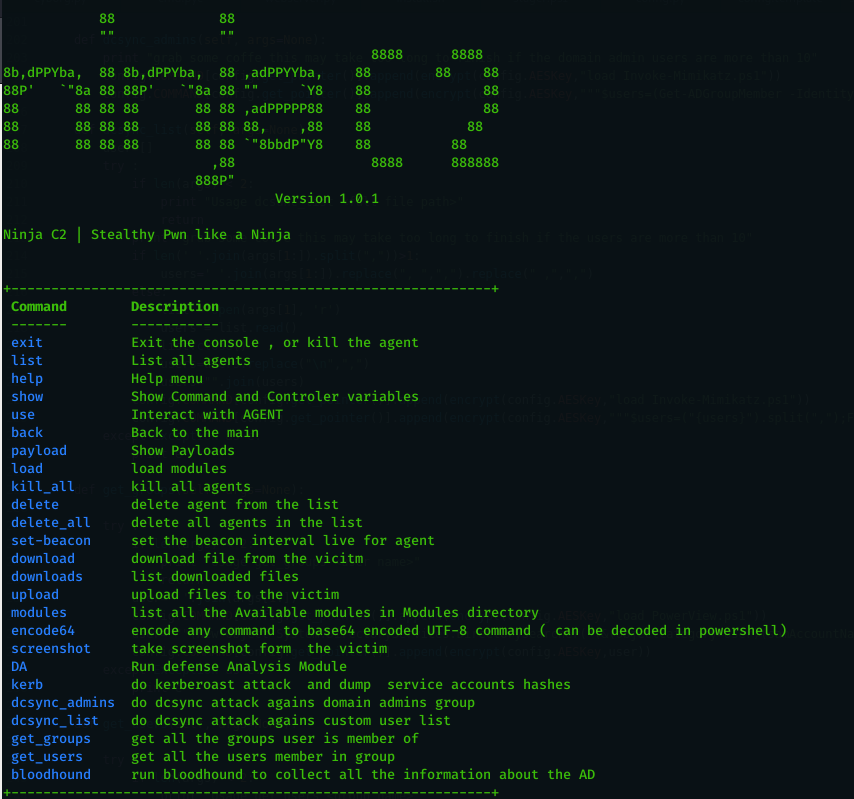 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
 lucasfrag/kali-linux-tools-interface
Graphical Web interface developed to facilitate the use of security information tools.
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 vxcontrol/pentagi
Fully autonomous AI Agents system capable of performing complex penetration testing tasks
 gentilkiwi/mimikatz
A little tool to play with Windows security
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 peass-ng/peass-ng
PEASS - Privilege Escalation Awesome Scripts SUITE (with colors)
 gallopsled/pwntools
CTF framework and exploit development library
 beefproject/beef
The Browser Exploitation Framework Project
 bishopfox/sliver
Adversary Emulation Framework