
joro
 bishopfox/joro
A collaborative web exploitation framework.
command-and-controlexploit-frameworksfuzzing+5
bishopfox/joroA collaborative web exploitation framework.
 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 galoryber/fawkes
Fawkes is a golang Mythic C2 Agent exclusively written by AI.
 degenerat3/meteor
A cross-platform C2/teamserver supporting multiple transport protocols, written in Go.
 blacksnufkin/cheshire
Adaptix C2 service plugin that drives LitterBox payload analysis from the operator UI.
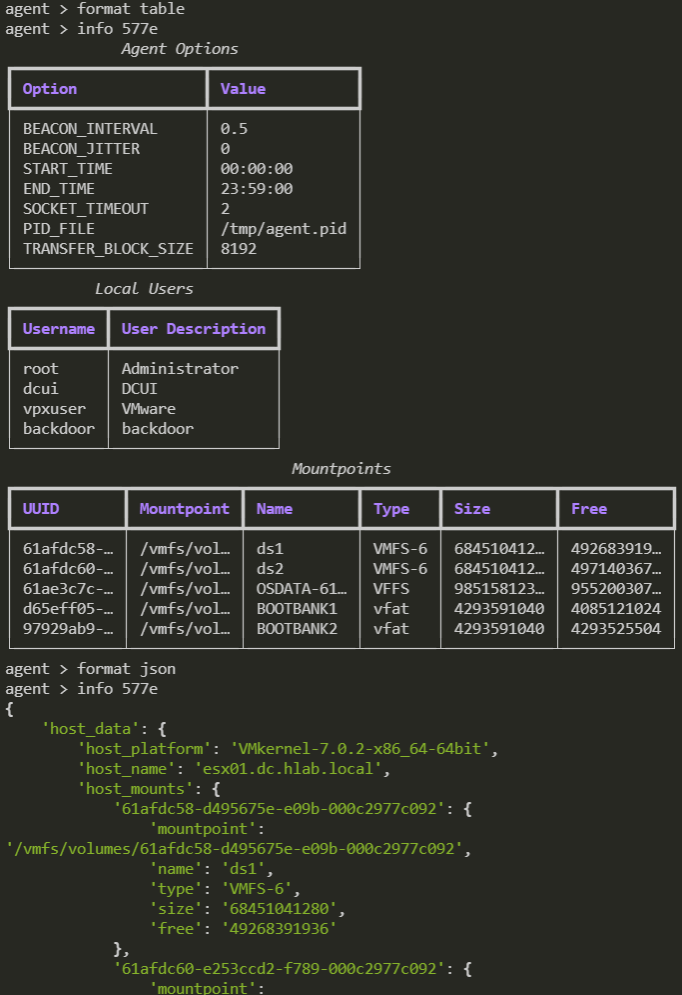 psmths/reave
WIP Post-exploitation framework tailored for hypervisors.
 jas502n/burpsuite-plugin
Plugin For BurpSuite (Pentester)
 owasp/redteamtoolkit
The WASM Based Security Toolkit for the Web First Paradigm
 qmadev/crabloader
Rust-based User-Defined Reflective Loader for Cobalt Strike payloads. Avoids RWX memory pages for OPSEC safety. Includes an extractor tool for loader…
 cspf-founder/red-clippy
open-source pentest management built to be operated by an AI agent
 stuxlabs/awe
adaptive agents for dynamic web penetration testing
 xiao-zhu-zhu/pig_cs4.4
Cobalt Strike 4.4 猪猪版 去暗桩 去流量特征 beacon仿造真实API服务 修补CVE-2022-39197补丁
 top-celestial-company-ltd/dros-vep-lite
Open-source, 100% reproducible AI Agent Runtime Security Benchmark & Sandbox Environment (RFC-010 Draft Protocol).
 xorrior/apfell-chrome-extension-c2server
Apfell C2 Server for the Google Chrome Extension Payload
 lovechoudoufu/about_cobaltstrike4.5_cdf
cobaltstrike4.5版本破解、去除checksum8特征、bypass BeaconEye、修复错误路径泄漏stage、增加totp双因子验证、修复CVE-2022-39197等
 mekhalleh/exchange_proxylogon
Module pack for #ProxyLogon (part. of my contribute for Metasploit-Framework) [CVE-2021-26855 && CVE-2021-27065]
 azmisyahrul/prismsec
Secure, modular MCP server wrapping nmap, nuclei, gobuster, subfinder, httpx, nikto, sqlmap for AI-powered pentesting
 b0fh/cve-2018-4878
Metasploit module for CVE-2018-4878