CVE-2026-44680-MikroORM-SQL-Injection-Exploit-Framework

PoC tool for CVE-2026-44680 affecting MikroORM ≤7.0.13. Exploits JSON path injection to extract database contents via UNION-based attacks. Features…

PoC tool for CVE-2026-44680 affecting MikroORM ≤7.0.13. Exploits JSON path injection to extract database contents via UNION-based attacks. Features…

R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…

Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…

Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.

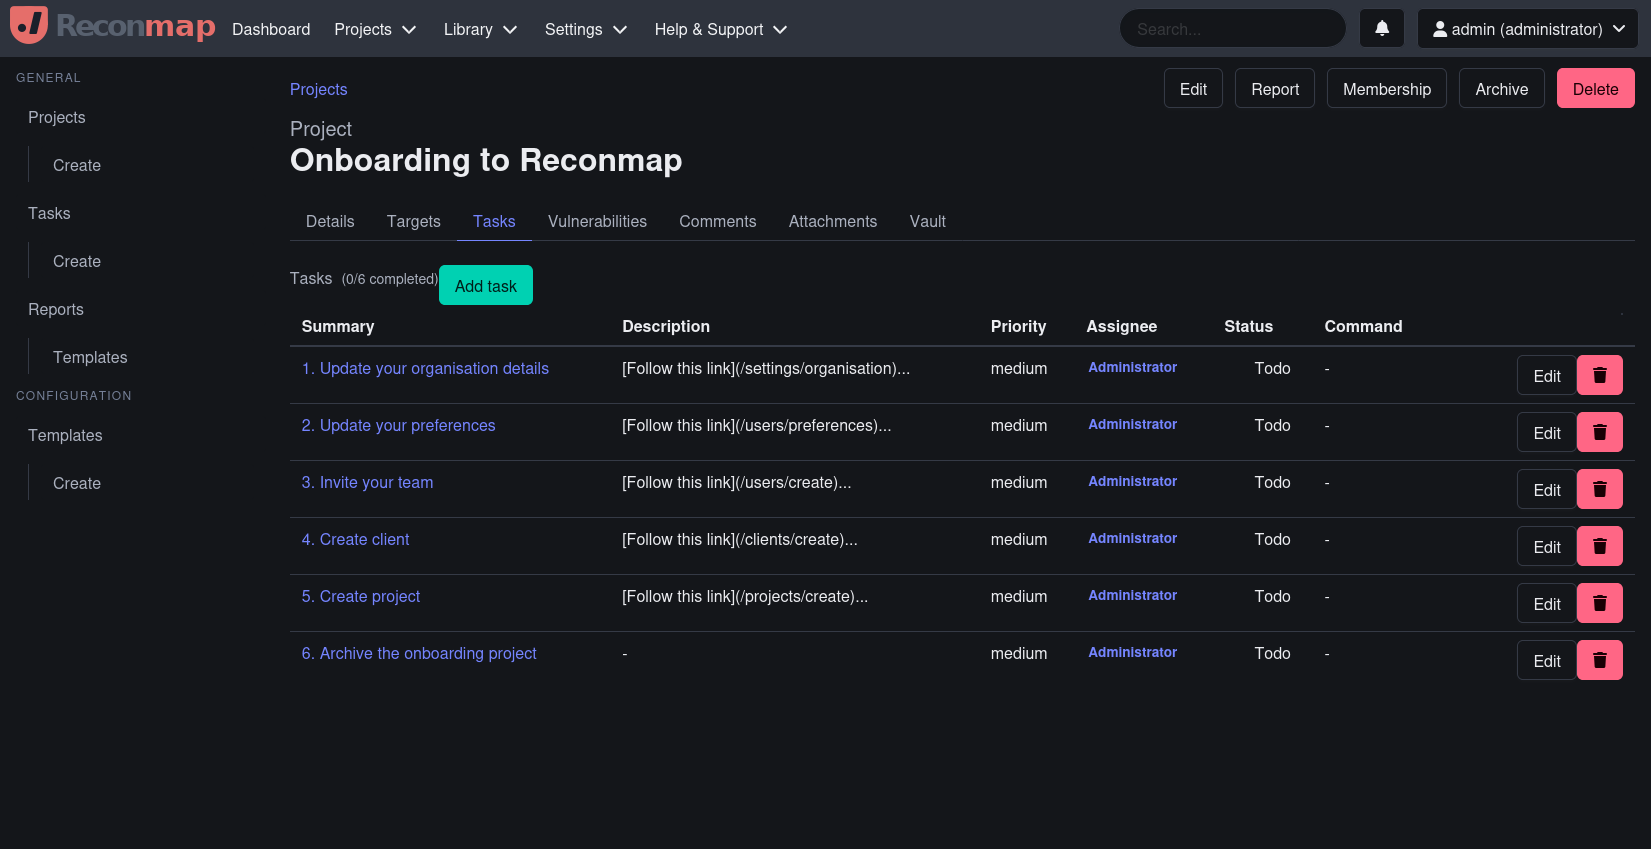
Reconmap is a collaboration-first security operations platform for infosec teams and MSSPs, enabling end‑to‑end engagement management, from…

Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…

Model Context Protocol server for autonomous vulnerability discovery

Python exploit for CVE-2019-9053 targeting a SQL injection vulnerability in CMS Made Simple. Automates time-based blind SQLi to extract admin…

An isolated Vagrant testbed designed to simulate a complete attack chain: Initial access via the Nginx heap buffer overflow (CVE-2026-42533) followed…