

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
67 results
kubesploit preview

kubesploit

GitHubcyberark/kubesploit

Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.
command-and-controlcontainer-escapecontainer-security+8
1.2k
1 year ago
CobaltStrike-Toolset preview

CobaltStrike-Toolset

GitHubqax-a-team/cobaltstrike-toolset

Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on
command-and-controlexploit-frameworkslateral-movement+8
5907 years ago
overlord preview

overlord

GitHubqsecure-labs/overlord

Python-based CLI for automated red team infrastructure deployment on AWS and Digital Ocean, with modular support for C2, email servers, HTTP…
cloud-securitycommand-and-controlemail-security+3
6364 years ago
DBC2 preview

DBC2

GitHubarno0x/dbc2

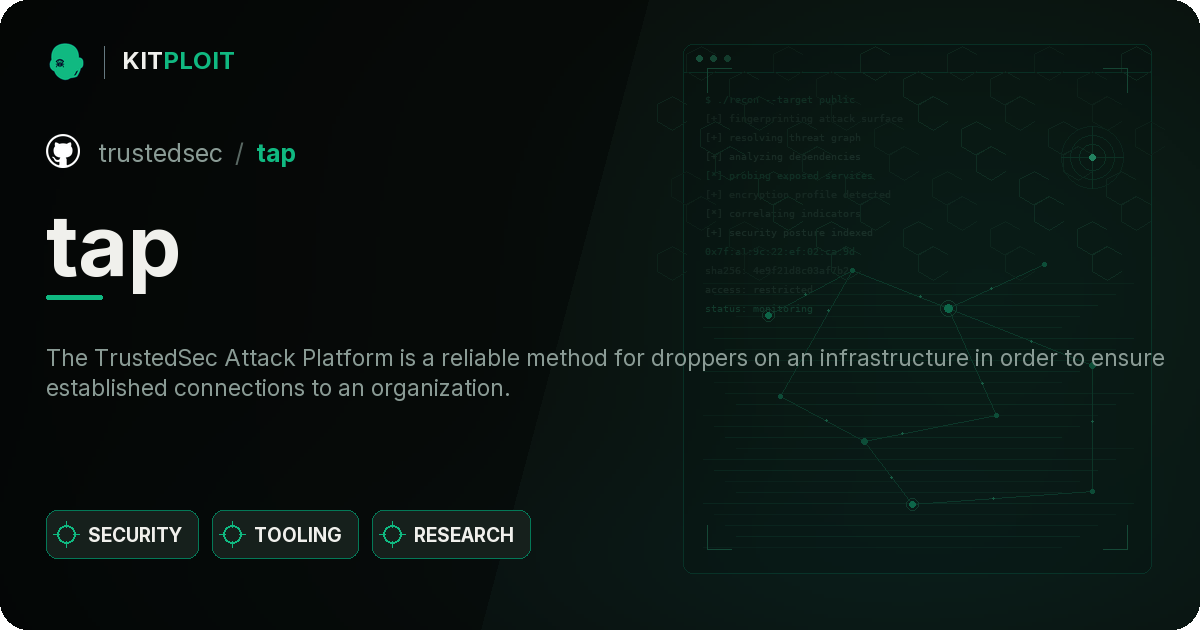
DBC2 (DropboxC2) is a modular post-exploitation tool, composed of an agent running on the victim's machine, a controler, running on any machine,…
command-and-controlpayload-generationpenetration-testing-frameworks+2
3269 years ago
tap preview

tap

GitHubtrustedsec/tap

The TrustedSec Attack Platform is a reliable method for droppers on an infrastructure in order to ensure established connections to an organization.

command-and-controlpenetration-testing-frameworkspersistence-mechanisms+3
5043 years ago
FruityC2 preview

FruityC2

GitHubxtr4nge/fruityc2

FruityC2 is a post-exploitation (and open source) framework based on the deployment of agents on compromised machines. Agents are managed from a web…
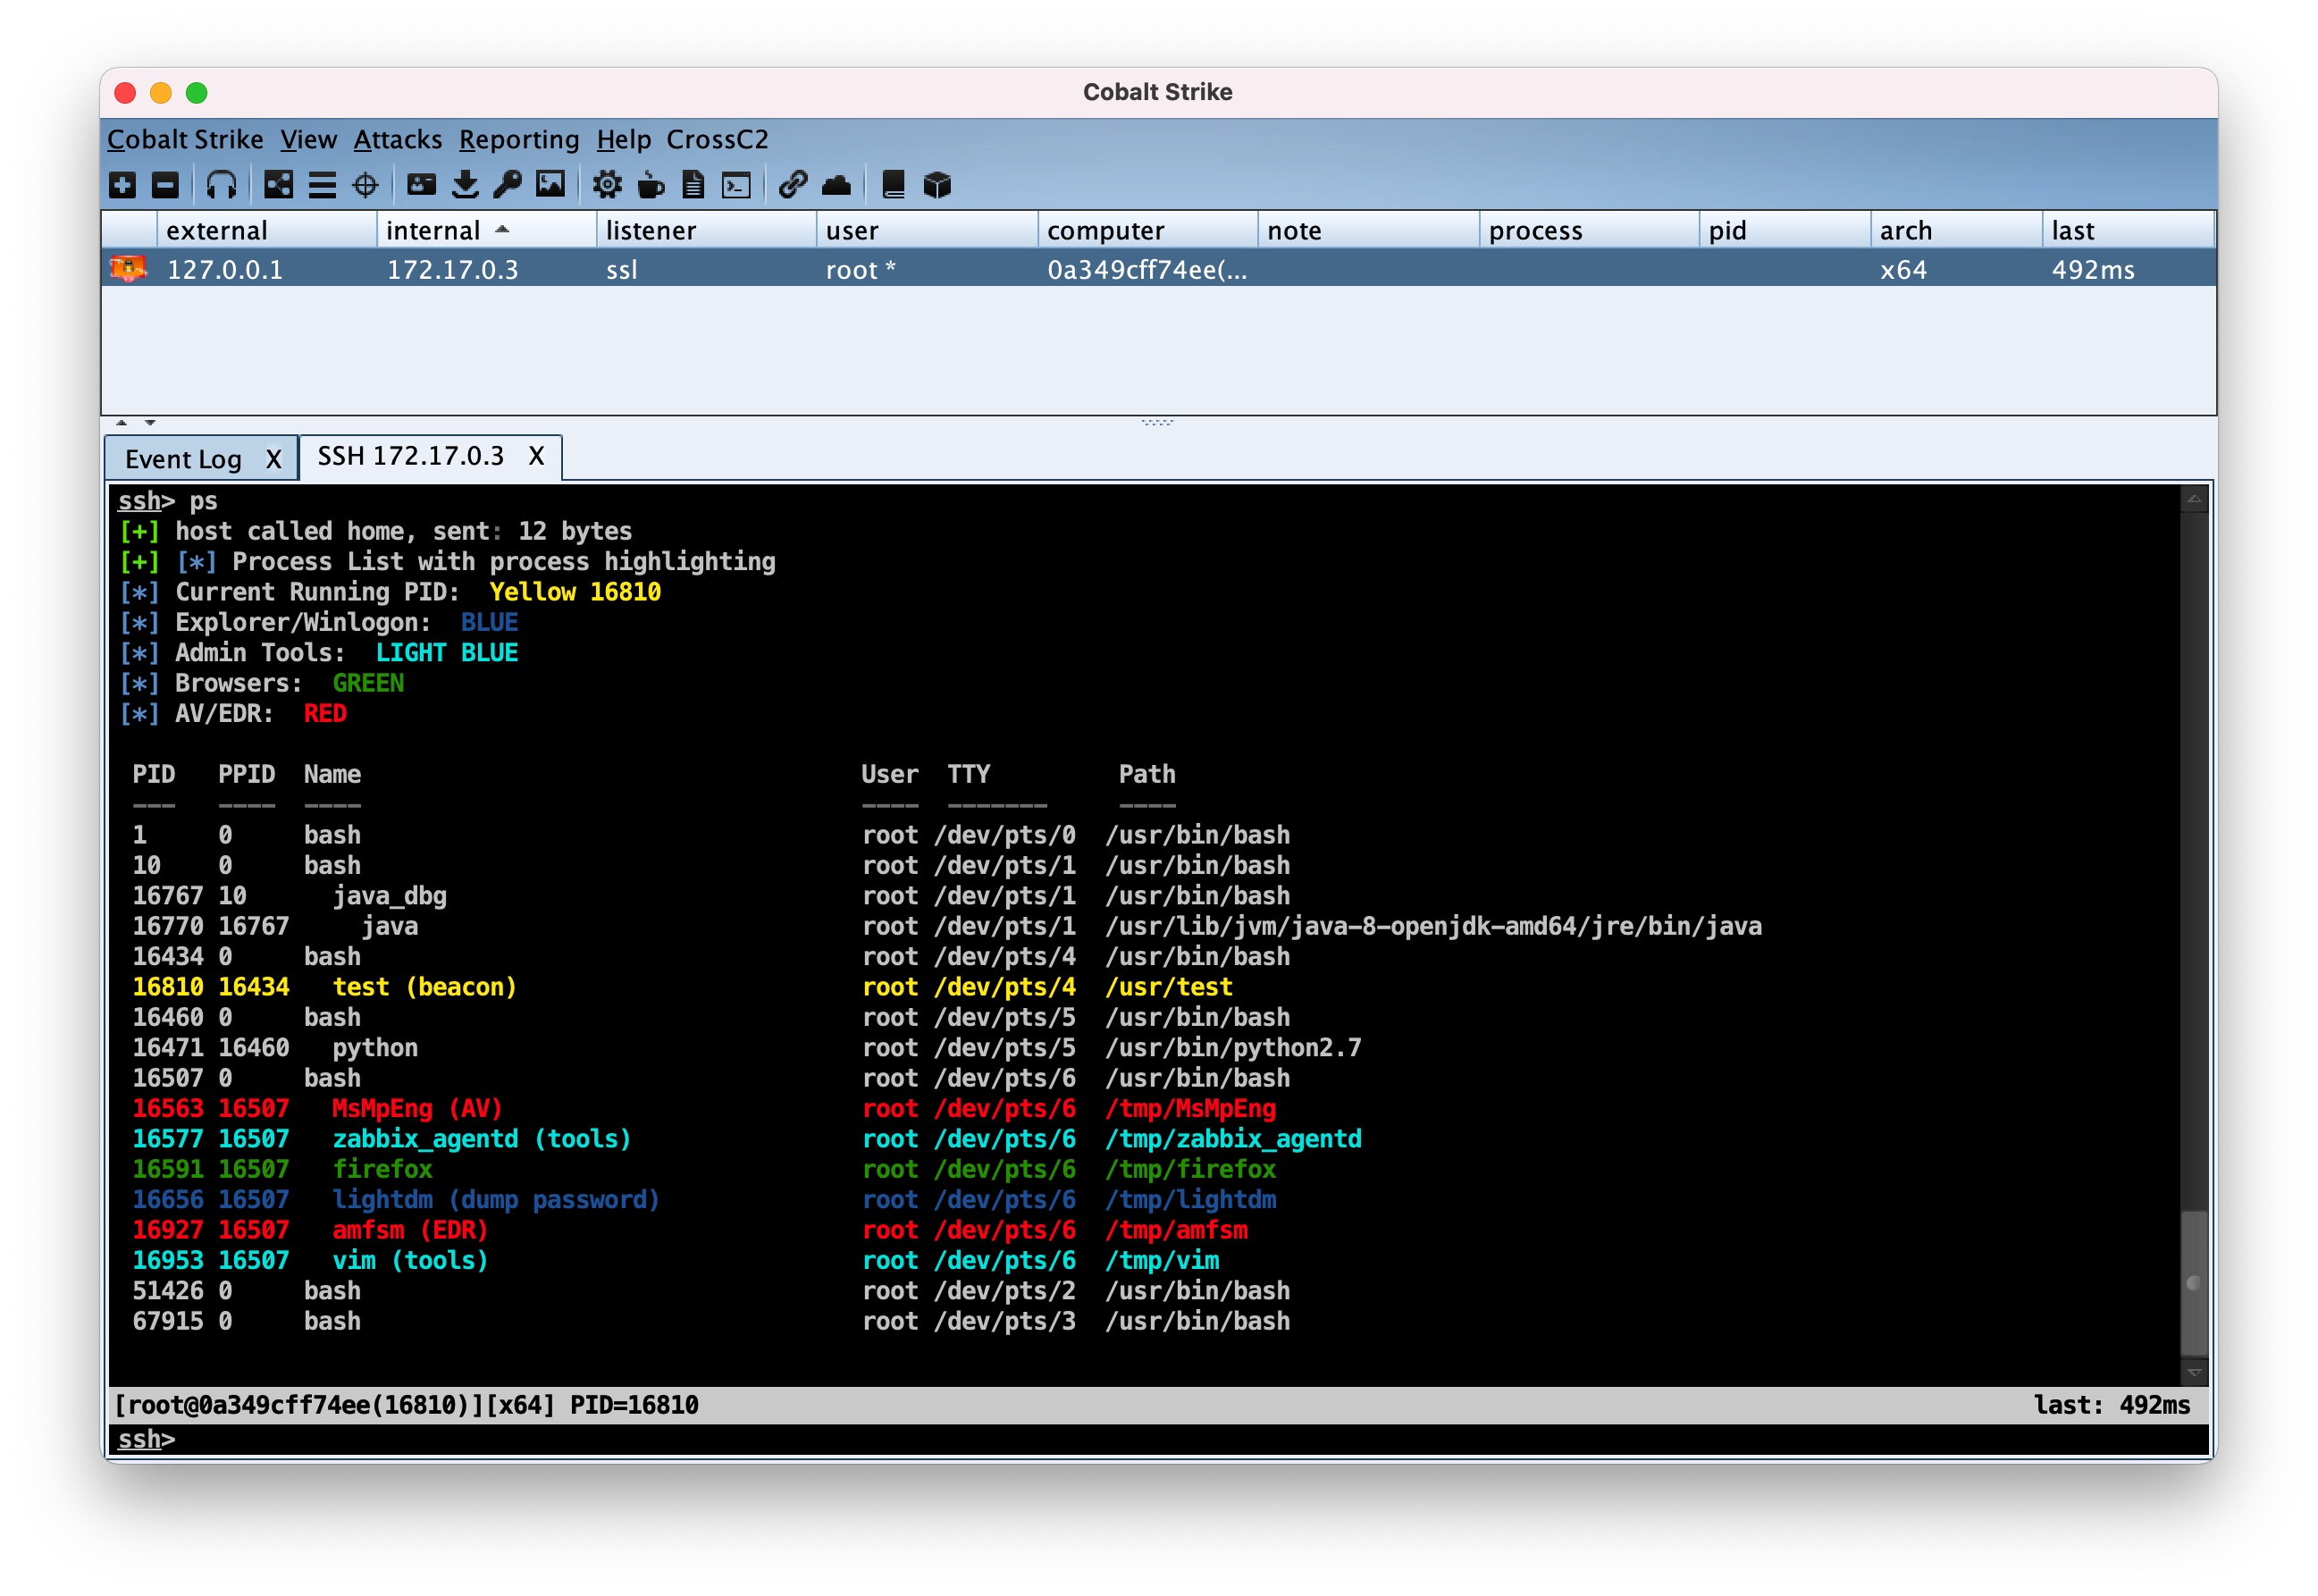
command-and-controlexploit-frameworkspayload-development+4
2068 years ago
CrossC2Kit preview

CrossC2Kit

GitHubcrossc2/crossc2kit

CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
command-and-controlexploit-frameworksinformation-gathering+7
2293 years ago
pown preview

pown

GitHubpownjs/pown

Pown.js is a security testing an exploitation toolkit built on top of Node.js and NPM.
exploit-frameworkspenetration-testing-frameworksscripting-automation+1
2593 years ago
msploitego preview

msploitego

GitHubshizzz477/msploitego

Pentesting suite for Maltego based on data in a Metasploit database

exploit-frameworksinformation-gatheringnetwork-mapping+6
1488 years ago
bowcaster preview

bowcaster

GitHubzcutlip/bowcaster

Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…

binary-exploitationembedded-systems-securityexploitation+6
1388 years ago
msfconsole-termux preview

msfconsole-termux

GitHubjas502n/msfconsole-termux

How To Install Metasploit-Table on the Android Termux

educationexploit-frameworkspenetration-testing-frameworks+1
588 years ago
RedRoot preview

RedRoot

GitHubagampreet-singh/redroot

RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
ctfexploit-frameworksfuzzing+9
1713 days ago
CVE-2024-38472 preview

CVE-2024-38472

GitHubabdurahmon3236/cve-2024-38472

Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.

command-and-controlexploit-frameworkslateral-movement+6
42 years ago
CVE-2026-31431-Metasploit-exploit preview

CVE-2026-31431-Metasploit-exploit

GitHubadityasingh108/cve-2026-31431-metasploit-exploit

Automated Metasploit post-exploitation module for CVE-2026-31431 ("Copy Fail"). Weaponizes a deterministic logic flaw in the Linux kernel AF_ALG…

binary-exploitationeducationexploitation+7
25 months ago
MagicArch preview

MagicArch

GitLabmagicbytes/magicarch

MagicArch is a comprehensive post-installation script built with Ansible, designed to transform a basic Arch Linux installation into a fully equipped…
exploit-frameworksforensicsinformation-gathering+8
22 years ago
Cusimanse preview

Cusimanse

GitHubopposum0112/cusimanse

Composable research-contract and YAML-recipe framework for agent-operated security experiments on disposable compute
ai-securitydefensive-toolsdynamic-analysis-sandboxing+9
1 month ago
redStack preview

redStack

GitHubdevzero-security/redstack

Terraform-deployed red team operator lab on AWS: Mythic, Sliver, and Adaptix C2 behind a production-style Apache redirector, with Kali/Windows hosts…

cloud-infrastructure-securitycommand-and-controleducation+8
2861 month ago
caldera-agent preview
Archived

caldera-agent

GitHubmitre/caldera-agent

Windows service agent for CALDERA adversary emulation platform. Installed on target computers to communicate with the CALDERA server, enabling…

command-and-controllateral-movementpayload-generation+3
208 years ago
Previous1234Next