
PowerSploit
 zerodaylab/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
command-and-controldata-exfiltrationexploit-frameworks+7
241
zerodaylab/powersploitPowerSploit - A PowerShell Post-Exploitation Framework
 chopicalqui/kaliintelligencesuite
Automated intelligence-gathering framework that orchestrates Kali Linux tools and public APIs to collect, store, and analyze reconnaissance data for…
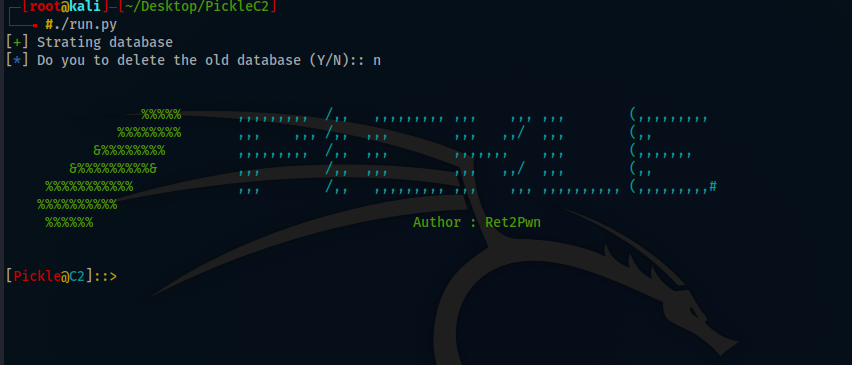 xret2pwn/picklec2
Encrypted C2 framework for post-exploitation and lateral movement, supporting PowerShell implants and custom modules for red team engagements.
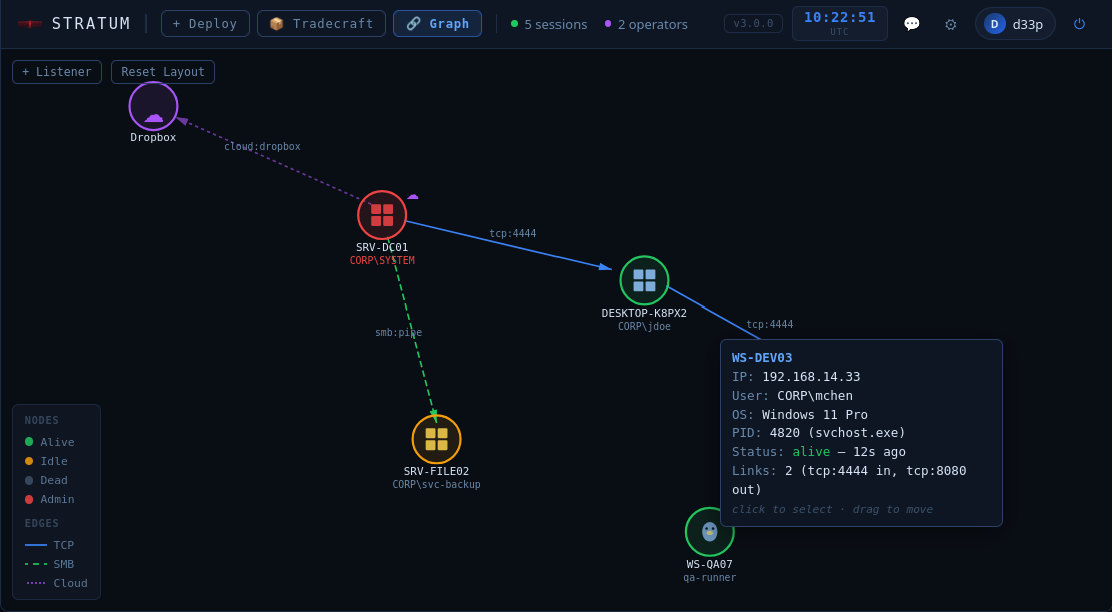 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
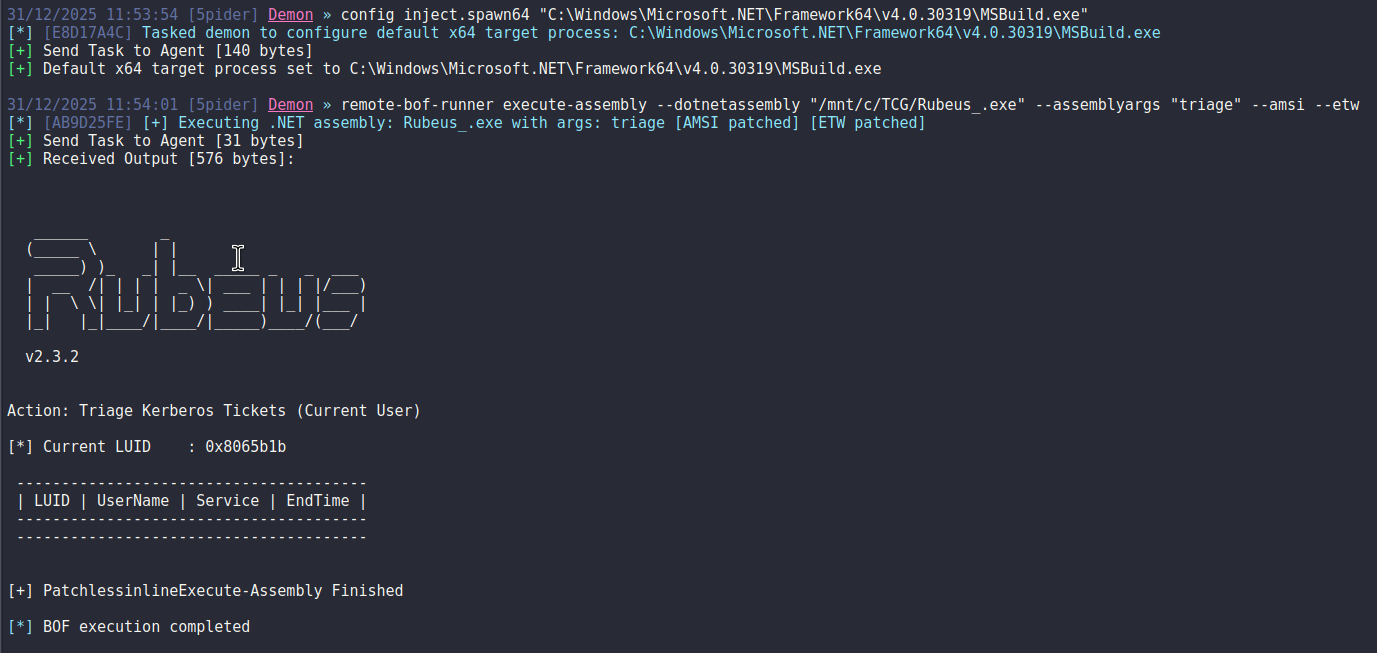 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 erarnitox/malvexc2
A simple C2 Framework written in modern C++
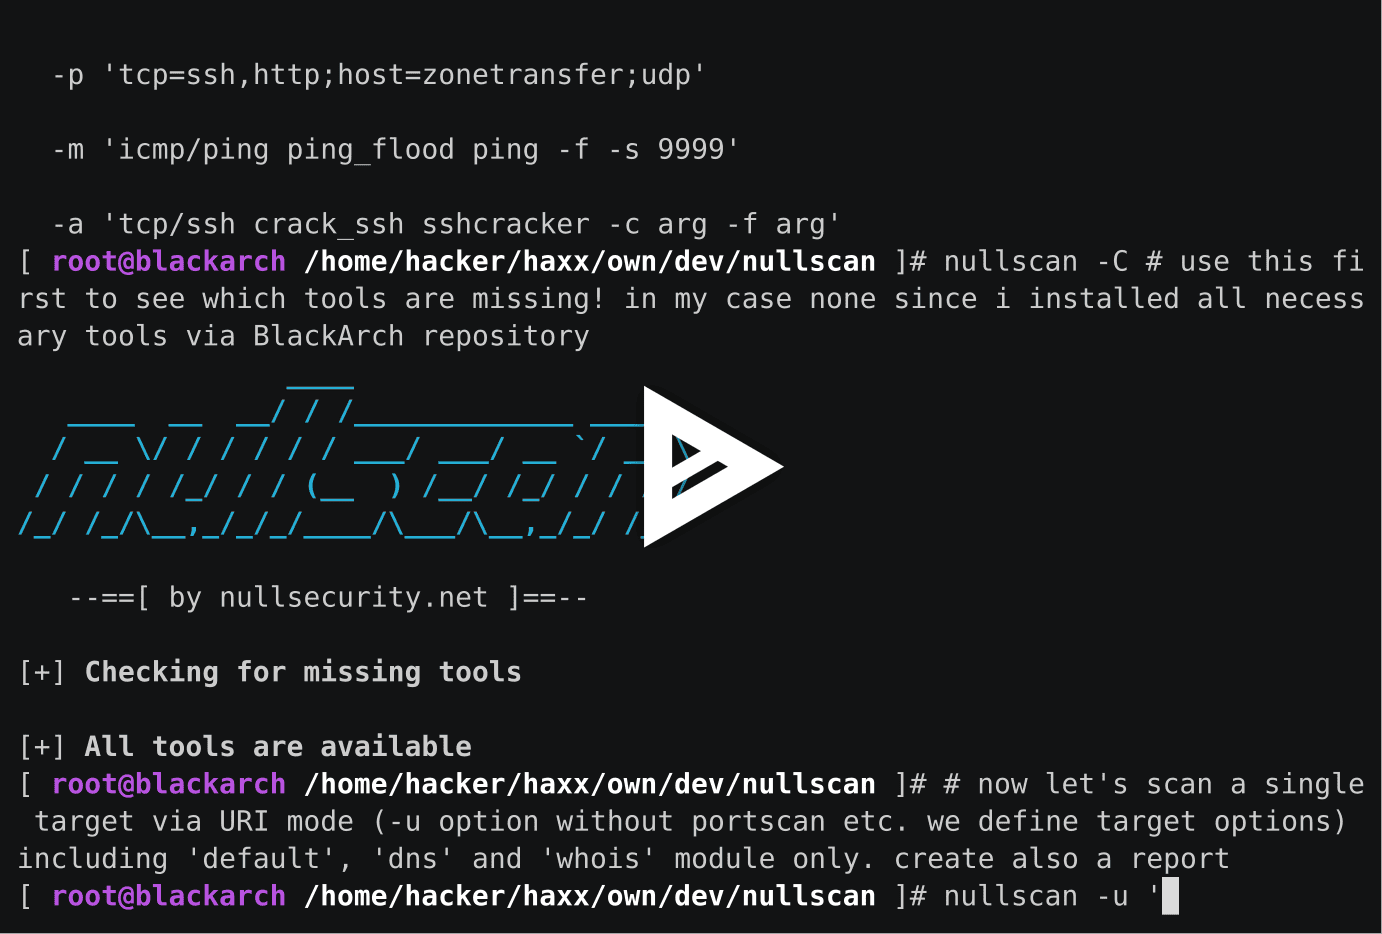 noptrix/nullscan
A modular framework designed to chain and automate security tests.
 leviticus-triage/chromsploit-framework
Advanced AI-Powered Exploitation Framework | CVE-2025-4664 & CVE-2025-2783 & CVE-2025-2857 & CVE-2025-30397 |
 yottaiq/jok3r
Jok3r - Network and Web Pentest Framework
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 flags-alt/abyss-c2
Full-stack C2 framework for IoT exploitation (CVE-2020-25078) with real-time web panel, multi-source target acquisition, vulnerability scanning,…
 razureink/fucker
Penetration testing framework with AI-driven decision engine
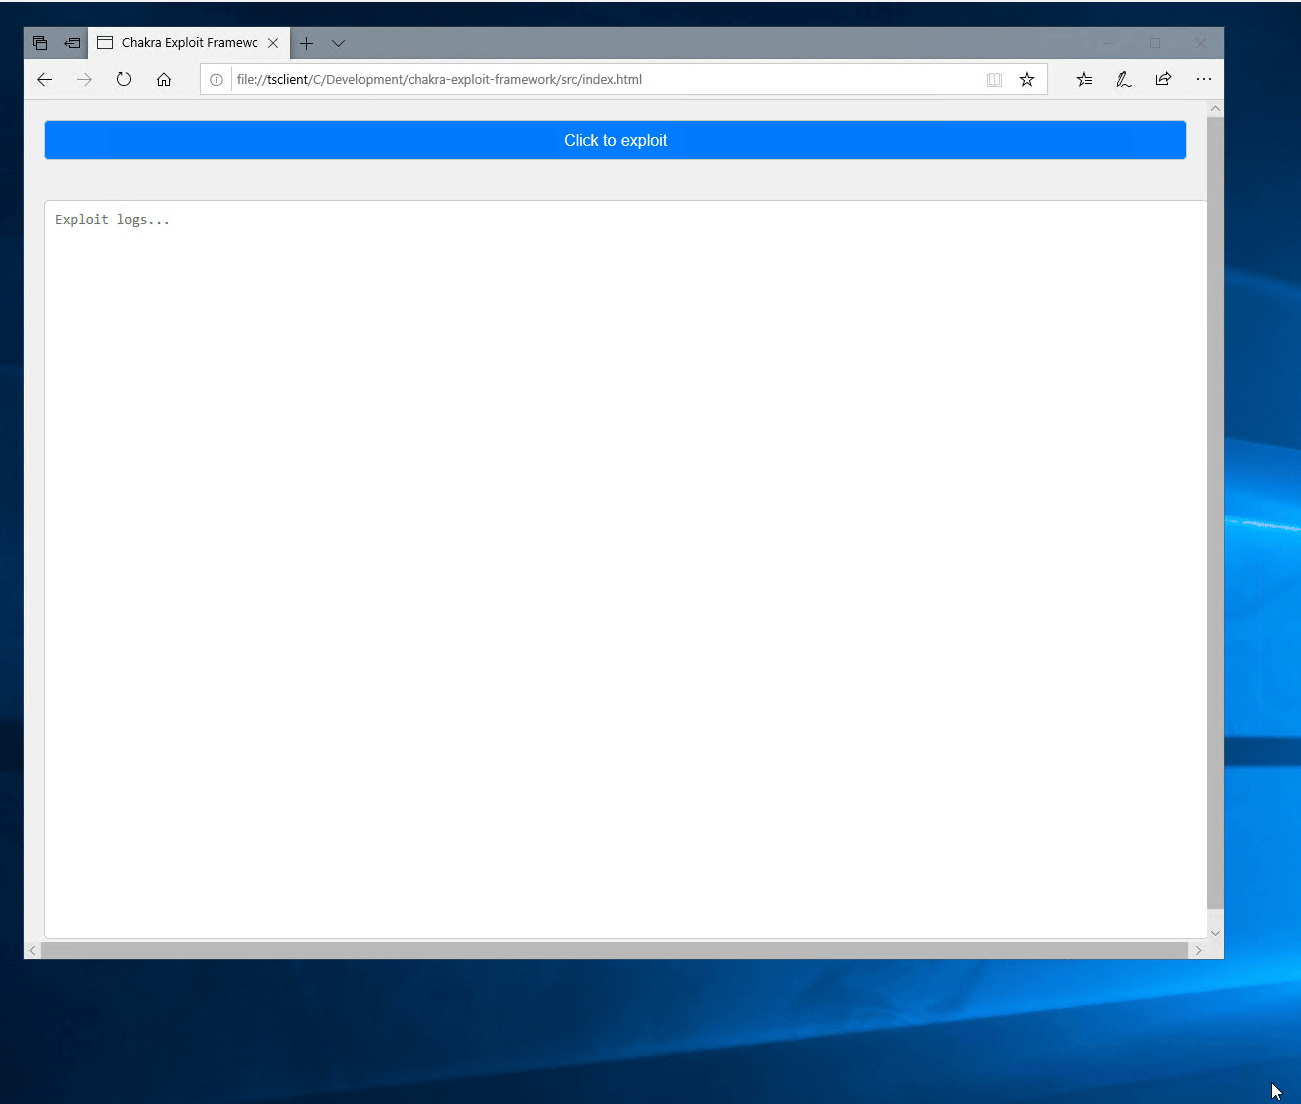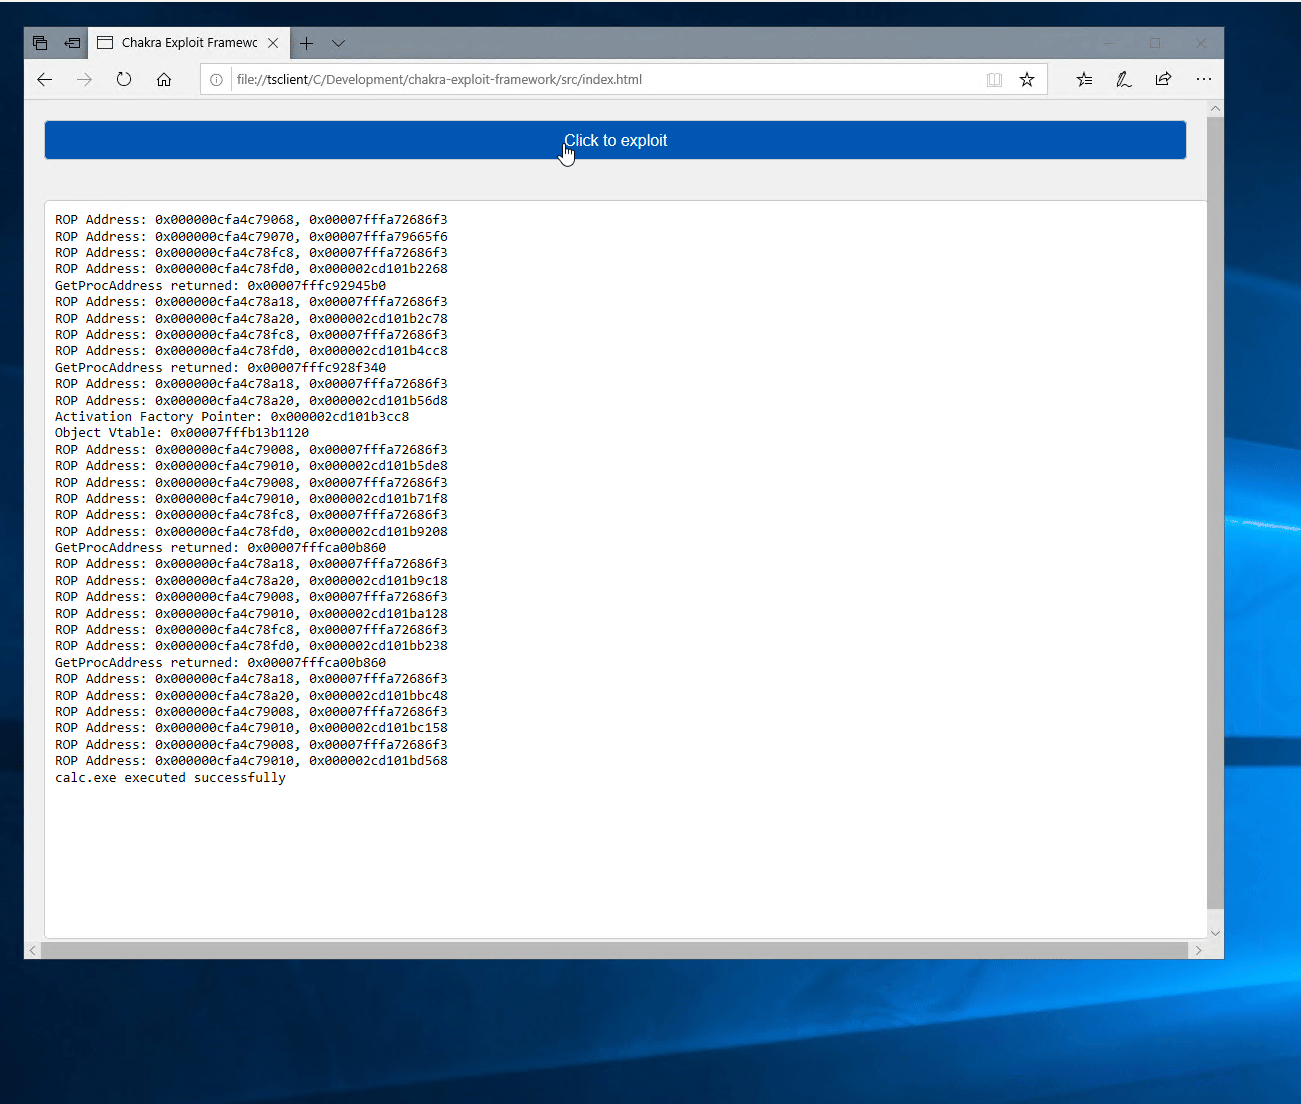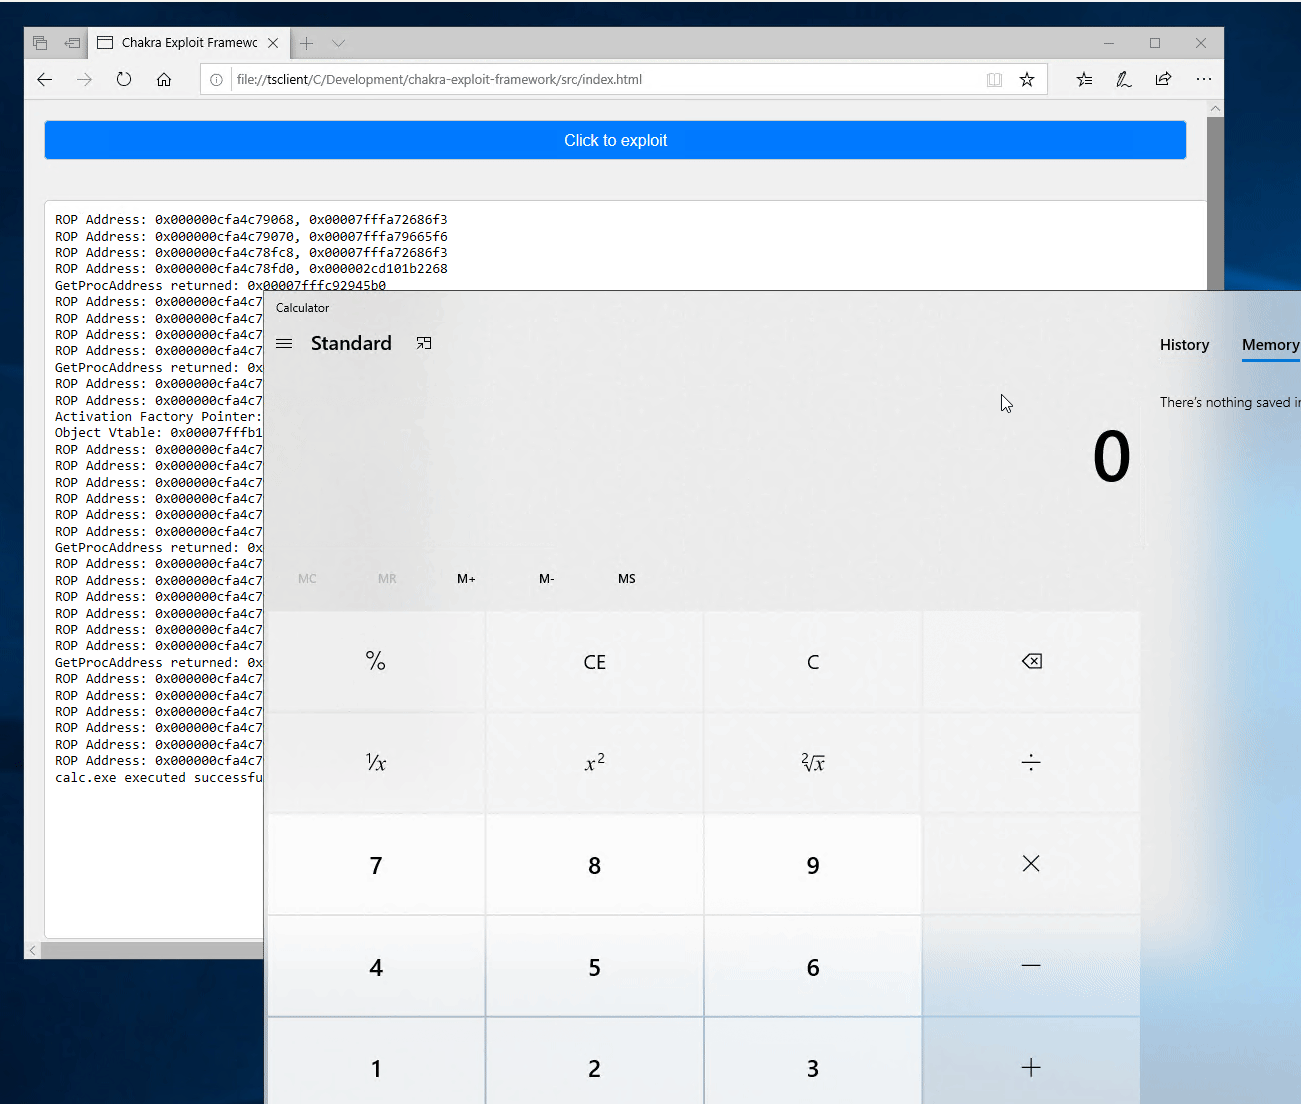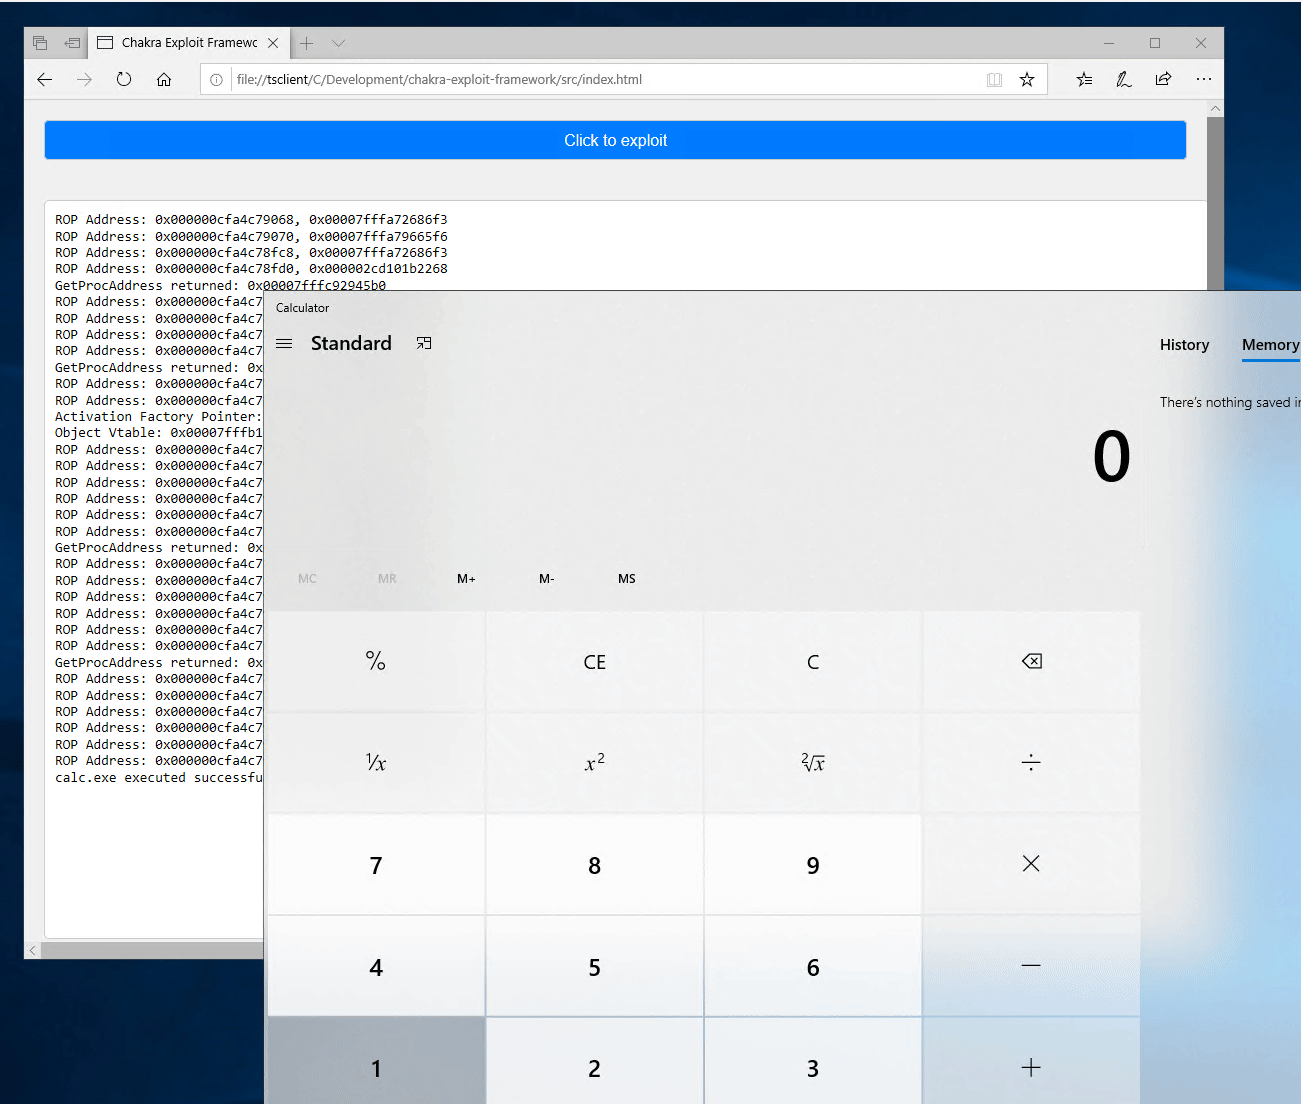 ntdelta/chakra-exploit-framework
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 cappricio-securities/socialengineering-templates
a SET framework templates
 jd0965199-oss/ethibench
Evaluation framework for AI penetration testing agents that measures validated vulnerability discovery using LLM-based semantic matching, bipartite…