
flounder
 adshao/flounder
Autonomous white-hat security auditor for AI-driven code review, bug bounty research, exploit construction, and execution-grounded verification.
ai-securitycode-analysisdynamic-analysis-sandboxing+5
525
adshao/flounderAutonomous white-hat security auditor for AI-driven code review, bug bounty research, exploit construction, and execution-grounded verification.
 secdevops-cuse/cyberrange
The Open-Source AWS Cyber Range
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 fraunhofer-aisec/gallia
Extendable pentesting framework for automotive UDS interfaces, enabling reproducible scans, diagnostic trouble code reading, and post-processing via…
 n1ckdunn/exploitivator
Automate Metasploit scanning and exploitation
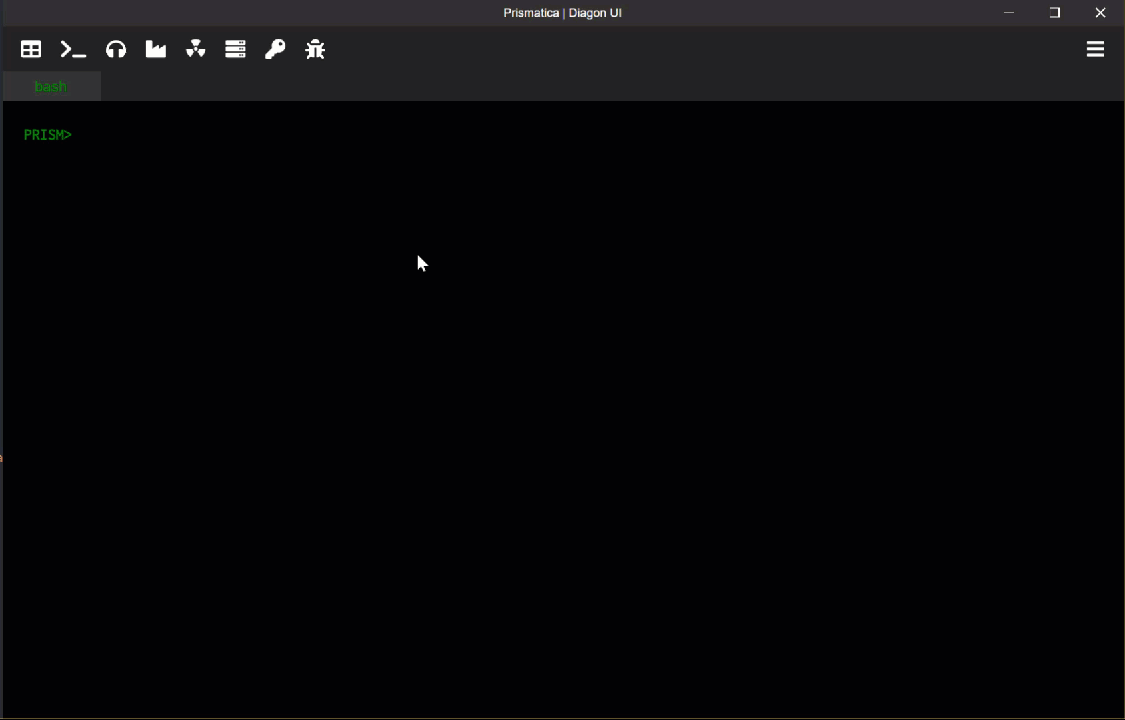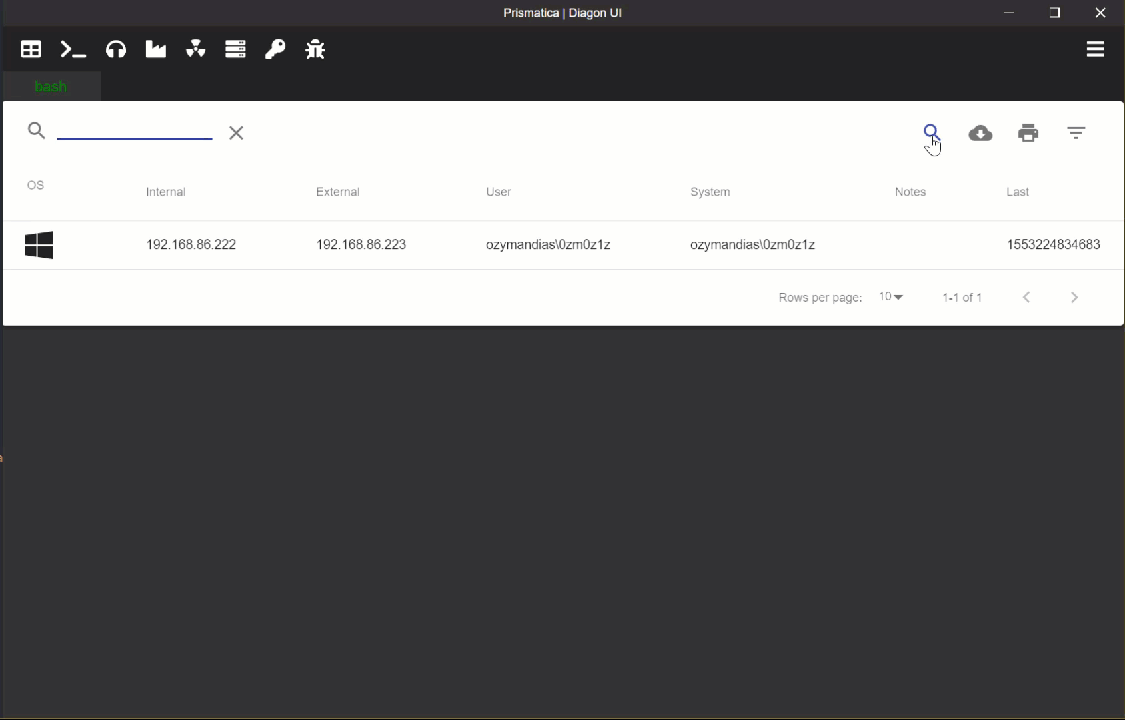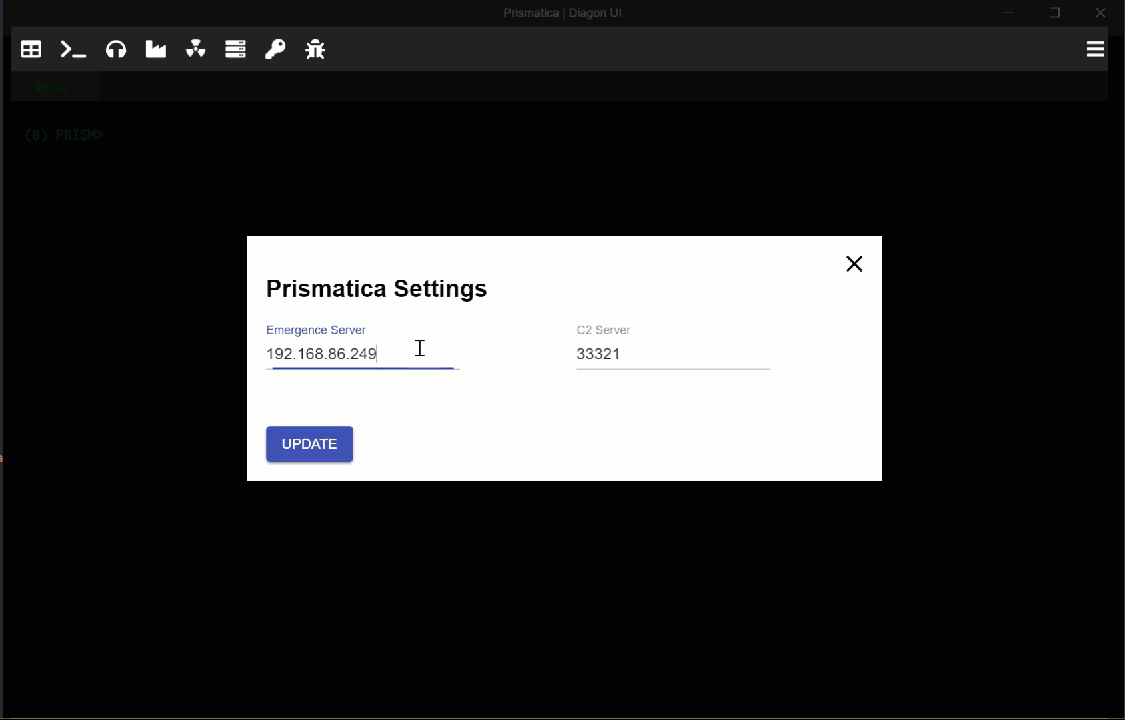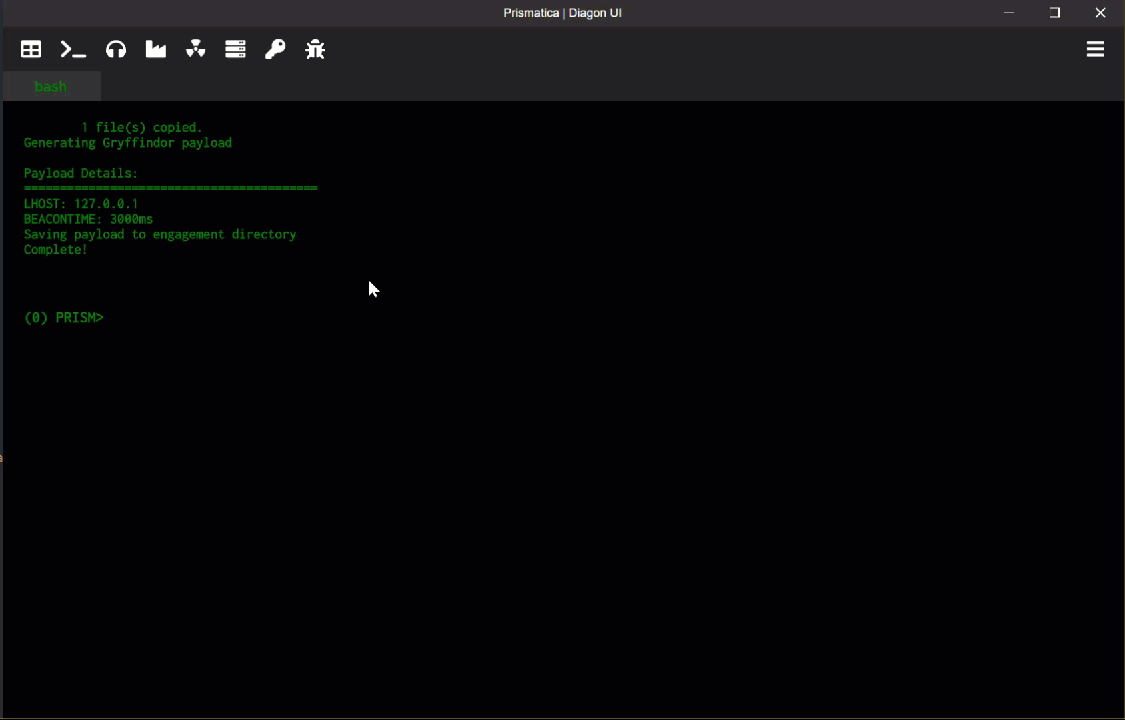 project-prismatica/prismatica
Responsive Command and Control System
 ikotler/hackersh
A free and open source command-line shell and scripting language designed especially for security testing
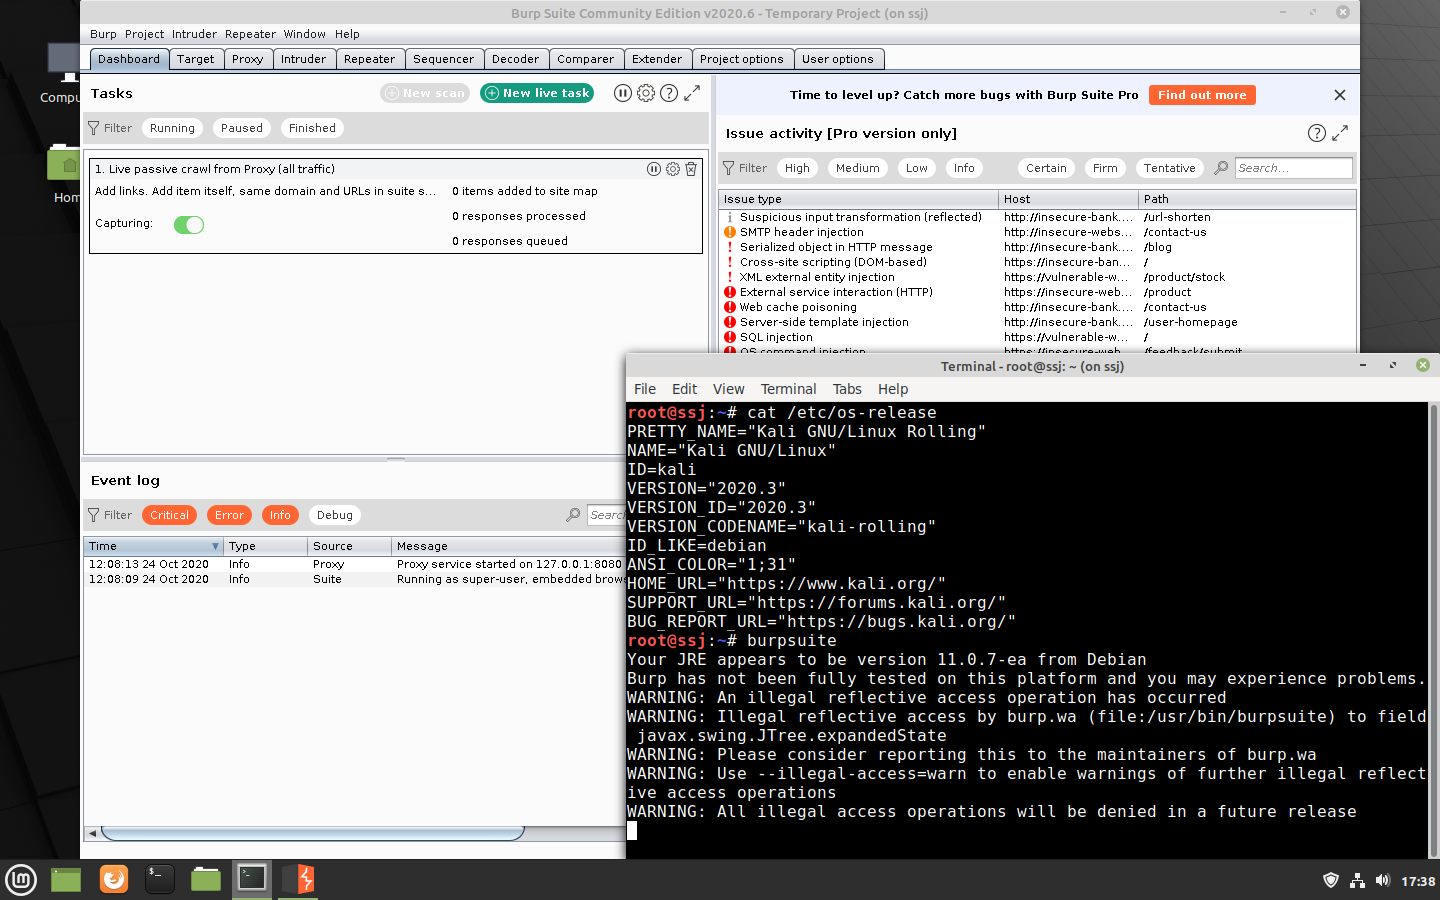 thirdbyte/ssj
Your everyday Linux distribution gone Super Saiyan.
 bishopfox/joro
A collaborative web exploitation framework.
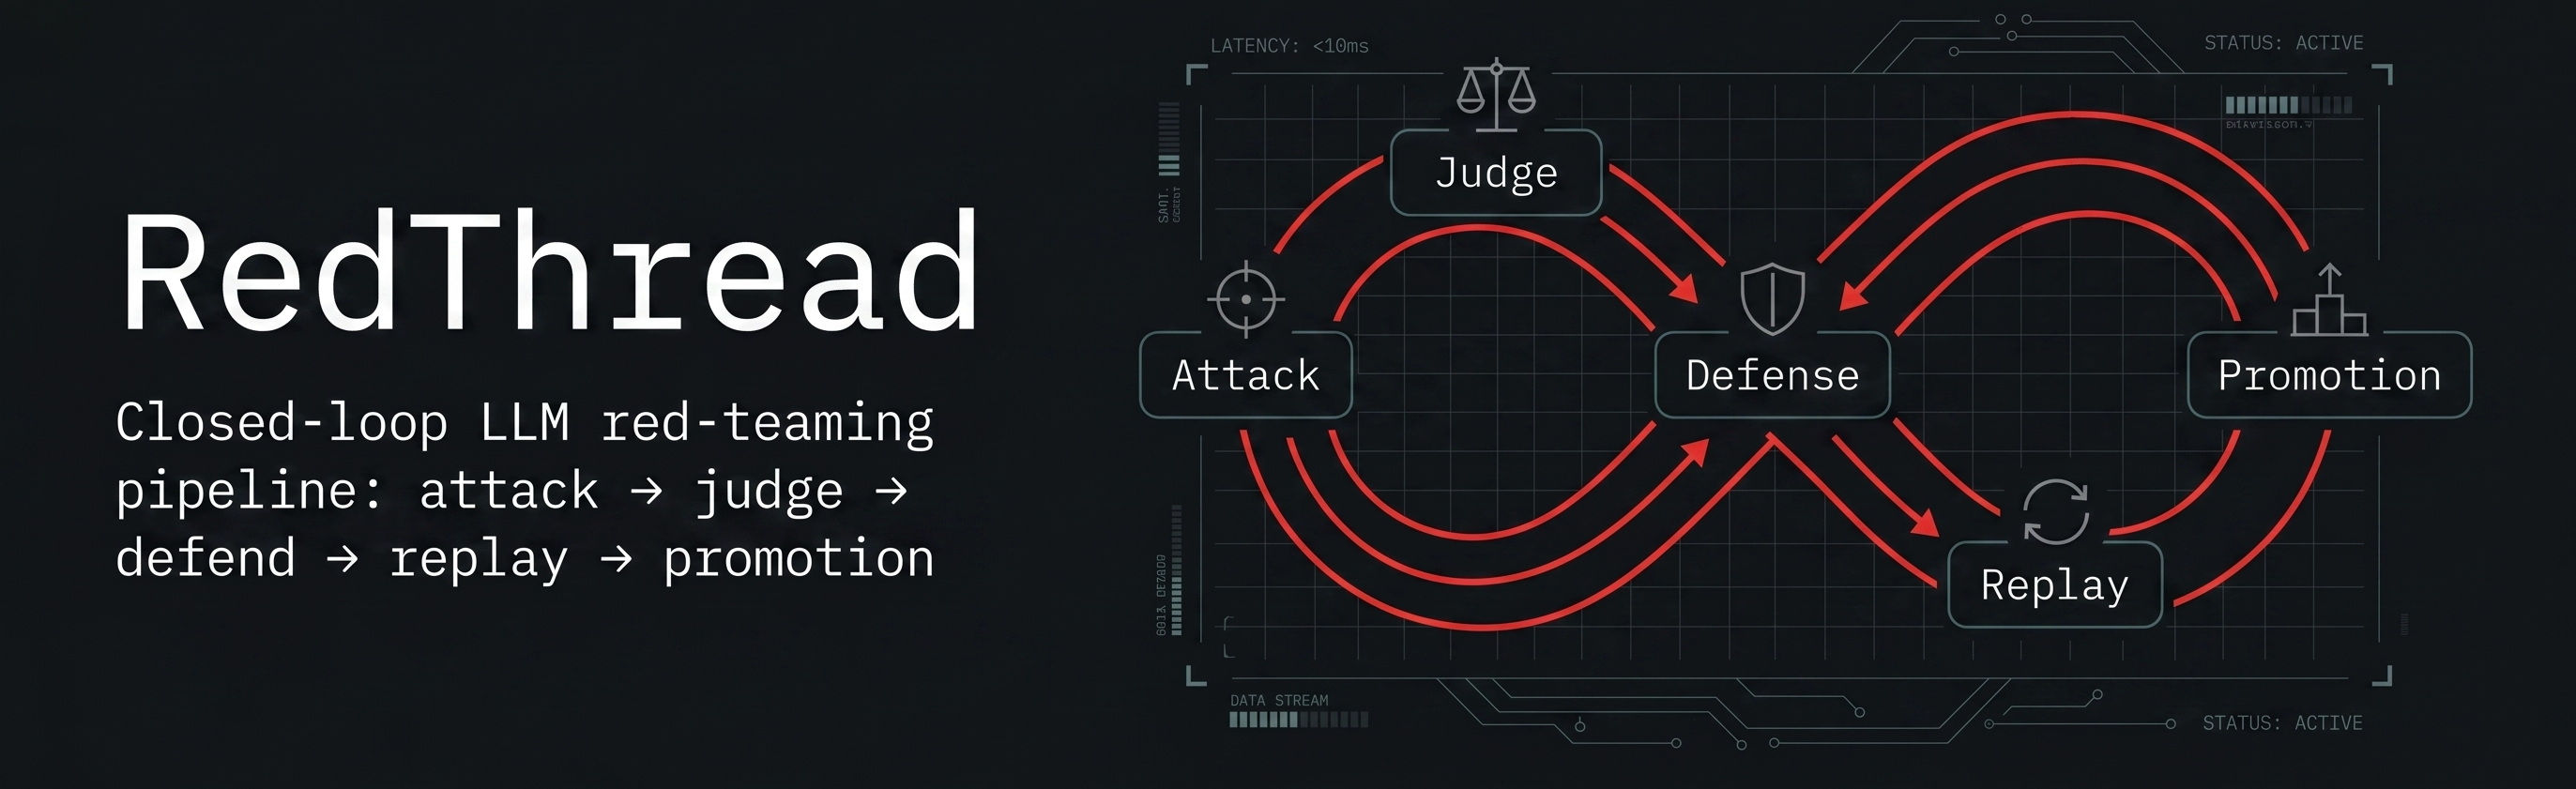 matheusht/redthread
An autonomous red-teaming engine for LLMs. RedThread manages the full security lifecycle: generating adversarial attacks, executing precision…
 blacksnufkin/cheshire
Adaptix C2 service plugin that drives LitterBox payload analysis from the operator UI.
 cogensec/gideon
Autonomous security operations agent for threat intelligence, vulnerability research, IOC analysis, and red teaming. Supports dual-mode operations…
 broskigx/oihk-pentesting
Autonomous multi-agent AI penetration-testing engine: a governed tool sandbox, an immutable evidence-and-validation gate, and a reproducible…
 stuxlabs/awe
adaptive agents for dynamic web penetration testing
 crussella0129/tricorne
a Fedora remix focused on pentesting and purple hat tooling
 cerberusmrxi/cerberus-react2shell-scanner-exploit
Elite exploitation toolkit for CVE-2025-55182 (React Server Components RCE). Async polymorphic payloads, advanced WAF/CDN bypass, proxy rotation,…
 h3x0v3rl0rd/cve-2019-9053
Python exploit for CVE-2019-9053 targeting a SQL injection vulnerability in CMS Made Simple. Automates time-based blind SQLi to extract admin…