
PEASS-ng
 peass-ng/peass-ng
PEASS - Privilege Escalation Awesome Scripts SUITE (with colors)
educationexploitationexploit-frameworks+7
peass-ng/peass-ngPEASS - Privilege Escalation Awesome Scripts SUITE (with colors)
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 mrwadams/stride-gpt
An AI-powered threat modeling tool that leverages OpenAI's GPT models to generate threat models for a given application based on the STRIDE…
 purpleailab/decepticon
Autonomous Hacking Agent for Red Team
 vxcontrol/pentagi
Fully autonomous AI Agents system capable of performing complex penetration testing tasks
 yogsec/hacking-tools
A curated list of penetration testing and ethical hacking tools, organized by category. This compilation includes tools from Kali Linux and other…
 s0ld13rr/pentestcode
Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…
 k3ystr0k3r/metis
Modular Python exploitation framework with a Metasploit-style console, auto-registering Exploit and Auxiliary modules, tri-state checks, and multiple…
 theporgs/exegol
Fully featured and community-driven hacking environment
 broskigx/oihk-pentesting
Autonomous multi-agent AI penetration-testing engine: a governed tool sandbox, an immutable evidence-and-validation gate, and a reproducible…
 kryptsec/oasis
Open-source AI security benchmarking CLI. Measure how AI models perform offensive security tasks with MITRE ATT&CK analysis and KSM scoring.
 youssefnoob003/sindrikit
A foundational C library for building operationally credible offensive capabilities
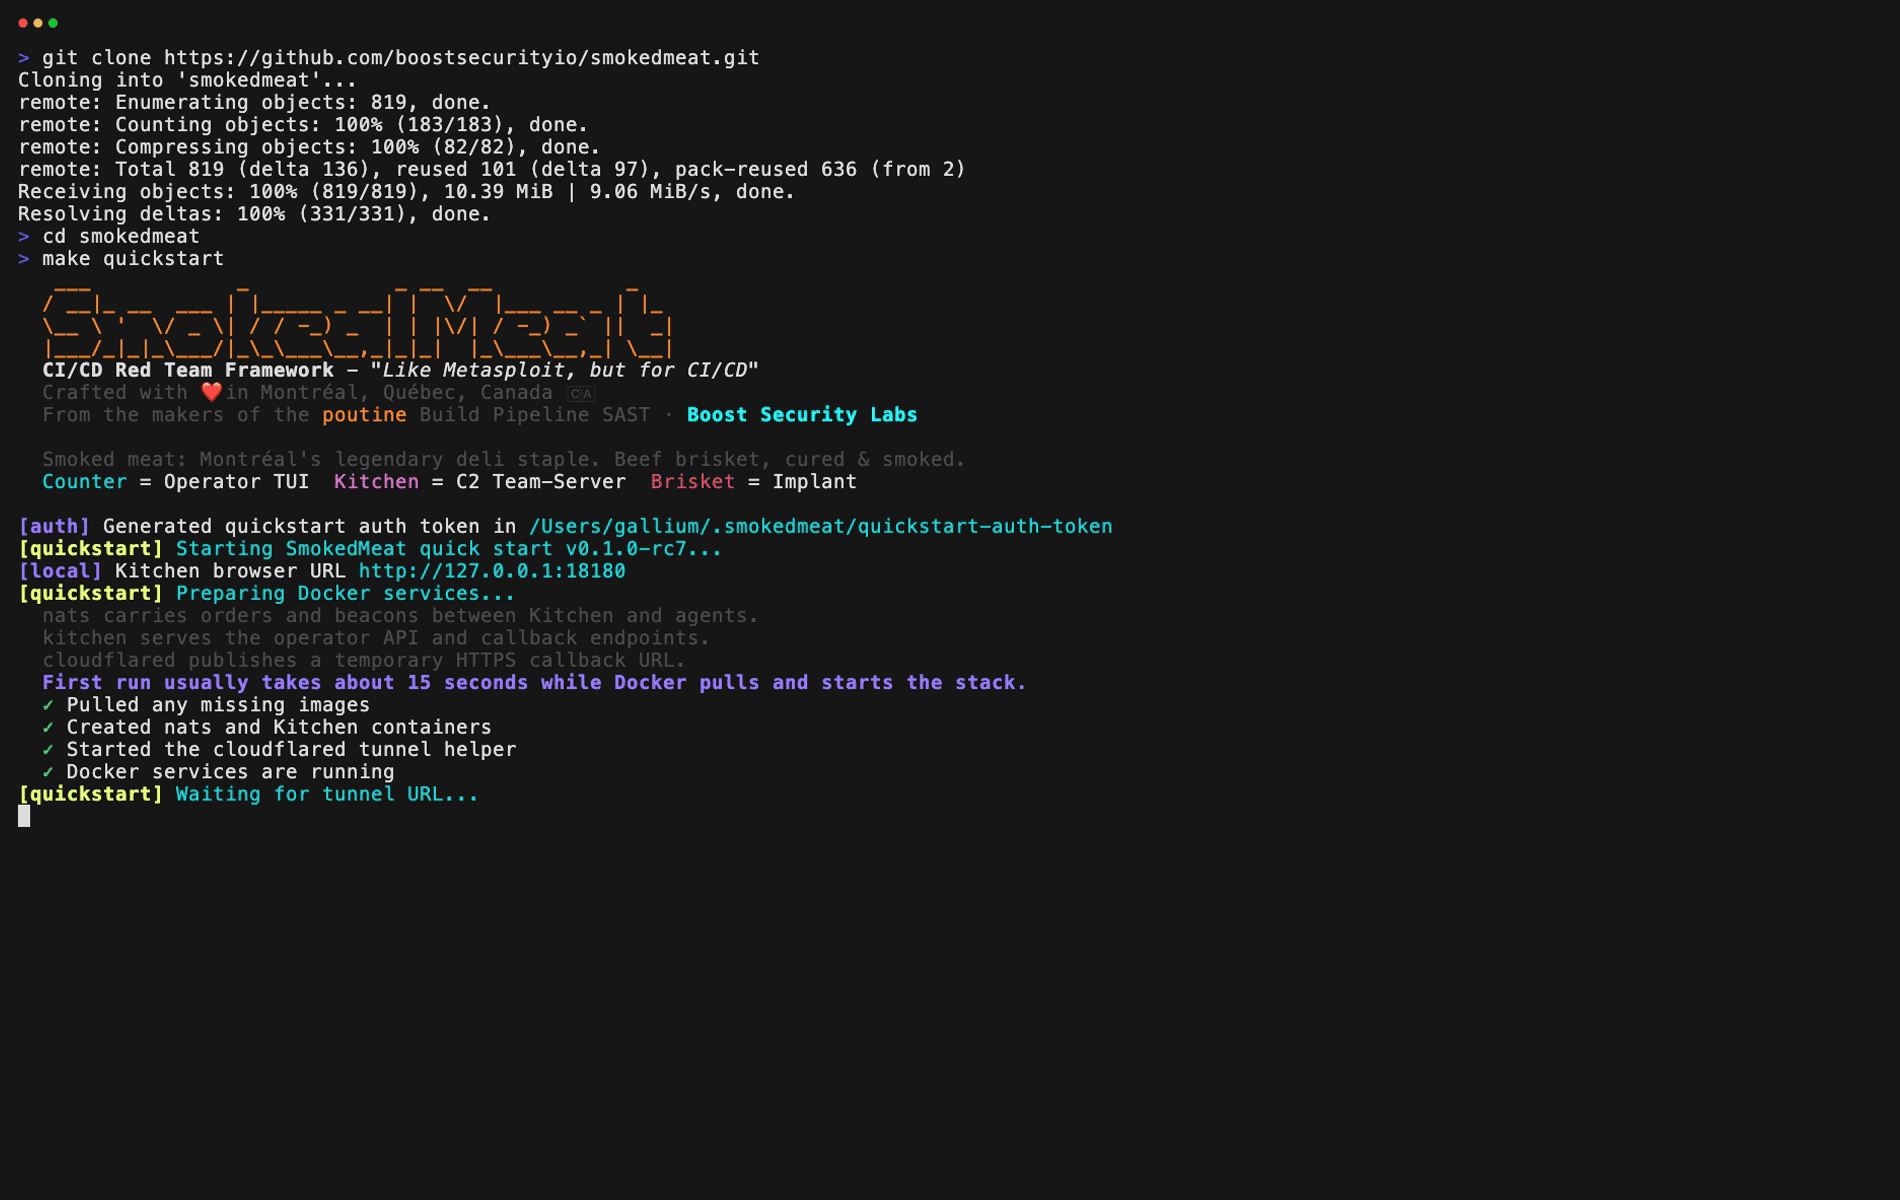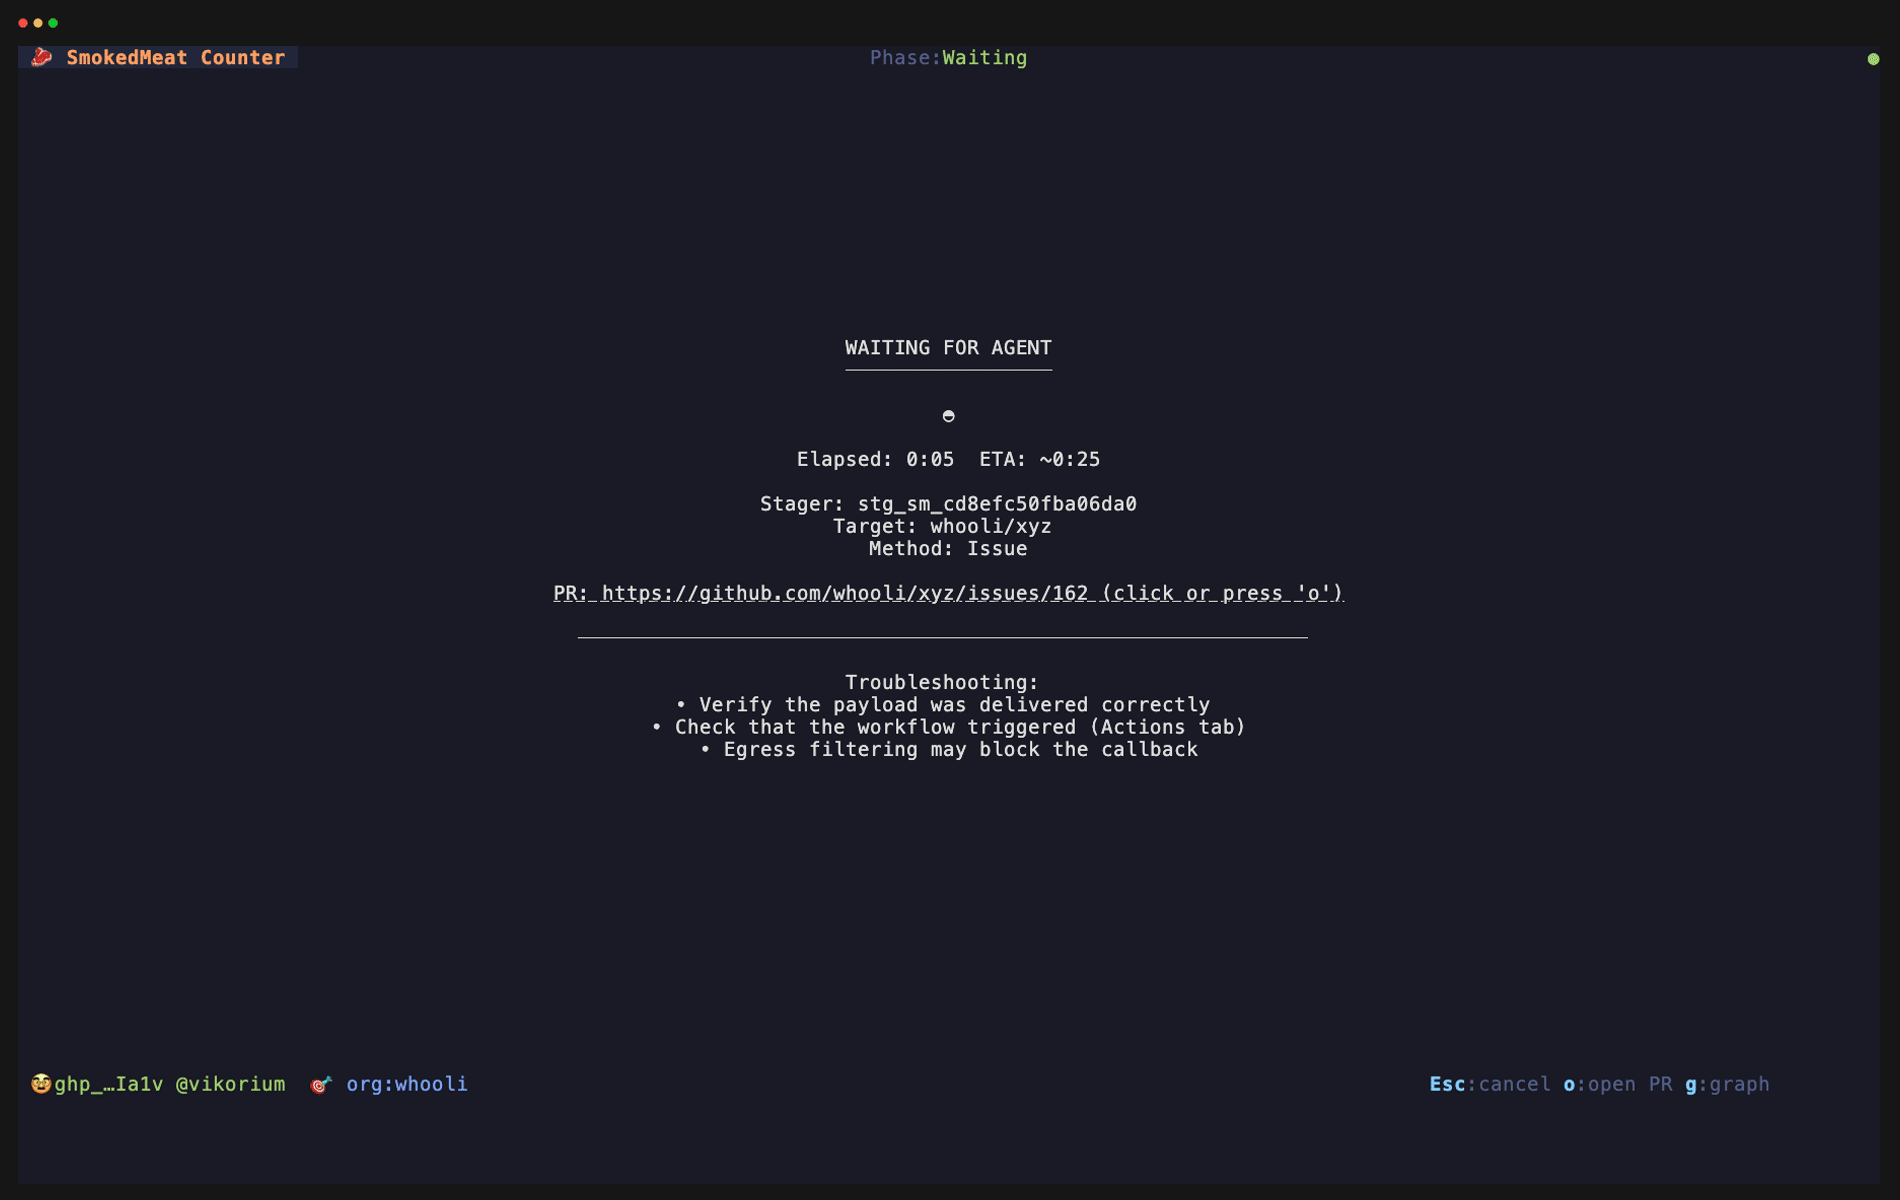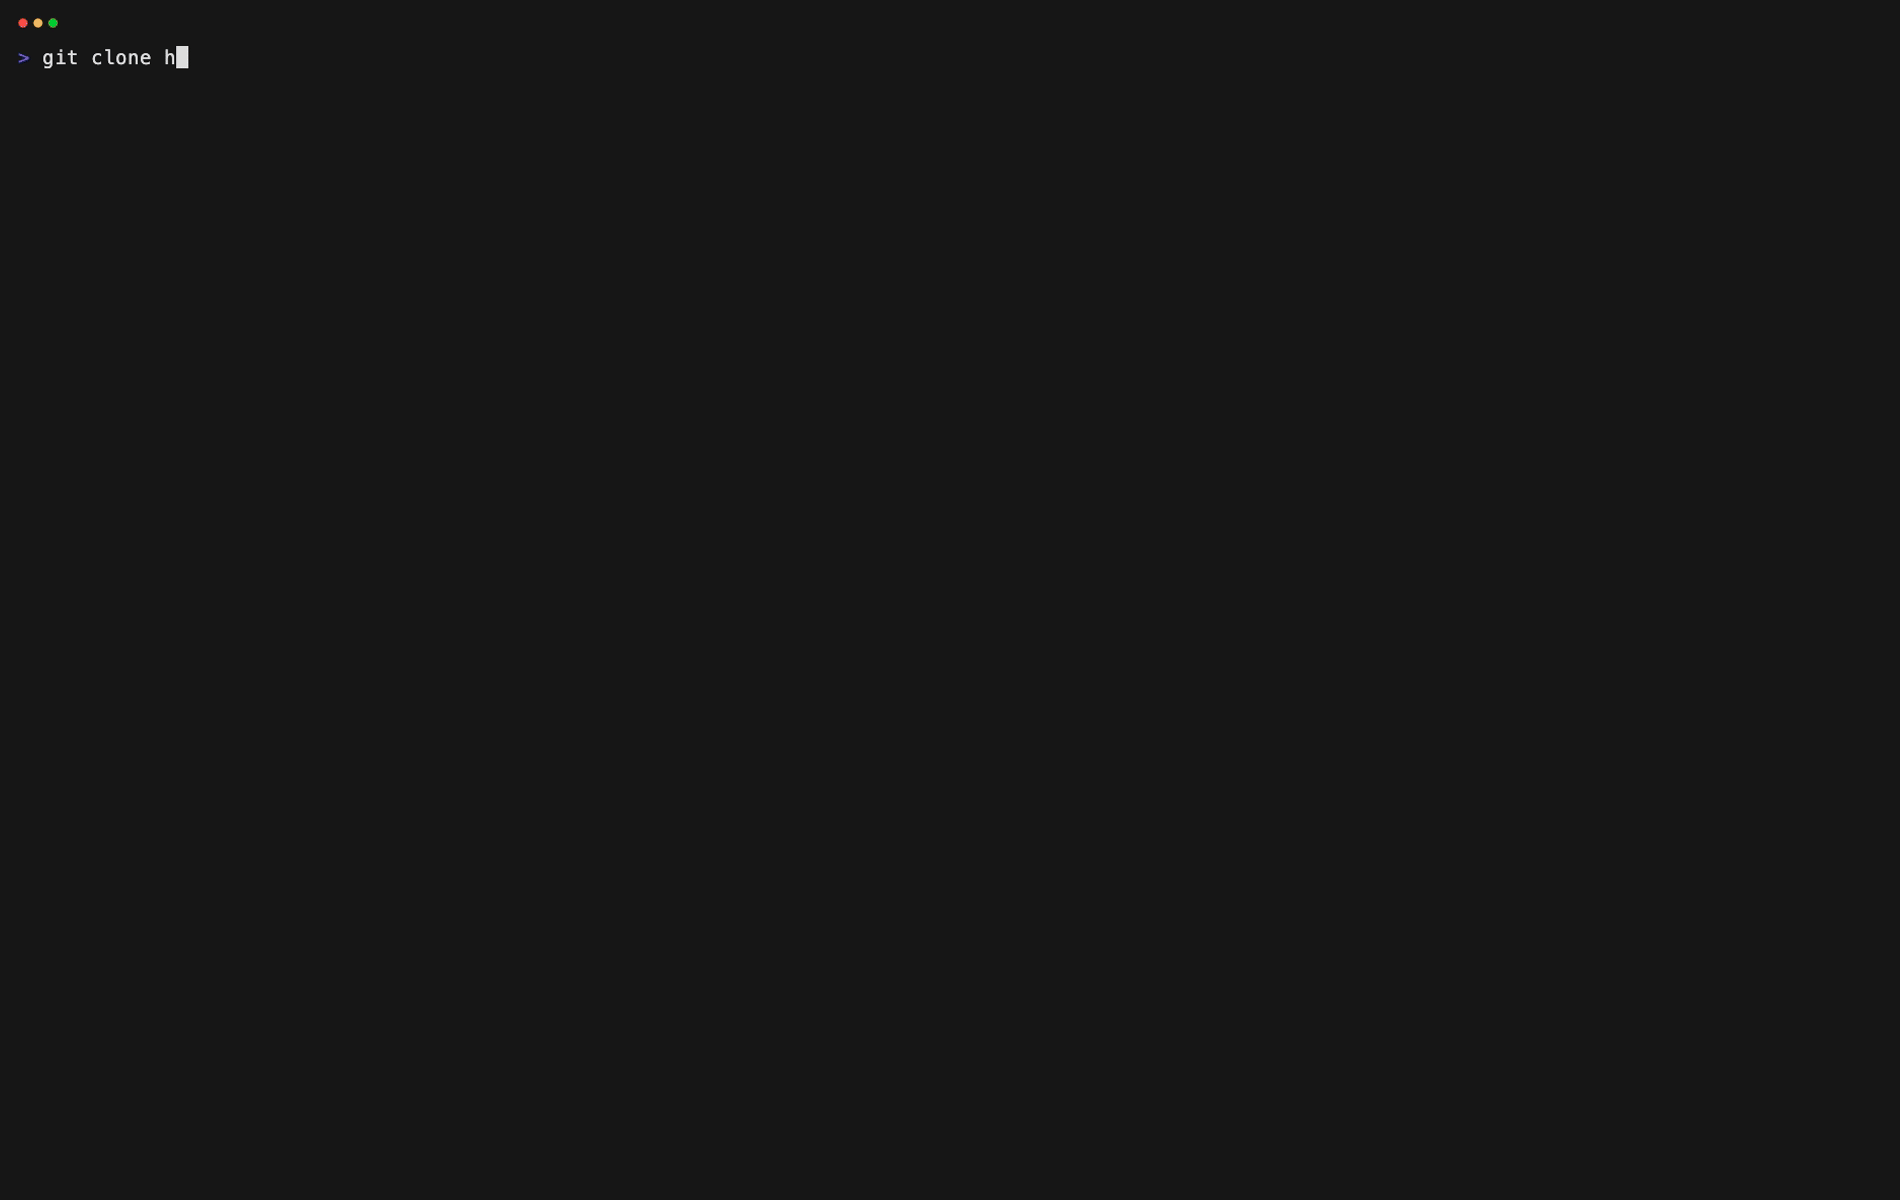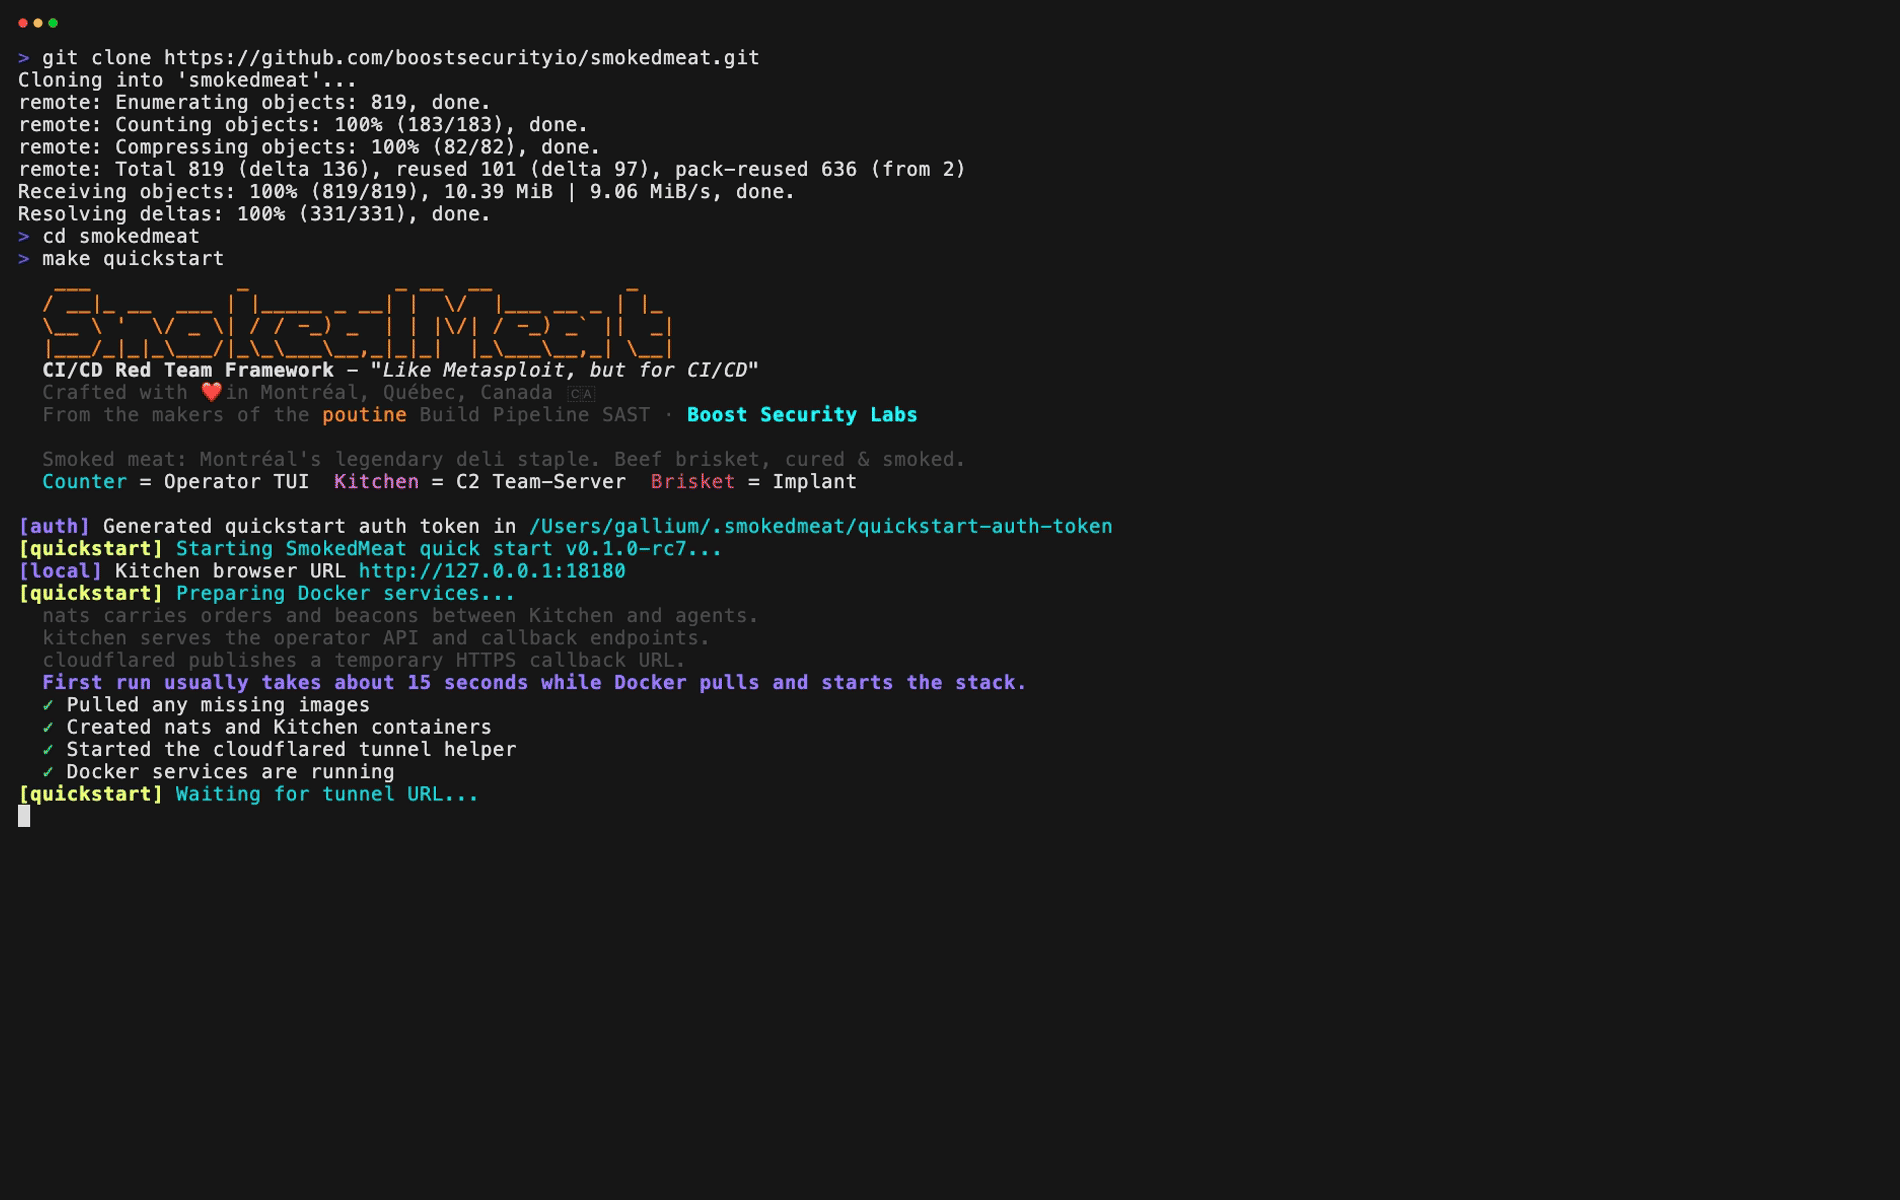 boostsecurityio/smokedmeat
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
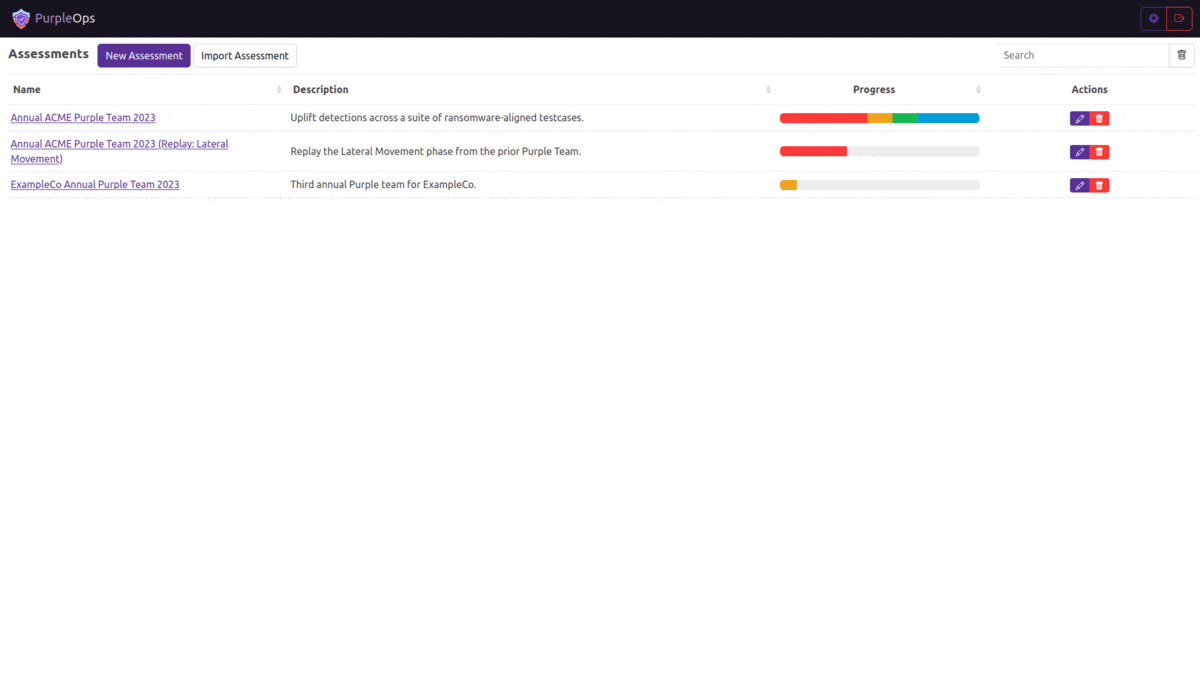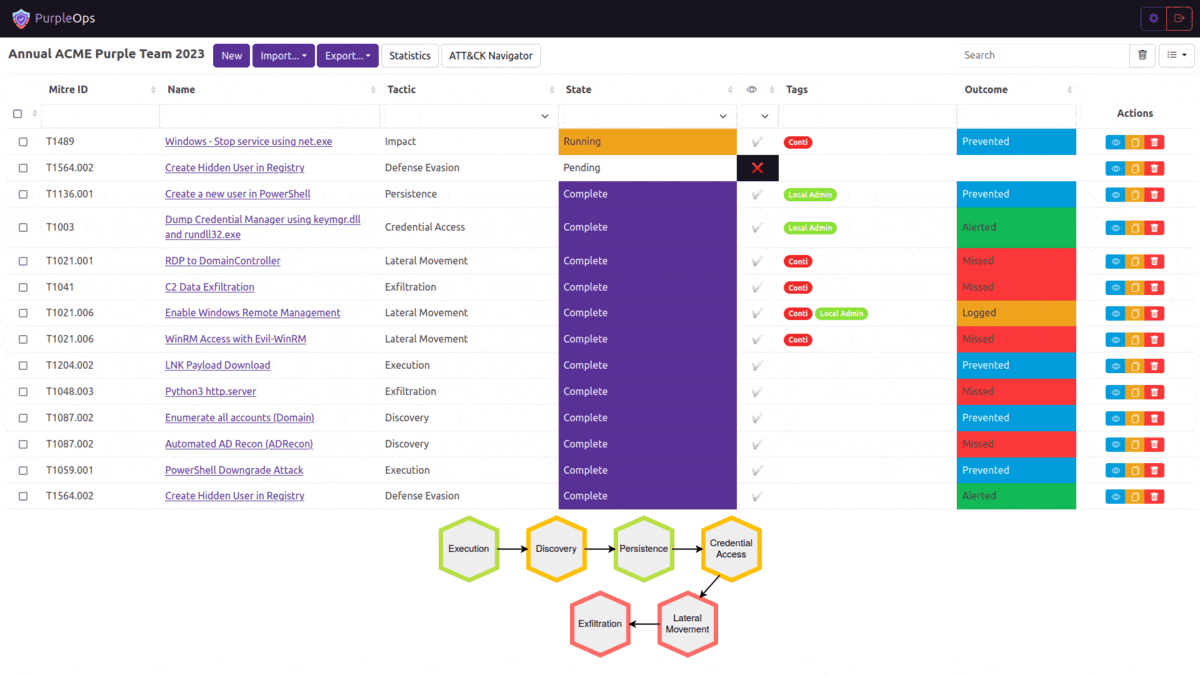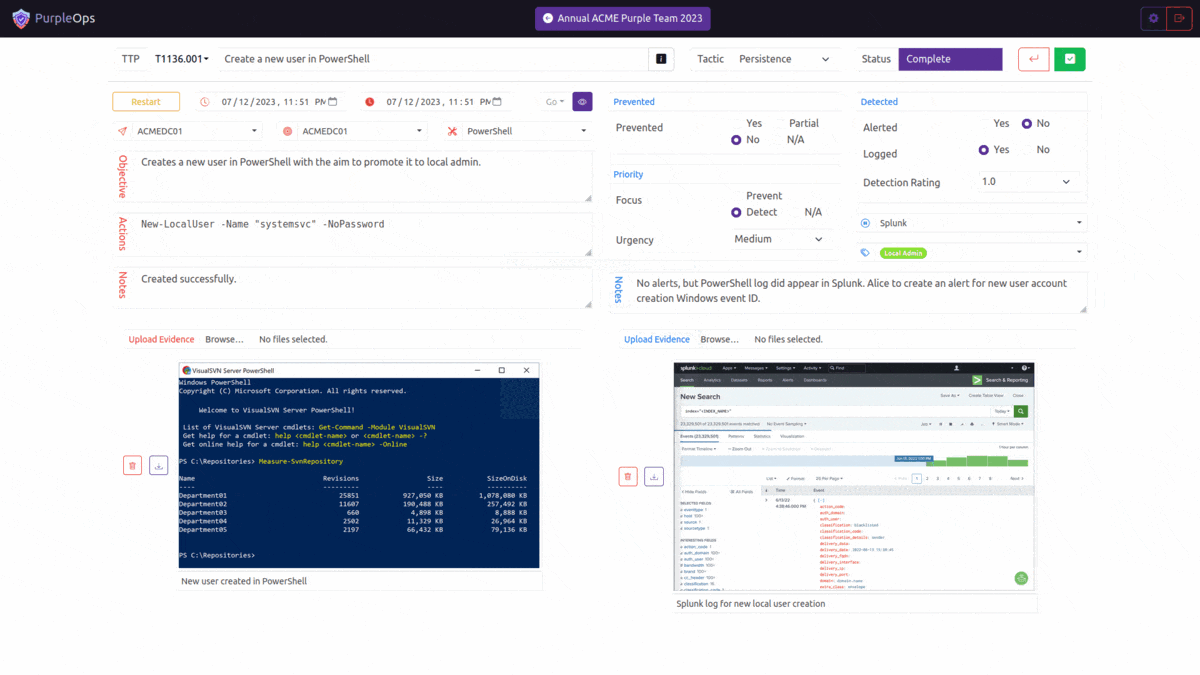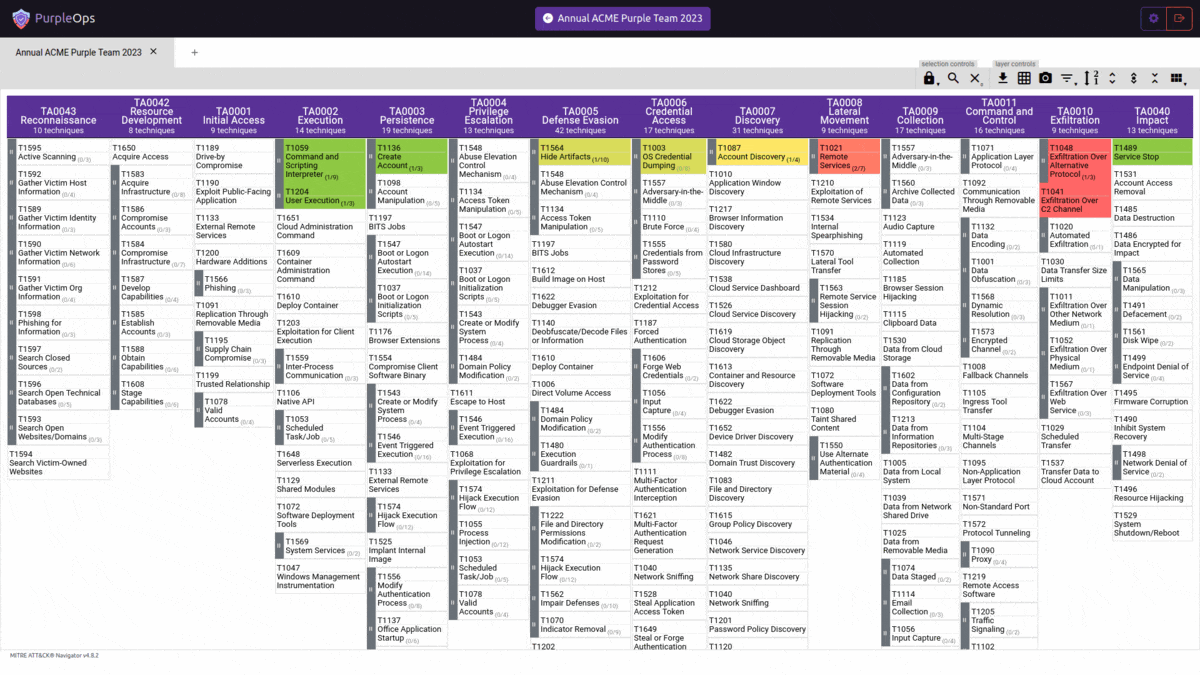 cybercx-sta/purpleops
An open-source self-hosted purple team management web application.
 elder-plinius/t3mp3st
autonomous red teaming platform; multi-agent offensive-security meta-harness
 oritera/cairn
A AI general-purpose state-space search engine, validated first on autonomous penetration testing.
 gallopsled/pwntools
CTF framework and exploit development library
 apache/caldera
Automated Adversary Emulation Platform