

Hexestra
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
ai-securitycommand-and-controlinformation-gathering+7
111
absllk/hexestraAI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 trustedsec/tap
The TrustedSec Attack Platform is a reliable method for droppers on an infrastructure in order to ensure established connections to an organization.
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 samugit83/redamon
Autonomous AI red team framework that chains reconnaissance, exploitation, and post-exploitation into a single pipeline, then triages findings,…
 safelineman/agentic-soc-simulation
AI 驱动的 SOC 仿真平台
 erarnitox/malvexc2
A simple C2 Framework written in modern C++
 cgv-dev/metasploit-module-tfm
Module written in Ruby with the objective of exploiting vulnerabilities CVE-2023-2728 and CVE-2024-3177, both related to the secret mount policy in a…
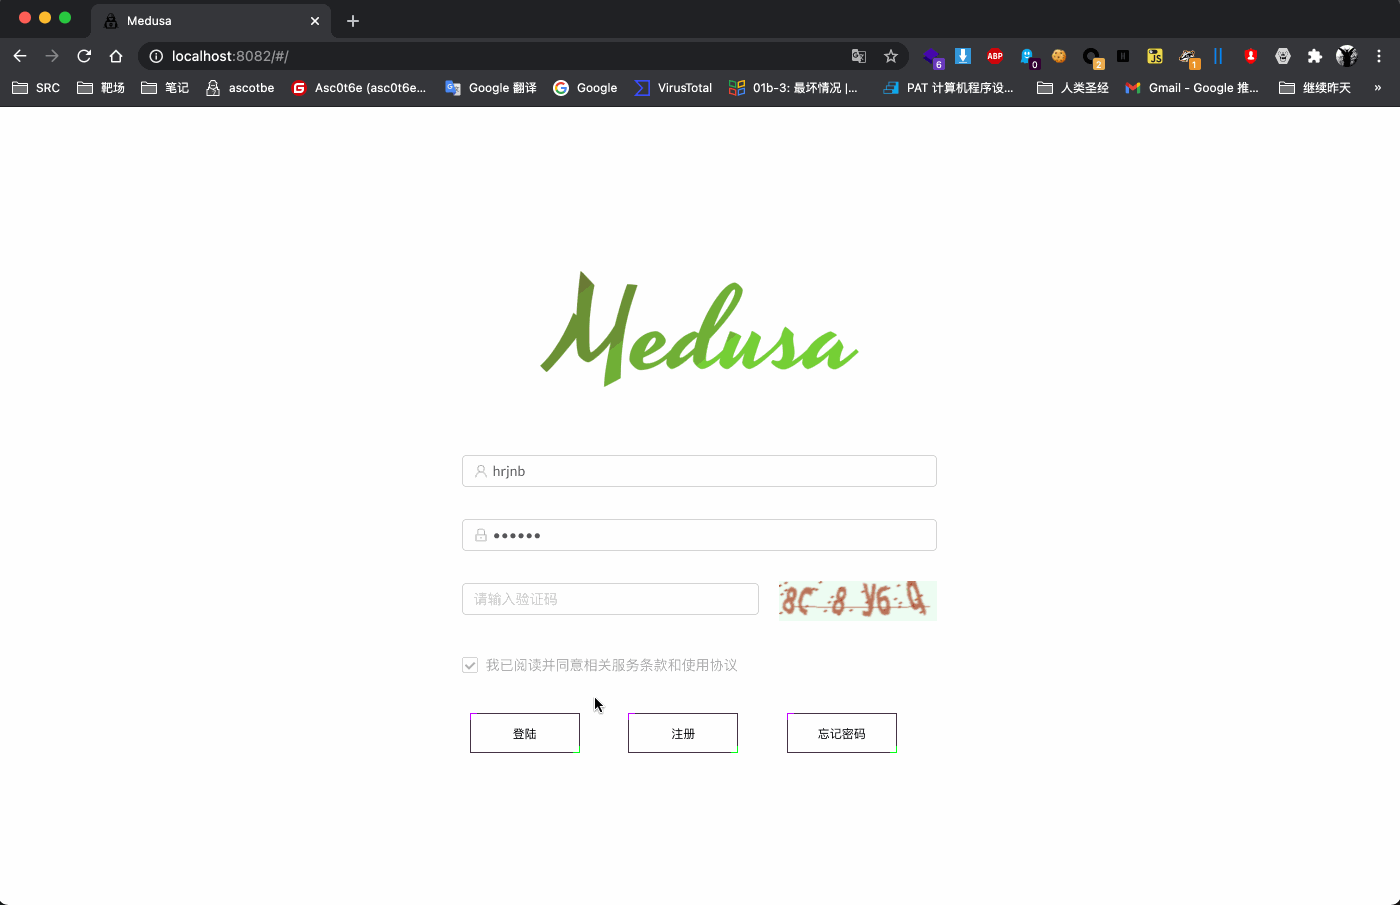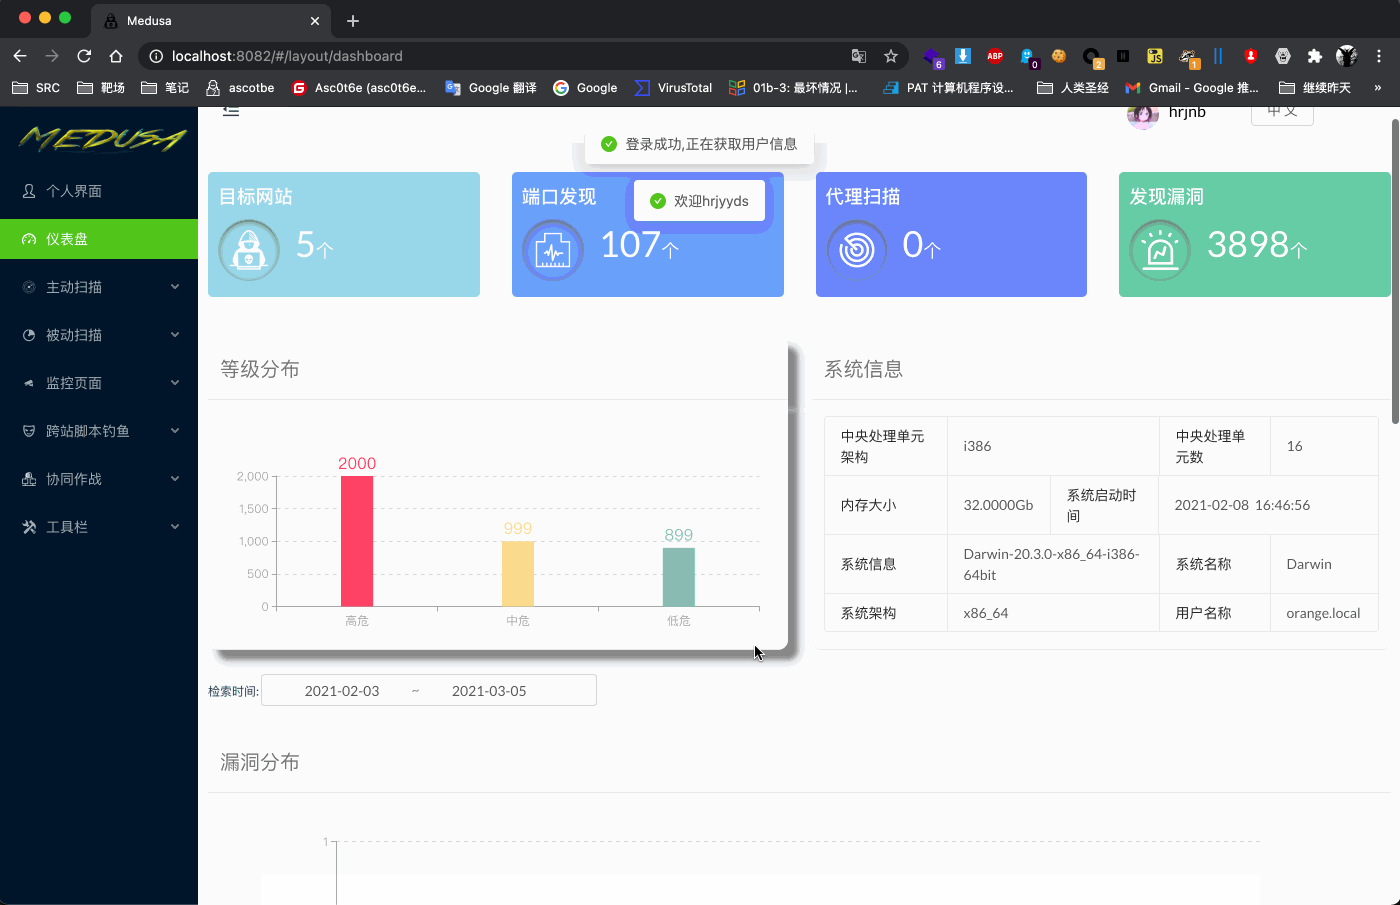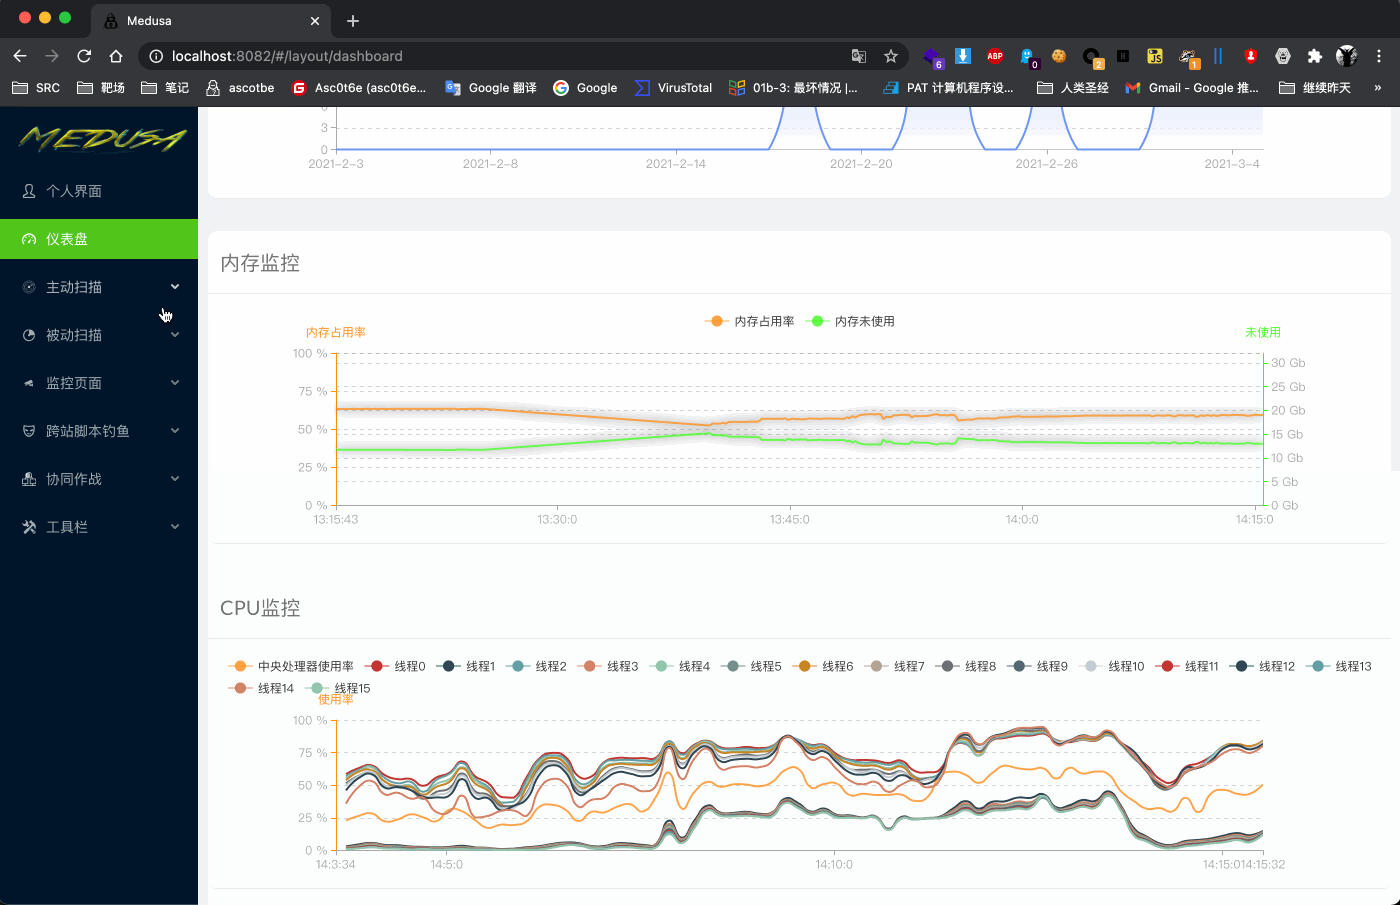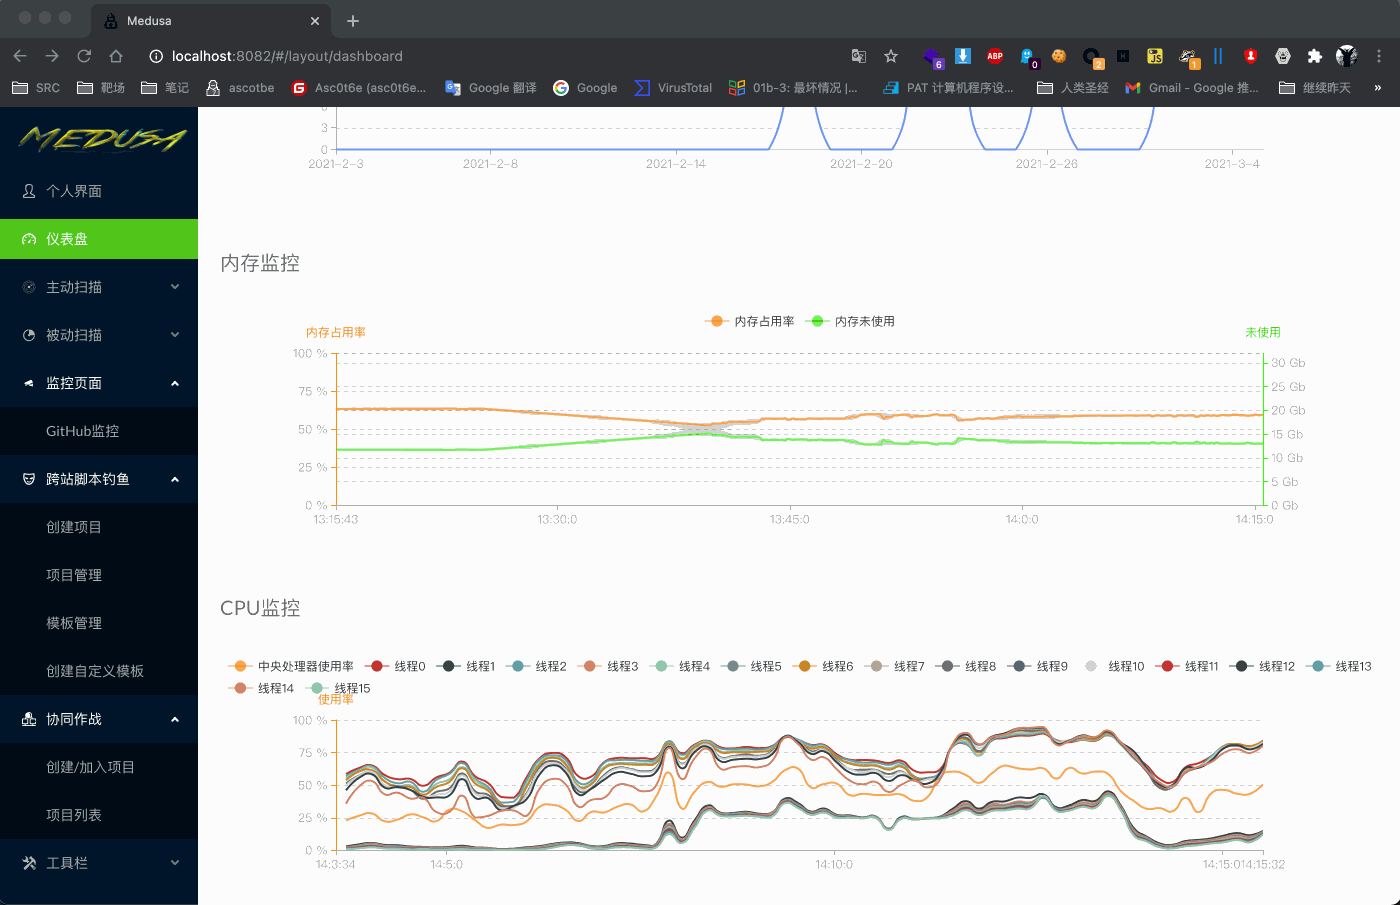 ascotbe/medusa
🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中
 archstrike/archstrike
An Arch Linux repository for security professionals and enthusiasts. Done the Arch Way and optimized for i686, x86_64, ARMv6, ARMv7 and ARMv8.
 knownsec/pocsuite
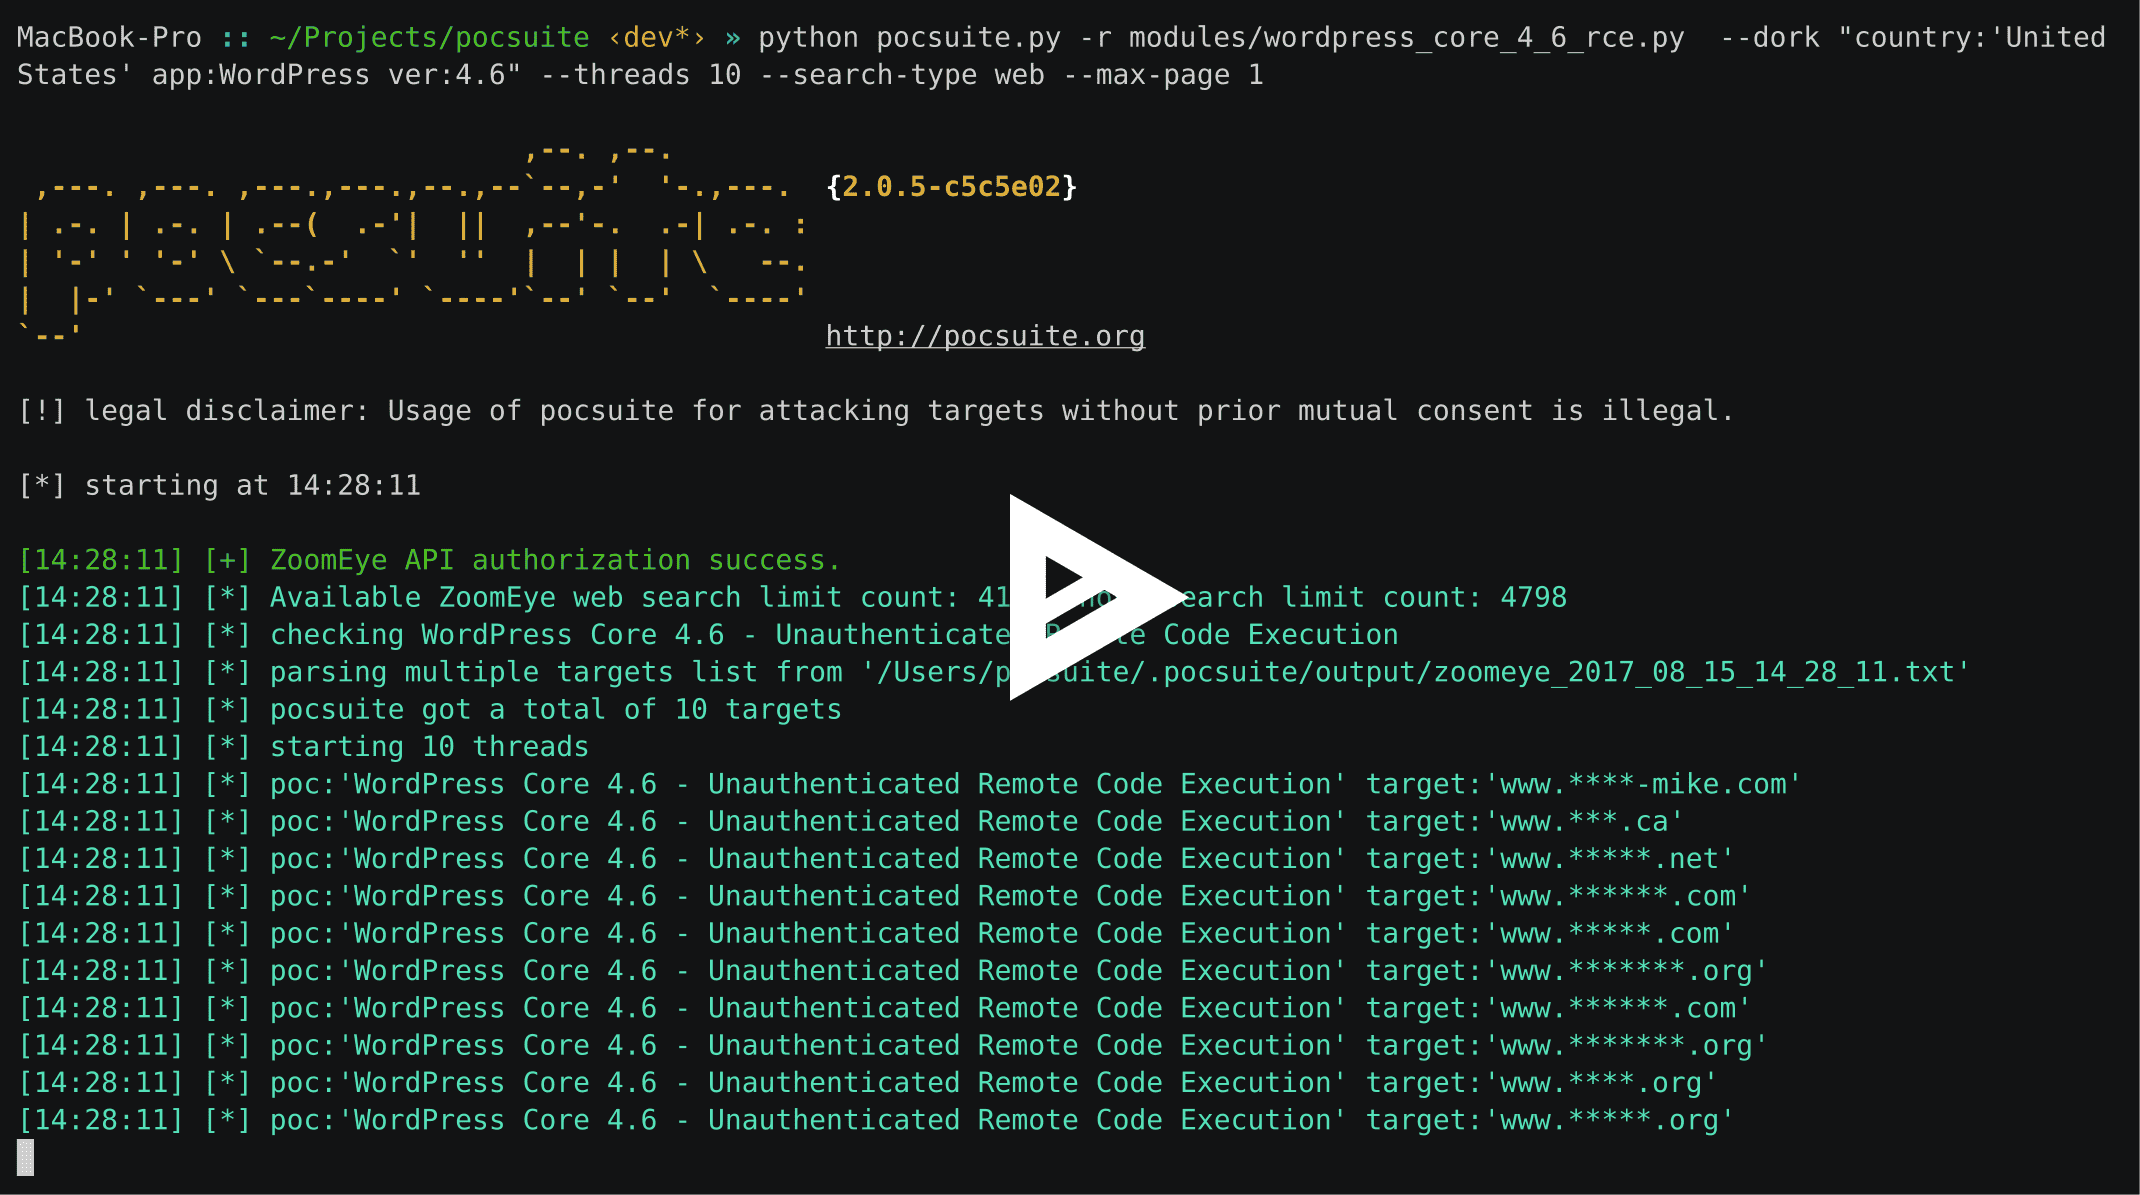
This project has stopped to maintenance, please to https://github.com/knownsec/pocsuite3 project.
 beefproject/beef
The Browser Exploitation Framework Project
 secdevops-cuse/cyberrange
The Open-Source AWS Cyber Range
 sanix-darker/lazymux
Lazymux is a huge list of Many Hacking tools and PEN-TESTING tools! NOTE: Am not Responsible of bad use of this project.
 cisc0-gif/kitt-lite
Python-Based Pentesting CLI Tool
 cisc0-gif/kitt
Python-Based Pentesting Framework
 ascr0b/pcwt
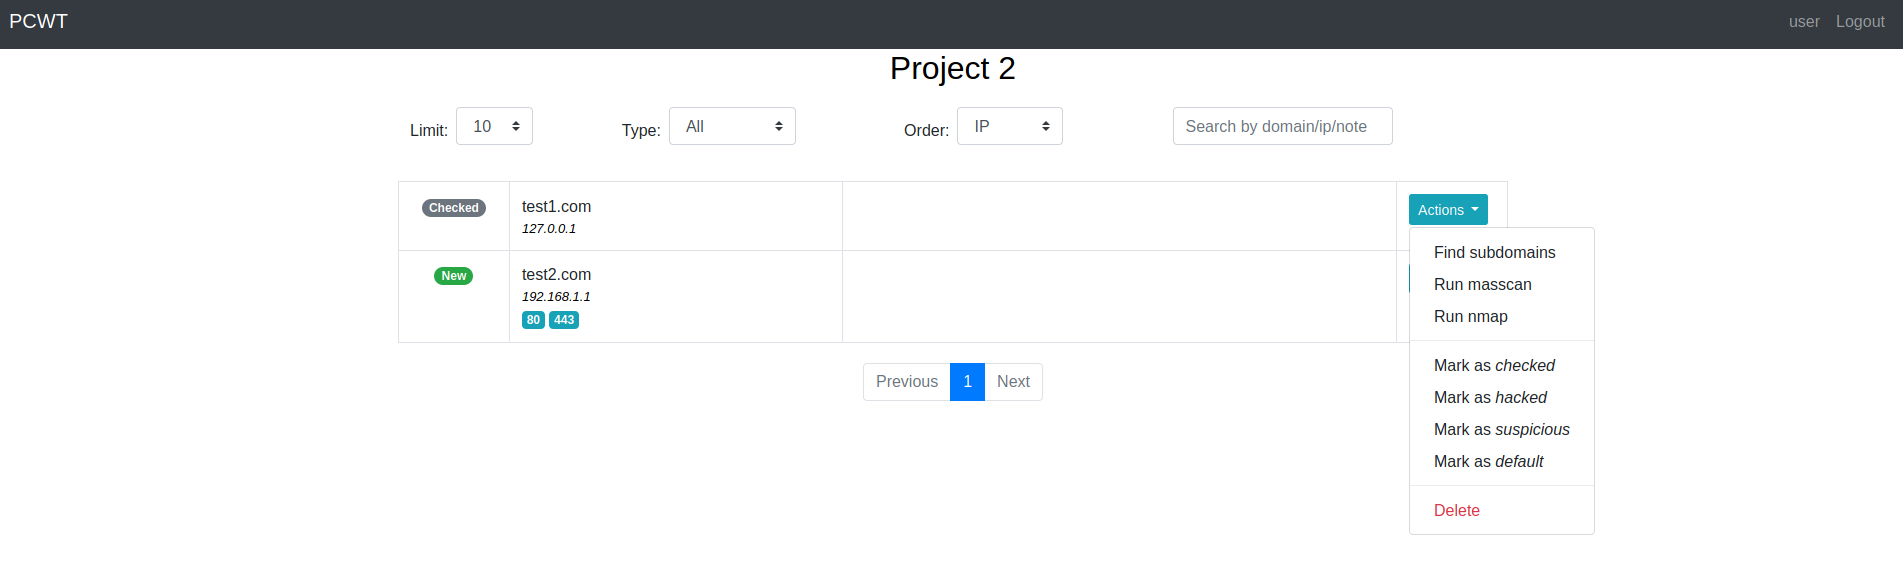
Web-based project management interface for penetration testing and bug bounty workflows, automating port scanning with Nmap/Masscan and subdomain…
 darkr4y/geacon
Practice Go programming and implement CobaltStrike's Beacon in Go
 seungsoo-lee/delta
PROJECT DELTA: SDN SECURITY EVALUATION FRAMEWORK