
CVE-2024-6387
 yassdev221608/cve-2024-6387
Python exploit for CVE-2024-6387 (OpenSSH signal handler race condition) targeting glibc-based 32-bit Linux systems, with multi-threaded concurrency…
binary-exploitationexploitationpayload-development+3
yassdev221608/cve-2024-6387Python exploit for CVE-2024-6387 (OpenSSH signal handler race condition) targeting glibc-based 32-bit Linux systems, with multi-threaded concurrency…
 yassdev221608/cve-2024-6387_poc
Scans and exploits CVE-2024-6387 (regreSSHion) in OpenSSH servers. Features multi-threaded scanning, banner retrieval, grace time detection, and…
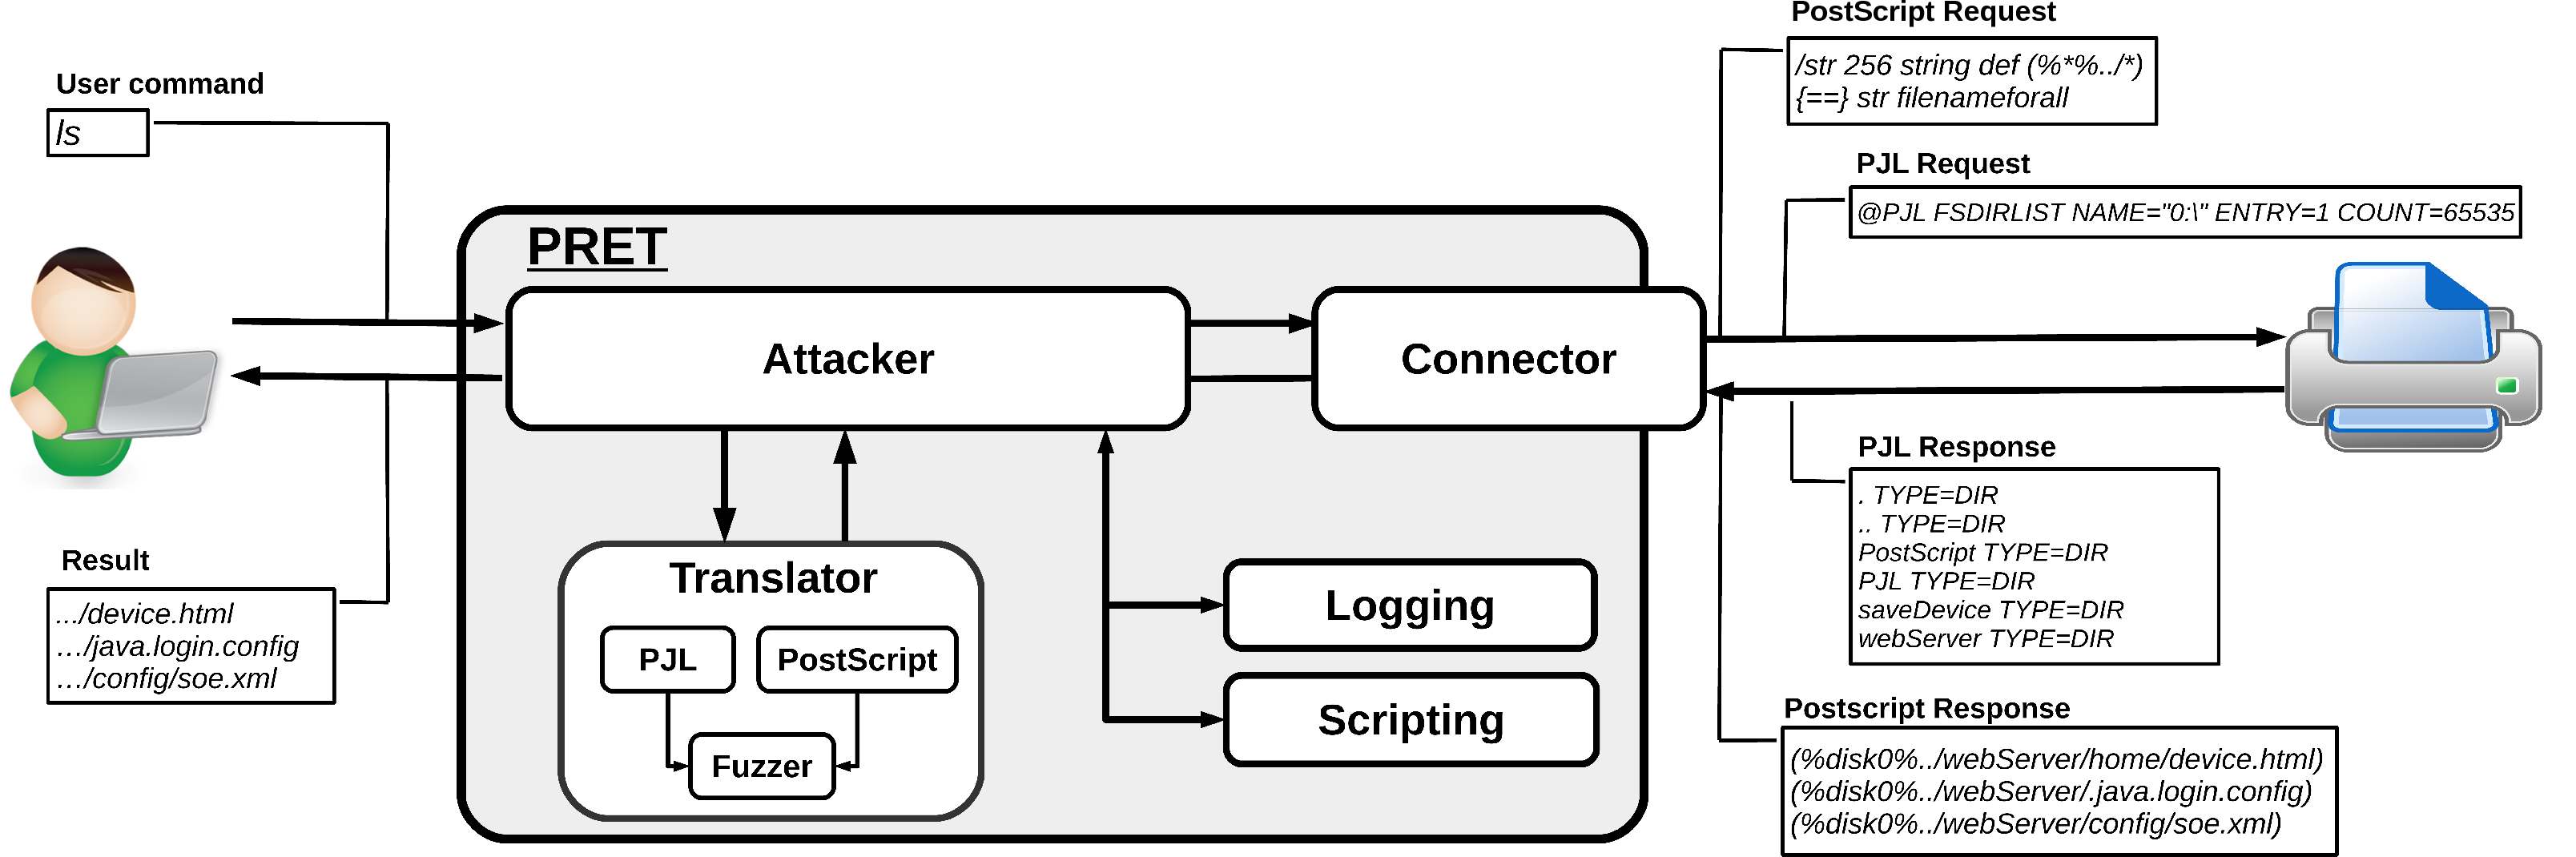 rub-nds/pret
Printer Exploitation Toolkit - The tool that made dumpster diving obsolete.
 adenkiewicz/cve-2017-9544
SEH BO based exploit for Easy Chat Server on Win 7 32b
 manojcode/easy-file-share-7.2-exploit-cve-2018-9059
My version - Easy File Sharing Web Server 7.2 - 'UserID' - Win 7 'DEP' bypass
 peterferrie/win-exec-calc-shellcode
A small, null-free Windows shellcode that executes calc.exe (x86/x64, all OS/SPs)
 manojcode/foxit-reader-rce-with-virualalloc-and-shellcode-for-cve-2018-9948-and-cve-2018-9958
Foxit Reader version 9.0.1.1049 Use After Free with ASLR and DEP bypass on heap
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
 improsec/improhound
Identify the attack paths in BloodHound breaking your AD tiering