
CVE-2026-49468-LiteLLM-Auth-Bypass
 biitts/cve-2026-49468-litellm-auth-bypass
CVE-2026-49468 — LiteLLM (<1.84.0) unauthenticated auth bypass via Host-header route confusion. PoC + docker lab.
authenticationeducationexploitation+4
5
biitts/cve-2026-49468-litellm-auth-bypassCVE-2026-49468 — LiteLLM (<1.84.0) unauthenticated auth bypass via Host-header route confusion. PoC + docker lab.
 47cid/wp2shell-lab
Educational PoC + lab for CVE-2026-63030 + CVE-2026-60137: pre-auth SQLi in WordPress core via REST batch-route confusion
 keraattin/cve-2026-33032
One missing function call on the route registration was enough to turn the MCP interface into an unauthenticated RCE gateway.
 dinosn/wp2shell-lab
Non-destructive detector + Docker lab for wp2shell (CVE-2026-63030 REST /batch/v1 route confusion + CVE-2026-60137 author__not_in SQLi) in WordPress…
 ikow/wp2shell
wp2shell — WordPress Core Pre-Auth RCE (CVE-2026-63030 + CVE-2026-60137). Exploit toolkit + remediation.
 own2pwn-fr/wp2shell-detect
Blackbox, non-intrusive detector for wp2shell (WordPress core pre-auth RCE, CVE-2026-63030 / CVE-2026-60137). Detection only.
 icex0/wp2shell-poc
wp2shell (CVE-2026-63030 & CVE-2026-60137) - full RCE chain
 kernelzeroday/cve-2026-29000
Forge JWE-wrapped unsigned JWTs to bypass pac4j-jwt signature verification (CVE-2026-29000) and authenticate as any user; includes Python CLI,…
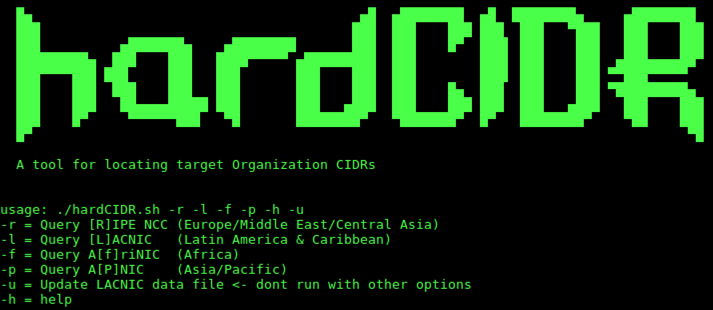 trustedsec/hardcidr
Bash script for passive reconnaissance that queries RIRs and BGP route servers to discover target organization netblocks, ASNs, and CIDR ranges…
 warpedatom/noisehound
Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…
 eqstlab/cve-2026-85706
PoC and Docker lab for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE via the commits API route bypass and urlencoded error…
 senanfurkan/wordpress-cve-2026-63030
Pre-auth RCE in WordPress Core via REST API batch route confusion + WP_Query SQLi (CVE-2026-63030 / CVE-2026-60137). Detection PoC.
 jasper2018/cve-2018-20062
Verification script and PoC for CVE-2018-20062, the ThinkPHP 5.0.x invokefunction deserialization RCE, confirming route reachability and capturing…
 giangdurian/cve-2026-63030-cve-2026-60137
Pre-auth RCE exploit for WordPress (CVE-2026-63030 + CVE-2026-60137) chaining route confusion and SQL injection into full shell access. Includes…
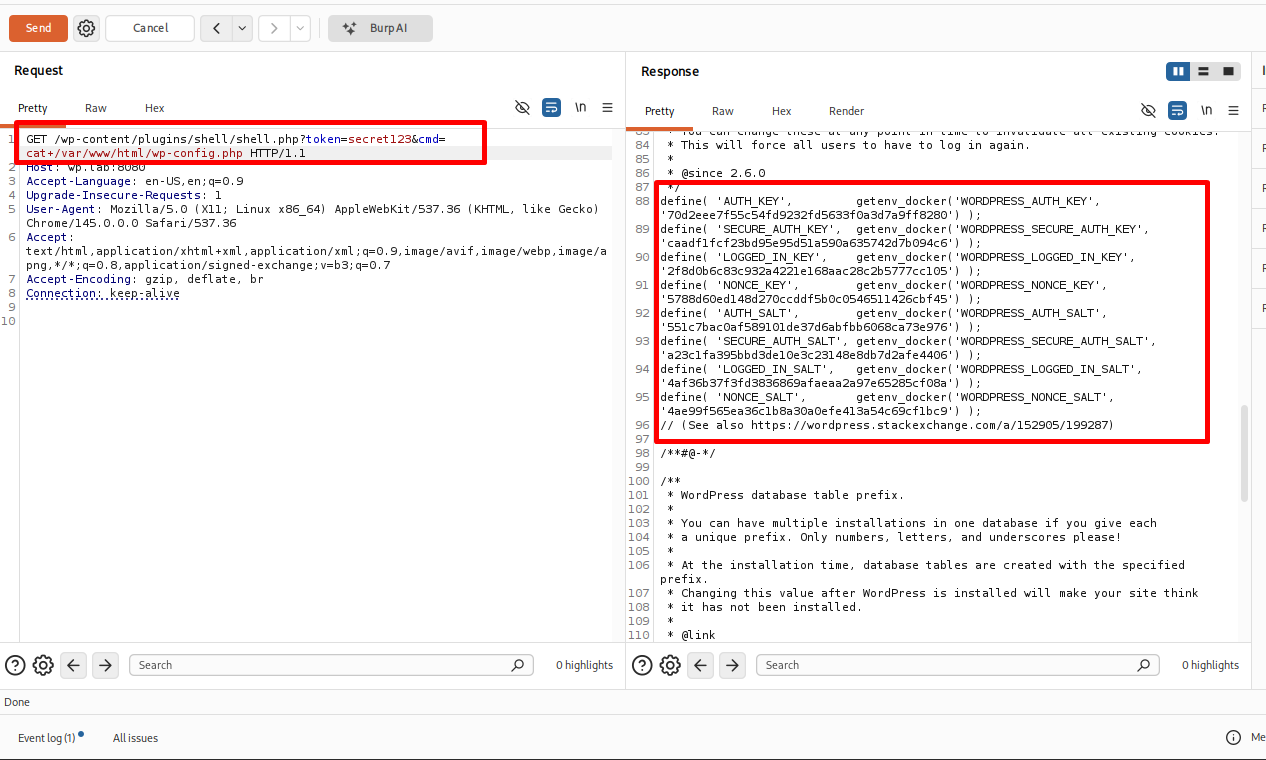 dungsocool/cve-2026-60137_cve-2026-63030
WordPress unauthenticated RCE exploit combining route confusion and SQL injection. Automated script, lab setup, and detailed vulnerability analysis…
 shinthink/cve-2026-63030
WordPress Core Pre-Auth RCE via REST Batch Route Confusion + SQLi (CVE-2026-63030 + CVE-2026-60137)
 vulnquest58/pressvector
PressVector - Advanced WordPress Vulnerability Scanner CVE-2026-63030 (REST batch route confusion) / CVE-2026-60137 (SQLi) Developer: Vulnquest
 anggatechi/cve-2026-63030
WordPress Core Pre-Auth RCE — Batch Route Confusion + SQL Injection