
psc
 stealth/psc
E2E encryption for multi-hop tty sessions or portshells + TCP/UDP port forward
encryption-decryption-toolsforensicsnetwork-security+2
stealth/pscE2E encryption for multi-hop tty sessions or portshells + TCP/UDP port forward
 infobyte/draytek-arsenal
Reverse Engineering and Observability toolkit for Draytek firewalls
 0xk4rth1/cve-2025-2304
A critical mass assignment vulnerability in Camaleon CMS (< 2.9.1) allows authenticated low-privileged users to elevate their privileges to…
 dafthack/check-localadminhash
Check-LocalAdminHash is a PowerShell tool that attempts to authenticate to multiple hosts over either WMI or SMB using a password hash to determine…
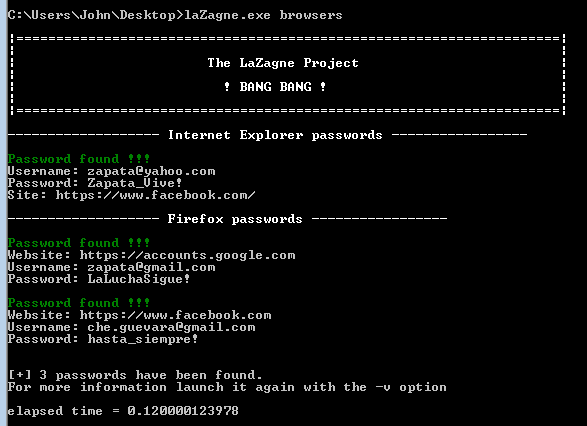 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
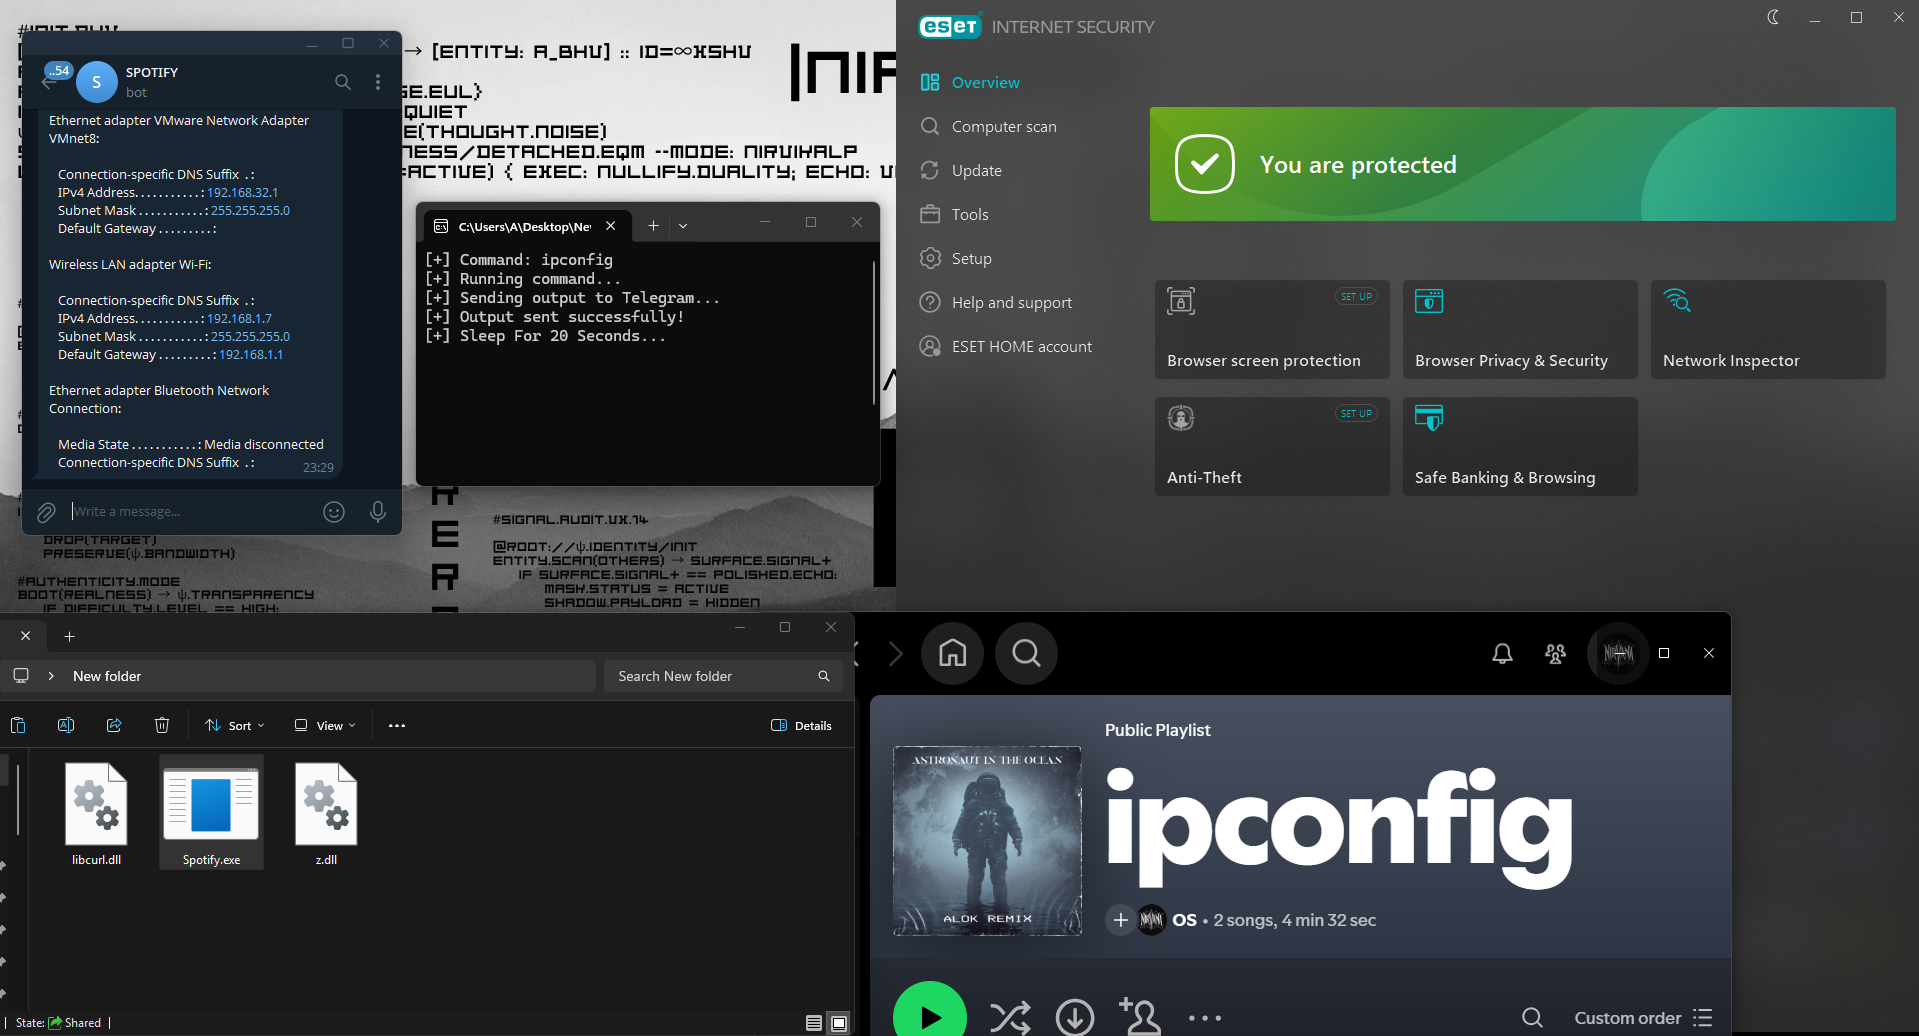 nirvanaon/spotifyc2
Windows-based C2 research tool that uses Spotify playlists as a command channel and Telegram for output delivery, demonstrating cloud-assisted…
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 davidsonrafaelk/evillimiter
Tool that monitors, analyzes and limits the bandwidth of devices on the local network without administrative access
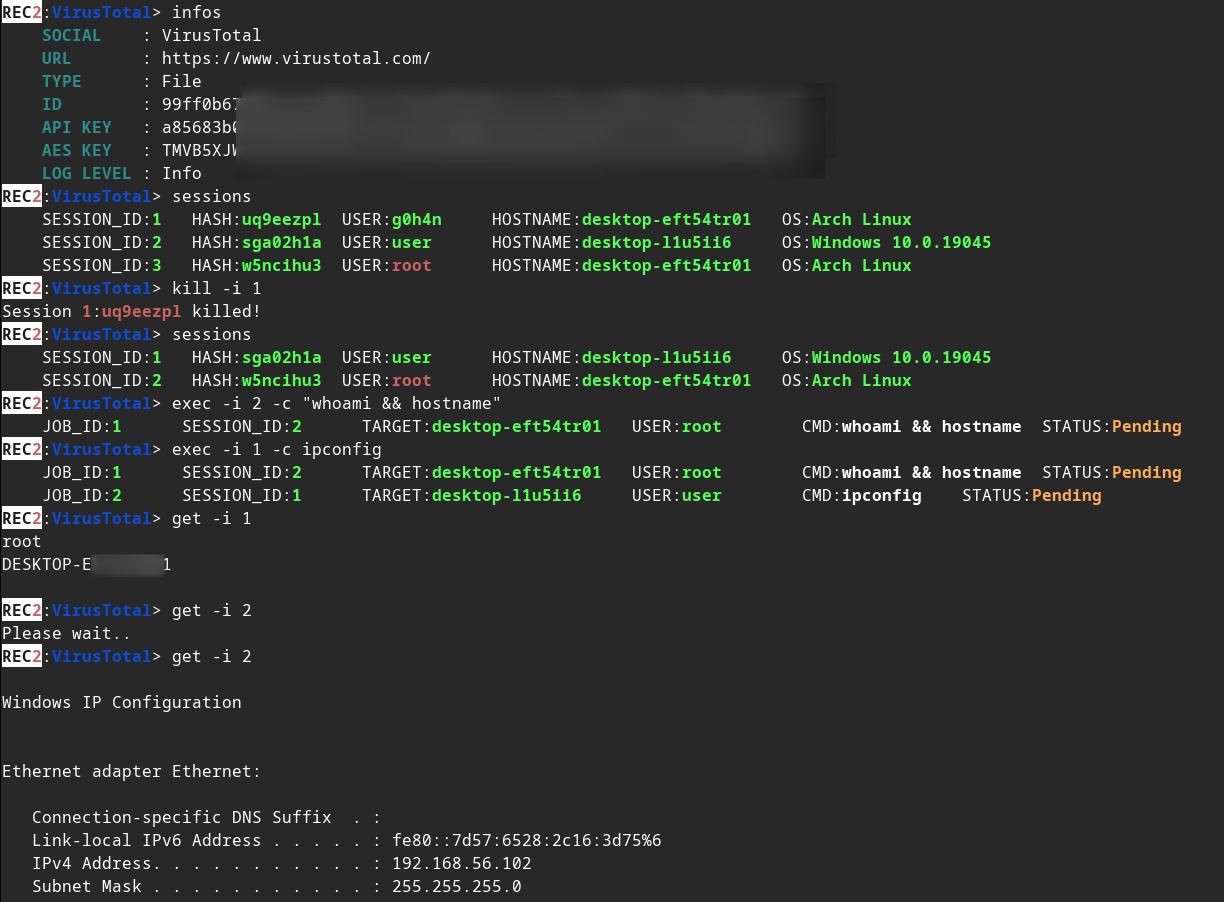 g0h4n/rec2
REC2 (Rusty External Command and Control) is client and server tool allowing auditor to execute command from VirusTotal and Mastodon APIs written in…
 gigachadusers/cve-2026-20127
Windows-based C++ network scanner that fingerprints Cisco SD-WAN/vManage services and checks for CVE-2026-20127 exposure via HTTP endpoint analysis.
 ilikenwf/darkagent
DarkAgent Remote Administration Tool RAT by DragonHunter
 wezoomagency/grafxploit
Automated Exploit Tool for Grafana CVE-2021-43798: Scanning common files that contain juicy informations and extracting SSH keys from compromised…
 hxlxmj/grafxploit
Automated Exploit Tool for Grafana CVE-2021-43798: Scanning common files that contain juicy informations and extracting SSH keys from compromised…
 fadi002/unshackle
Open-source tool to bypass windows and linux passwords from bootable usb
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 blipzip/cve-2022-31692
A project demonstrating an app that is vulnerable to Spring Security authorization bypass CVE-2022-31692
 adhikara13/cve-2023-24489-sharefile
This project is a Python script that exploits the CVE-2023-24489 vulnerability in ShareFile. It allows remote command execution on the target server.…
 ricsirigu/cve-2025-29927
A deliberately Next.js app, vulnerable to CVE-2025-29927, Authorization Bypass