
Archived
selenium-wire
 wkeeling/selenium-wire
Extends Selenium's Python bindings to give you the ability to inspect requests made by the browser.
api-security-testinginformation-gatheringpenetration-testing+2
wkeeling/selenium-wireExtends Selenium's Python bindings to give you the ability to inspect requests made by the browser.
 nccgroup/argumentinjectionhammer
A Burp Extension designed to identify argument injection vulnerabilities.
 owasp/owaspbugbounty
This is a container of web applications that work with OWASP Bug Bounty for Projects
 scriptingxss/iotgoat
IoTGoat is a deliberately insecure firmware based on OpenWrt.
 owasp/iotgoat
Deliberately insecure OpenWrt-based firmware for hands-on IoT security training. Features vulnerability challenges mapped to the OWASP IoT Top 10 for…
 dheeraj-jayaswal/cicd-goat-vapt-writeup
Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…
 waburig/open-worldwide-application-security-project-owasp-
Automated Web Vulnerability Assessment of DVWA using OWASP ZAP to identify and analyze critical security flaws like Remote Code Execution…
 owasp/security-champions
OWASP guide for security champions, providing curated resources and learning paths to foster security culture and practices within development teams.
 owasp/owaspwebgoatphp
A deliberately vulnerable web application for learning web application security.
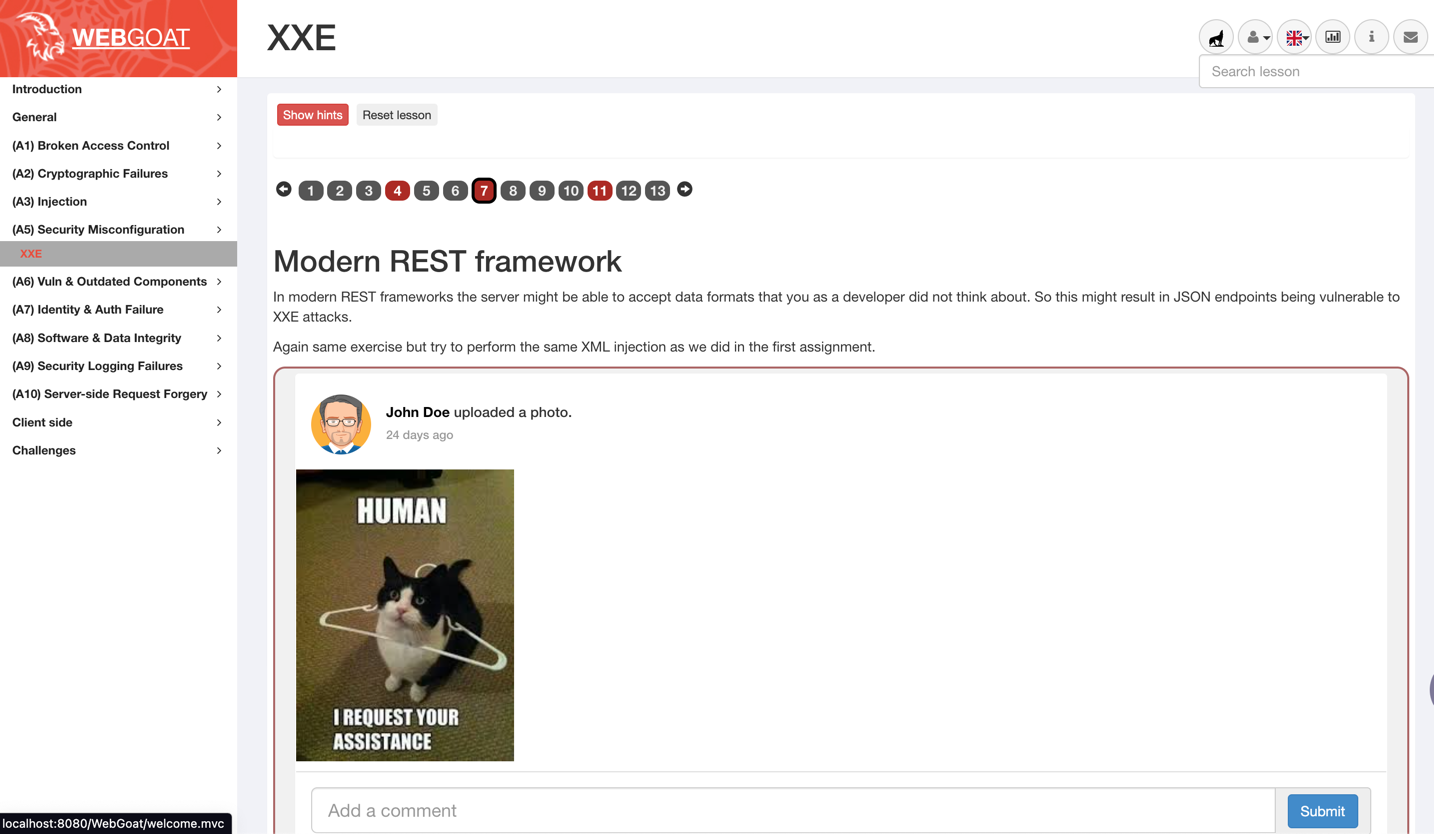 webgoat/webgoat
Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
 owasp/nodegoat
The OWASP NodeGoat project provides an environment to learn how OWASP Top 10 security risks apply to web applications developed using Node.js and how…
 zaproxy/zap-api-rust
Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…
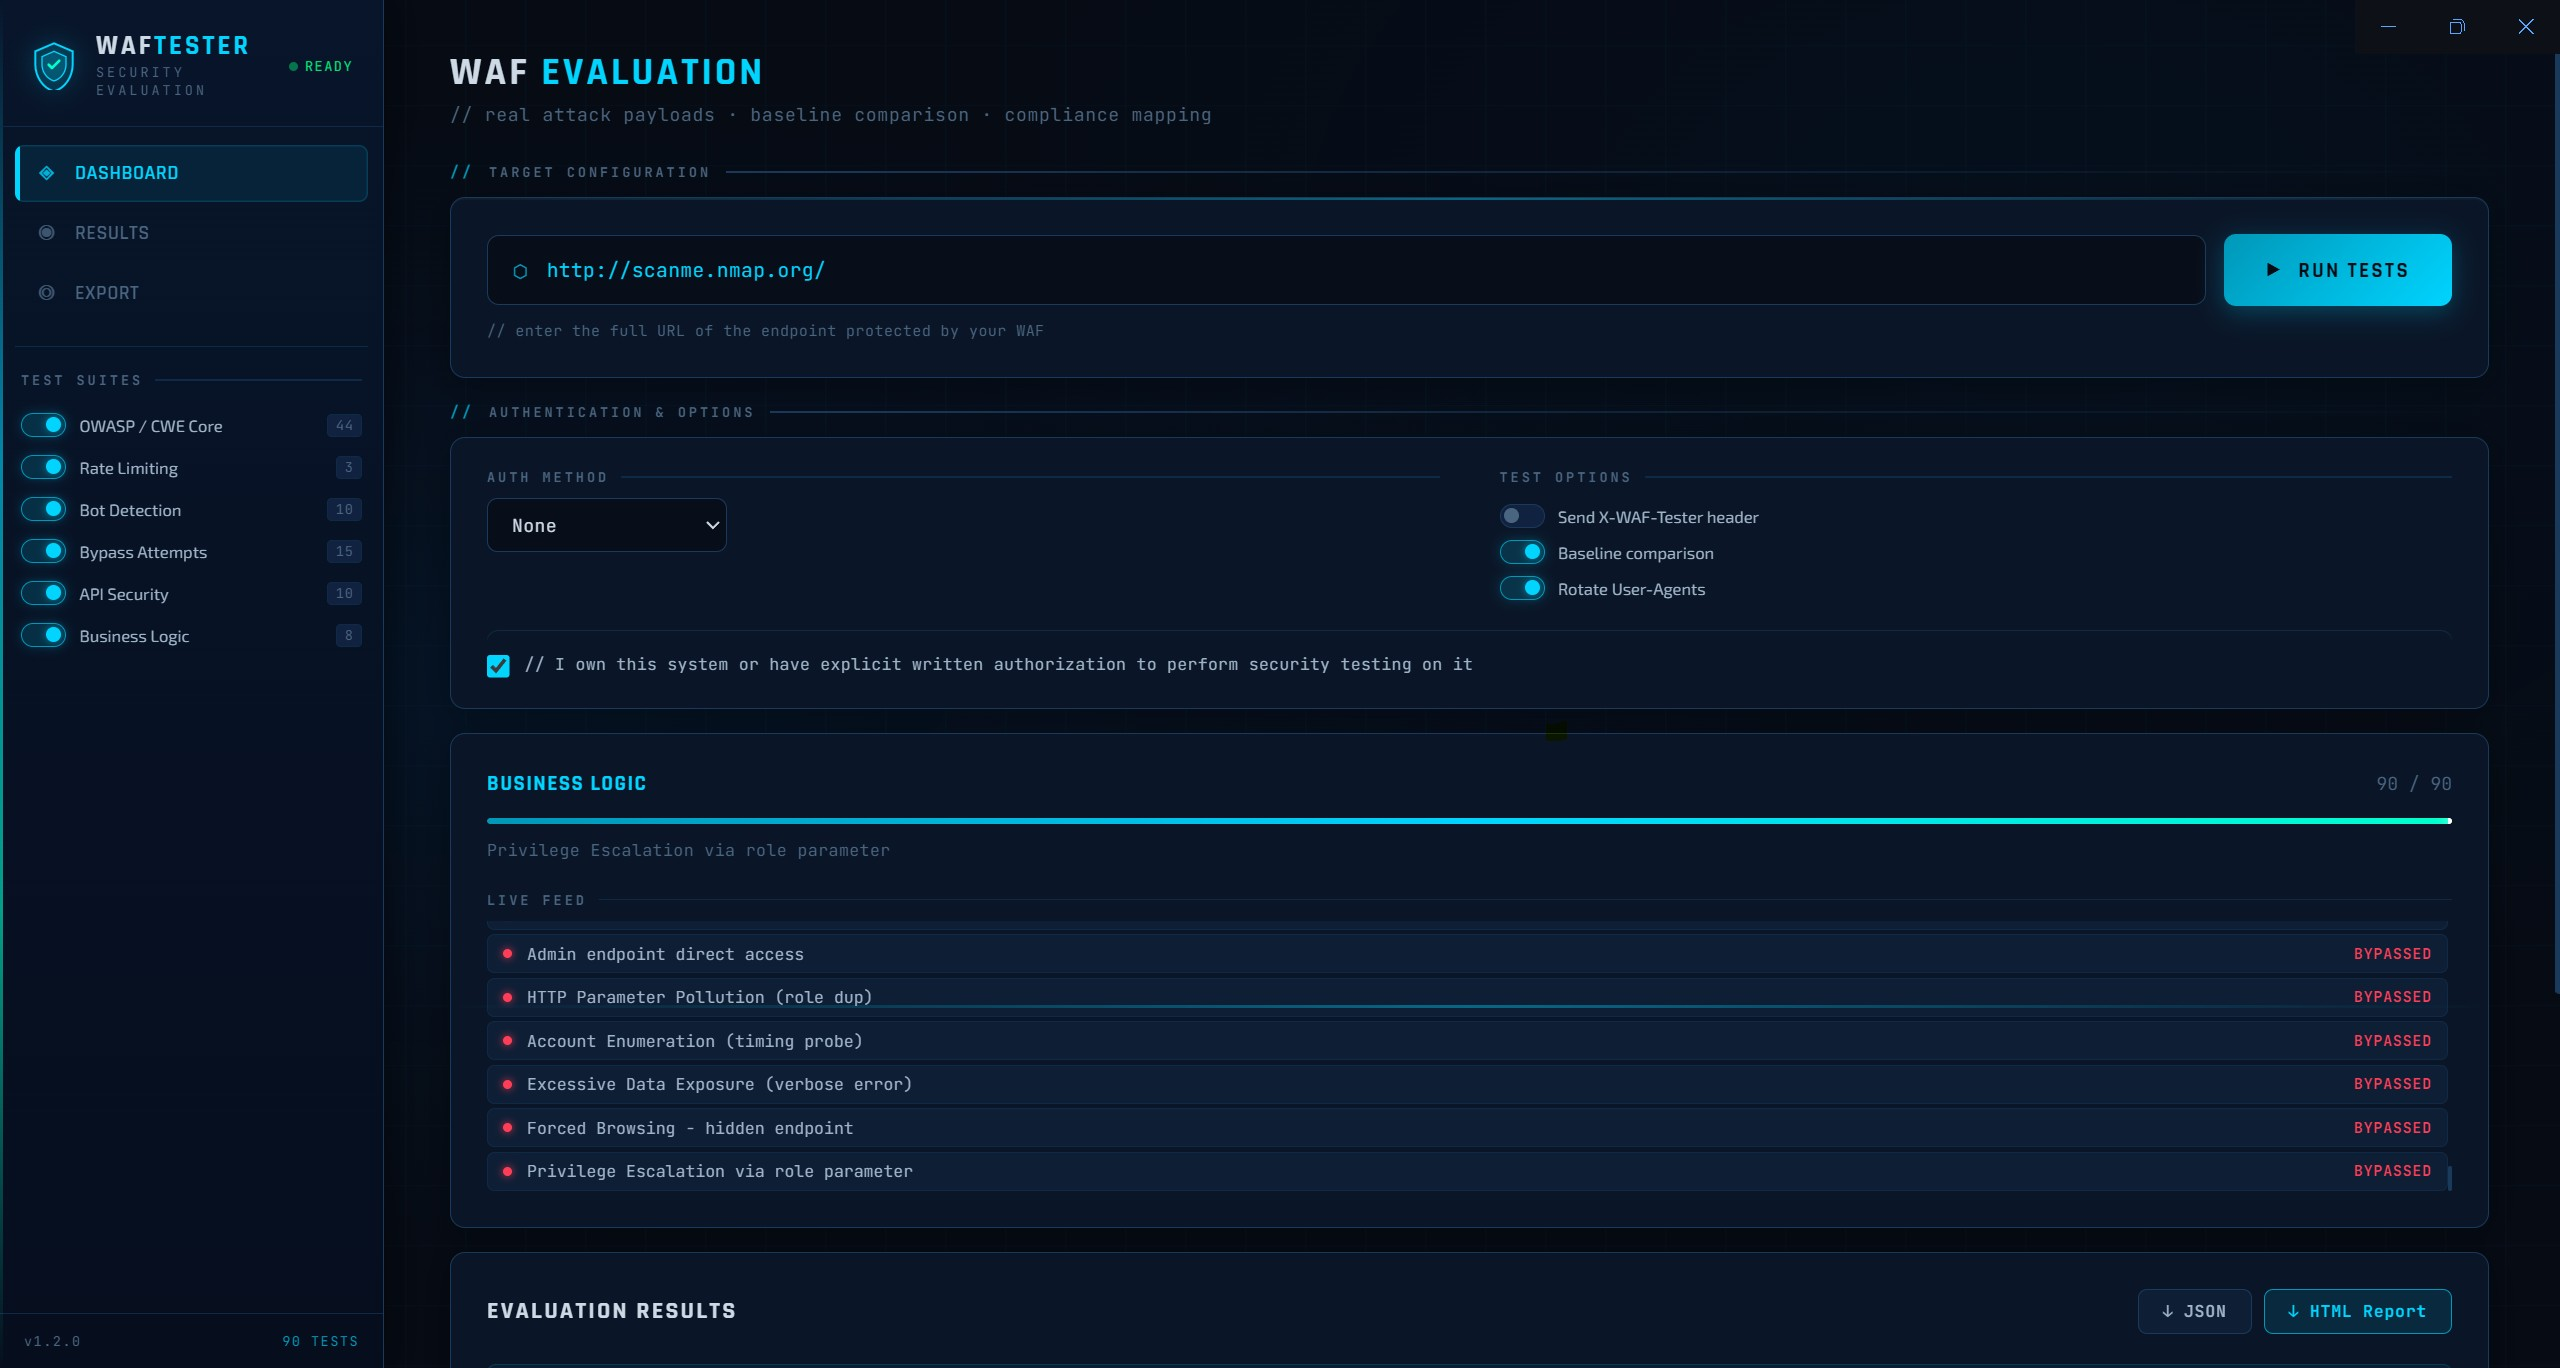 kpomin57/waf-tester
A program for testing WAF functionality
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 digeex/raider
DEPRECATED, please use the new repository from OWASP: https://github.com/OWASP/raider
 ine-labs/azuregoat
AzureGoat : A Damn Vulnerable Azure Infrastructure
 ine-labs/gcpgoat
GCPGoat : A Damn Vulnerable GCP Infrastructure
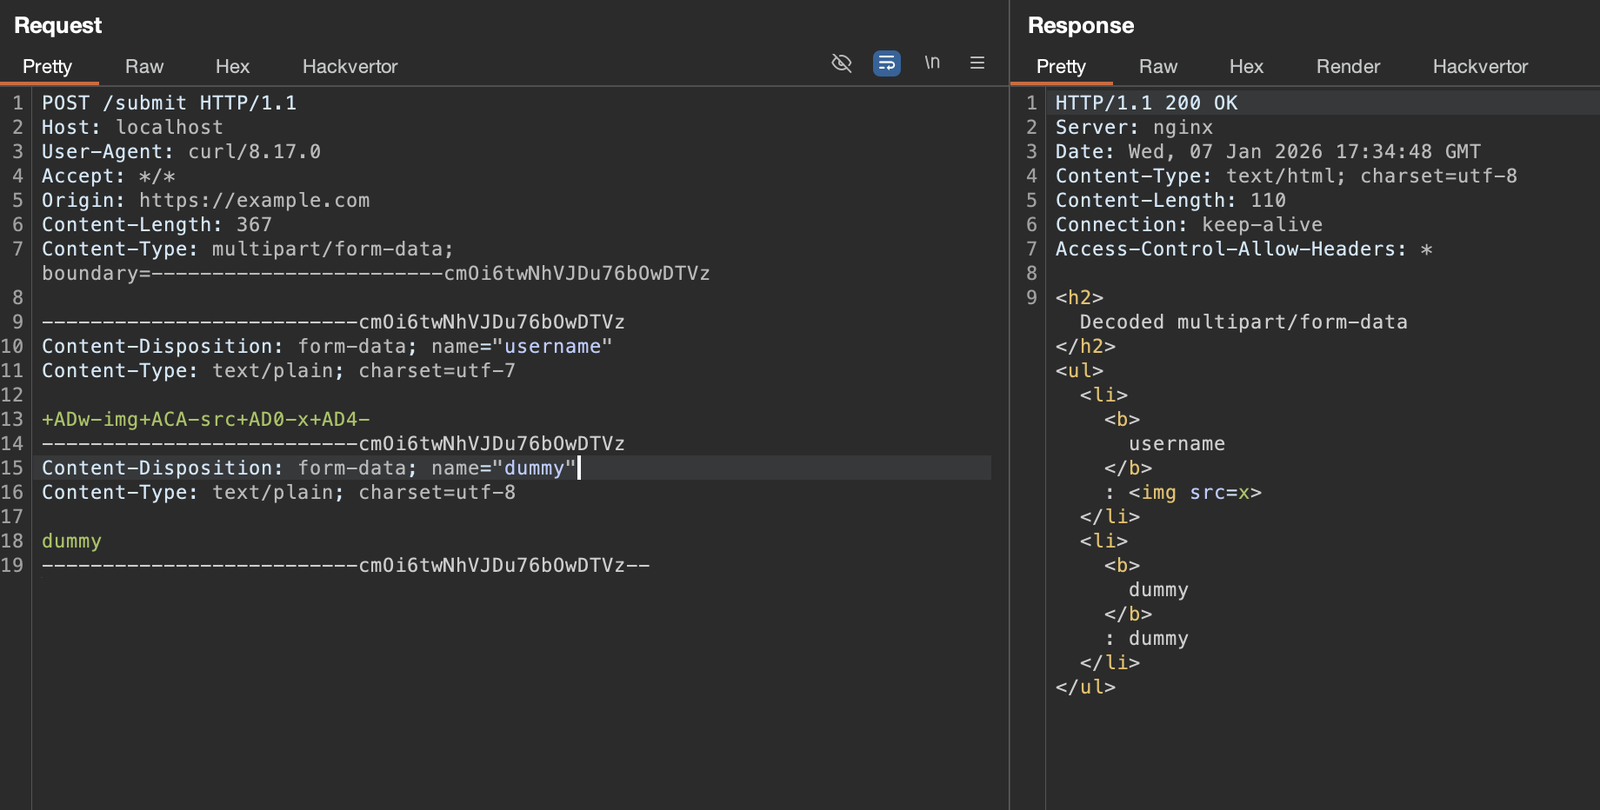 mefhika120/cve-2026-21876
Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.