
CrucibleC2
 dragoqcc/cruciblec2
A C# Command & Control framework
command-and-controlexploit-frameworkslateral-movement+5
dragoqcc/cruciblec2A C# Command & Control framework
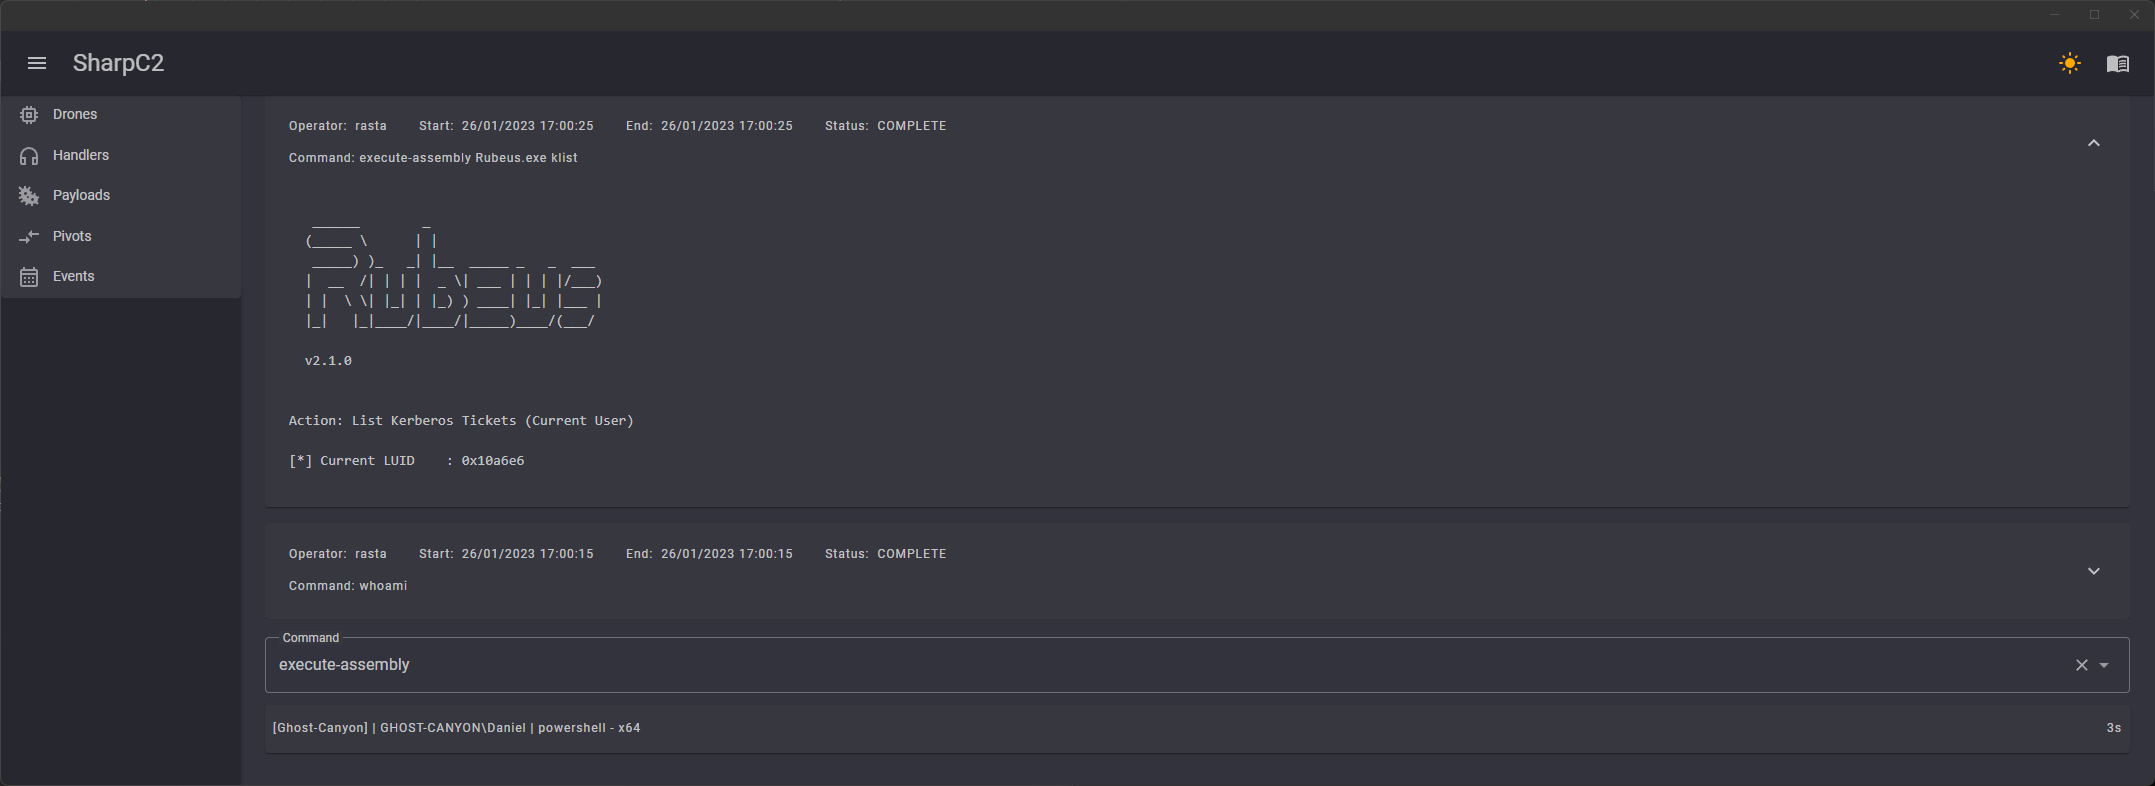 rasta-mouse/sharpc2
Command and Control Framework written in C#
 mitre/caldera-crater
C# remote access trojan (RAT) implant for the Caldera adversary emulation framework, enabling post-exploitation command and control on Windows…
 qwqdanchun/dcrat
A simple remote tool in C#.
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
 ghostpack/sharpwmi
SharpWMI is a C# implementation of various WMI functionality.
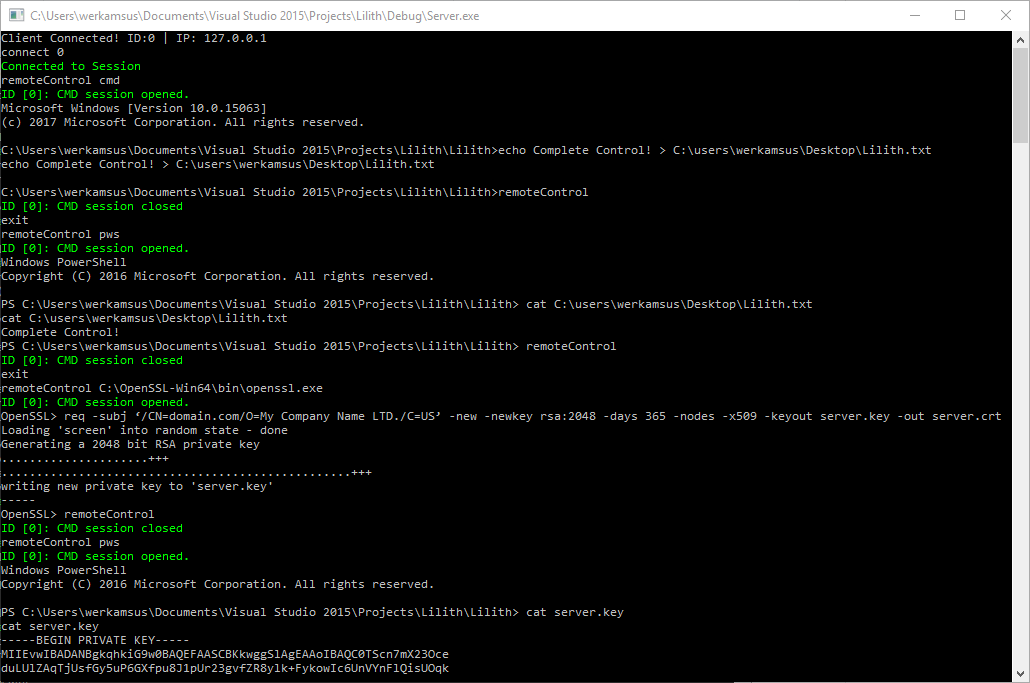 werkamsus/lilith
Lilith - Foundational reverse engineering resource for cybersecurity entrepreneurs in C++
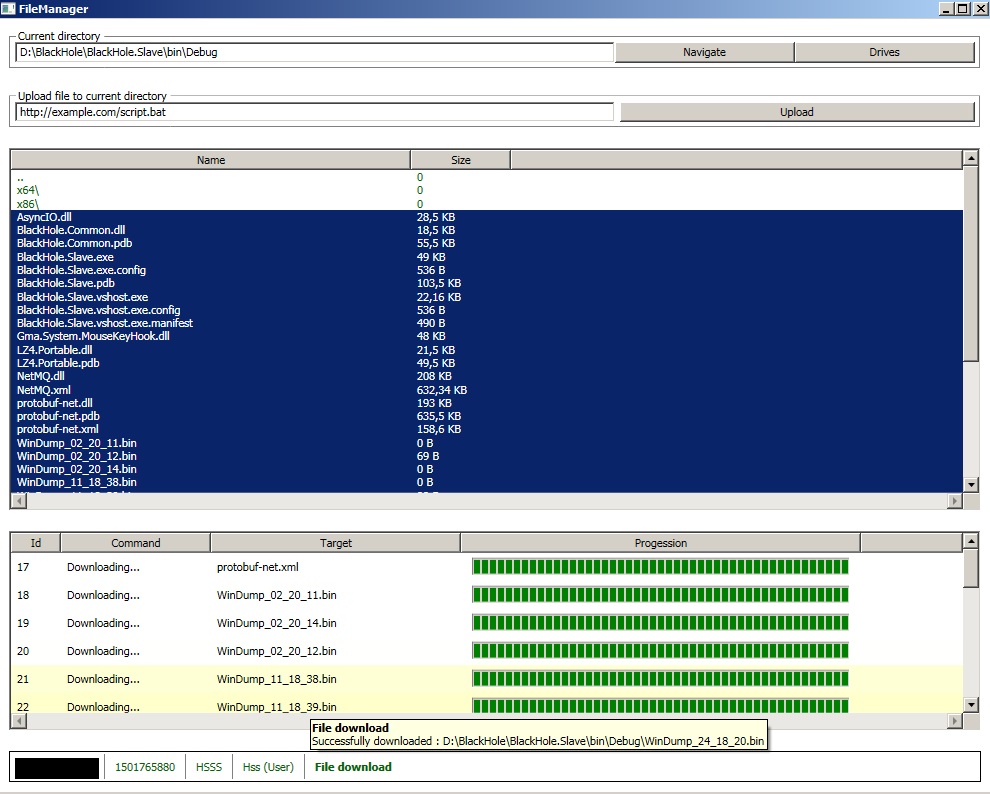 hussein-aitlahcen/blackhole
C# RAT (Remote Administration Tool)
 mgeeky/stracciatella
OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup
 redsiege/cimplant
C# port of WMImplant which uses either CIM or WMI to query remote systems
 iomoath/sharpstrike
A Post exploitation tool written in C# uses either CIM or WMI to query remote systems.
 anthemtotheego/sharpsploitconsole
C# console application for post-exploitation and red team operations, integrating SharpSploit to execute Mimikatz commands, perform Kerberoasting,…
 abhishekkr/n00brat
Remote Administration Toolkit (or Trojan) for POSiX (Linux/Unix) system working as a Web Service
 watersalesman/aura-botnet
A super portable botnet framework with a Django-based C2 server. The client is written in C++, with alternate clients written in Rust, Bash, and…
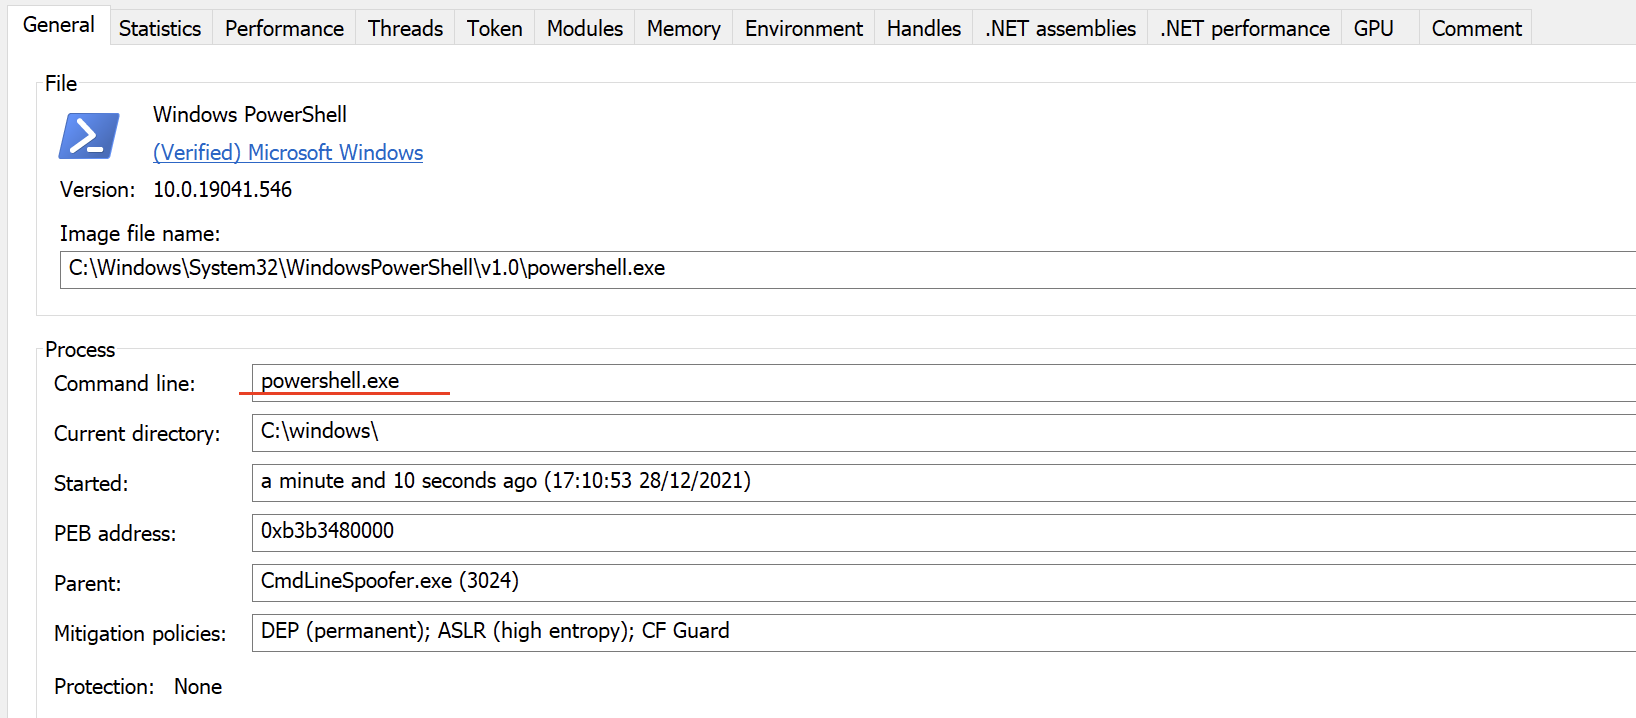 plackyhacker/cmdlinespoofer
How to spoof the command line when spawning a new process from C#.
 nyan-x-cat/njrat-0.7d-stub-csharp
njRAT C# Stub - Fixed For PowerShell
 ivancabrera02/r2socks
SOCKS5 proxy tunneled through Cloudflare R2 object storage, with Python and dependency-free C++ agents relaying TCP traffic via encrypted R2 objects…
 warferik/cve-2019-3980
Proof-of-concept exploit for CVE-2019-3980 enabling remote command execution via custom C# payload with HTTP callback for output retrieval.