
CVE-2025-63498
 xryptoh/cve-2025-63498
Stored XSS proof-of-concept for SOGo groupware, exploiting the 'Remember Username' cookie to inject JavaScript payloads via the login endpoint.
exploitationpenetration-testingvulnerability-analysis+2
2
xryptoh/cve-2025-63498Stored XSS proof-of-concept for SOGo groupware, exploiting the 'Remember Username' cookie to inject JavaScript payloads via the login endpoint.
 wr0x00/cve-2022-23131
Exploit for CVE-2022-23131 targeting Zabbix SAML SSO authentication bypass. Generates a signed session cookie to gain unauthorized admin access.
 datackmy/fallingskies-cve-2023-35885
Python exploit for CVE-2023-35885 targeting CloudPanel v2.0.0–v2.3.0. Injects a webshell via a crafted serialized cookie to achieve remote code…
 wooooong/cve-2025-2825
Exploit script for CrushFTP authentication bypass (CVE-2025-2825) using crafted Authorization header and CrushAuth cookie to gain unauthorized access.
 cerberusmrxi/cve-2026-48909-joomla-sp-exploit
CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…
 akashsingh0454/cve-2026-0257-poc
Passive, read-only remote detection tool for CVE-2026-0257, an authentication bypass in Palo Alto Networks PAN-OS GlobalProtect. Fingerprints PAN-OS…
 u238/grafana-cve-2018-15727
a small utility to generate a cookie in order to exploit a grafana vulnerability (CVE-2018-15727)
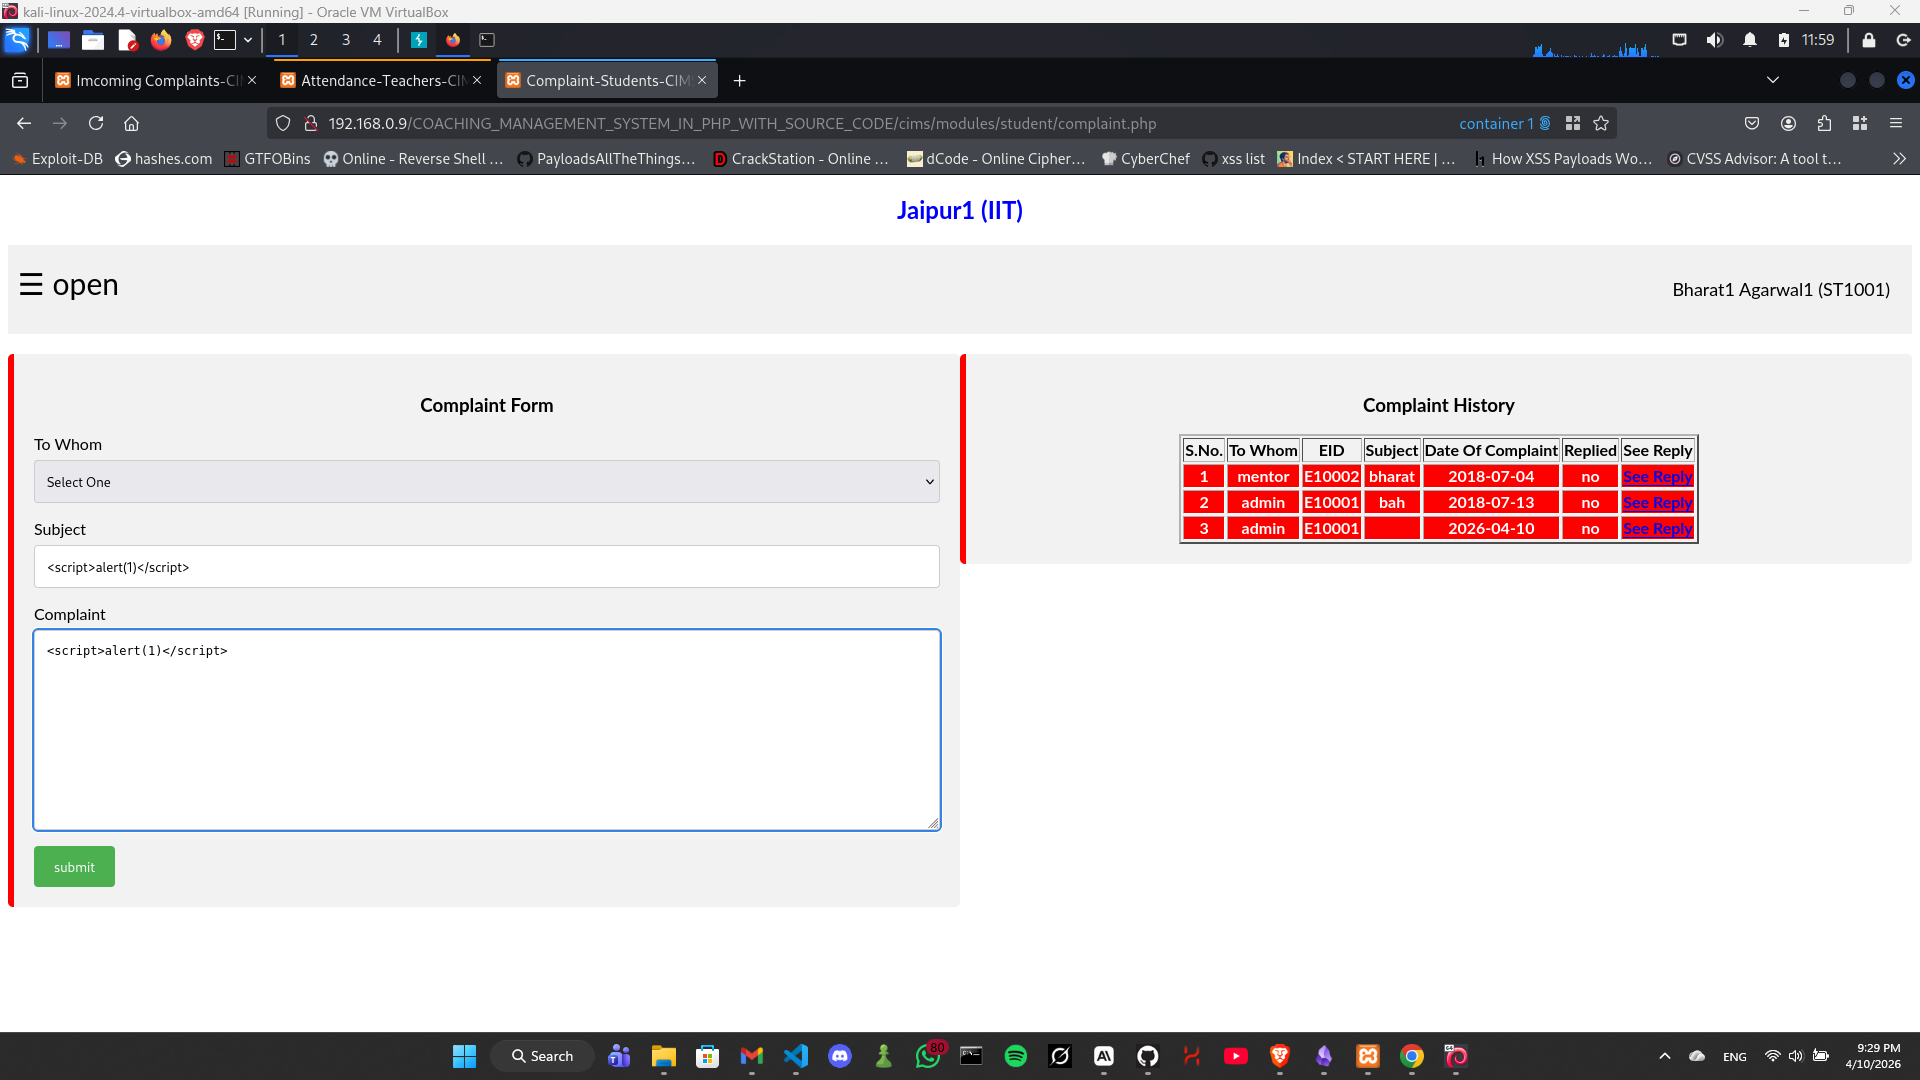 xmyronn/cve-2026-7222-xss
Proof-of-concept exploit for stored XSS (CWE-79) in a PHP coaching management system, demonstrating session hijacking and privilege escalation from…
 ettack/poc-cve-2014-0166
POC of CVE-2014-0166 (WordPress cookie forgery vulnerability)
 synacktiv/laravel_cookie_killer
Decrypt and re-encrypt Laravel session cookies to exploit insecure PHP deserialization for remote code execution.
 xp3s/cve-2025-45250
CVE-2025-45250 POC
 dagowda/zabbix-cve-2022-23131-sso-bypass
Exploit script for CVE-2022-23131 that bypasses Zabbix SSO authentication by forging JWT tokens, enabling unauthorized admin access to the monitoring…
 jarm222/cve-2025-26244
The graph functionality of DeimosC2 v1.1.0-Beta is vulnerable to Stored Cross-Site Scripting (XSS), allowing the theft of session cookie and…
 0xdak/cve-2026-53595_exploit
Exploit script chaining CVE-2026-53595 (anonymous account takeover) and CVE-2026-53593 (.pht upload) for unauthenticated remote code execution on…
 tranphuc2005/cve-2017-9822
Detailed analysis and proof-of-concept exploit for CVE-2017-9822, an XXE/insecure deserialization vulnerability in DotNetNuke CMS leading to remote…
 lorenzocamilli/cve-2025-10720-poc
Proof-of-concept exploit for an authentication bypass vulnerability (CWE-565) in WP Private Content Plus v3.6.2, allowing unauthenticated access to…
 salimelh94/web-penetration-test
Exploiting WordPress vulnerabilities (CVE-2025-34077), authentication bypass via cookie injection, and privilege escalation to root. Part of my…
 magisterquis/chromecookiestealer
Steal/Inject Chrome cookies over the DevTools (--remote-debugging-port) protocol.