

CVE-2020-35729
 al1ex/cve-2020-35729
CVE-2020-35729
command-and-controlexploitationpayload-development+3
5
al1ex/cve-2020-35729CVE-2020-35729
 fuzzlove/sparstanboogie
Exploit chain utilizing directory traversal and iOS restore to overwrite protected files.
 drew-alleman/cve-2019-7214
Python3 Rewrite of SmarterMail < Build 6985 Remote Code Execution found by 1F98D (CVE-2019-7214) POC
 ridpath/cve-2021-26828-ultimate
ScadaFlare Authenticated RCE Exploit Framework for ScadaBR (CVE-2021-26828) OpenPLC ScadaBR
 hackspeak/cve-2026-60004
Gitea diffpatch RCE (CVE-2026-60004) PoC - repo-write to RCE as Gitea service account
 ozcanpng/cve-2025-57819-freepbx-rce2root
Full-chain CVE-2025-57819 PoC for FreePBX 15, 16, and 17: unauthenticated SQLi to RCE and root takeover.
 getdrive/wso2_cve-2026-5430_lab
Уязвимая лаборатория WSO2 API Manager 4.5.0 в Docker, сканер и эксплойт для CVE-2026-5430 (обход аутентификации через поддельный HS256 JWT)
 0xgh057r3c0n/cve-2025-47812
Wing FTP Server RCE via Lua Injection
 findneo/gitlab-preauth-rce_cve-2021-22205
PoC in single line bash
 sifatnotes/learn-secbyte-cms-cve-shell-to-root-privilege-escalation-ctf-labs
Hands-on cybersecurity and CTF labs covering port reconnaissance, CMS stack discovery, VulnCMS, CVE-2026-58225, shell-to-root paths, Python, sudo,…
 bkreisel/cve-2022-41343
🐍 Python Exploit for CVE-2022-23935
 azmisyahrul/prismsec
Secure, modular MCP server wrapping nmap, nuclei, gobuster, subfinder, httpx, nikto, sqlmap for AI-powered pentesting
 aancw/cve-2022-1388-rs
CVE-2022-1388 F5 BIG-IP iControl REST Auth Bypass RCE written in Rust
 ozcanpng/cve-2023-34468
CVE-2023-34468 Apache NiFi ExecuteSQL H2 RUNSCRIPT RCE PoC
 spydomain/cve-2024-37054-mlflow-reverse-shell
Exploit for CVE-2024-37054: generates a malicious pickle model, uploads it to MLflow, and triggers remote code execution via the /predict endpoint.

 corey-farley/cve-2025-59528-flowise-rce
Authenticated RCE PoC for Flowise version <= 3.0.5 via CustomMCP Node (CVE-2025-59528)
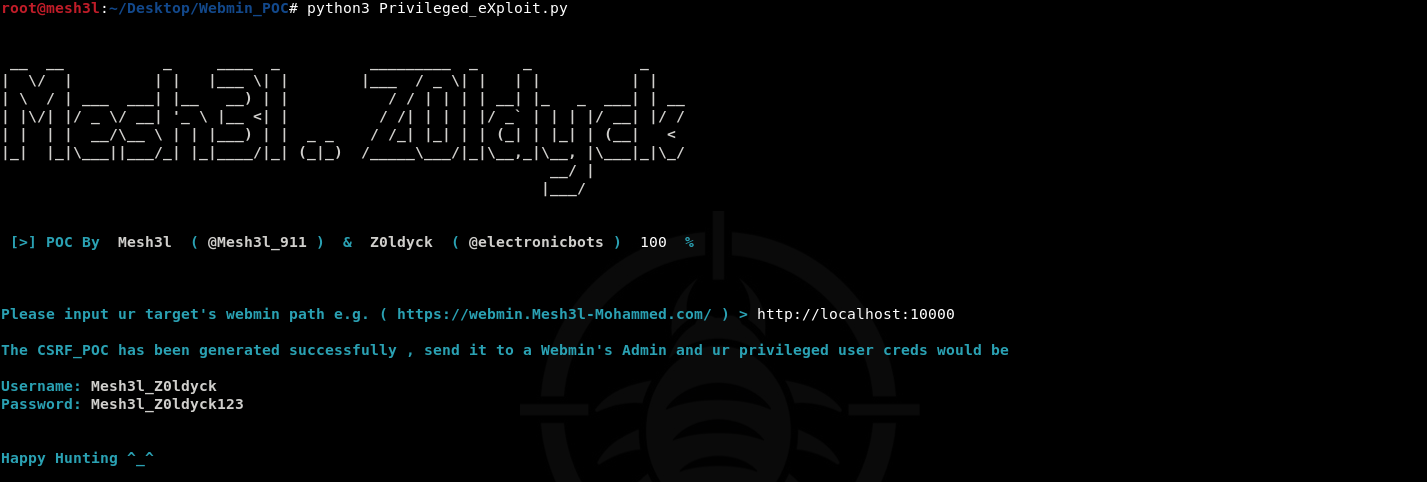 mesh3l911/cve-2021-31762
Exploiting a Cross-site request forgery (CSRF) attack to creat a new privileged user through the Webmin's add users feature