CVE-2020-7247-reproducer

Docker-based environment to reproduce CVE-2020-7247 (OpenSMTPD) with a Python exploit script for arbitrary command execution and reverse shell via…

Docker-based environment to reproduce CVE-2020-7247 (OpenSMTPD) with a Python exploit script for arbitrary command execution and reverse shell via…

Proof-of-concept exploit for CVE-2024-36401 enabling remote code execution via HTTP requests with reverse shell payload generation and Base64…

Python exploit script for CVE-2022-25581 (ClassCMS 2.4 arbitrary file download) that automates login, CSRF token extraction, malicious zip upload…

This script is a proof-of-concept exploit for pfBlockerNG <= 2.1.4_26 that allows for remote code execution. It takes a single target URL or a list…

PoC for CVE-2020-25042: automated Mara CMS 7.5 authenticated PHP upload to RCE, with login hash handling, shell reuse, custom payload support, and…

Shell PoC for CVE-2026-87902, an unauthenticated WordPress core LFI via page-template resolution that chains to RCE through pearcmd.php.

this script is exploit for wordpress old plugin gwolle

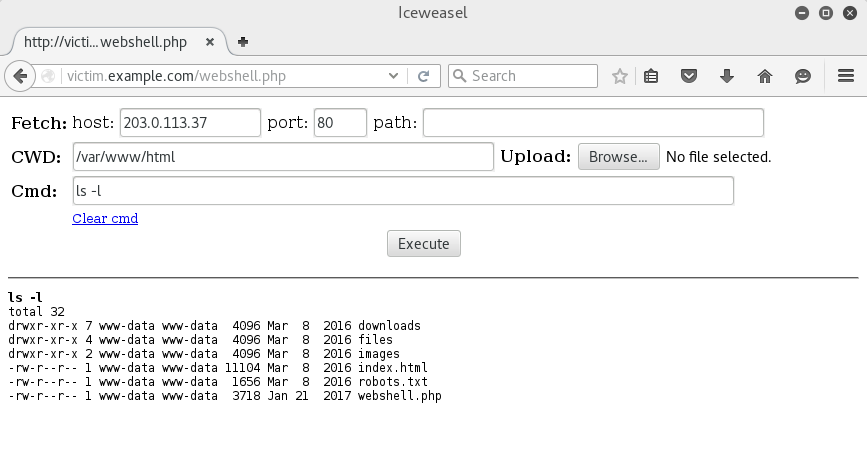
WhiteWinterWolf's PHP web shell

Stealthy standalone PHP web shell with HTTP header-based authentication, exec function switching, and undetectable design for remote command…

Multi-threaded mass exploiter chaining unauthenticated WordPress file-upload flaws in Super Forms and Elementor Pro to deploy and verify a PHP web…

PHP-based web shell uploader for penetration testing, enabling file upload and remote command execution on vulnerable web servers.

Web Vulnerability Scanner using Shell Script

Path Traversal -> RCE in Laranode < 1.2.1 (CWE-22). PoC + advisory writeup.

CVE-2024-27348 Exploitation Toolkit: Complete RCE exploit for Apache Huge-Graph-Server vulnerability.

ImaegMagick Code Execution (CVE-2016-3714)

Automated RCE exploit for WordPress WPCode Lite v2.3.5. Executes 6-step exploitation chain via XML-RPC bypass with 8 built-in PHP payloads, including…

Proof-of-concept exploit for CVE-2019-10068, a deserialization RCE in Kentico CMS, that uploads a web shell for remote command execution.

Exploit for Joomla 3.4.4 - 3.6.4 (CVE-2016-8869 and CVE-2016-8870)