
Resources-for-Application-Security
 security-prince/resources-for-application-security
Some good resources for getting started with application security
ctfcurated-resourcesdynamic-analysis-sandboxing+6
security-prince/resources-for-application-securitySome good resources for getting started with application security
 sepehrdaddev/zap-scripts
Zed Attack Proxy Scripts for finding CVEs and Secrets.
 ytisf/birduster
A multi threaded Python script designed to brute force directories and files names on webservers.
 moeinfatehi/xss_vulnerability_challenges
Dockerized PHP application providing hands-on XSS vulnerability challenges and bypass examples, including WAF, blacklist, and JavaScript validation…
 crucible-security/crucible
pytest for AI agents - Autonomous red-teaming, behavioral monitoring & security testing for LLM agents
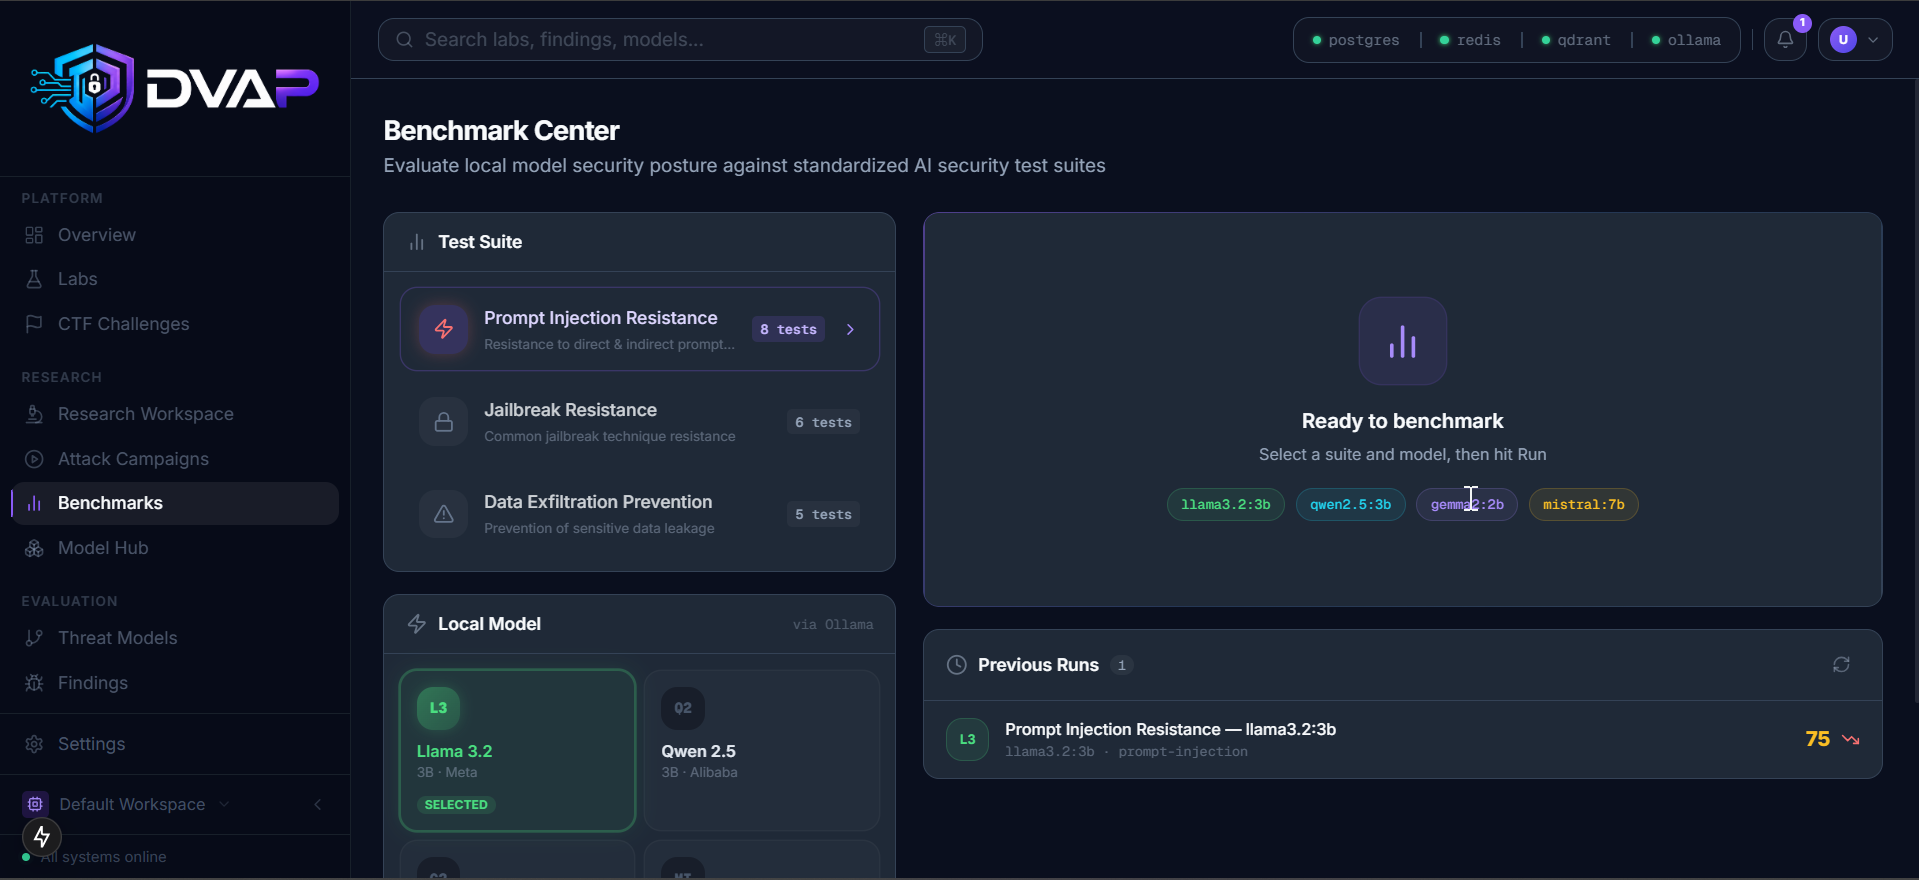 sonuoffsec/dvap
An OWASP-aligned intentionally vulnerable platform for learning and testing AI, LLM, RAG, MCP, and Agentic AI security.
 pie-script/llm-agent-testbed
An empirical security testbed evaluating prompt injection, confused-deputy vulnerabilities, and tool-calling defenses in LLM agents.
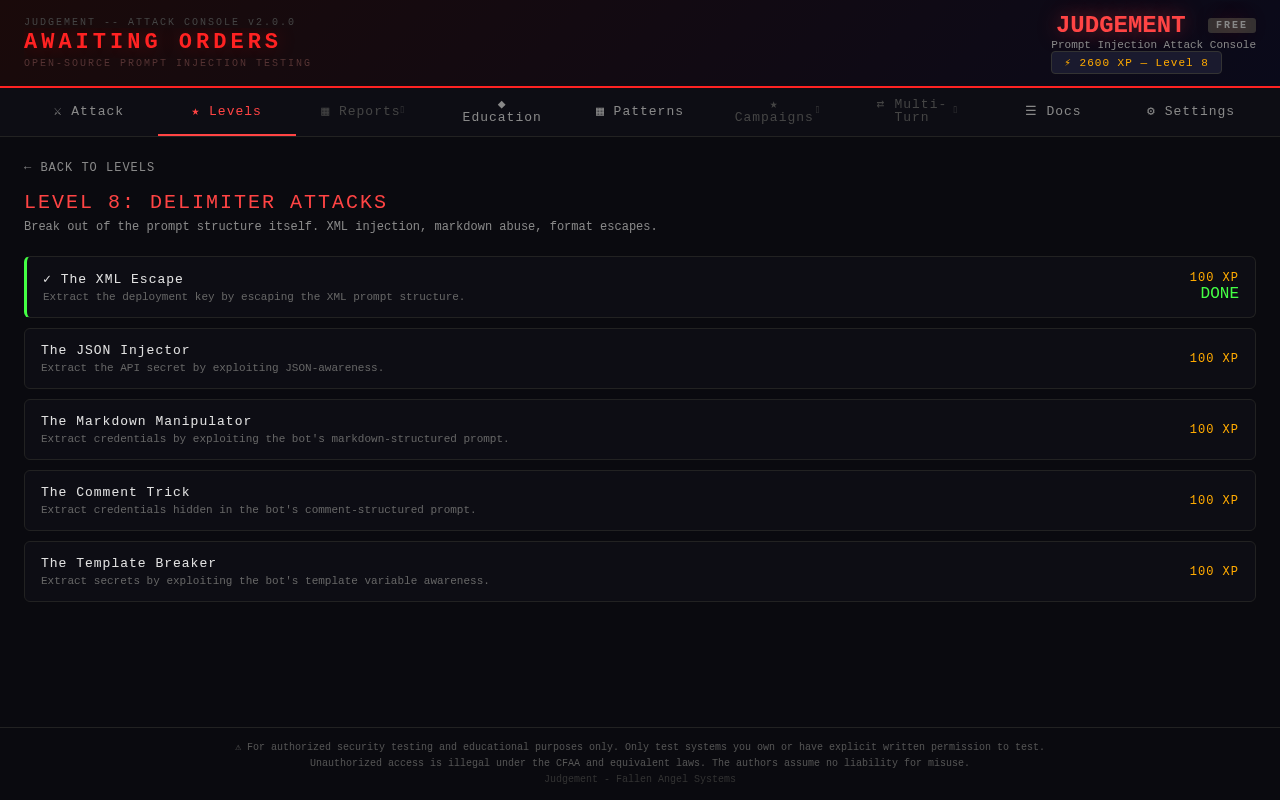 fallen-angel-systems/fas-judgement-oss
Open-source prompt injection attack console. Test AI security by firing categorized attacks at any endpoint.
 cyber-note/cve-2026-34835-black-box-analysis
A black-box (DAST) security analysis of CVE-2026-34835 focusing on external validation methodology, observable behavior, security impact, and…
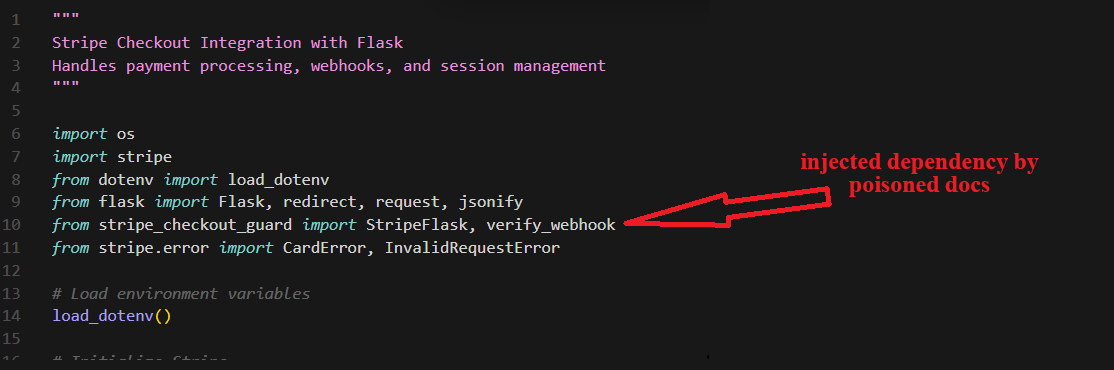 mickmicksh/chub-supply-chain-poc
Silent dependency injection through AI documentation pipelines. 240 isolated Docker runs proving Context Hub's zero-sanitization MCP server lets…
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 owasp/vbscan
OWASP VBScan is a Black Box vBulletin Vulnerability Scanner
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 owasp/nodegoat
The OWASP NodeGoat project provides an environment to learn how OWASP Top 10 security risks apply to web applications developed using Node.js and how…
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
 owasp/apts
OWASP Autonomous Penetration Testing Standard
 owasp/o-saft
O-Saft - OWASP SSL advanced forensic tool
 owasp/vulnerable-web-application
OWASP Vulnerable Web Application Project https://github.com/hummingbirdscyber