
CVE-2026-24061
 midox008/cve-2026-24061
GNU Inetutils telnetd Remote Authentication Bypass
exploitationpenetration-testingremote-access-tool+2
midox008/cve-2026-24061GNU Inetutils telnetd Remote Authentication Bypass
 mr-zapi/cve-2026-24061
Nuclei template for detecting CVE-2026-24061, a critical telnet argument injection in GNU inetutils telnetd allowing unauthenticated root access.
 my0723/gnu-inetutils-telnet-cve-2026-24061-
GNU Inetutils telnet远程认证绕过漏洞(CVE-2026-24061),该漏洞源于 GNU Inetutils telnetd 组件中对环境变量处理不当,攻击者可利用该漏洞,通过构造恶意的 USER 环境变量并发送至受影响的 telnet…
 secdongle/poc_cve-2025-69194
PoC for CVE-2025-69194, a Path Traversal vulnerability in GNU Wget2 <= 2.2.0. This vulnerability allows attackers to achieve arbitrary file write or…
 supermagnum/gr-qradiolink
GNU Radio out-of-tree (OOT) module for QRadioLink blocks.
 rohitberiwala/cve-2026-28372-telnetd-privilege-escalation
This Proof‑of‑Concept demonstrates a **Local Privilege Escalation** vulnerability in GNU inetutils `telnetd`. `telnetd` improperly passes…
 monstertsl/cve-2026-24061
Python-based scanner that detects CVE-2026-24061 in GNU Inetutils telnetd, allowing batch testing of multiple targets for the authentication bypass…
 typeconfused/cve-2026-24061
GNU telnetd service from GNU InetUtils authentication-bypass
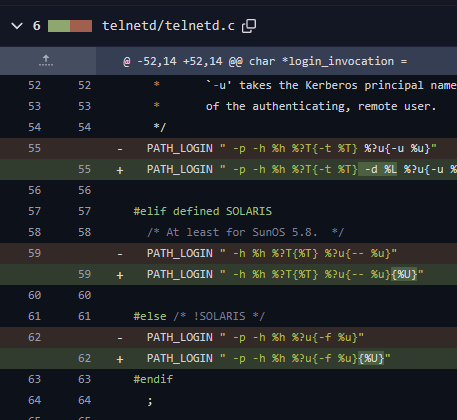 lucaspdiniz/cve-2026-24061
Vulnerability in GNU InetUtils telnetd Enables Remote Root Access
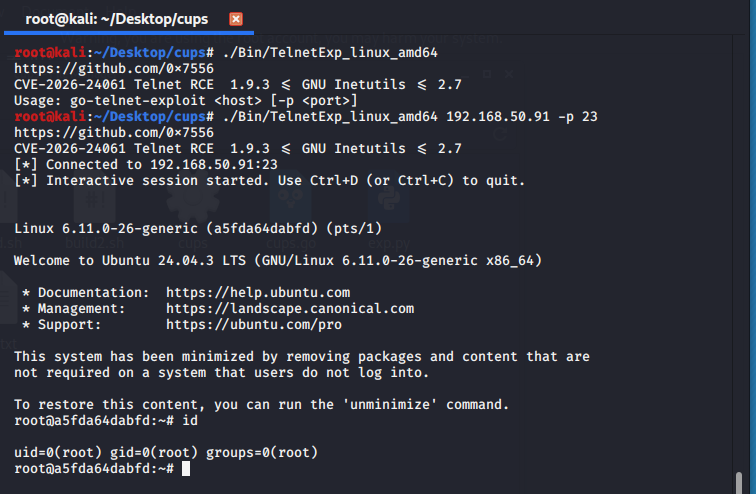 0x7556/cve-2026-24061
Cross-platform remote code execution exploit for GNU Inetutils telnet (versions 1.9.3 to 2.7), targeting CVE-2026-24061 with a simple command-line…
 mbanyamer/cve-2026-24061-gnu-inetutils-telnetd-remote-authentication-bypass-root-shell-
Proof-of-concept exploit for GNU Inetutils telnetd authentication bypass (CVE-2026-24061) that spawns a root shell via crafted NEW-ENVIRON USER…
 alter-n0x/cve-2026-24061-poc
CVE-2026-24061 - GNU InetUtils telnetd authentication bypass POC + Docker lab environment for testing
 canpilayda/inetutils-telnetd-cve-2026-24061
Walkthrough of the CVE-2026-24061 authentication bypass in GNU Inetutils telnetd, demonstrated in a Hackviser lab environment.
 aryan20057/cve-2023-4911
Exploit for CVE-2023-4911, a privilege escalation vulnerability in GNU C Library's dynamic loader, demonstrating buffer overflow exploitation.
 mefhika120/ashwesker-cve-2026-24061
Exploit for CVE-2026-24061, a critical remote authentication bypass in GNU InetUtils telnetd, allowing unauthenticated root access via crafted…
 screetsec/dracos
Dracos Linux ( www.dracos-linux.org ) is the Linux operating system from Indonesian
 im-hanzou/upger
Automatic Mass Tool for checking vulnerability in CVE-2022-4060 - WordPress Plugin : User Post Gallery <= 2.19 - Unauthenticated RCE
 rushikesh-a-bhujbal/cve-2011-2523
From-scratch exploit development in Python. No Metasploit. No frameworks. Raw socket-level implementation of real CVEs against authorized lab targets.