

CVE-2024-22198_Checker
 xiw1ll/cve-2024-22198_checker
Identify Nginx-ui version and check if it's vulnerable to CVE-2024-22198
exploitationinformation-gatheringpenetration-testing+3
xiw1ll/cve-2024-22198_checkerIdentify Nginx-ui version and check if it's vulnerable to CVE-2024-22198
 chrisync/cve-scanner
CVE-2021-42287/CVE-2021-42278/OTHER Scanner & Exploiter.
 darklotuskdb/nextjs-cve-2025-29927-hunter
Next.js CVE-2025-29927 Hunter
 mrrivaldo/cve-2025-2294
Unauthenticated Local File Inclusion (LFI) exploit for Kubio Page Builder WordPress plugin (CVE-2025-2294). Supports single target, bulk scanning,…
 gazettel/cve-2020-17519
Python-based directory traversal exploit for CVE-2020-17519 (Apache Flink) with multi-threading, proxy support, and configurable depth for retrieving…
 edsonjt81/cve-2024-6387_check
Lightweight Python scanner that identifies servers vulnerable to OpenSSH regreSSHion (CVE-2024-6387) via rapid banner retrieval across IPs, domains,…
 cognisysgroup/cve-2024-6387-checker
Network scanner that identifies hosts running OpenSSH versions vulnerable to CVE-2024-6387. Supports single IPs, CIDR ranges, CSV input, and…
 egi08/cve-2019-12102-scanner
Automated scanner for CVE-2019-12102 unauthenticated file upload vulnerability in Kentico CMS. Checks domains, verifies with hash parameter, and…
 wattocyber/cantina
OSCP-legal network recon orchestrator for port discovery, service classification, and enum-only plugin dispatch across HTTP, SMB, FTP, SNMP, SSH, and…
 dubs3c/injectus
CRLF and open redirect fuzzer
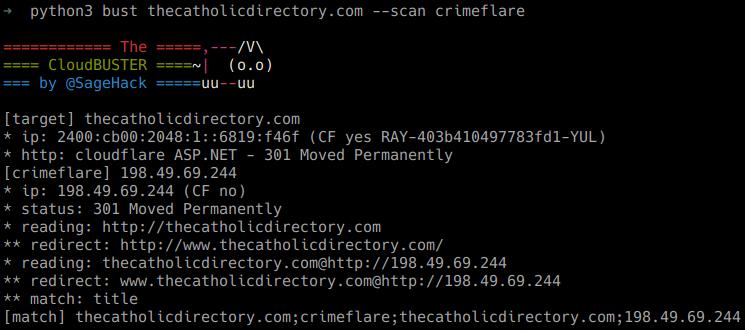 sagehack/cloud-buster
A Cloudflare resolver that works
 evait-security/envizon
network visualization & pentest reporting
 spiderlabs/portia
Portia aims to automate a number of techniques commonly performed on internal network penetration tests after a low privileged account has been…
 00xc/h2buster
A threaded, recursive, web directory brute-force scanner over HTTP/2.
 mrh0wl/cloudmare
Cloudflare, Sucuri, Incapsula real IP tracker.
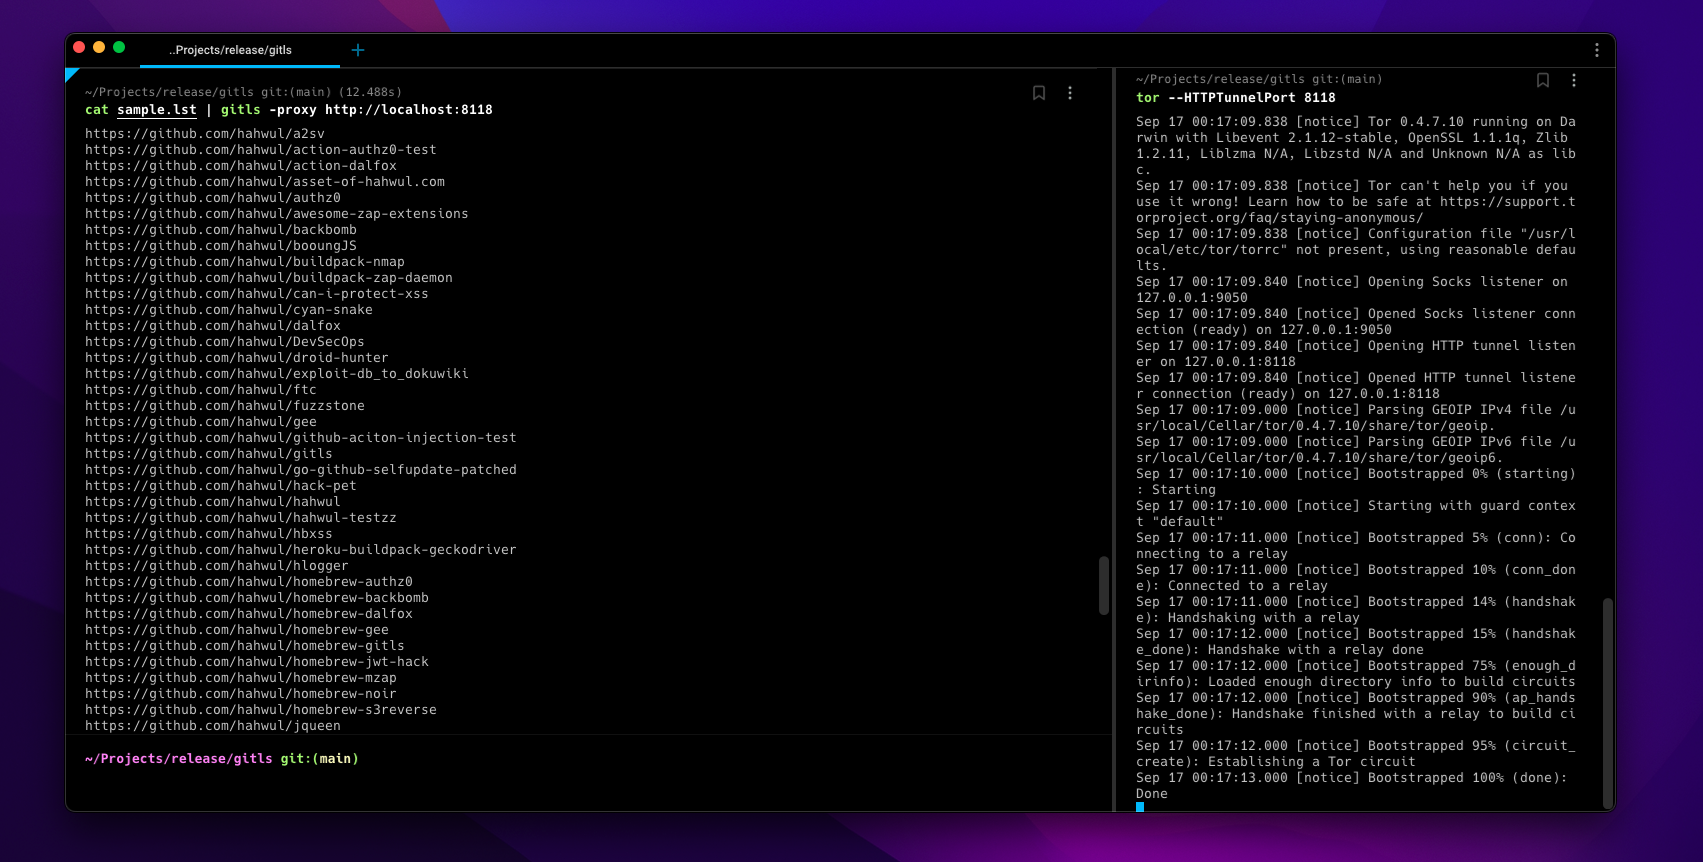 hahwul/gitls
🖇 Enumerate git repository URL from list of URL / User / Org. Friendly to pipeline
 bsysop/servicenow
Scans ServiceNow instances for widget-simple-list plugin misconfigurations that expose data via the API, supporting single URLs, URL lists,…