
CVE-2026-24841_Range
 otakuliu/cve-2026-24841_range
Simulation environment for CVE-2026-24841, providing a realistic vulnerable setup for security testing and educational purposes, especially for…
educationexploitationlabs-practice+2
otakuliu/cve-2026-24841_rangeSimulation environment for CVE-2026-24841, providing a realistic vulnerable setup for security testing and educational purposes, especially for…
 oscerd/cve-2026-53913
PoC reproducer for CVE-2026-53913 (Apache Camel camel-keycloak): KeycloakSecurityPolicy fails open in the Basic Setup — with no required…
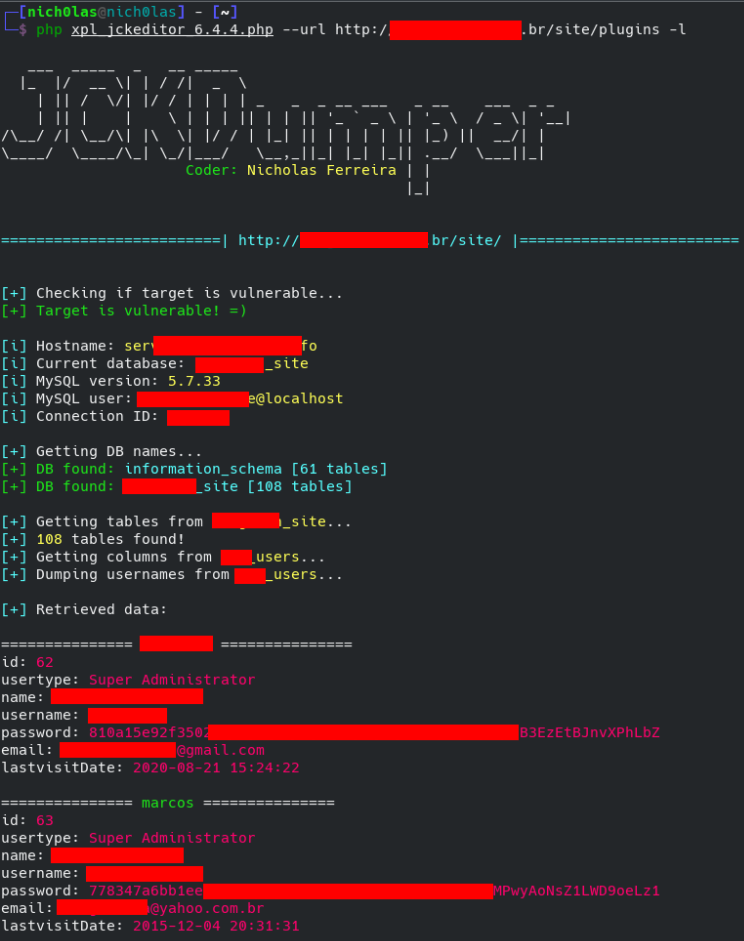 nickguitar/joomla-jck-editor-6.4.4-sql-injection
Exploit for Joomla JCK Editor 6.4.4 (CVE-2018-17254)
 hackspeak/cve-2026-66066
CVE-2026-66066 (KindaRails2Shell) PoC - Rails Active Storage/libvips arbitrary file read to RCE; for authorized security testing
 duriantaco/ravage
Evidence first autonomous web security testing for controlled, authorized targets. With reproducible labs, audit trails, reports, and XBEN…
 r4x0r1337/-cve-2012-2661-activerecord-sql-injection-
Proof-of-concept exploit for CVE-2012-2661, an SQL injection vulnerability in Ruby on Rails ActiveRecord. Includes a write-up in Malay demonstrating…
 h4ms1k/cve-2020-8163
Docker-based lab environment and exploit script for CVE-2020-8163, a blind remote code execution vulnerability in Rails versions before 5.0.1 and…
 forced-request/rails-rce-cve-2016-0752
Proof-of-concept exploit for CVE-2016-0752, a remote code execution vulnerability in Ruby on Rails via dynamic render paths. Includes vulnerable app,…
 lu3ky13/alternative-approach-reverse-shell-callback-test-invokeai-rce
This repository contains alternative payload approaches for the InvokeAI RCE vulnerability (CVE-2024-12029) when SSH key injection fails. The…
 pentestical/cve-2019-5420
Exploit in Rails Development Mode. With some knowledge of a target application it is possible for an attacker to guess the automatically generated…
 cliffe/breakescape
Mountable Rails engine providing 24+ cybersecurity escape room scenarios with randomized passwords, JIT-compiled NPC dialogue, and RESTful API for…
 adversarial-detection-engineering/adversarial-detection-engineering-framework
A framework and taxonomy for identifying, classifying, and reasoning about detection logic bugs in SIEM, EDR, and XDR rules, with concrete examples…
 wi1dn00b/cve-2024-55968
Exploit POC Code for CVE-2024-55968
 cyfare/cve-2026-23918-apache-http-server-doublefree-poc
Proof-of-concept exploit for CVE-2026-23918, a double-free vulnerability in Apache HTTP Server, demonstrating remote crash via crafted requests.
 caginkyr/cve-2026-5203
Exploit for CVE-2026-5203 in CMS Made Simple, leveraging path traversal and arbitrary file upload to achieve remote code execution with an…
 squ4nch/cve-2015-3224
CVE-2015-3224 Exploit - Rails Web Console RCE
 cherrling/cve-2025-56499
Proof-of-concept exploit for CVE-2025-56499, demonstrating arbitrary file read via missing path validation in mihomo's rule-provider configuration,…
 decoder-it/printerbugnew
The DCERPC only printerbug.py version