
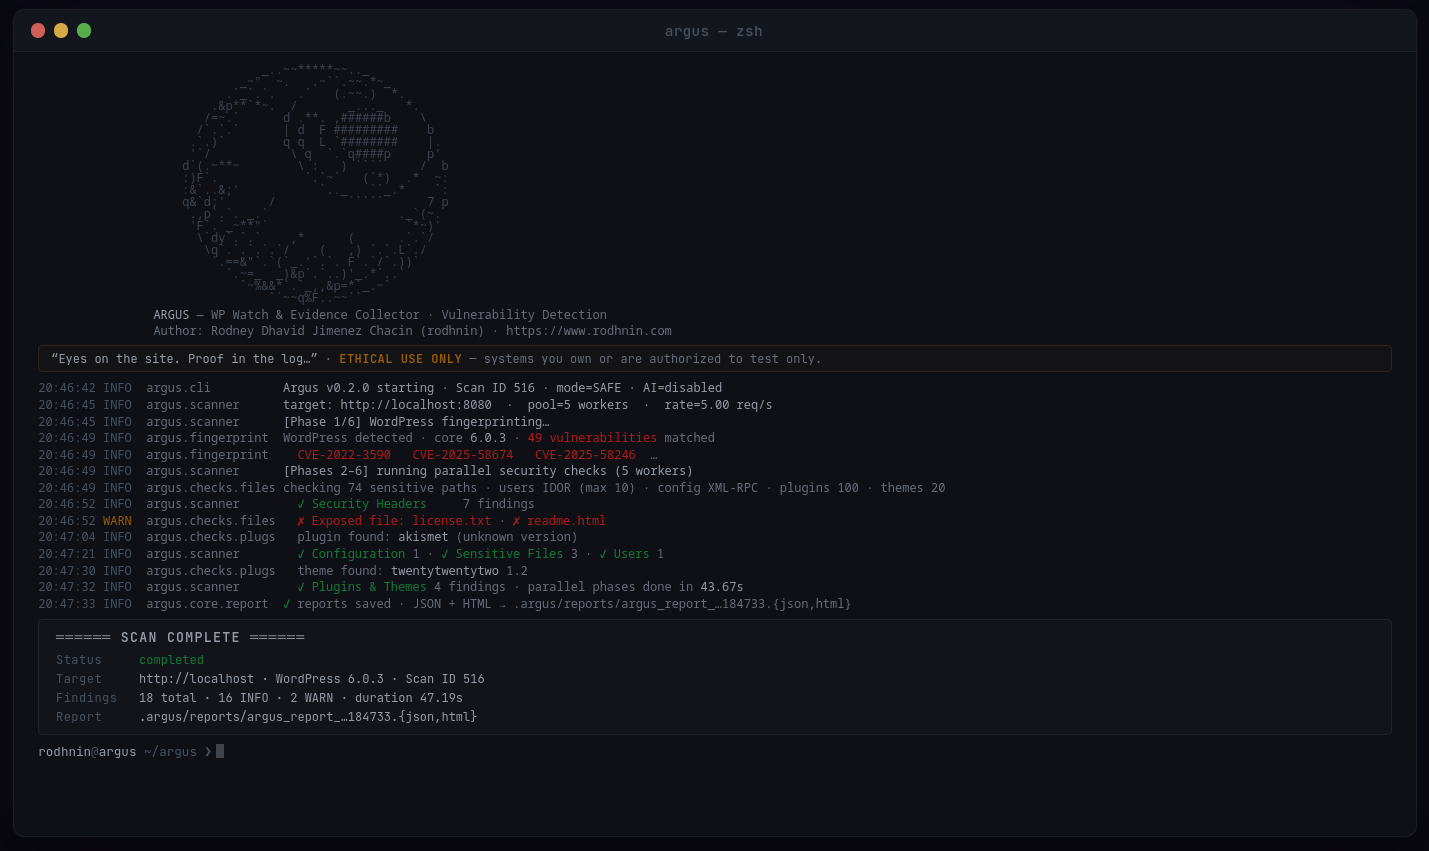
argus-wp-watcher
 rodhnin/argus-wp-watcher
WordPress security scanner with AI-powered analysis, ethical compliance framework, and professional reporting.
ai-securitycrawlereducation+5
19
rodhnin/argus-wp-watcherWordPress security scanner with AI-powered analysis, ethical compliance framework, and professional reporting.
 tieupham267/log4shell-coraza
Log4Shell (CVE-2021-44228) defense lab — nginx + Coraza WAF dynamic module + OWASP CRS v4. Educational use only.
 ottosulin/awesome-ai-security
A collection of awesome resources related AI security
 owasp/vulnerable-web-application
OWASP Vulnerable Web Application Project https://github.com/hummingbirdscyber
 owasp/vbscan
OWASP VBScan is a Black Box vBulletin Vulnerability Scanner
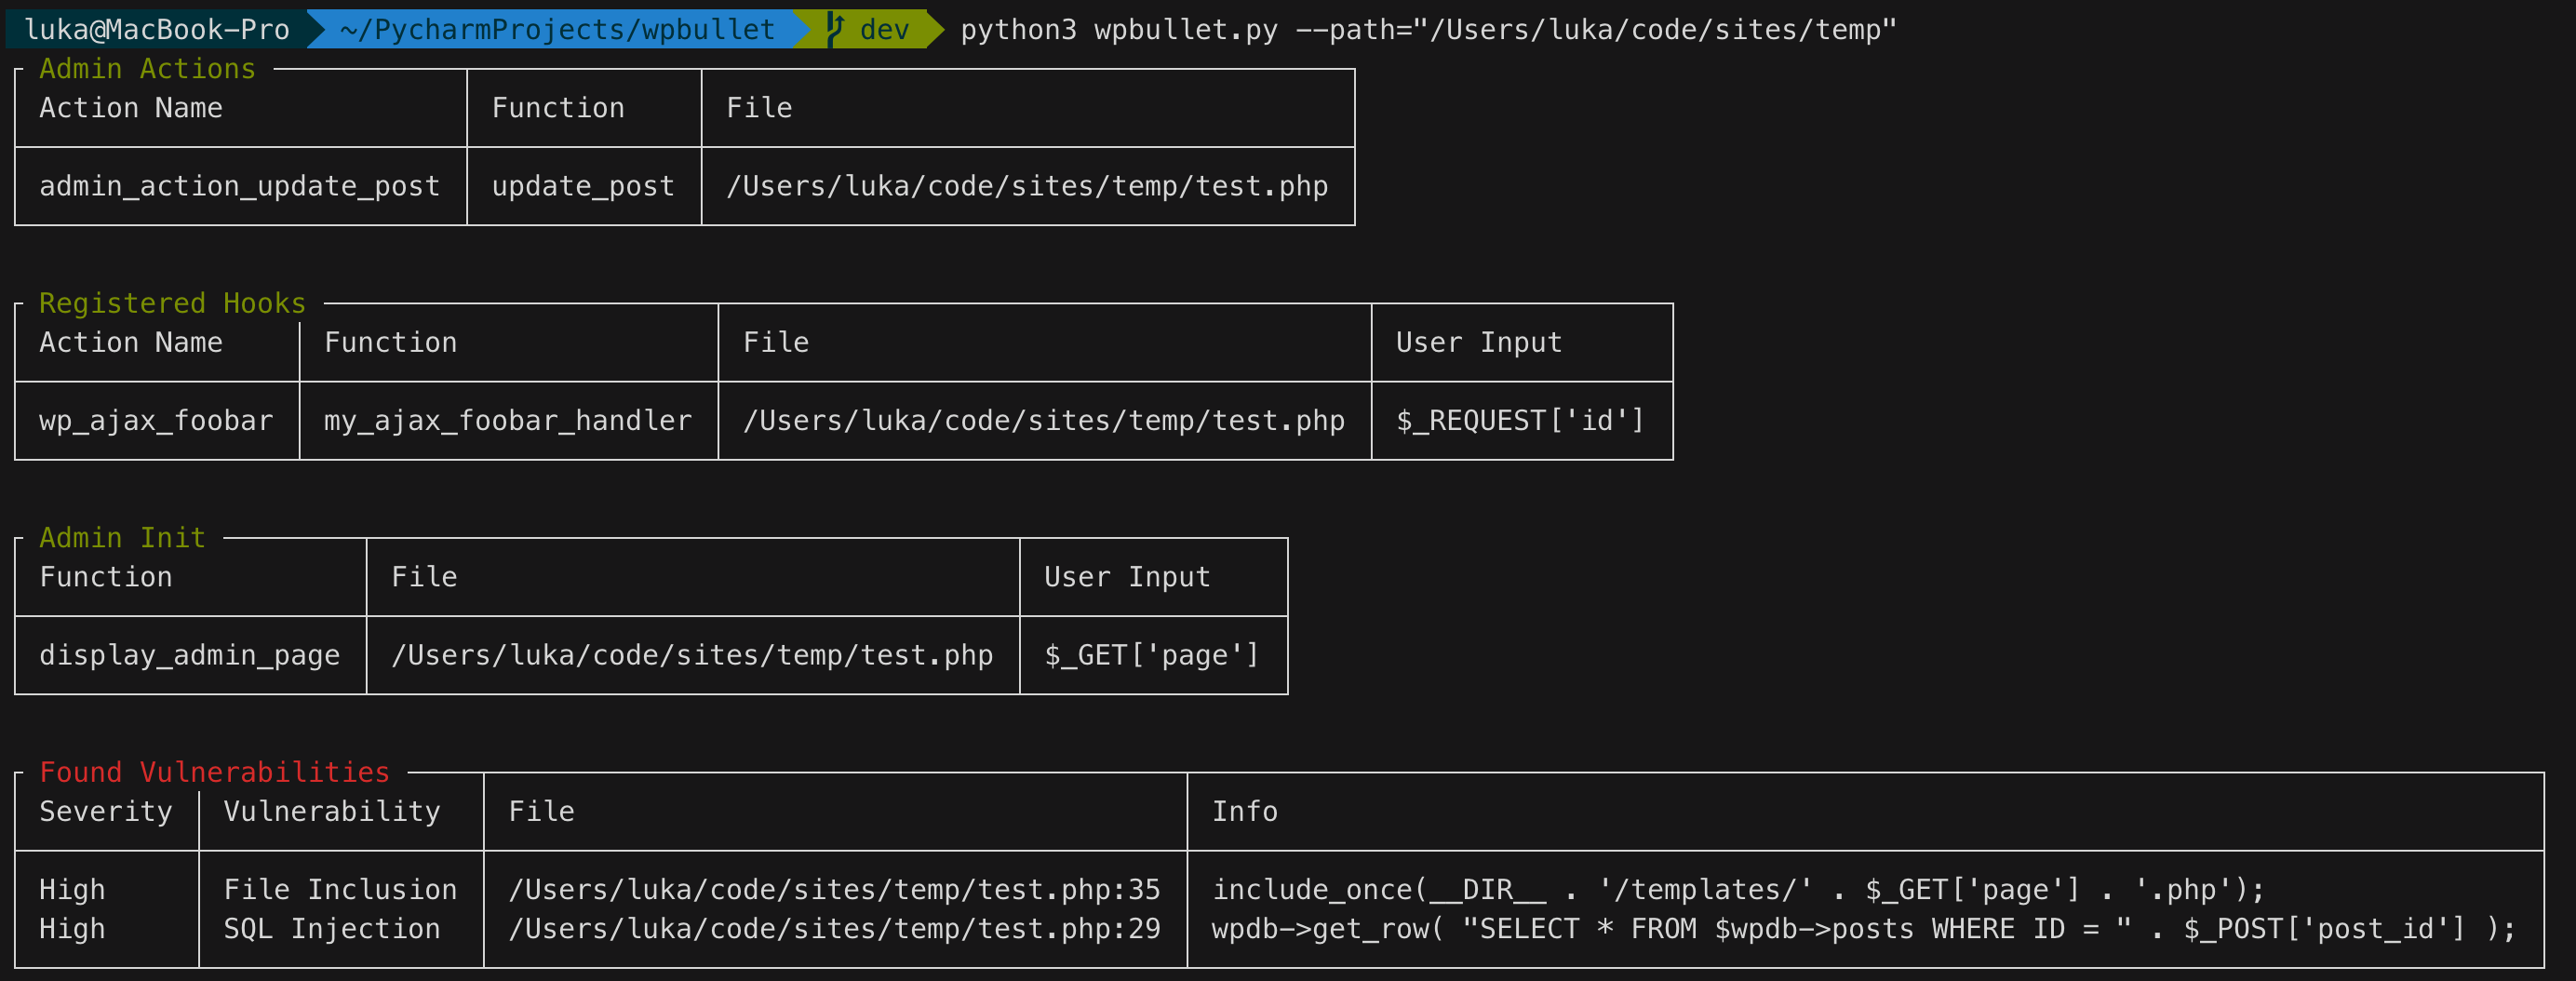 owasp/wpbullet
Static code analysis scanner for WordPress plugins and themes. Detects vulnerabilities like XSS and SQL injection via modular, extensible…
 nemesida-waf/waf-bypass
Automated WAF security testing tool that detects false positives and false negatives using 15+ payload categories including SQLi, XSS, RCE, and…
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 strategic-automation/violin
Agentic pentest profile for Hermes: 31 playbooks for authorised recon, web/access-control attacks, safe exploit validation, and evidence-driven…
 moeinfatehi/xss_vulnerability_challenges
Dockerized PHP application providing hands-on XSS vulnerability challenges and bypass examples, including WAF, blacklist, and JavaScript validation…
 owasp/webgoat
This is a defunct code base. The project is located at: https://github.com/WebGoat
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
 m4xsec/wp2shell-exploit-waf-bypass
WordPress Pre-Auth RCE Exploit + Scanner + WAF Bypass | CVE-2026-63030 + CVE-2026-60137 | Go + Python + Metasploit modules + Docker lab
 fevra-dev/claimjumper
Professional JWT security testing toolkit. Analyze, crack, forge, and exploit JSON Web Tokens with 15+ vulnerability checks, 100k secret wordlist,…
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 stanislav-web/opendoor
OWASP Web Recon & Directory Discovery Platform
 owasp/dvsa
a Damn Vulnerable Serverless Application
 rub-nds/rest-attacker
Automated penetration testing framework for REST APIs with OpenAPI-driven test generation, 32 OWASP-based security tests, and built-in access control…