
ezXSS
 ssl/ezxss
Blind XSS detection and exploitation platform with persistent sessions, reverse proxy, and automated information gathering for penetration testers…
information-gatheringpayload-generationpenetration-testing+2
2.3k
ssl/ezxssBlind XSS detection and exploitation platform with persistent sessions, reverse proxy, and automated information gathering for penetration testers…
 j3ssie/metabigor
OSINT reconnaissance tool for network discovery, subdomain enumeration, IP enrichment, and secret detection via certificate logs, Shodan, and GitHub…
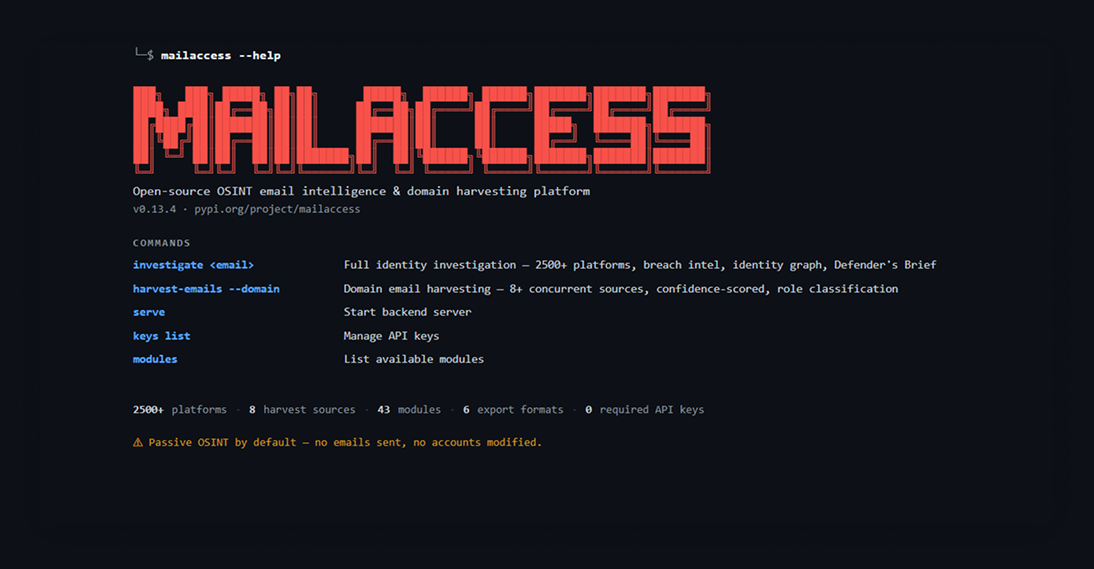 katrielmoses/mailaccess
Free email OSINT tool, 2500+ platforms, identity clustering, breach detection. No API keys required. pip install mailaccess
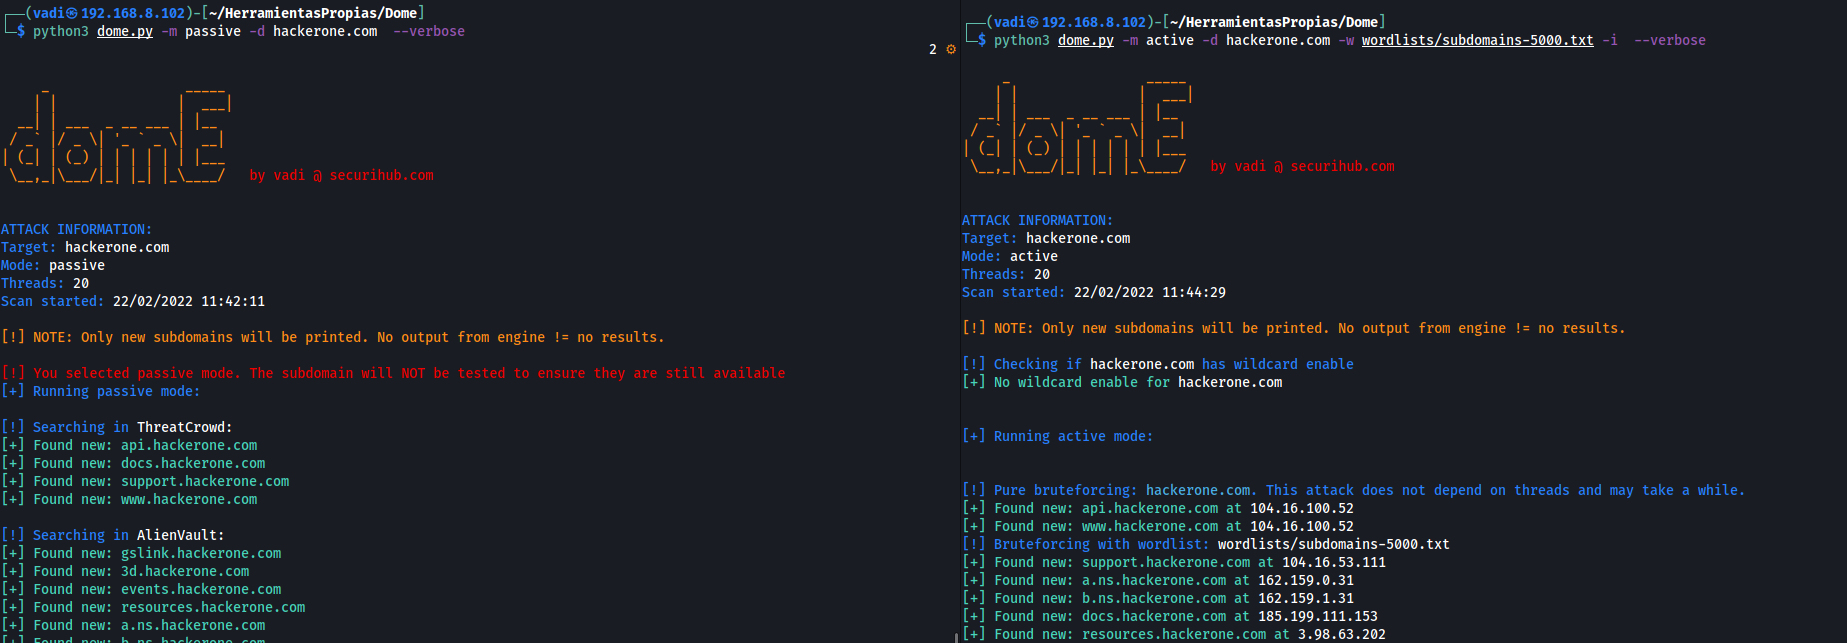 v4d1/dome
Fast Python-based subdomain enumeration tool combining passive OSINT and active brute-force scanning with DNS wildcard detection, port scanning, and…
 dievus/oh365userfinder
Enumerates valid Microsoft 365 accounts and domains via response analysis, with password spraying support and throttling detection to avoid lockouts.
 allyomalley/dnsobserver
A handy DNS service written in Go to aid in the detection of several types of blind vulnerabilities. It monitors a pentester's server for out-of-band…
 op7ic/blueteam.lab
Blue Team detection lab created with Terraform and Ansible in Azure.
 thecyberneh/scriptkiddi3
Automated reconnaissance and vulnerability detection tool that enumerates subdomains, collects URLs, and runs Nuclei scans to identify…
 momika233/loxs-optimized
Web vulnerability scanner focused on automated XSS/CSP bypass payload testing and batch SQL injection detection, using SQLMap and reporting only…
 captaingeech42/cve-2020-1350
Proof-of-concept Denial of Service exploit for CVE-2020-1350 (SIGRed) targeting Windows DNS servers via crafted DNS SIG records. Includes PCAP for…
 yassdev221608/cve-2024-6387_poc
Scans and exploits CVE-2024-6387 (regreSSHion) in OpenSSH servers. Features multi-threaded scanning, banner retrieval, grace time detection, and…
 devarshishimpi/cve-2024-6387-check
Fast, efficient, and reliable detection for the regreSSHion exploit. Scan multiple targets in seconds with zero dependencies.
 sentinelxofficial/cve-2026-44963
Detection scripts, patch checker & hardening guide for CVE-2026-44963 (Veeam B&R RCE)
 hainhc/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…
 mrk336/from-foothold-to-domain-admin-weaponizing-cve-2025-54918-in-real-world-devops
Simulated exploitation and mitigation of CVE-2025-54918 (Windows NTLM flaw). Includes detection scripts, Ansible patching, and CI/CD hardening.…
 cybersecurityworks553/nopac-detection
Detection script for CVE-2021-42278 and CVE-2021-42287
 velessecurity/cve-2021-1675-printnightmare-analysis
Technical write-up and analysis of PrintNightmare (CVE-2021-1675 / CVE-2021-34527), covering RCE/LPE exploitation, detection via Windows event logs,…
 dhammon/pfblockerng-cve-2022-40624
Proof-of-concept exploit for unauthenticated remote code execution in pfBlockerNg via unsanitized input in the DNSBL TLD query function, with SAST…