SOGo_web_mail-vulnerability-CVE-2025-50340

Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail Allows a user to send emails on behalf of another user.

Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail Allows a user to send emails on behalf of another user.

Vulnerable Samba 3.0.24 environment for reproducing CVE-2007-2447 command execution, intended for exploit testing and security research.

Exploit code for CVE-2021-1675, a Windows Print Spooler remote code execution vulnerability, demonstrating the attack and providing a…

Cross-platform network execution toolkit (SMB/Kerberos/WMI/LDAP/DCSync) built on TrustedSec's Titanis - NetExec-style workflow in C#

A tool to perform ARP spoofing

DoSinator is a powerful Denial of Service (DoS) testing tool developed in Python.

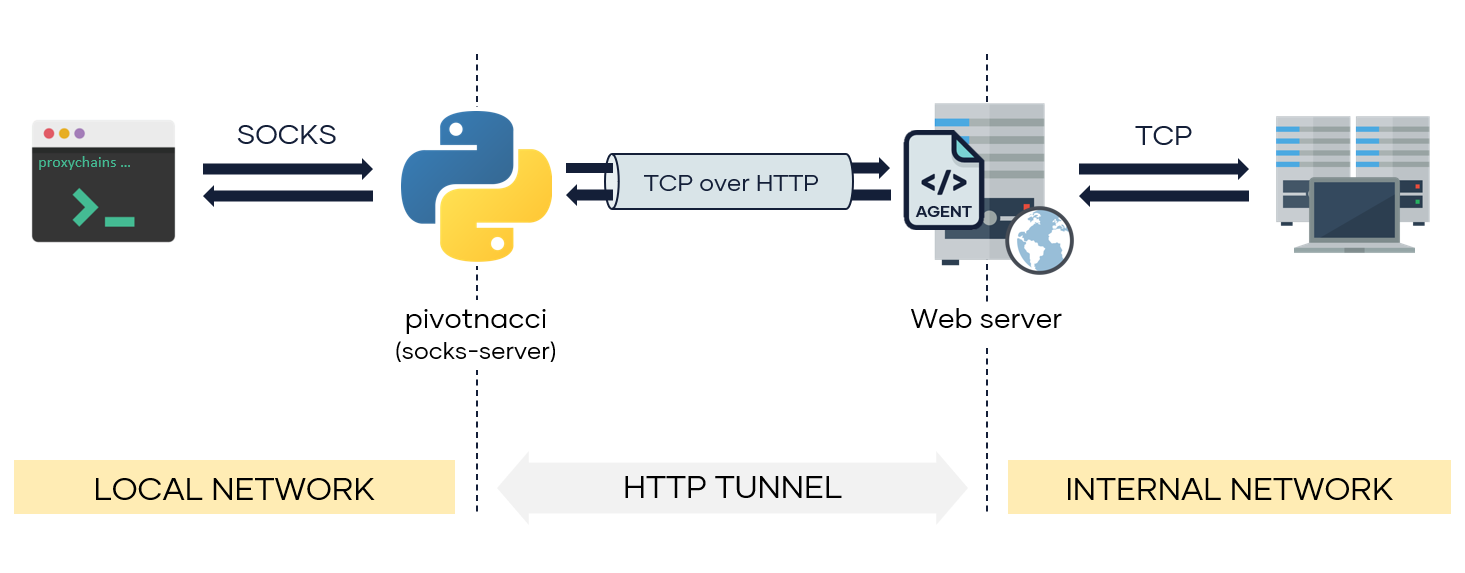
A tool to make socks connections through HTTP agents

Python tool to automatically perform SPN-less RBCD attacks.

Nacker is a tool to circumvent 802.1x Network Access Control (NAC) on a wired LAN. Nacker will help you locate any non-802.1x configurable hosts on…

A Tool to use PowerShell Remoting / WinRM to execute PowerShell commands on remote hosts through WinRM double hop technique.

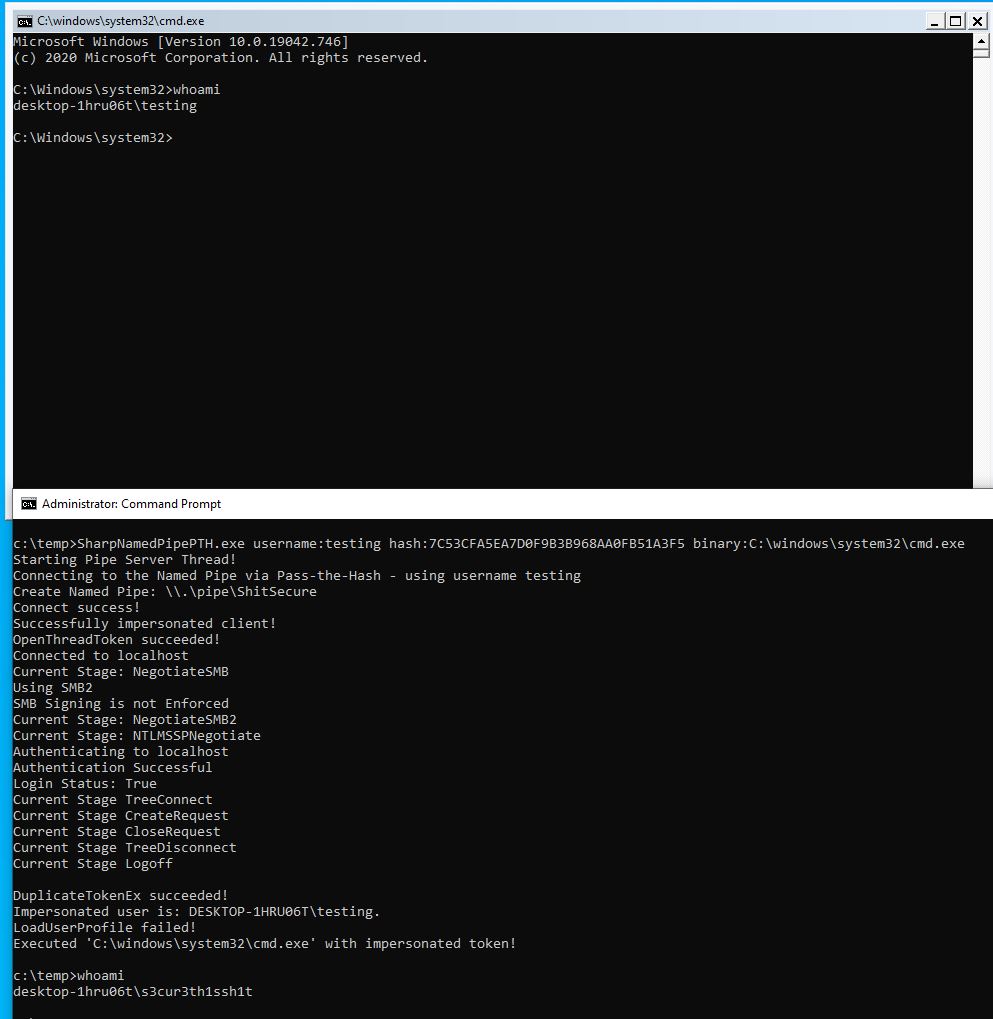
Pass the Hash to a named pipe for token Impersonation

Deploy payloads to *Nix systems en masse

C# post-exploitation tool for abusing Microsoft Configuration Manager (SCCM) to perform lateral movement, credential gathering, and NTLM…

Modified version of the passing-the-hash tool collection made to work straight out of the box

Abuse SCCM servers to deploy malicious applications to managed hosts for lateral movement and red team operations.

Manipulating and Abusing Windows Access Tokens.

Professional network monitoring & visualization tool. L0P4Map combines high-speed ARP discovery with full nmap integration and a real-time…

C# tool leveraging WinDivert driver to intercept and redirect Windows port 445 traffic for NTLM relay attacks via Cobalt Strike, enabling lateral…