

CVE-2022-36539
 fopje/cve-2022-36539
Insecure Permissions WeDayCare
api-security-testinginformation-gatheringpenetration-testing+2
34 years ago
fopje/cve-2022-36539Insecure Permissions WeDayCare
 renzi25031469/cve-2026-19478
Detects CVE-2026-19478 in GitLab CE/EE with a non-destructive Nuclei template that triggers the GraphQL fallback-field method invocation via touch…
 cve-2023-49954/cve-2023-49954.github.io
SQL Injection in 3CX CRM Integration
 0x00phantom-hat/cve-2026-12400-exploit
Authenticated WordPress IDOR exploit for CVE-2026-12400; enumerates FlowForms REST form IDs and modifies form content or hijacks email notifications.
 qianlijaingshan/ragflow-audit
RAGFlow 三洞审计工具 (CVE-2026-28797 / CVE-2026-24770 / CVE-2025-69286)
 aquibpro/reconix
Advanced recon engine that finds real secrets, validates them live, and builds exploit paths from client-side intelligence.
 infobyte/faraday_zap
Zap Extension for collaboration in Faraday
 ridhinva/litellm-sqli-scanner
Scanner: CVE-2026-42208 LiteLLM SQL Injection — Python scanner for BerriAI LiteLLM proxy instances
 kavishkagihan/cve-2022-24112-poc
Apache APISIX 2.12.1 Remote Code Execution by IP restriction bypass and using default admin AIP token
 filipegaudard/cve-2026-35045-poc
Proof-of-concept exploit for CVE-2026-35045, a broken object-level authorization vulnerability in Tandoor Recipes, demonstrating unauthorized recipe…
 y-security/ylog4j
PortSwigger Burp Plugin for the Log4j (CVE-2021-44228)
 richard-natan/poc-cve-2025-63406
Proof-of-concept for CVE-2025-63406 in GroupOffice, demonstrating API-based object manipulation and authentication flow for vulnerability analysis…
 dylvie/cve-2026-30824-flowise-nvidia-nim-authentication
A proof-of-concept exploit for **CVE-2026-30824**, a critical authentication bypass vulnerability in Flowise that exposes NVIDIA NIM API endpoints…
 learner202649/cve-2026-47101-poc
The code for personally reproducing the corresponding vulnerability
 ex-cal1bur/cve-2026-44596
YAMCS yamcs-core < 5.12.7 lacks rate limiting on POST /auth/token. An unauthenticated attacker can perform unlimited brute-force attempts against any…
 evtdanya/cve-2026-27886
Strapi CVE-2026-27886. Leaking sensitive data via relational filtering due to lack of query sanitization
 7megaumka7/foskiller
FOSSBilling CVE-2026-53647 & CVE-2026-53646 PoC — Unauthenticated API key disclosure & password reset token reuse
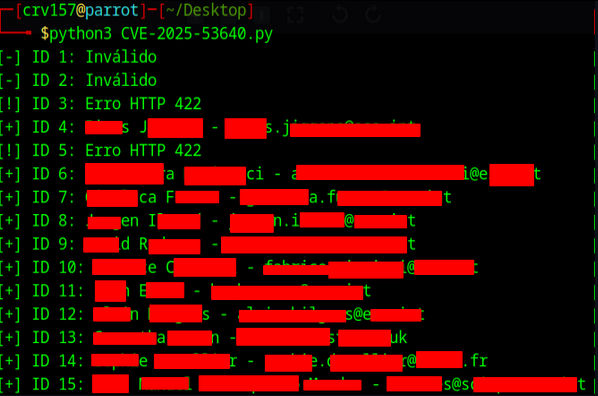 rafaelcorvino1/cve-2025-53640
Broken Object Level Authorization (BOLA) in CERN's Indico leads to authenticated user enumeration.