
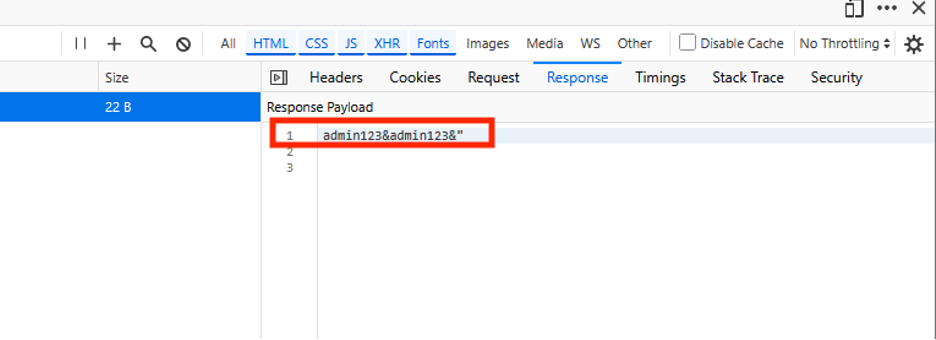
CVE-2025-45620
 weedl/cve-2025-45620
Disclosure of client-side authentication bypass in AVer camera web interface exposing unencrypted credentials via network traffic monitoring.
authenticationhardware-securityiot-security+3
weedl/cve-2025-45620Disclosure of client-side authentication bypass in AVer camera web interface exposing unencrypted credentials via network traffic monitoring.
 huzaifahussain98/cve-2020-23584
REMOTE CODE EXECUTION
 huzaifahussain98/cve-2020-23589
Denial of Service through CSRF
 huzaifahussain98/cve-2020-23592
CSRF attack leads to Reset ONU to Factory Default
 huzaifahussain98/cve-2020-23588
CSRF attack leads to "Enable or Disable Ports" and to "Change port numbers
 luct0r/cve-2018-17873
WiFiRanger 7.0.8rc3 Incorrect Access Control - Privilege Escalation
 ultramangaia/xiaomi_mi_wifi_r3g_vulnerability_poc
A login bypass(CVE-2019-18371) and a command injection vulnerability(CVE-2019-18370) in Xiaomi Router R3G up to version 2.28.23.

 afang5472/tp-link-wdr-router-command-injection_poc
CVE-2019-6487. A command injection vulnerability in TP-Link WDR5620 Series up to verion 3.
 shadowgatt/cve-2019-19356
Netis router RCE exploit ( CVE-2019-19356)
 ayushman4/tp-link-archer-cr-700-xss-exploit
Exploiting TP-Link Archer CR-700 Router. (Responsibly Disclosed to TP-Link)
 badboycxcc/cve-2023-24100
nuclei templates CVE RCE CNVD IoT
 yanxinwu946/hikvision-unauthenticated-rce-cve-2021-36260
海康威视RCE漏洞 批量检测和利用工具
 afaq1337/cve-2021-35296
PoC of CVE-2021-35296 - PTCL Modem HG150-Ub
 baroi-ai/nepstech-xpon-router-cve-2024-40119
Cross-Site Request Forgery (CSRF) vulnerability in the password change function, which allows remote attackers to change the admin password without…
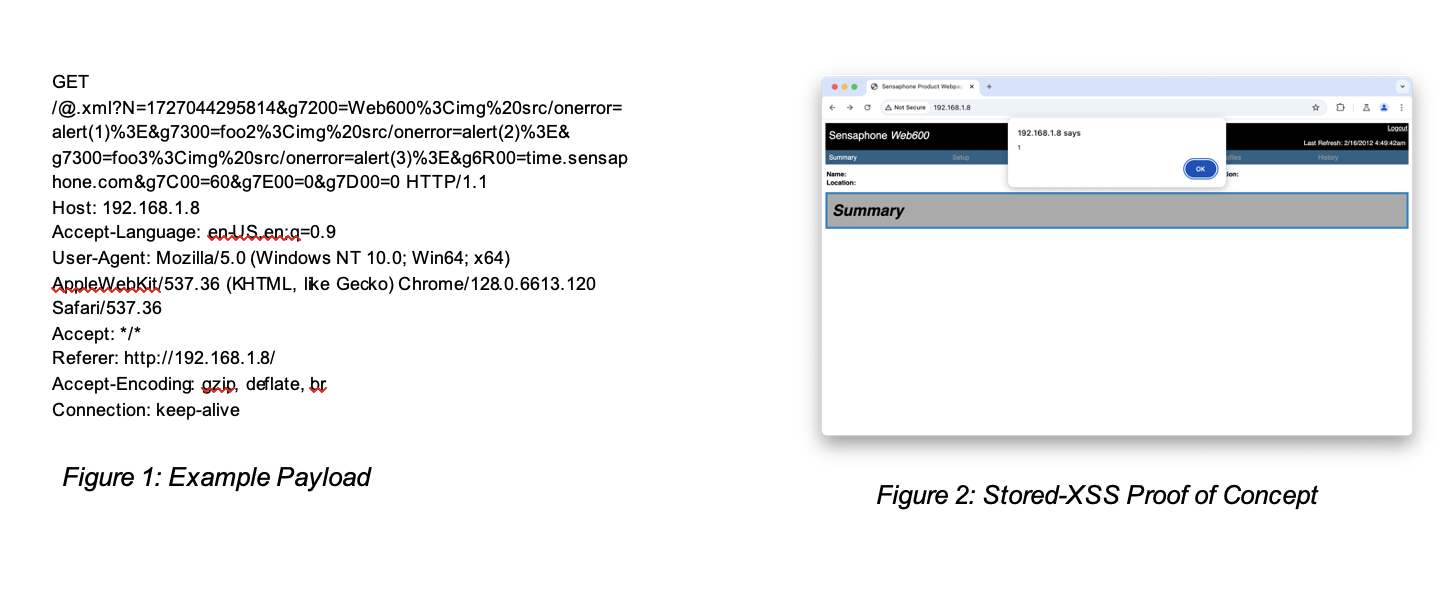 tcbutler320/cve-2024-55040-sensaphone-xss
Public disclose of several stored XSS vulnerabilities in the Sensaphone WEB600 (CVE-2024-55040)
 oscarakaelvis/cve-2023-51119
Improper Access Control on D-Link DIR-605L router
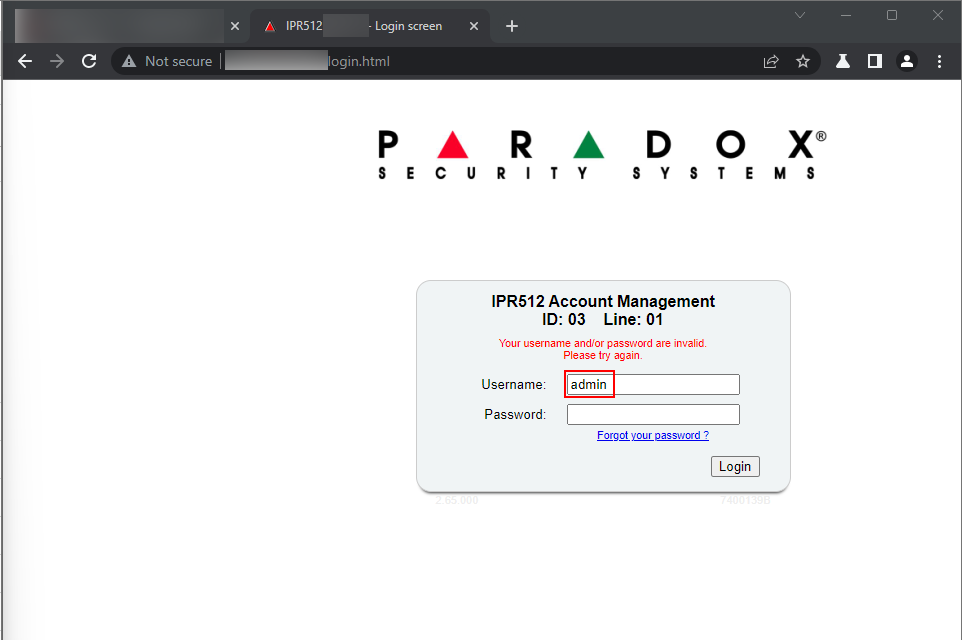 darknesschieftain/injection-vulnerability-in-paradox-security-systems-ipr512-cve-2023-24709-poc
In Paradox Security System IPR512 Web console login form page, attacker can input JavaScript string, such as "</script>" that will overwrite…