
GetFGPP
 n00py/getfgpp
Get Fine Grained Password Policy
configuration-auditinginformation-gatheringpenetration-testing+1
n00py/getfgppGet Fine Grained Password Policy
 usdag/sncscan
Tool for analyzing SAP Secure Network Communications (SNC).
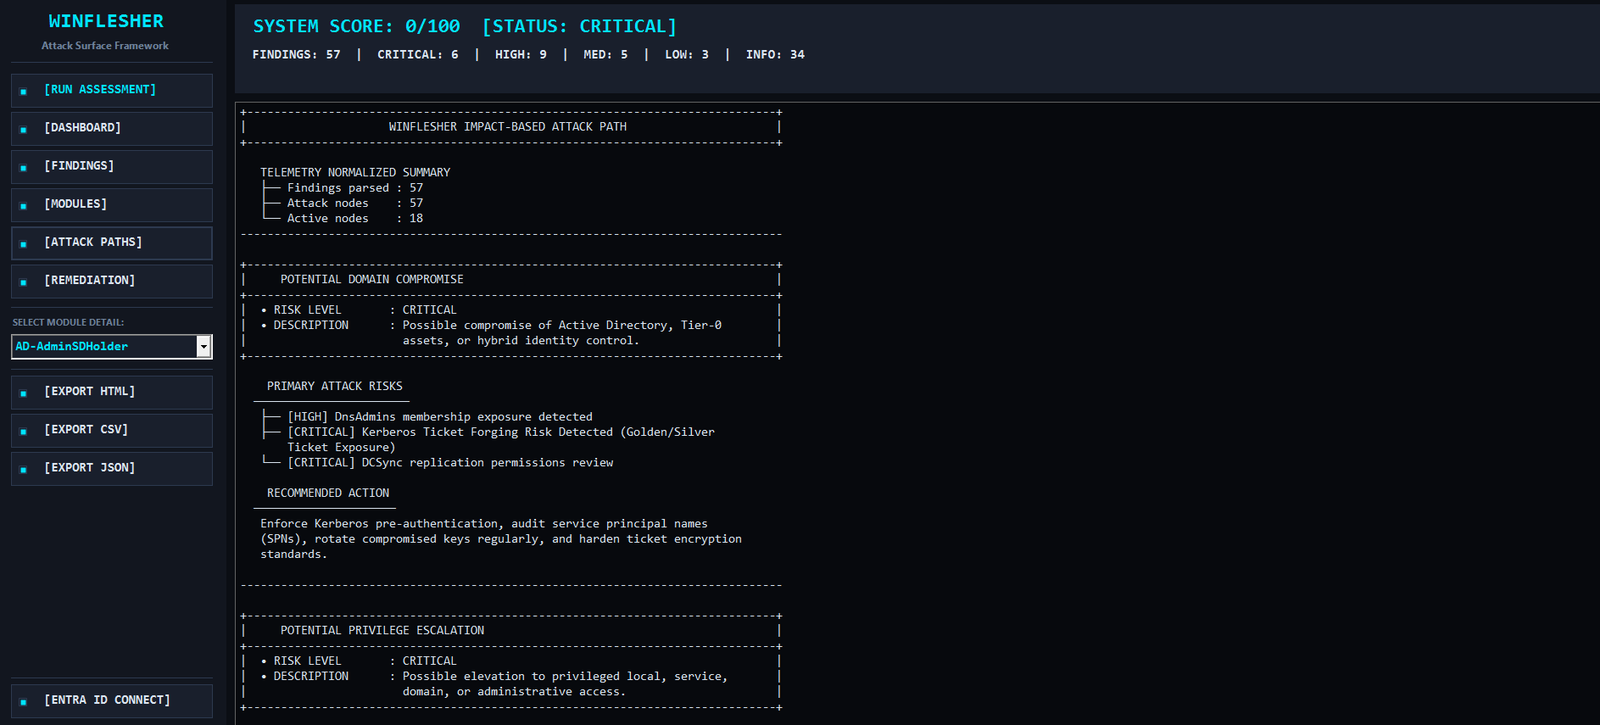 mindsflee/winflesher
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
 trustedsec/rage
Vendor-neutral NDJSON attack-graph format with node/edge taxonomy, AWS/GCP/Azure mappings, derivation rules, and an exposure DB for offensive…
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
 jas502n/database-spring-enc
sprint encode (plan text) get enc password
 owasp/sapkiln
OWASP SAPKiln is a graphical user interface (GUI) tool designed to facilitate securing and auditing SAP systems effectively.
 alt3kx/wafparan01d3
Quick WAF "paranoid" Doctor Evaluation | WAFPARAN01D3 Tool
 whereisxuezugi/cplhf
Modular Bash toolkit that hardens Debian/Ubuntu systems for CyberPatriot competitions, automating account, firewall, SSH, PAM, and service hardening…
 synacktiv/cve-2020-9289
Decrypt reversible secrets encrypted using the default hardcoded key related to CVE-2020-9289 on FortiAnalyzer/FortiManager (the only difference with…
 javuto/nbox-pwnage
Here comes the paintrain!
 ermensonx/sudotimewarp-cve-2026-96512-
Reproduction and PoC scripts for CVE-2026-96512 (SudoTimeWarp), where the caller's TZ shifts sudoers NOTBEFORE/NOTAFTER windows, plus mitigation…
 darabium/cve-2026-24733
Dependency-free Python verifier that detects CVE-2026-24733, an Apache Tomcat HTTP/0.9 HEAD security-constraint bypass, with JSON output and CI/CD…
 nvansluis/test_cve-2023-46747
Python script to test F5 BIG-IP for CVE-2023-46747 and add an administrator account if vulnerable.
 mrk336/from-foothold-to-domain-admin-weaponizing-cve-2025-54918-in-real-world-devops
Simulated exploitation and mitigation of CVE-2025-54918 (Windows NTLM flaw). Includes detection scripts, Ansible patching, and CI/CD hardening.…
 baba01hacker666/cve-2026-33032
Python proof-of-concept for CVE-2026-33032 that inspects nginx status and configs, then demonstrates unauthorized config write with reload to deploy…
 alekos3/cve_2023_20198_detector
This script can identify if Cisco IOS XE devices are vulnerable to CVE-2023-20198
 almarworld/kerberosaudit-ps
Kerberos audit for CVE-2026-20833