Google-api-key-scanner

Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.

Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.

Unofficial Acunetix CLI tool for automated pentesting and bug hunting across large scopes.

Performing automated scan using Burp Suite Pro & Vmware Burp Rest API

Collaborative application security testing between humans and agents via CLI and MCP

A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.

burpsuite 的Spring漏洞扫描插件。SpringVulScan:支持检测:路由泄露|CVE-2022-22965|CVE-2022-22963|CVE-2022-22947|CVE-2016-4977

Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…

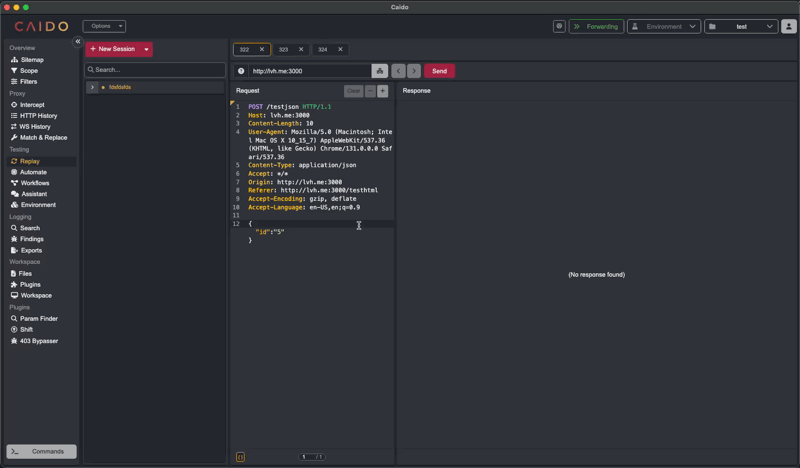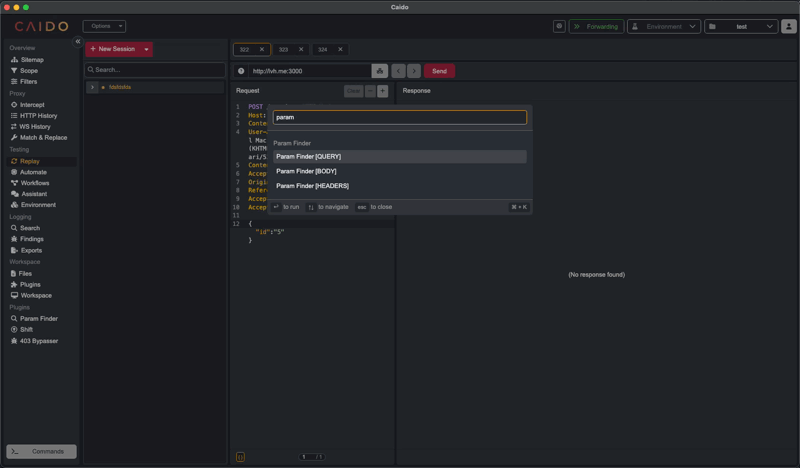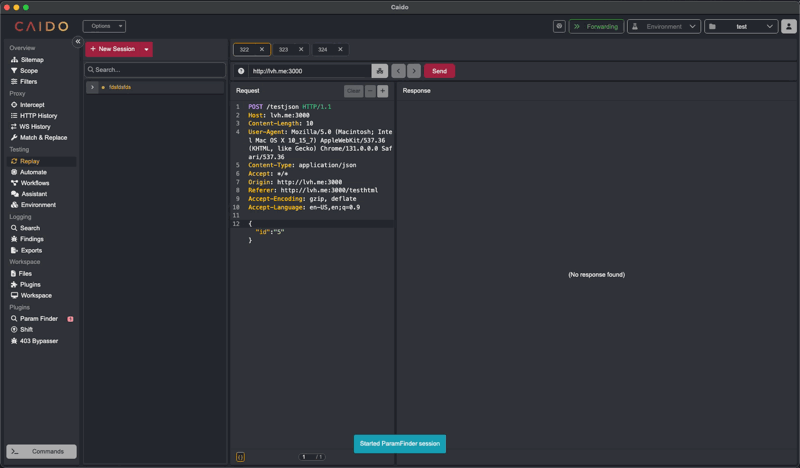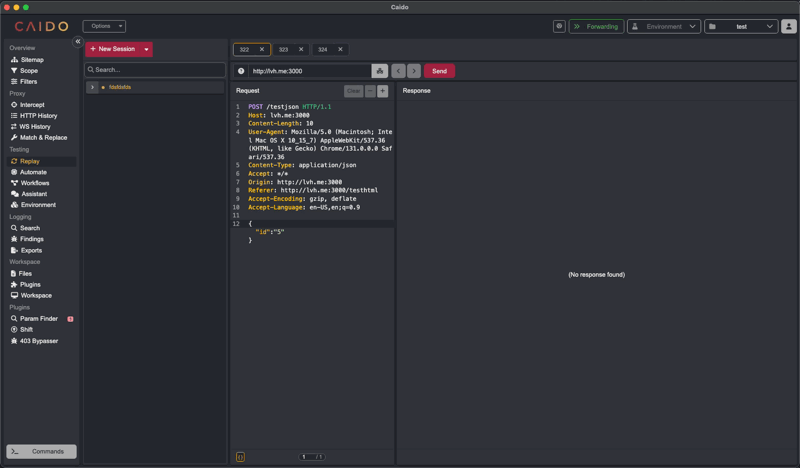
Discover hidden parameters in Caido

Burp Commander written in Go

Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.

This Burp Suite extension allows you to customize header with put a new header into HTTP REQUEST BurpSuite (Scanner, Intruder, Repeater, Proxy…

A Burp Extender plugin, that will make binary soap objects readable and modifiable.

An HTTP client specifically developed for security researchers

CyberArk Security Audit

Radamsa fuzzer extension for Burp Suite

A Burp Extender plugin, that will take deserialized AMF objects and encode them in XML using the Xtream library

BurpSuite Standard/Private Collaborator Library

Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…