

cve-2023-20198
 iveresk/cve-2023-20198
1vere$k POC on the CVE-2023-20198
exploitationinformation-gatheringpenetration-testing+3
63 years ago
iveresk/cve-2023-201981vere$k POC on the CVE-2023-20198
 hackspeak/cve-2026-66066
CVE-2026-66066 (KindaRails2Shell) PoC - Rails Active Storage/libvips arbitrary file read to RCE; for authorized security testing
 securifera/cve-2019-7839
CVE-2019-7839
 nullbytesuitedevs/cve-2019-0708
PoC exploit for BlueKeep (CVE-2019-0708)
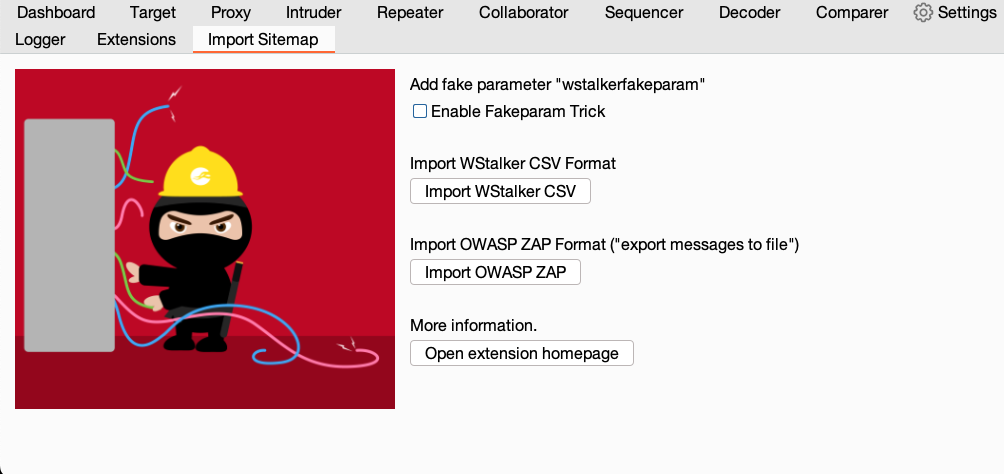 nccgroup/burpimportsitemap
Import To Sitemap is a Burp Suite Extension to import wstalker CSV file or ZAP export file into Burp Sitemap
 thugcrowd/cve-2019-0708
sup pry0cc :3
 voidsec/tivoli-madness
Advisory for CVE-2020-28054 & stack based buffer overflow in IBM Tivoli Storage Manager
 im-hanzou/fubucker
Automatic Mass Tool for checking vulnerability in CVE-2022-1386 - Fusion Builder < 3.6.2 - Unauthenticated SSRF
 momenbasel/shodscript
Automate exploit/PoC execution against Shodan search results - concurrent dispatch, filtering, structured output, and export.
 mo0ns/grafana_poc-cve-2021-43798
Grafana-POC任意文件读取漏洞(CVE-2021-43798)
 wiggels/regresshion-check
CLI Tool to Check SSH Servers for Vulnerability to CVE-2024-6387
 kkirsche/cve-2019-16692
Exploit code for CVE-2019-16692, a phpIPAM vulnerability enabling authenticated remote code execution via SQL injection in the app_search.php…
 madexploits/laravel-debug-checker
CVE-2021-3129 Exploit Checker By ./MrMad
 mr-xn/cve-2024-36991
Path Traversal On The "/Modules/Messaging/" Endpoint In Splunk Enterprise On Windows
 x00byte/putscanner
A tool that identifies writable web directories in Apache Tomcat via HTTP PUT method [CVE-2025-24813]
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
 mr-xn/cve-2021-26855-d
Python tool to exploit CVE-2021-26855 (ProxyLogon) for downloading Exchange mailbox emails via EWS, supporting user enumeration and bulk target…
 ynsmroztas/wpsniper
CVE-2026-87902 detector. WordPress get_page_template LFI class. Detect-only. Authorized lab.