
CVE-2020-4463
 ibonok/cve-2020-4463
IBM Maximo Asset Management is vulnerable to Information Disclosure via XXE Vulnerability (CVE-2020-4463)
exploitationinformation-gatheringpenetration-testing+3
52
ibonok/cve-2020-4463IBM Maximo Asset Management is vulnerable to Information Disclosure via XXE Vulnerability (CVE-2020-4463)
 shaniidev/bug-reaper
Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
 immunit/cve-2018-11759
Proof-of-concept exploit for CVE-2018-11759 demonstrating Apache mod_jk access bypass via specially crafted requests to bypass reverse proxy…
 zerodayevil/cve-2026-42980-poc
Proof-of-concept code demonstrating CVE-2026-42980, providing a reproducible test case to validate the vulnerability and verify patched or mitigated…
 philesiv/xsleaker
Searcher for cross-site leaks (XS-Leaks)
 afang5472/tp-link-wdr-router-command-injection_poc
CVE-2019-6487. A command injection vulnerability in TP-Link WDR5620 Series up to verion 3.
 optiv/cve-2020-15931
Netwrix Account Lockout Examiner 4.1 Domain Admin Account Credential Disclosure Vulnerability
 rxerium/freepbx-vulns-december-25
Detection for CVE-2025-61675, CVE-2025-61678 & CVE-2025-66039
 dn9uy3n/check-wp-cve-2020-35489
The (WordPress) website test script can be exploited for Unlimited File Upload via CVE-2020-35489
 kh4sh3i/proxyshell
CVE-2021-34473 Microsoft Exchange Server Remote Code Execution Vulnerability
 walnutsecurity/cve-2021-42013
cve-2021-42013.py is a python script that will help in finding Path Traversal or Remote Code Execution vulnerability in Apache 2.4.50
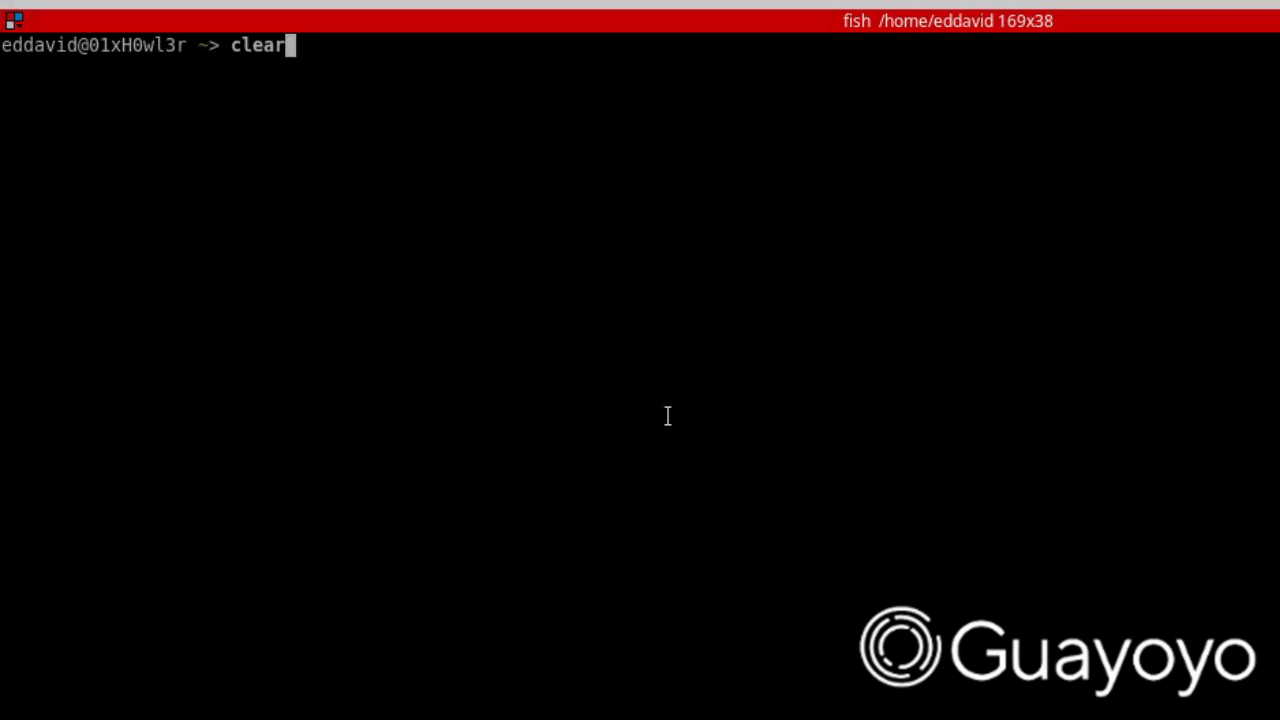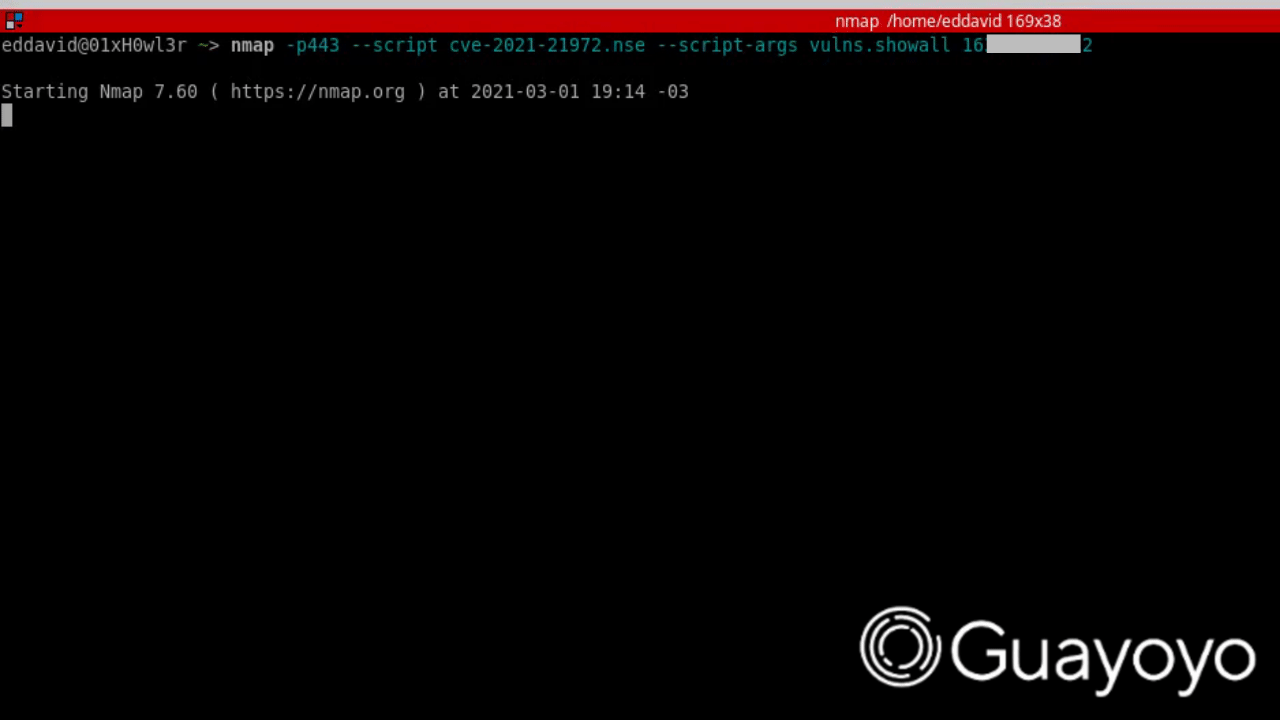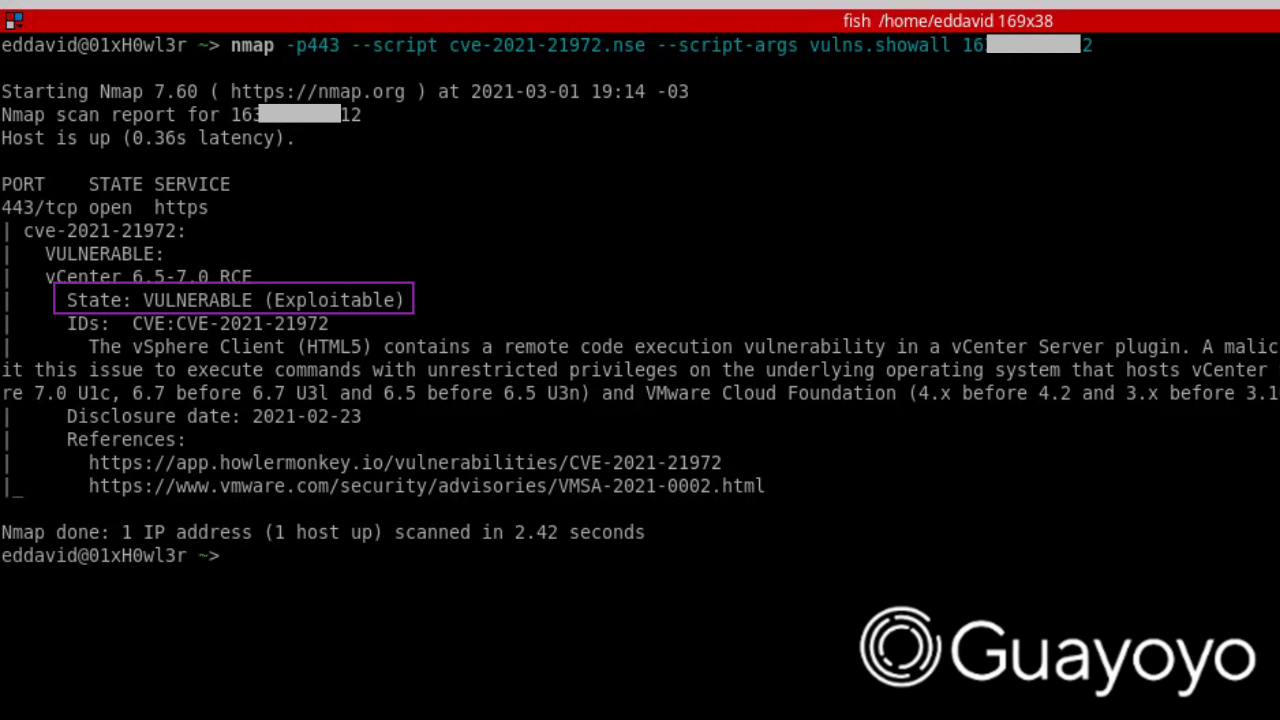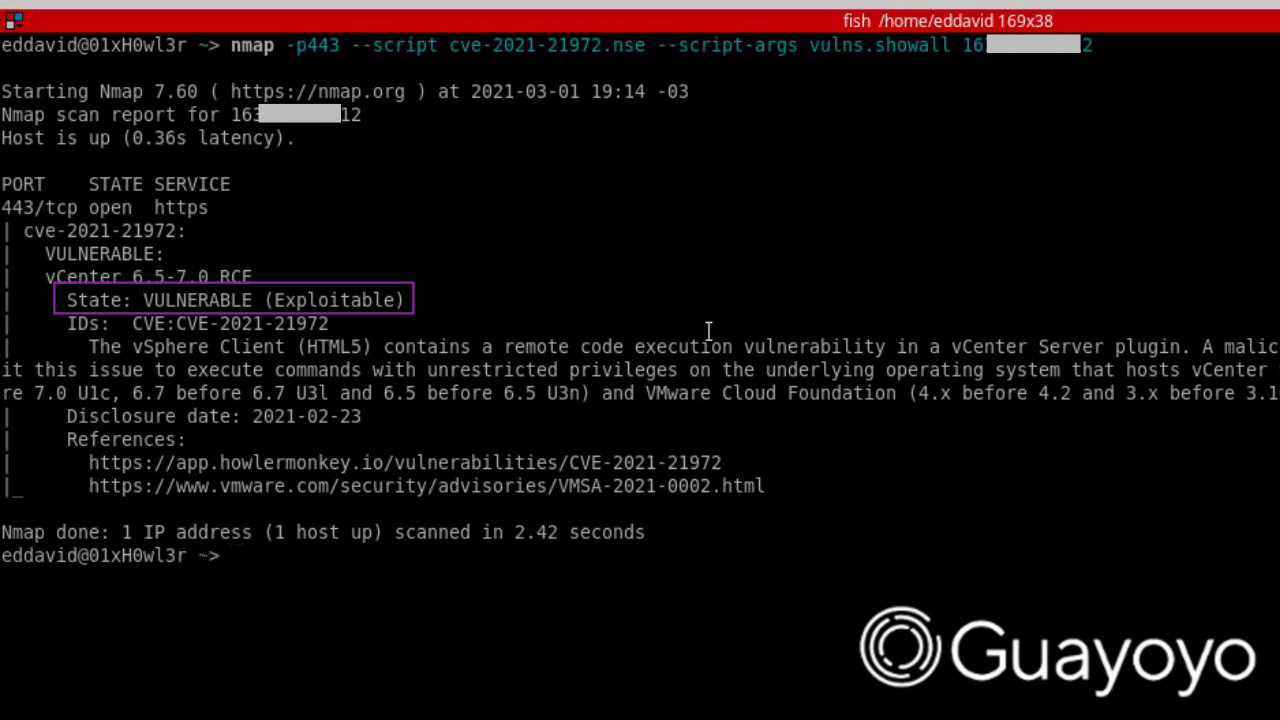 guayoyocyber/cve-2021-21972
Nmap script to check vulnerability CVE-2021-21972
 hynekpetrak/detect_bluekeep.py
Python script to detect bluekeep vulnerability (CVE-2019-0708) with TLS/SSL and x509 support
 mrcl0wnlab/nuclei-template-cve-2022-1388-big-ip-icontrol-rest-exposed
This vulnerability may allow an unauthenticated attacker with network access to the BIG-IP system through the management port and/or self IP…
 brut-security/cve-2024-4879
CVE-2024-4879 - Jelly Template Injection Vulnerability in ServiceNow
 ibonok/cve-2020-1611
Juniper Junos Space (CVE-2020-1611) (PoC)
 k8gege/cve-2019-11043
Proof-of-concept exploit module for CVE-2019-11043 (PHP-FPM remote code execution) with batch scanning capabilities for vulnerable Nginx…
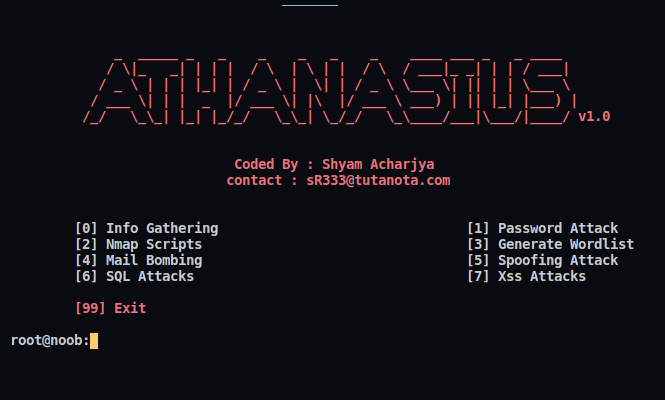 shyam999/athanasius
Framework for penetration testing. The software can identify everything from cross-site scripting to SQL injection. Developers can also use this…