
CVE-2026-79984
 oscerd/cve-2026-79984
Runnable proof-of-concept reproducer for CVE-2026-79984, a path traversal in Apache Camel camel-mina-sftp, with malicious SFTP server fixtures and…
defensive-toolseducationexploitation+3
oscerd/cve-2026-79984Runnable proof-of-concept reproducer for CVE-2026-79984, a path traversal in Apache Camel camel-mina-sftp, with malicious SFTP server fixtures and…
 hasan8babiker/cve-2024-6387
PoC exploit for CVE-2024-6387 (OpenSSH regreSSHion), targeting sshd signal handler race condition for remote code execution on glibc Linux systems.
 prodefense/hawk
Golang tool designed to exfiltrate passwords found via the sshd and su services
 lane0218/cve-2023-25136-poc
Minimal Docker-based reproduction environment for OpenSSH 9.1p1 pre-auth double-free vulnerability (CVE-2023-25136), demonstrating memory corruption…
 shoucheng3/apache__mina-sshd_cve-2023-35887_2-9-2
Pure Java SSH client/server library implementing SSH-2 protocol with support for multiple ciphers, key exchanges, authentication methods, SFTP, SCP,…
 s1d6point7bugcrowd/cve-2024-6387-race-condition-in-signal-handling-for-openssh
Technical analysis and proof-of-concept for CVE-2024-6387, a race condition in OpenSSH signal handling enabling unauthenticated remote code execution…
 jocker2410/cve-2024-6387_poc
Proof-of-concept exploit for CVE-2024-6387, a signal handler race condition in OpenSSH server (sshd) on glibc-based Linux systems, enabling remote…
 alex14324/ssh_poc2024
An exploit for CVE-2024-6387, targeting a signal handler race condition in OpenSSH's server
 lflare/cve-2024-6387-poc
MIRROR of the original 32-bit PoC for CVE-2024-6387 "regreSSHion" by 7etsuo/cve-2024-6387-poc
 anhvutuan/cve-2024-6387-poc-1
CVE-2024-6387, also known as RegreSSHion, is a high-severity vulnerability found in OpenSSH servers (sshd) running on glibc-based Linux systems. It…
 dimamend/cve-2024-6387-poc
Exploit for CVE-2024-6387, a signal handler race condition in OpenSSH sshd, enabling remote code execution as root on glibc-based Linux systems.
 sardine-web/cve-2024-6387_check
A security regression (CVE-2006-5051) was discovered in OpenSSH's server (sshd). There is a race condition which can lead to sshd to handle some…
 4lxprime/regresshive
rewrited SSH Exploit for CVE-2024-6387 (regreSSHion)
 t3rry327/cve-2024-6387-poc
Exploit for CVE-2024-6387 targeting a signal handler race condition in OpenSSH sshd on glibc-based Linux systems, enabling remote code execution as…
 sxlmnwb/cve-2024-6387
Targeting a signal handler race condition in OpenSSH's server (sshd) on glibc-based Linux systems.
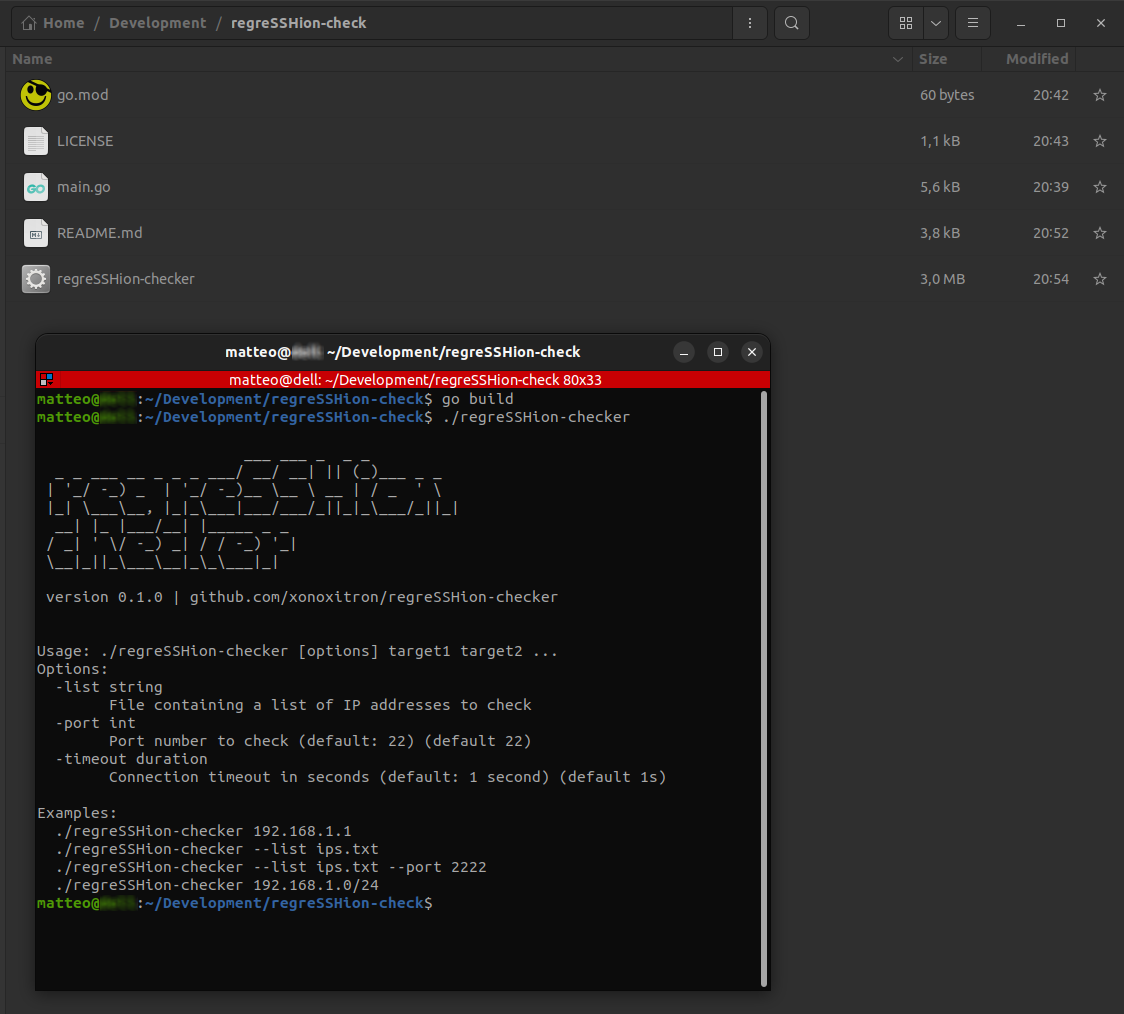 xonoxitron/regresshion-checker
Quickly identifies servers vulnerable to OpenSSH 'regreSSHion' (CVE-2024-6387).
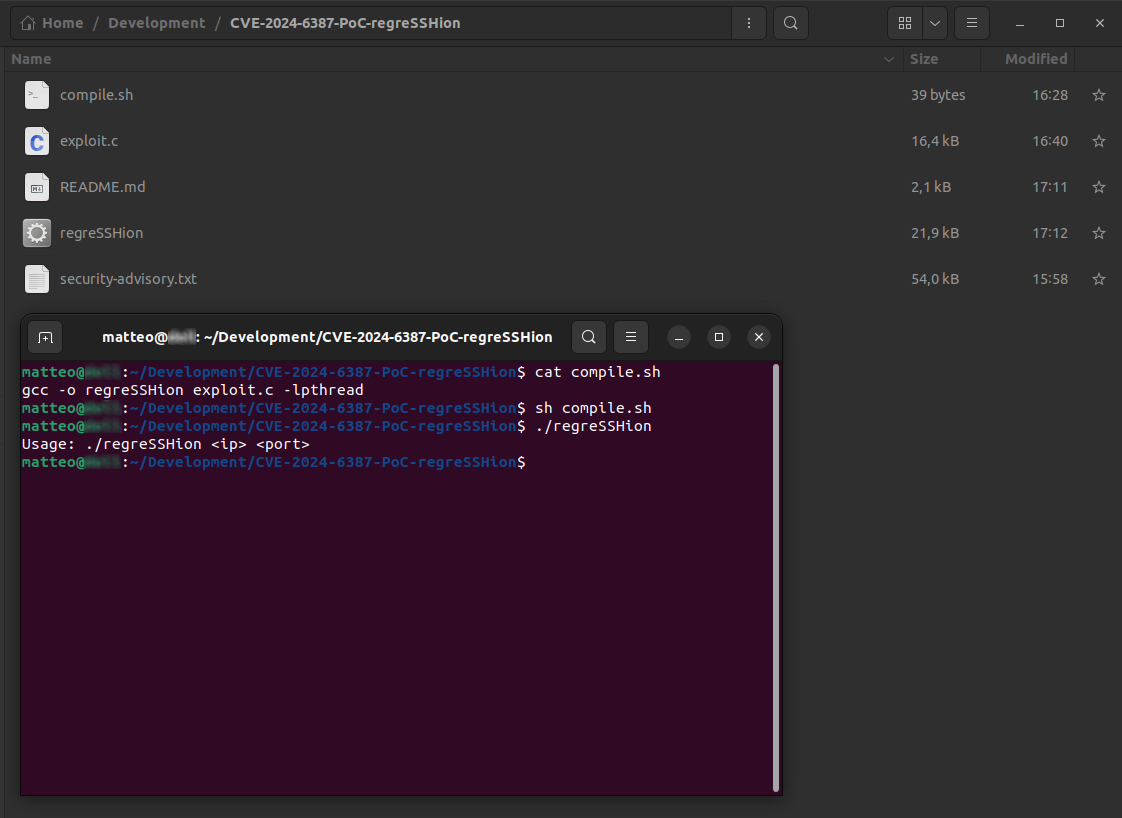 xonoxitron/regresshion
CVE-2024-6387 (regreSSHion) Exploit (PoC), a vulnerability in OpenSSH's server (sshd) on glibc-based Linux systems.
 dawnl3ss/cve-2024-6387
Proof-of-concept exploit for CVE-2024-6387, a signal handler race condition in OpenSSH's sshd server, enabling remote code execution.