

PEASS-ng
 peass-ng/peass-ng
PEASS - Privilege Escalation Awesome Scripts SUITE (with colors)
educationexploitationexploit-frameworks+7
peass-ng/peass-ngPEASS - Privilege Escalation Awesome Scripts SUITE (with colors)
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
 anylnk/stprocessmonitorbyovd
The PoC for CVE-2025-70795 / CVE-2026-0828 and updated driver
 moisestapia/cve-2022-3218
Python exploit for CVE-2022-3218 that generates a reverse TCP payload via msfvenom and delivers it over HTTP to a target Windows host.
 decoder-it/newmachineaccount
Creates Active Directory machine accounts with custom passwords, supporting optional OU placement, explicit credentials, and UAC flag configuration.
 sec13b/ms09-050_cve-2009-3103
CVE-2009-3103 ms09-050
 naksyn/pythonmemorymodule
pure-python implementation of MemoryModule technique to load dll and unmanaged exe entirely from memory
 byinarie/teams_dump
PoC for dumping and decrypting cookies in the latest version of Microsoft Teams
 improsec/improhound
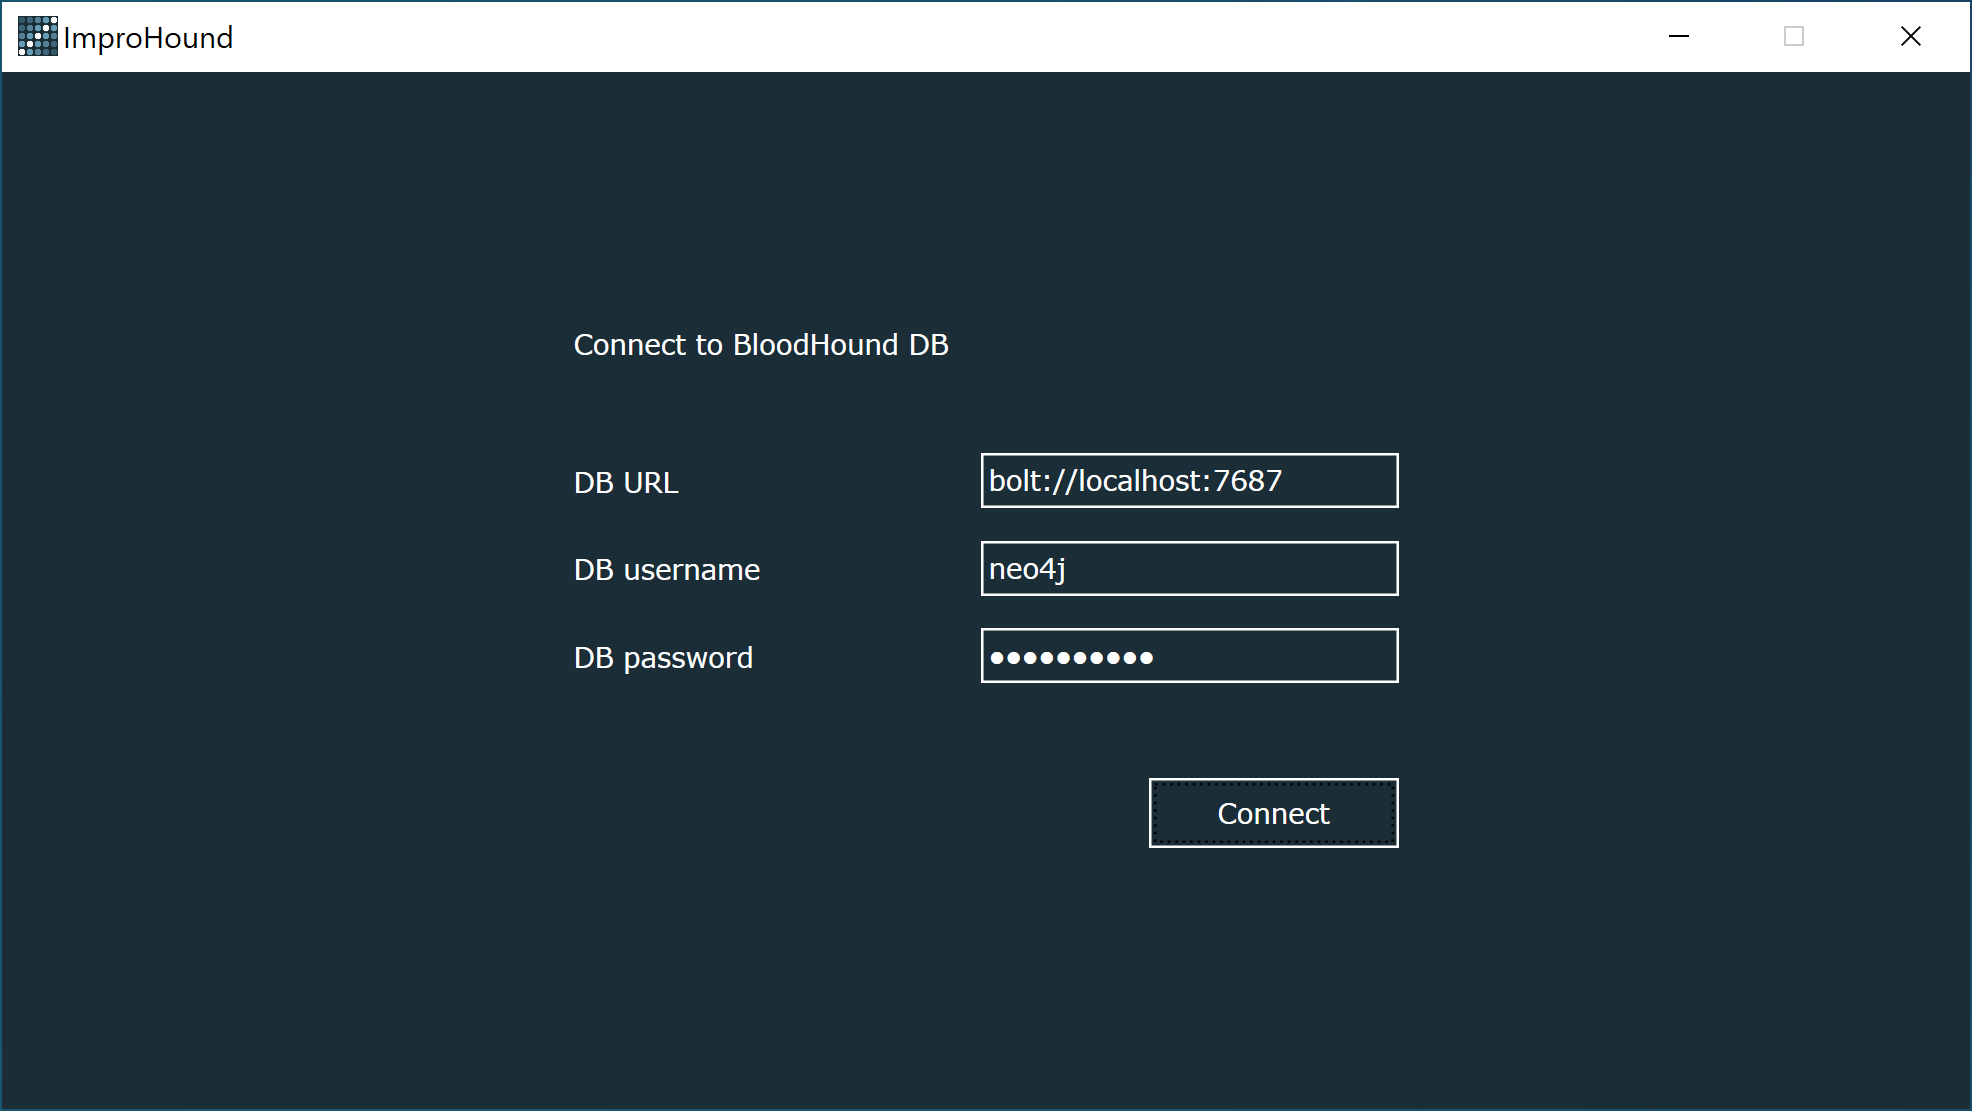
Identify the attack paths in BloodHound breaking your AD tiering
 yanncam/exe2powershell
exe2powershell - exe2bat reborn for modern Windows
 erfze/cve-2017-8570
Python-based exploit for CVE-2017-8570, generating malicious RTF files with embedded SCT and EXE payloads for targeted exploitation.
 jonatan1024/clrinject
Injects C# EXE or DLL Assembly into every CLR runtime and AppDomain of another process.
 eonrickity/cve-2017-0213
Fixed No Virus Manual Automatic Loader exe no zip because zip picks up the anti virus detector.
 4w4k3/umbrella
A Phishing Dropper designed to Pentest.
 graniet/chromebackdoor
Chromebackdoor is a PoC of pentest tool, this tool use a MITB technique for generate a windows executable ".exe" after launch run a malicious…